| [*] | the slides were prepared for S5 and can be viewed directly in modern browsers. The best experience is with a 1024x768 or higher resolution. Here are instructions on how to browse them (though you probably don't need them). |
| [ ] | If nothing else, then an account on skynet.ie should allow me to port-forward or even use VPN from Zurich, to access some of the electronic library resources available here, to which the University of Zurich has not subscribed. |
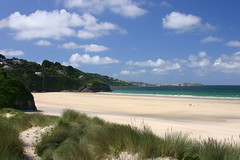
Ah yes. After the horrendously grim weather had passed, the weather
improved and we headed for the beach. On the way down we commented on how
this was the classic British burning weather: bright sunshine, a strong
breeze, and occassional clouds combine to burn skin without even feeling
that hot. Of course knowing this meant nothing, we were too distracted
with purchasing pasties and drink to think about putting a decent amount
of sunblock on.
Obviously the main thing to do at the beach, after we'd sat down, not
applied sunblock, and scoffed a pasty, was to dig a hole. A huge hole.
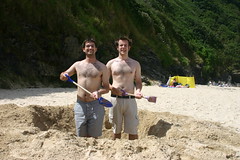
Spades were purchased and we took turns to help Pete dig The Hole.
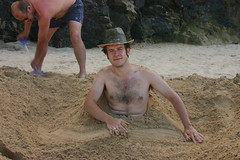
Astute readers will notice the inevitable outcome of saying this is burning weather, not putting enough sunblock on, and digging a hole (an activity that results in the back being exposed to the sun). Ouch. After the hole had been dug we had to full it in again to avoid trapping small childen in it. Obviously this led to a series of hilarious scenes involving burying Pete up to his chest, modelling breasts and a penis, and so on. Finally the hole was flat again, at which point an impromptu long jump sand pit was arranged. I came first in the long jump, and although failing miserably at triple jump although I swear my technique was best (it's all in the wrists).
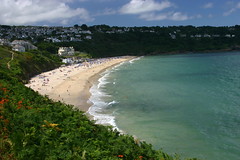
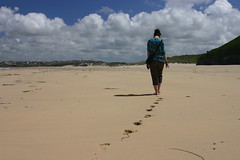
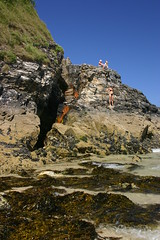
Next was to explore the costal path in the opposite direction towards
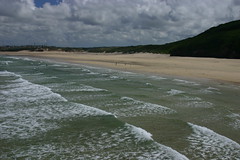
Porthkidney beach. The beach is pretty huge by my standards, and due to
the lack of facilities (no close car park, shops, toilets, and so on) it's
almost deserted: there were a few other people there with dogs (the other
local beaches are dog-free in summer) and that's about it. Googling to
confirm the name of the beach reveals that there is a history of naturism
and "inappropriate gay activity", but we didn't encounter any of that. ;)
The costal path was great, far more rough than the walk to St Ives (often
just a foot wide cutting in the ground), steep in places, and generally
running very close to the cliff edge. The views were great, but I always
think what a horror paths like these would be in winter, with the full
force of the Atlantic winds pounding against the cliffs. As a finale it
turns out that the costal path follows the cliff all the way along the
back of the beach, which would easily be another twenty minutes of walking
to reach sand. There is a shortcut down some stone stairs to the beach,
but we arrived at high tide and the bottom of the stairs (well, rocks)
were a foot deep in water. Wading up to the beach was a fitting end to
the walk, and made the beach feel like our own little desert island!
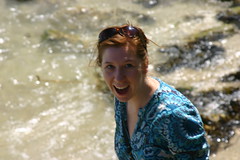
I'll have to explain the expression on Vicky in the above photo. As a
child when Vicky went to visit her father in Devon they used to go to the
beach and spend the day annoying the wildlife: chasing crabs, kicking
limpets off rocks and so on. When Vicky noticed that the rocks at the
bottom of the cliff were covered in limpets, she shouted "limpets!" with a
manic expression and preceeded to prod them frantically.
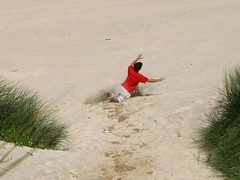
After lots of sitting around and digging tunnels, we headed for the dunes
for a spot of dune diving. This involves running at top spead down the
dunes and throwing yourself into the sand at the bottom. Ah, the simple
pleasures in life!
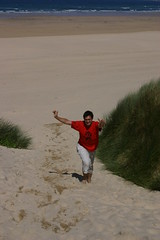
After my dive I ran back up the hill in the manner of a mad man, arms
out-stretched to Vicky as I collapsed in front of her, gasping "It's".
"What?", was the confused reply. This is terrible, I really need to get
Vicky to watch the Best Of Monty Python DVD we have
somewhere...
Possibly more to write, but Lost is on, so I'm off for now.
libacr38u. Obviously you will also need the belpic packages. For now, just install all of them—there still appears to be a dependency issue which I will need to fix; I'll announce on this blog when that has been done. Just run
aptitude install $(apt-cache showsrc belpic sed -e '/^Binary/!d;s/^Binary: //;s/,//g')and you will install them. I uploaded these packages to backports.org, too, where they'll hopefully show up some time soon (the current packages are still at 2.3.13 for some weird reason). This will give you:
apt-get install openssh-server
Then you can login with:
$ ssh efossnet@proxy.dream.edu.et
To verify the host key fingerprint of a machine:
$ ssh-keygen -l -f /etc/ssh/ssh_host_rsa_key.pub
Note: you need to verify it before logging in!
More information at http://www.securityfocus.com/infocus/1806
Example ssh usages
To log in:
$ ssh efossnet@proxy
To run a command in the remote computer:
$ ssh efossnet@proxy "cat /etc/hosts"
To copy a file to the remote computer:
$ scp Desktop/july-18.tar.gz efossnet@proxy:
To copy a file from the remote computer:
$ scp efossnet@proxy:july-18.tar.gz /tmp/
Beware of brute-force login attempts
Warning about SSH: there are people who run automated scans for ssh servers and
try to login using commonly used easy passwords.
If you have an SSH server on the network, use strong passwords, or if you can
it's even better to disable password authentication: in
/etc/ssh/sshd_config, add:
PasswordAuthentication no
To log in using public/private keys:
ssh-keygen -t rsa
ssh-copy-id -i .ssh/id_rsa.pub efossnet@proxy
1153294204.912 887 192.168.0.200 TCP_MISS/503 1441 GET http://www.google.com.et/search? - NONE/- text/html
That "/503" is one of the HTTP error codes.
Explanation of the error codes:
apt-get install mailx
echo ciao mail efossnet@localhost
To configure a workstation not to do any mail delivery locally and send all
mail produced locally to smtp.dream.edu.et:
apt-get install squirrelmail (on a working apache
setup).
To setup mailing lists: apt-get install mailman, then follow the
instructions in /usr/share/doc.
Mail server issues we encountered
When a mail is sent to efossnet@localhost, the system tries to send it to
efossnet@yoseph.org
Investigation:
rm ~efossnet/.forward
Apache
To add a new website:
cd /etc/apache2/sites-availablesudo cp default coursesudo vi course:
ServerName directive with the address of your server:
ServerName course.dream.edu.et/usr/share/doc and you want to use a different document
root.sudo a2ensite coursesudo /etc/init.d/apache2 reloadu (in command mode)
Redo: ^R (in command mode)
You can undo and redo multiple times.
To recover a lost password for root or for the ubuntu admin user
Boot with a live CD, mount the system on the hard disk (the live CD usually
does it automatically), then edit the file /etc/shadow, removing the
password:
enrico:$1$3AJfasjJFHa234dfh230:13343:0:99999:7:::
becomes:
enrico::13343:0:99999:7:::
You can edit the file because, in the live CD system, you can always become
root.
After you do this, reboot the system: you can log in without password, and set
yourself a new password using the command passwd.
Installing packages not on the CDs
To get a package for installing when offline:
apt-get --print-uris install dnsmasqapt-get --download-only install dnsmasq will download the
package for you in /var/cache/apt/archives.
You can install various previously downloaded debian packages with:
dpkg -i *.deb
Backups
There are various ways:
dump (for ext2/ext3 file systems)
or xfsdump (for xfs file systems).
Makes a low-level dump of the file system.
It must be used for every different partition.
It makes the most exact backup possible, including inode numbers.
It can do full and incremental backups.
To see the type of the filesystems, use 'mount' with no parameters.
To restore: restore or xfsrestore.tar
Filesystem independent.
It can work accross partitions.
It correctly backups permissions and hard links.
It can do full and incremental backups.
Example:
tar lzcpf backup.tar.gz /home /var /etc /usr/local
tar lzcpf root.tar.gz /
To restore:
tar zxpf backup.tar.gz
faubackup
Filesystem independent.
Uses hard drive as backup storage.
Always incremental.
It cannot do compression.
Unchanged files in new backups are just links to old backups, and do not
occupy space.
Any old backup can be deleted at any time without compromising the others.
It can be used to provided a "yesterday's files" service to users (both
locally and exported as a read-only samba share...).
To restore, just copy the files from the backup area.amanda
apt-get install amanda-client amanda-server
It is a network backup system.
It can do full and incremental backups.
You can have a backup server which handles the storage and various backup
clients that send the files to backup to the server.
It takes some studying to set up.
To restore: it has its own tool.dpkg --get-selections > pkglist
debconf-get-selections > pkgconfig
To restore:
dpkg --set-selections < list
debconf-set-selections < pkgconfig
apt-get dselect-upgrade
If you do this, they you only need to backup /etc, /home,
/usr/local, /var.mysqldump name-of-database gzip > name-of-database.dump.gz
To restore:
zcat name-of-database.dump.gz mysql
crontab -e
As root: add a file in one of the /etc/cron.* directories.
In cron. hourly,daily,weekly,monthly you put scripts.
In the other directories you put crontab files (man 5 crontab).
If the system is turned off during normal maintainance hours, you can do two
things:
$ at 17:40
echo "Please tell Enrico that the lesson is finished" mail efossnet@dream.edu.et
^D
When and how to automate
rkhunter, chkrootkitchecksecuritydebsecantiger^C: interrupt (sends SIGTERM)^\: interrupt (send SIGQUIT)^D: end of input^S: stop scrolling^Q: resume scrolling^Q.
Problems we had today with postfix
efossnet@dream.edu.et is accepted only if sent locally.
Reason:
$ host -t mx dream.edu.et
Host dream.edu.et not found: 3(NXDOMAIN)
Solution: tell dnsmasq to handle a MX record also for dream.edu.et:
mx-host=dream.edu.et,smtp.dream.edu.et,50apt-get --print-uris doesn't print the URIs if the package is in the
local cache, and there seems to be no way to have it do it./etc/apache2/sites-available/default, is the NameVirtualHost *
directive appropriate there? It gets in the way when using 'default' as a
template for new sites.
Otherwise, one can add a new (disabled) site that can be used as a template
for new sites instead of default.crontab -e are not that easy to read.You're eligible for a big discount on our blogging software! Only $3.95 a month!
[Continue] Cancel... where the "Continue" button adds the add-on to your account and "Cancel" is what you need to go on with your order. I think this is borderline fraud, but as far as I know nobody's been shut down or fined for it. For contrast, there are a lot of really good community-oriented and Open Source-friendly hosting services out there, like Montreal's Koumbit. They'll usually be able to devote more time and energy to individuals' technical needs. Often, though, small companies and community groups can't get the same economy of scale and thus price level to compete with the big guys. Of course, what you usually trade away for that $0.75 a month is any customer service or friendliness or control of your own site. The big guys are organized around selling hard to inexperienced people on price, then ignoring their requests for help and treating them like idiots for asking until they go away. Getting help with real problems like server downtime or misbehaviour can be as humiliating as having someone explain what "Cut", "Copy", and "Paste" mean, and probably get you as many over-the-phone eye roll pauses. "My Web site is down!" <eye roll> "Did your AOL Chat window get in front of your browser window, sir?" I think the best option for people is to look around, find a group or company that has a price you can live with and business practices that don't turn your stomach, and give them a try. Make frequent local backups of your site, and be ready to leave if you need to. tags: web hosting community comparison customer service
apt-get install openssh-serverThen you can login with:
$ ssh efossnet@proxy.dream.edu.etTo verify the host key fingerprint of a machine:
$ ssh-keygen -l -f /etc/ssh/ssh_host_rsa_key.pubNote: you need to verify it before logging in! More information at http://www.securityfocus.com/infocus/1806 Example ssh usages:
Warning about SSH: there are people who run automated scans for ssh servers and try to login using commonly used easy passwords. If you have an SSH server on the network, use strong passwords, or if you can it's even better to disable password authentication: in /etc/ssh/sshd_config, add:
To log in:
$ ssh efossnet@proxyTo run a command in the remote computer:
$ ssh efossnet@proxy "cat /etc/hosts"To copy a file to the remote computer:
$ scp Desktop/july-18.tar.gz efossnet@proxy:To copy a file from the remote computer:
$ scp efossnet@proxy:july-18.tar.gz /tmp/
PasswordAuthentication noTo log in using public/private keys:
If you use ssh often, read these:
Create your key:
ssh-keygen -t rsaCopy your public key to the machine where you want to log in:
ssh-copy-id -i .ssh/id_rsa.pub efossnet@proxyNow you can ssh using your RSA key
ssl does not work. Reason: squid tries to directly connect to the ssl server, but the AAU network wants us to go through their proxy. Ideal solution: none. There is no way to tell squid to use a parent proxy for SSL connections. Solution: update the documentation for the Dream university users telling to setup a different proxy for SSL connections. Longer term solution: get the AAU network admins to enable outgoing SSL connections from the Dream university proxy. Other things that can be done:
- report a bug on squid reporting the need and requesting the feature
- download squid source code and implement the feature ourselves, then submit the patch to the squid people
Browsing normal pages returns an error of 'Connection refused'. In the logs, the line is:
1153294204.912 887 192.168.0.200 TCP_MISS/503 1441 GET http://www.google.com.et/search? - NONE/- text/htmlThat "/503" is one of the HTTP error codes. Explanation of the error codes:Reason: the other proxy is refusing connections from our proxy. Solution: none so far. Will need to get in touch with the admins of the other proxy to try to find out why it refuses connection to our proxy, and how we can fix the problem.
Quick way to send test mails:
- The mail name is the name of the mail server you're setting up (TODO: need more details on what's it used for)
- The smarthost is the name of the mail server that will relay mail for you.
apt-get install mailx echo ciao mail efossnet@localhostTo configure a workstation not to do any mail delivery locally and send all mail produced locally to smtp.dream.edu.et:
To setup a webmail: apt-get install squirrelmail (on a working apache setup). To setup mailing lists: apt-get install mailman, then follow the instructions in /usr/share/doc. Mail server issues we encountered:
- install postfix choosing "Satellite system"
- put smtp.dream.edu.et as a smarthost.
When a mail is sent to efossnet@localhost, the system tries to send it to efossnet@yoseph.org
Cause: the user efossnet had forgotten that he or she had setup a .forward file in the home directory. Solution:
- Investigation:
- "yoseph.org" does not appear anywhere in /etc or /var/spool/postfix
- postfix configuration has been reloaded
- postfix logs show that the mail has been 'forwarded'
rm ~efossnet/.forward
cd /etc/apache2/sites-available
sudo cp default course
sudo vi course:
Remove the first line
Add a ServerName directive with the address of your server:
ServerName course.dream.edu.etCustomize the rest as needed: you at least want to remove the support for browsing /usr/share/doc and you want to use a different document root.
sudo a2ensite course
sudo /etc/init.d/apache2 reload
enrico:$1$3AJfasjJFHa234dfh230:13343:0:99999:7:::becomes:
enrico::13343:0:99999:7:::You can edit the file because, in the live CD system, you can always become root. After you do this, reboot the system: you can log in without password, and set yourself a new password using the command passwd.
Otherwise, apt-get --download-only install dnsmasq will download the package for you in /var/cache/apt/archives. You can install various previously downloaded debian packages with:
- apt-get --print-uris install dnsmasq
- Manually download the packages at the URLs that it gives you
dpkg -i *.deb
Some data requires exporting before backing it up:
dump (for ext2/ext3 file systems) or xfsdump (for xfs file systems). Makes a low-level dump of the file system. It must be used for every different partition. It makes the most exact backup possible, including inode numbers. It can do full and incremental backups. To see the type of the filesystems, use 'mount' with no parameters. To restore: restore or xfsrestore.
tar Filesystem independent. It can work accross partitions. It correctly backups permissions and hard links. It can do full and incremental backups. Example:
tar lzcpf backup.tar.gz /home /var /etc /usr/local tar lzcpf root.tar.gz /To restore:tar zxpf backup.tar.gzfaubackup Filesystem independent. Uses hard drive as backup storage. Always incremental. It cannot do compression. Unchanged files in new backups are just links to old backups, and do not occupy space. Any old backup can be deleted at any time without compromising the others. It can be used to provided a "yesterday's files" service to users (both locally and exported as a read-only samba share...). To restore, just copy the files from the backup area.
amanda apt-get install amanda-client amanda-server It is a network backup system. It can do full and incremental backups. You can have a backup server which handles the storage and various backup clients that send the files to backup to the server. It takes some studying to set up. To restore: it has its own tool.
You can schedule these dumps to be made one hour before the time you make backups.
To save the list of installed packages and the answer to configuration questions:
dpkg --get-selections > pkglist debconf-get-selections > pkgconfigTo restore:dpkg --set-selections < list debconf-set-selections < pkgconfig apt-get dselect-upgradeIf you do this, they you only need to backup /etc, /home, /usr/local, /var.To save the contents of a MySQL database:
mysqldump name-of-database gzip > name-of-database.dump.gzTo restore:zcat name-of-database.dump.gz mysql
crontab -eAs root: add a file in one of the /etc/cron.* directories. In cron. hourly,daily,weekly,monthly you put scripts. In the other directories you put crontab files (man 5 crontab). If the system is turned off during normal maintainance hours, you can do two things:
For scheduling one-shot tasks, use at(1):
- Change /etc/crontab to use different maintanance hours
- Install anacron (it's installed by default in ubuntu)
$ at 17:40 echo "Please tell Enrico that the lesson is finished" mail efossnet@dream.edu.et ^D
Start at step 1 and go to 2 or 3 if/when you actually need it. (credits to sto@debian.org: he's the one from which I heard it for the first time, said so well).
- First, you manage to do it yourself
- Then, you document it
- Then, you automate it
- rkhunter, chkrootkit
- checksecurity
- debsecan
- tiger
Therefore, if the terminal looks like it got stuck, try hitting ^Q.
- ^C: interrupt (sends SIGTERM)
- ^\: interrupt (send SIGQUIT)
- ^D: end of input
- ^S: stop scrolling
- ^Q: resume scrolling
Problems found yesterday and today:
Problem: mail to efossnet@dream.edu.et is accepted only if sent locally. Reason:
$ host -t mx dream.edu.et Host dream.edu.et not found: 3(NXDOMAIN)Solution: tell dnsmasq to handle a MX record also for dream.edu.et:mx-host=dream.edu.et,smtp.dream.edu.et,50The problem not solved with the previous solution. Reason: postfix was making complaints which mentioned localhost as a domain name. Solution: fixed by changing 'myhostname' in main.cf to something different than localhost. Note: solved by luck. Investigate why this happened.
there is no way to tell squid to use another proxy for SSL connections: it only does them directly
if you want to configure evolution to get mail from /var/mail/user, you need to explicitly enter the path. It would be trivially easier if evolution presented a good default, since it's easy to compute. It would also be useful if below the "Path" entry there were some text telling what path is being requested: the mail spool? the evolution mail storage?
In Evolution: IMAP or IMAPv4r1? What is the difference? Why should I care?
apt-get --print-uris doesn't print the URIs if the package is in the local cache, and there seems to be no way to have it do it.
in /etc/apache2/sites-available/default, is the NameVirtualHost * directive appropriate there? It gets in the way when using 'default' as a template for new sites. Otherwise, one can add a new (disabled) site that can be used as a template for new sites instead of default.
the default comments put by crontab -e are not that easy to read.
Next.