Jacob Adams: What to Do When You Forget Your Root Password
Forgetting your root password would initially seem like a problem requiring
a full re-install, one that you can t easily recover from without wiping
everything away.
Forgetting your user password can of course be solved by changing it as root,
as in the following, which changes the password for user
but only the Changing Root s Password with Sudo
This one is probably obvious, but if you have a user with the ability to use
jacob:
# passwd jacob
root user can change their own password,
so you need to somehow get root access in order to do so.
Changing Root s Password with Sudo
This one is probably obvious, but if you have a user with the ability to use
sudo, then you can change root s password without access to the root
account by running:
$ sudo passwd
which will reset the password for the root account without requiring the
existing password.
Boot Directly to a Shell
Getting root access to any Linux machine you have physical access to
is surprisingly simple.
You can just boot the machine directly into a root shell without any access
control, i.e. passwords.
Why You Should Always Encrypt Your Storage1
To boot directly to a shell you need to append the following text to
the kernel command line:
init=/bin/sh
(You could use pretty much any program here, but you re putting your system into a weird state doing this, and so I d recommend the simplest approach.)
GRUB
GRUB will allow you to edit boot parameters on startup using the e
key. You ll then be presented with a editor2 that you can
use to change the kernel command line by appending to the linux line.
E.g. If your editor looks like this:
        load_video
        insmod gzio
        if [ x$grub_platform = xxen ]; then insmod xzio; insmod lzopio; fi
        insmod part_gpt
        insmod ext2
        search --no-floppy --fs-uuid --set=root abcd1234-5678-0910-1112-abcd12345678
        echo    'Loading Linux 6.1.0-21-amd64 ...'
        linux   /boot/vmlinuz-6.1.0-21-amd64 root=UUID=abcd1234-5678-0910-1112-abcd12345678 ro  quiet
        echo    'Loading initial ramdisk ...'
        initrd  /boot/initrd.img-6.1.0-21-amd64
Then you would add init=/bin/sh like so:
        load_video
        insmod gzio
        if [ x$grub_platform = xxen ]; then insmod xzio; insmod lzopio; fi
        insmod part_gpt
        insmod ext2
        search --no-floppy --fs-uuid --set=root abcd1234-5678-0910-1112-abcd12345678
        echo    'Loading Linux 6.1.0-21-amd64 ...'
        linux   /boot/vmlinuz-6.1.0-21-amd64 root=UUID=abcd1234-5678-0910-1112-abcd12345678 ro  quiet init=/bin/sh
        echo    'Loading initial ramdisk ...'
        initrd  /boot/initrd.img-6.1.0-21-amd64
Once you ve edited it you can start your machine with Ctrl+x, as you can
see from the prompt text under the editor.
Raspberry Pi cmdline.txt
On a Raspberry Pi you ll want to append the above to only line of the
cmdline.txt file on the boot partition of the SD card.
This is the first partition of the disk, the one that is FAT32.
You ll need to do this on another machine, since if you had root access
to edit cmdline.txt you could also just change your password.
As it is a FAT32 partition on an SD card, it should be editable on any other
machine that supports SD cards.
E.g. If your cmdline.txt looks like this
console=serial0,115200 console=tty1 root=PARTUUID=fb33757d-02 rootfstype=ext4 fsck.repair=yes rootwait quiet
Then you would add init=/bin/sh like so:
console=serial0,115200 console=tty1 root=PARTUUID=fb33757d-02 rootfstype=ext4 fsck.repair=yes rootwait quiet init=/bin/sh
Mount Read / Write
Since you re replacing the init process
of the machine with a shell, no other processes will be running.
Also, your root filesystem will be mounted read-only,
as init is expected to remount it read-write as needed.
# mount -o remount,rw /
Change Root Password
Once you ve remounted the root filesystem, all that s needed is to
run the passwd command.
# passwd
Since you re running the command as root you won t need to provide your
existing password, and will only need to type a new password twice.
Now of course you simply need to remember that password in order to
ensure you don t need to do this again.
Reboot Safely
You now cannot follow the standard reboot process here, as you re only running
one process.
Therefore it s important to put your root filesystem back into read-only before
powering off your machine:
# mount -o remount,ro /
Once you ve done that you just need to hold down the power button until the
machine completely powers off or pull the plug.
And then you re done! Boot the computer again and you ll have everything
working as normal, with a root password you remember.
-
Not that this is the only reason, anyone with physical access to your machine could also boot it into another operating system they control, or just remove your storage device and put it into another computer, or probably other things I m not thinking of now. You should always encrypt your devices.
-
The editor uses emacs-like keybindings. The manual includes a list of all the options available.
$ sudo passwd
root access to any Linux machine you have physical access to
is surprisingly simple.
You can just boot the machine directly into a root shell without any access
control, i.e. passwords.
Why You Should Always Encrypt Your Storage1
To boot directly to a shell you need to append the following text to
the kernel command line:
init=/bin/sh
(You could use pretty much any program here, but you re putting your system into a weird state doing this, and so I d recommend the simplest approach.)
GRUB
GRUB will allow you to edit boot parameters on startup using the e
key. You ll then be presented with a editor2 that you can
use to change the kernel command line by appending to the linux line.
E.g. If your editor looks like this:
load_video
insmod gzio
if [ x$grub_platform = xxen ]; then insmod xzio; insmod lzopio; fi
insmod part_gpt
insmod ext2
search --no-floppy --fs-uuid --set=root abcd1234-5678-0910-1112-abcd12345678
echo 'Loading Linux 6.1.0-21-amd64 ...'
linux /boot/vmlinuz-6.1.0-21-amd64 root=UUID=abcd1234-5678-0910-1112-abcd12345678 ro quiet
echo 'Loading initial ramdisk ...'
initrd /boot/initrd.img-6.1.0-21-amd64
Then you would add init=/bin/sh like so:
load_video
insmod gzio
if [ x$grub_platform = xxen ]; then insmod xzio; insmod lzopio; fi
insmod part_gpt
insmod ext2
search --no-floppy --fs-uuid --set=root abcd1234-5678-0910-1112-abcd12345678
echo 'Loading Linux 6.1.0-21-amd64 ...'
linux /boot/vmlinuz-6.1.0-21-amd64 root=UUID=abcd1234-5678-0910-1112-abcd12345678 ro quiet init=/bin/sh
echo 'Loading initial ramdisk ...'
initrd /boot/initrd.img-6.1.0-21-amd64
Once you ve edited it you can start your machine with Ctrl+x, as you can
see from the prompt text under the editor.
Raspberry Pi cmdline.txt
On a Raspberry Pi you ll want to append the above to only line of the
cmdline.txt file on the boot partition of the SD card.
This is the first partition of the disk, the one that is FAT32.
You ll need to do this on another machine, since if you had root access
to edit cmdline.txt you could also just change your password.
As it is a FAT32 partition on an SD card, it should be editable on any other
machine that supports SD cards.
E.g. If your cmdline.txt looks like this
console=serial0,115200 console=tty1 root=PARTUUID=fb33757d-02 rootfstype=ext4 fsck.repair=yes rootwait quiet
Then you would add init=/bin/sh like so:
console=serial0,115200 console=tty1 root=PARTUUID=fb33757d-02 rootfstype=ext4 fsck.repair=yes rootwait quiet init=/bin/sh
Mount Read / Write
Since you re replacing the init process
of the machine with a shell, no other processes will be running.
Also, your root filesystem will be mounted read-only,
as init is expected to remount it read-write as needed.
# mount -o remount,rw /
Change Root Password
Once you ve remounted the root filesystem, all that s needed is to
run the passwd command.
# passwd
Since you re running the command as root you won t need to provide your
existing password, and will only need to type a new password twice.
Now of course you simply need to remember that password in order to
ensure you don t need to do this again.
Reboot Safely
You now cannot follow the standard reboot process here, as you re only running
one process.
Therefore it s important to put your root filesystem back into read-only before
powering off your machine:
# mount -o remount,ro /
Once you ve done that you just need to hold down the power button until the
machine completely powers off or pull the plug.
And then you re done! Boot the computer again and you ll have everything
working as normal, with a root password you remember.
-
Not that this is the only reason, anyone with physical access to your machine could also boot it into another operating system they control, or just remove your storage device and put it into another computer, or probably other things I m not thinking of now. You should always encrypt your devices.
-
The editor uses emacs-like keybindings. The manual includes a list of all the options available.
init=/bin/sh
e
key. You ll then be presented with a editor2 that you can
use to change the kernel command line by appending to the linux line.
E.g. If your editor looks like this:
load_video
insmod gzio
if [ x$grub_platform = xxen ]; then insmod xzio; insmod lzopio; fi
insmod part_gpt
insmod ext2
search --no-floppy --fs-uuid --set=root abcd1234-5678-0910-1112-abcd12345678
echo 'Loading Linux 6.1.0-21-amd64 ...'
linux /boot/vmlinuz-6.1.0-21-amd64 root=UUID=abcd1234-5678-0910-1112-abcd12345678 ro quiet
echo 'Loading initial ramdisk ...'
initrd /boot/initrd.img-6.1.0-21-amd64
init=/bin/sh like so:
load_video
insmod gzio
if [ x$grub_platform = xxen ]; then insmod xzio; insmod lzopio; fi
insmod part_gpt
insmod ext2
search --no-floppy --fs-uuid --set=root abcd1234-5678-0910-1112-abcd12345678
echo 'Loading Linux 6.1.0-21-amd64 ...'
linux /boot/vmlinuz-6.1.0-21-amd64 root=UUID=abcd1234-5678-0910-1112-abcd12345678 ro quiet init=/bin/sh
echo 'Loading initial ramdisk ...'
initrd /boot/initrd.img-6.1.0-21-amd64
Ctrl+x, as you can
see from the prompt text under the editor.
Raspberry Pi cmdline.txt
On a Raspberry Pi you ll want to append the above to only line of the
cmdline.txt file on the boot partition of the SD card.
This is the first partition of the disk, the one that is FAT32.
You ll need to do this on another machine, since if you had root access
to edit cmdline.txt you could also just change your password.
As it is a FAT32 partition on an SD card, it should be editable on any other
machine that supports SD cards.
E.g. If your cmdline.txt looks like this
console=serial0,115200 console=tty1 root=PARTUUID=fb33757d-02 rootfstype=ext4 fsck.repair=yes rootwait quiet
Then you would add init=/bin/sh like so:
console=serial0,115200 console=tty1 root=PARTUUID=fb33757d-02 rootfstype=ext4 fsck.repair=yes rootwait quiet init=/bin/sh
Mount Read / Write
Since you re replacing the init process
of the machine with a shell, no other processes will be running.
Also, your root filesystem will be mounted read-only,
as init is expected to remount it read-write as needed.
# mount -o remount,rw /
Change Root Password
Once you ve remounted the root filesystem, all that s needed is to
run the passwd command.
# passwd
Since you re running the command as root you won t need to provide your
existing password, and will only need to type a new password twice.
Now of course you simply need to remember that password in order to
ensure you don t need to do this again.
Reboot Safely
You now cannot follow the standard reboot process here, as you re only running
one process.
Therefore it s important to put your root filesystem back into read-only before
powering off your machine:
# mount -o remount,ro /
Once you ve done that you just need to hold down the power button until the
machine completely powers off or pull the plug.
And then you re done! Boot the computer again and you ll have everything
working as normal, with a root password you remember.
-
Not that this is the only reason, anyone with physical access to your machine could also boot it into another operating system they control, or just remove your storage device and put it into another computer, or probably other things I m not thinking of now. You should always encrypt your devices.
-
The editor uses emacs-like keybindings. The manual includes a list of all the options available.
console=serial0,115200 console=tty1 root=PARTUUID=fb33757d-02 rootfstype=ext4 fsck.repair=yes rootwait quiet
console=serial0,115200 console=tty1 root=PARTUUID=fb33757d-02 rootfstype=ext4 fsck.repair=yes rootwait quiet init=/bin/sh
init is expected to remount it read-write as needed.
# mount -o remount,rw /
Change Root Password
Once you ve remounted the root filesystem, all that s needed is to
run the passwd command.
# passwd
Since you re running the command as root you won t need to provide your
existing password, and will only need to type a new password twice.
Now of course you simply need to remember that password in order to
ensure you don t need to do this again.
Reboot Safely
You now cannot follow the standard reboot process here, as you re only running
one process.
Therefore it s important to put your root filesystem back into read-only before
powering off your machine:
# mount -o remount,ro /
Once you ve done that you just need to hold down the power button until the
machine completely powers off or pull the plug.
And then you re done! Boot the computer again and you ll have everything
working as normal, with a root password you remember.
-
Not that this is the only reason, anyone with physical access to your machine could also boot it into another operating system they control, or just remove your storage device and put it into another computer, or probably other things I m not thinking of now. You should always encrypt your devices.
-
The editor uses emacs-like keybindings. The manual includes a list of all the options available.
# passwd
# mount -o remount,ro /
root password you remember.
- Not that this is the only reason, anyone with physical access to your machine could also boot it into another operating system they control, or just remove your storage device and put it into another computer, or probably other things I m not thinking of now. You should always encrypt your devices.
- The editor uses emacs-like keybindings. The manual includes a list of all the options available.
 A short status update of what happened on my side last month. A broken
gcovr in Debian triggered a bit of busy work but 0.39.0 came out
nicely nevertheless. We also reduced build time quiet a bit in phosh
and phoc.


 This blog has become a bit quiet
 Visit any GitHub project page, and the first thing you see is something that looks like this:
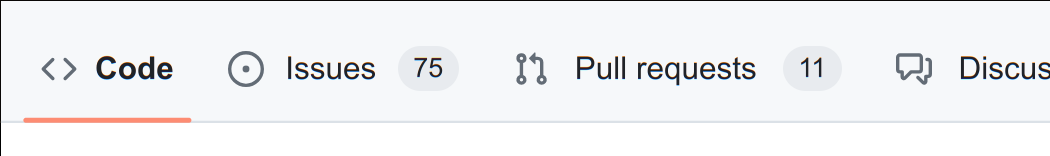 Code , that s fairly innocuous, and it s what we came here for.
The Issues and Pull Requests tabs, with their count of open issues, might give us some sense of how active the project is, or perhaps
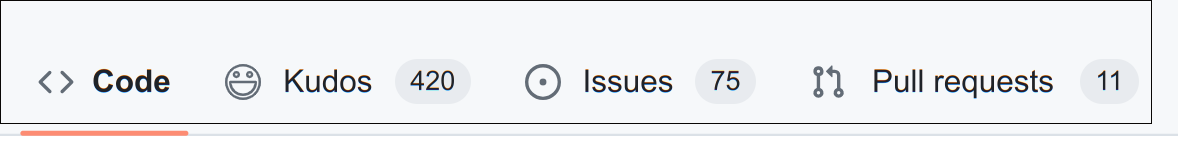 My conception of this is that it would, essentially, be a kind of yearbook , that people who used and liked the software could scribble their thoughts on.
With some fairly straightforward affordances elsewhere to encourage its use, it could be a powerful way to show maintainers that they are, in fact, valued and appreciated.
There are a number of software packages I ve used recently, that I d really like to say a general thanks, this is awesome! to.
However, I m not about to make the Issues tab look even scarier by creating an issue to say thanks, and digging up an email address is often surprisingly difficult, and wouldn t be a public show of my gratitude, which I believe is a valuable part of the interaction.
 Fira Mono
 Commit Mono