Search Results: "ed"

28 October 2011

Raphaël Hertzog: Debian joins Dropbox s officially supported platforms along with Fedora and Ubuntu

If you checkout Dropbox s Linux download page, you will see that Debian packages are provided. Up to a few days ago, they only provided packages for Ubuntu and Fedora. I m glad to see that packaging nautilus-dropbox for Debian and being in touch with them due to this led to this result. Another positive outcome is that the version 0.7.0 now ensures the origin of the downloaded binaries with GPG.

7 comments Liked this article? Click here. My blog is Flattr-enabled.

Matthew Garrett: Feeding the trolls

A few years ago I got up on stage and briefly talked about how the Linux community contained far too many people who were willing to engage in entirely inappropriate behaviour, how this discouraged people from getting involved and how we weren't very good at standing up against that sort of behaviour. Despite doing this in front of several hundred people, and despite the video of me doing so then being uploaded to the internet, this got me a sum total of:
Which is, really, what you'd expect, right? The internet seems intent on telling me otherwise:

Well, she didn't do herself any favors by talking at conferences about women in tech, or setting up a feminist movement. If you wanted to attract abuse, that's a good way to go about it. It should be expected.
(Source)

MikeeUSA is a troll. He has no means to actually harm anyone, and he does it purely for the lulz.

Thus, MikeeUSA trolled a woman, and she took the bait. I just don't get why this is news, I've been trolled before, I don't get a news story.

(Source)

I was going to start a rant about how this behavior is encouraged by the macho men online, but this was just one guy harassing her. "Due to harassment" reads as due to harassment from the community, but she gave in to one idiot. She let him win.
(Source)

The full comment thread has rather more examples. If you stand up and say anything controversial, you should expect abuse. And if you let that abuse change your behaviour in any way, you've let the trolls win.

These attitudes are problematic.

The immediate assumption underlying such advice is that the degree of abuse is related to what you've said, not who you are. I'm reasonably visible in the geek world. I've said a few controversial things. The worst thing that's happened to me has been Ryan Farmer deciding to subscribe me to several thousand mailing lists. Inconvenient, but not really threatening. I haven't, for instance, been sent death threats. Nobody has threatened to rape me. And even if they had done, I wouldn't need to worry too much - there's a rather stronger track record of violent antifeminism being targeted at women than men.

I don't have to worry about this kind of thing. That means I don't get to tell other people that they should have expected it. Nor do I get to tell them that they should ignore it, or that if they don't call the police then they have no grounds to complain. And nor does anyone else.

The trolls don't win because someone decides that getting out of the tech business is more appealing than continuing to face abuse. The trolls win because we consider their behaviour acceptable and then blame the victim for inviting them in the first place. That needs to change.

[1] It was justifiably pointed out that saying all this while standing on stage next to a mostly naked guy wearing a loincloth with a raccoon tail covering his penis may have weakened my message somewhat.

comment count unavailable comments

Matthew Palmer: rsync for LVM-managed block devices

If you ve ever had to migrate a service to a new machine, you ve probably found rsync to be a godsend. It s ability to pre-sync most data while the service is still running, then perform the much quicker sync the new changes action after the service has been taken down is fantastic. For a long time, I ve wanted a similar tool for block devices. I ve managed ridiculous numbers of VMs in my time, almost all stored in LVM logical volumes, and migrating them between machines is a downtime hassle. You need to shutdown the VM, do a massive dd netcat, and then bring the machine back up. For a large disk, even over a fast local network, this can be quite an extended period of downtime. The naive implementation of a tool that was capable of doing a block-device rsync would be to checksum the contents of the device, possibly in blocks, and transfer only the blocks that have changed. Unfortunately, as network speeds approach disk I/O speeds, this becomes a pointless operation. Scanning 200GB of data and checksumming it still takes a fair amount of time in fact, it s often nearly as quick to just send all the data as it is to checksum it and then send the differences.1 No, a different approach is needed for block devices. We need something that keeps track of the blocks on disk that have changed since our initial sync, so that we can just transfer those changed blocks. As it turns out, keeping track of changed blocks is exactly what LVM snapshots do. They actually keep a copy of what was in the blocks before it changed, but we re not interested in that so much. No, what we want is the list of changed blocks, which is stored in a hash table on disk. All that was missing was a tool that read this hash table to get the list of blocks that had changed, then sent them over a network to another program that was listening for the changes and could write them into the right places on the destination. That tool now exists, and is called lvmsync. It is a slightly crufty chunk of ruby that, when given a local LV and a remote machine and block device, reads the snapshot metadata and transfers the changed blocks over an SSH connection it sets up. Be warned: at present, it s a pretty raw piece of code. It does nothing but the send updated blocks over the network , so you have to deal with the snapshot creation, initial sync, and so on. As time goes on, I m hoping to polish it and turn it into something Very Awesome. Patches Accepted , as the saying goes.
  1. rsync avoids a full-disk checksum because it cheats and uses file metadata (the last-modified time, or mtime of a file) to choose which files can be ignored. No such metadata is available for block devices (in the general case).

Russell Coker: Capabilities vs SE Linux

In December 2010 a paper was published by Robert N.M. Watson and Jonathan Anderson from the Cambridge University and Ben Laurie and Kris Kennaway of Google about the Capsicum capabilities system [1]. It seems that the aim of the project is to allow systems that need privileges briefly when they start (such as tcpdump) a safe method of dropping privs. The main project page is here [2]. The focus of the paper is on the Chromium web browser and six different ways of constraining the Chromium sandbox are compared. For the SE Linux comparison they claim 200 lines of code changes as of Fedora 15, in Fedora 16 I couldn t find a Chromium package, so I presume that they mean 200 lines of SE Linux policy (I am not aware of anyone modifying the Chromium source for SE Linux). They note that SE Linux doesn t support separating different sandboxes, while it would be possible to have each sandbox be assigned a different MCS sensitivity label to separate them that option would be unwieldy enough that they are essentially correct in this regard. For SE Linux systems running the MLS policy the correct thing to do would be to run multiple copies of Chromium at different levels to access different sensitivity levels of data, this would normally be done by polyinstantiating the home directory. One thing to note however is that there is no requirement that only one security method be implemented. I can t think of any technical reason why it would be impossible to run SE Linux and Capsicum on the same system. SE Linux could constrain daemons and restrict the access to Capsicum services while Capsicum could be used to give minimum privileges to parts of Chromium. I m not sure that such a combination would offer anything that the MLS users would desire, but it seems that everyone else (the vast majority of computer users) would be served well by a combination of SE Linux and Capsicum. It s disappointing that the paper didn t mention Posix 1003.1e capabilities, but given the lack of use that Posix capabilities get that s understandable. It s also disappointing when someone develops something new and different nowadays and doesn t provide a virtual machine image for it. Installing and configuring something that requires application and kernel changes is a lot of work and most people who are idly curious about the technology won t go to the effort. By today s standards it s not that difficult to share a 1GB filesystem image via Bittorrent.

Andrew McMillan: In which an obscure conundrum is exposed

Some time ago someone reported issues accessing cpan.catalyst.net.nz a little peculiar and puzzling at the time, but we put it down to some weird DNS cache issues and moved on. Turns out the problem is a DNS one, though not what we were thinking at the time:
$ host -t aaaa mail.catalyst.net.nz
mail.catalyst.net.nz has IPv6 address 2404:130:0:10::40:0
2404:130:0:10::40:0 == 2404:0130:0000:0010:0000:0000:0040:0000
$ echo $((0x24)).$((0x04)).$((0x01)).$((0x30))
36.4.1.48
So somewhere, some crappy device is getting a bunch of bytes back when it asks DNS for the address of something, and then it's taking the first four of them and calling that the IP address. Kudos to David Clarke for spotting the actual problem.

27 October 2011

Axel Beckert: Conkeror usable on Ubuntu again despite XULRunner removal

Because of the very annoying new Mozilla release politics (which look like a pissing contest with the similar annoying Google Chrome/Chromium release schedule), Ubuntu kicked out Mozilla XULRunner with its recent release of 11.10 Oneiric. And with XULRunner, Ubuntu also kicked out Conkeror and all other XULRunner reverse dependencies, too. Meh. Sparked by this thread on the Conkeror mailing list, I extended the Debian package s /usr/bin/conkeror wrapper script so that it looks for firefox in the search path, too, if no xulrunner* is found, and added an alternative dependency on firefox versions greater or equal to 3.5, too. From now on, if the wrapper script finds no xulrunner but firefox in the search path, it calls firefox -app instead of xulrunner-$VERSION to start Conkeror. With the expection of the about:-page showing the orange-blue Firefox logo and claiming that this is Firefox $CONKEROR_VERSION , it works as expected on my Toshiba AC100 netbook running the armel port of Ubuntu 11.10. From version 1.0~~pre+git1110272207-~nightly1 on, the Conkeror Nightly Built Debian Packages will be installable on Ubuntu 11.10 Oneiric again without the need to install or keep XULRunner version from Ubuntu 11.04 Natty. For those who don t want to use the nightly builds, I created a (currently still empty) specific PPA for Conkeror where I ll probably upload all the conkeror packages I upload to Debian Unstable.

Jaldhar Vyas: Sal Mubarak 2068

[India at night] Wishing the entire Debian community worldwide a happy and prosperous Gujarati New Year (Vikram Samvat 2068 called Shobhan.) The picture above, is one that's been making the rounds of the Indian blogosphere. It purports to be a NASA satellite image of India on Diwali (which was last night.) Actually it is a composite of several night shots taken over a period of a few years. Also the red dots are people who have been injured by fireworks and the green dots those immobilized by the ingestion of too much baraphi and halwa. But I could be wrong about that. I've had some terrific news these past few days but alas I'm not at liberty to divulge it just yet...

MJ Ray: RISE Faces Demutualisation Threat at EGM

Photo of UWE Bristol

UWE Frenchay, Bristol: Venue of the RISE EGM

The RISE co-op is the sole shareholder in the Social Enterprise Mark CIC and its members have been called to an Extraordinary General Meeting during the lunch break of next Tuesday s Knowing and Growing conference at UWE Bristol. The RISE board has proposed Four Special Resolutions that would dissolve the co-op and transfer all assets as windfalls to the SEM CIC and a trust, ignoring RISE Ltd s Memorandum of Association. software.coop is calling on other RISE members to attend the EGM and oppose this demutualisation attempt. Update: dissolved but not demutualised (see below) RISE is constituted as a common ownership co-op and its Memorandum of Association contains a clause that directs the assets to be transferred to another common ownership social enterprise organisation if the co-operative is dissolved. However, unlike the CIC asset lock, there is no independent regulator enforcing it and, unlike in many co-ops, there has been no requirement for new members to pledge to obey the RISE common ownership clause at an individual level and there has been no member education about common ownership in the last three years. This demutualisation is the wrong solution for RISE because: software.coop will vote against the demutualisation, in favour of social enterprise, and calls on other RISE members to show solidarity with the co-operative and common ownership social enterprise movements. Update 2 November: rise has announced its dissolution but they ve got to give further consideration to where the assets go because the demutualisation resolutions were defeated. I fear that they ll still try some way to bail out the Social Enterprise Mark despite the rejection, but I hope they ll do the right thing and give the assets to good common ownership social enterprise like the RISE Memorandum of Association requires.

Russell Coker: Dual SIM Phones vs Amaysim vs Contract for Mobile Phones

Currently Dick Smith is offering two dual-SIM mobile phones for sale in Australia. One is the LG T510 for $99, but it only supports GSM on each SIM. This might be a good phone for someone who needs to receive both work and personal calls and doesn t want to carry two phones, but the lack of 3G support is a major limit on what can be done with the phone. The other phone is the Huawei U8520 which supports 3G on one SIM and GSM on the other. It costs $249, runs Android 2.2, has a 320*480 display, and a 3.2 megapixel camera. For comparison the LG Optimus One is a single-SIM phone with similar specs that only costs $179 from TeleChoice, so there is a 40% price premium to pay for a dual-SIM phone. When I first heard about dual-SIM phones (before they were commonly and cheaply available in Australia) I had thought that it would be a good option for using a cheap 3G broadband SIM along with a SIM for voice calls from one of the cheaper pre-paid mobile companies. But the helpful guy at Dick Smith informed me that Amaysim offers good pre-paid deals for voice and data [1]. With 10G of data quota to be used in one year for $100 and reasonable rates on voice calls it should be easy to keep under $200 per annum if you don t use many calls. Rene Cunningham has described how to use a pre-paid data-only plan on the Optus network with VOIP for most outbound calls [2]. To do that he is paying $30 every 6 months to keep his old number for inbound calls for which he gets $30 of credit, with Amaysim you can pay $10 every 3 months to get the same result with $40 per annum call cost instead of $60. As Amaysim are on the Optus network the result should be the same as long as Amaysim have enough capacity for IP data transfer. Rene uses an iPhone but the same result can be achieved with an Android phone. If by using VOIP the cost of running a phone on Amaysim was reduced to something like $160 per annum (with a possibly optimistic aim of $20 per annum for outbound VOIP calls) then over two years that could save $376 over a $29 per month contract. A Virgin $29 contract includes a Sony Ericsson Xperia X10 which is a fairly nice phone if you can deal with the short battery life and the fact that it s locked to Android 2.1. An Xperia X10 can be bought on Ebay for less than $376 but the hassle of setting up VOIP and Amaysim will be more effort than it s worth to save $100 over two years. A couple of my relatives have phone contracts that are about to expire. I m not going to set them up on VOIP as it s too much effort for too little benefit and the dual-SIM phone really isn t an option. I will recommend Virgin contracts with Xperia X10 phones or Amaysim with their existing phones (2yo smart phones that are still quite usable).

Michal Čihař: GePeS 0.1.0

After finalizing DOF Calc 0.1.0 yesterday, I've decided to push new version of GePeS as well. The update utilizes new Meego loader, so application should start much faster, add azimuth calculation for sun (set, rise and current) as well as compass is utilized for showing this azimuth. You can check all new features on screenshots page. New version is currently available in git and tarballs, binary version will be in Nokia store as soon it passes QA tests there.

Filed under: English Meego 0 comments Flattr this!

Russell Coker: Donating old Hardware

On a recent visit to my local e-waste disposal place I noticed an open PC on the top of the pile with a pair of DIMMs that were begging to be removed. I also noticed three PCI Ethernet cards that were stacked in a manner that made them convenient to grab possibly some nice person deliberately placed them so someone like me could take them. The DIMMs turned out to be 3G of DDR2-800 RAM and were regarded as good by Memtest86+ a nice upgrade for one of my test systems that previously only had 1G of RAM. If you have old hardware to dispose of then please try to take the RAM to your local computer users group meeting. In any such gathering there s always someone who wants old RAM, anything better than PC-133 will find good home unless it s very small (128M sticks of DDR-266 and 256M sticks of anything faster probably won t get any interest). RAM is small and light so you can carry it in your pocket without inconvenience. Ethernet cards of all vintages are in demand due to people reusing old desktop systems as routers and PCIe video cards are in great demand, PCI and PCIe cards are small enough that it s usually not a great inconvenience to transport them. Hard drives larger than about 100G are in demand as are ATX power supplies, these are really inconvenient to transport unless you travel by car. For computer systems, anything that can use DDR2-800 RAM will probably be of use to some member of a computer users group, if you offer it on the mailing list then you can expect that someone will want to collect it from you at your home or a meeting. There are organisations such as Computerbank that take donations of old hardware and make systems for disadvantaged people [1], it s worth considering them if you have hardware to dispose of. But for me the hardware I use every day is quite close to the minimum specs for donations that Computerbank will accept so there s no possibility of me discarding systems that are useful to them. I ve created a page listing hardware that I need, if anyone in my area has such hardware that they don t need then please let me know [2].

26 October 2011

Mike (stew) O'Connor: Bye Bye G+

Well, when I got an invite to try G+, I decided to make my first foray into social networking sites since friendster. It was mildly interesting while it lasted, however it seems that it is over for me now. I tried to use the name "Mike (stew) O'Connor" as I do on my gpg key. This caused my accounted to get flagged as violating their "real names" policy. I can't help but to feel a little offended that they think they know what my name is better than I do. I have a bit of a unique situation with my name. Pretty much NOBODY calls me "Mike" or "Michael" save a few people from my childhood. Its been this way for more than half of my life. My wife only ever has called me "stew". My two year old knows my name is "stew" but doesn't know my name is also "Mike". If I meet somebody new, I always introduce myself as "stew". All my clients call me stew... The instructions on google plus tell you "To help fight spam and prevent fake profiles, use the name your friends, family or co-workers usually call you.", So when my account was initially flagged. I tried changing my name to "Stew O'Connor". My account was "pending review" and I was still able to post and reply and the like. After review, my account was suspended, some of my privacy settings were changed, and I cannot change them back. Out of the 60 or so people that added me on G+, only one of them should ever be referring to me as "Mike". When someone calls me Mike that isn't one of the handful of people that "should" be calling me "Mike", my brain immediately puts them in the "oh, you don't know me very well" category. Oh well, Google, amazingly, you don't know me very well. After explaining to someone "oh, no you really should call me stew like everyone else", you say "No, I'd rather just not talk to you", now you are just being a jerk. Now I guess I have a retort to people that use the phrase which I find so annoying: "GIYF". Update: I appealed to change my name to Stew O'Connor which was denied, then appealed to change my name to Mike O'Connor which was also denied. I guess I was supposed to use "Michael" or something? Being denied "Mike", I deleted my suspeneded G+ account, feeling extra flouncy, chnaged by default search engine to duckduckgo.com.

Kai Wasserb ch: comScore/Nedstat: a larger Phish market

You might have read my recent post about an open redirect on WEB.DE's homepage. Now, as it turns out, the spread of this particular bug is far wider, than I first thought. After posting the previous story, I was surprised, how long it's taking to fix the bug. Then I remembered, that the domain for the redirect wasn't web.de but ui-portal.de. Now, knowing that WEB.DE is owned by United Internet doesn't make it that suspicious, but I was intrigued enough to check what the DNS said about the domain. And, as it turns out, the domain points to an IP owned by comScore/Nedstat:
$ dig @85.214.73.63 wa.ui-portal.de
; <<>> DiG 9.7.3 <<>> @85.214.73.63 wa.ui-portal.de
; (1 server found)
;; global options: +cmd
;; Got answer:
;; ->>HEADER<<- opcode: QUERY, status: NOERROR, id: 51273
;; flags: qr rd ra; QUERY: 1, ANSWER: 2, AUTHORITY: 3, ADDITIONAL: 3
;; QUESTION SECTION:
;wa.ui-portal.de.               IN      A
;; ANSWER SECTION:
wa.ui-portal.de.        10      IN      CNAME   wa-ui-portal-de.sitestat.com.
wa-ui-portal-de.sitestat.com. 30 IN     A       77.72.113.50
;; AUTHORITY SECTION:
wa-ui-portal-de.sitestat.com. 83 IN     NS      glns03.sitestat.com.
wa-ui-portal-de.sitestat.com. 83 IN     NS      glns02.sitestat.com.
wa-ui-portal-de.sitestat.com. 83 IN     NS      glns01.sitestat.com.
;; ADDITIONAL SECTION:
glns01.sitestat.com.    24      IN      A       77.72.113.10
glns02.sitestat.com.    24      IN      A       77.72.115.10
glns03.sitestat.com.    24      IN      A       87.249.105.10
;; Query time: 63 msec
;; SERVER: 85.214.73.63#53(85.214.73.63)
;; WHEN: Wed Oct 26 14:27:54 2011
;; MSG SIZE  rcvd: 202
All that is missing now, to confirm everything, is a whois for 77.72.113.50, which shows Nedstat B.V. as the owner (Nedstat is a part of comScore since 2010). That was, when I realized, that there are probably a lot more sites offering such links, and as a search for inurl:ns_url=http shows (I'm not yet linking to a result page, but you can look it up yourself, of course), that assumption was correct. There are some big names like Siemens or the Bertelsmann Stiftung, using the click-tracking service by Nedstat, returned by the search. That is a problem, as links looking like they're pointing to a trustworthy site/domain have a high potential for being clicked. Most people won't notice the open redirect, especially not, if the attacker took some time to design a target page, that looks like the original (most likely for phishing) or let the redirect point directly at some installer for malicious software or both. I've informed Siemens and the Bertelsmann Stiftung too, but I can't inform every affected website operator, so I've informed comScore/Nedstat directly and hope, they'll fix the issue in a timely manner. And not less important: inform their customers immediately.

Michal &#268;iha&#345;: New DOF Calc version

I've been doing some updates to DOF Calc in last days and today I decided it's time to push new it to public. The application has been switched to dark theme (which seems to be preferred one) and got working settings module. This means you can now configure list of cameras, lenses and apertures it offers, so that only choices you really use will be show. New version is currently available in git and tarballs, binary version will be in Nokia store as soon it passes QA tests there. Besides that, application got new homepage with screenshots (what is true for GePeS as well).

Filed under: English Meego 0 comments Flattr this!

Ingo Juergensmann: Roundcube doesn't work anymore because of suhosin

Well, yesterday out of nothing my webmailer roundcube started to refuse to work. At least as I remember it. For some reasons reloading the Inbox just showed the "Loading..." message on the screen, but there was no list of mails anymore. Funny enough other folders do actually work as before. But anyway, doing an update did not help and improve anything. (I really don't know whether I updated before or after because of the first occurence of this issue.) There's an entry in syslog when loading the Inbox folder:
Oct 26 07:24:59 muaddib suhosin[32432]: ALERT - Include filename ('http://www.gnu.org/s/hello/manual/automake/ ?.php') is an URL that is not allowed (attacker '127.0.0.1', file '/usr/share/roundcube/program/include/iniset.php', line 110
This lead to bug #1488086 in the Roundcube issue tracker which states:
This messages made me wonder why suhosin thinks there's an include going on. Line 111 of iniset.php shows: include_once("$filename.php"); It seems like roundcube wants to include what is displayed in the subject, which happens to be a url - and suhosin legitimately blocks this attempt. In short, I can send an email to a user on a suhosin protected mail server and make his inbox unavailable. Needless to say, the user cannot delete this email himself via RoundCube. In my case, I had to delete the email file on the server to make roundcube show the inbox again.
In Debian there's bug #619411 that is related to PATH setting in iniset.php, but I'm not sure if this is really related to #1488086 in the Roundcube issue tracker and my problem? However, disabling suhosin doesn't seem the right way to "solve" this issue and the trac issue tracker suggests a security related problem. Anyway, I filed this as bug #646675 in Debian, waiting for the bug number. But when someone else knows some quick fixes or something I can try, please speak up! :-) UPDATE: It seems as if some mail triggered this issue like reported in the Roundcube ticket. After filtering my mails with Iceweasel, I'm being able to read my Inbox now again.

Jose Luis Rivas Contreras: and issues on vim with $TERM= screen

Because of tmux I run with $TERM= screen instead of my regular rxvt-unicode, but I had a big issue with VIM because of this, it kept writing and F\n and H\n each time I pressed <end> and <home> keys respectively. I finally found the way to solve this, making VIM use $TERM= xterm internally writing this on my ~/.vimrc:
if &term == "screen"
set term=xterm
endif
So, this way, even in my servers without XTerm installed (but ncurses-term) I can use VIM as I m used to.

Russ Allbery: Review: Scrum and XP from the Trenches

Review: Scrum and XP from the Trenches, by Henrik Kniberg
Publisher: InfoQ
Copyright: 2007
ISBN: 1-4303-2264-0
Format: Trade paperback
Pages: 127
For those not already familiar with it, Scrum is a project management methodology that's most often seen in the agile software development community. It attempts to do for project management what agile techniques do for software development (and, other than test-driven development, I think is more useful than most of agile). I'm not going to explain it here in detail, but if you do software development or project management of software-style projects (including integration and computing infrastructure), it's worth your attention. It provides some nice techniques for dealing with some of the banes of technical projects, particularly constantly changing requirements and the difficulties of estimates. Scrum and XP from the Trenches is subtitled "How we do Scrum" and is exactly what it says on the tin. It is a fairly detailed description of how Crisp (an agile Java development company in Sweden) does Scrum (with a little discussion of Extreme Programming). It doesn't explain what Scrum is, although it does provide a few pointers to resources if you've never heard of it (but this isn't the sort of book you'd be buying if you'd never heard of it). It also doesn't try to convince you that Scrum is wonderful, which is a nice trap to avoid. It gets right down to business and packs quite a bit of relentlessly practical content into a small number of pages. I've been doing Scrum for about a year, across two large projects, both times not entirely following the full Scrum model. Both times, most of the team was learning Scrum during the project. I've gone to some Scrum training and read a bit, largely on-line, but I haven't made an exhaustive study of it. I think I'm exactly the ideal audience for this book, although my guess is that people who have been doing Scrum for longer will also get something out of it. This is not an introduction; I don't think one is likely to get much benefit out of it without a couple of Scrum projects under one's belt so that one has a feel for the problems and failure modes. As Kniberg accurately points out, Scrum is a framework, not a precise rule set, and it can't be applied blindly in one situation using analysis from another. For that audience, though, this book is great. Kniberg has used Scrum in a variety of different situations and tried multiple solutions to many of its problems, so he can provide guidance not only on his preferred solutions but on the other solutions he's tried and why they don't work. I started taking extensive notes just a few pages in; it was exactly the book I needed to read for the full-project retrospective on how Scrum worked for a just-concluded work project, and for planning what changes we'll want to make for the next project. He goes through every step of the Scrum cycle and offers advice on each step, particularly for the sprint planning (which was extremely helpful). He then walks through release planning and advance estimation (one of the best parts of the book; I've seen the concept of a focus factor before, but this is one of the best and clearest explanations I've seen), talks about XP (Extreme Programming) techniques and testing, and then discusses how to coordinate multiple Scrum teams in a larger organization. The chapter on testing was the reason why I bought the book; the rest of the book lives up to it. As mentioned, my Scrum exposure is not broad, so Kniberg may just be following different orthodoxies. That said, he broke with the ones I was previously familiar with in some useful places. One is to attach a time unit to story points, something that I was told was close to anethema, but as presented here looks very useful. Another, not so much a break but an idea that I'd not encountered elsewhere, is downtime between sprints, an brilliant solution to a problem that I'd not even fully articulated but which had been plaguing our Scrum process. He also has some suggestions about communication that, while fairly obvious and common-sense stuff, still were things that hadn't occurred to me and that we should adopt. I paid for a hard-copy version of this book from Lulu because I like things like this on paper and am happy to support the author financially, but you can download a PDF file and read it for free from InfoQ and see whether it works as well for you as it did for me. If you're ramping up on Scrum, seeing some problems, and looking for good ideas on how to fix them, I highly recommend it. I'd love to read two or three more case studies like this to get some more perspectives on how to make Scrum work. The paper book will likely be making a circuit around our office to serve as fodder for our upcoming Scrum projects. Rating: 8 out of 10

Gunnar Wolf: Construcci n Colaborativa del Conocimiento , the book: Finally!

Finally! Last Friday, after two years worth of work, I finally got the first box of books for the Construcci n Colaborativa del Conocimiento (Collaborative Knowledge Construction) project I worked on as a coordinator together with Alejandro Miranda (pooka), and together with a large group of 11 authors: Translating over from the back cover text (and this is just a quick translation from me It reads better in Spanish ;-) ):
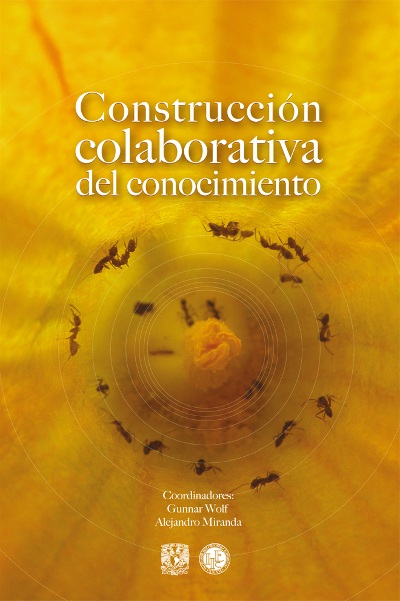
What defines us as humans is our ability, on one side, to
create knowledge, and on the other, to share or communicate it with our neighbors. Both features have worked together over tens of thousands of years, and, working together, have led the knowledge to transcend the individual, avoiding the need to rediscovery or reinvention of is already known. Sharing knowledge is what has taken our species to the dominant role it occupies today. But knowledge creation and sharing has seen a deep transformation in recent decades, thanks to the quick evolution of telecommunications, specially the massification of Internet and cellular telephony. We are transiting towards the so desired and at the same time so feared knowledge society. In this book, eleven authors from very different disciplinary backgrounds and geographic origins ellaborate on how a hyper-connected world has modified the basic rules of interaction in areas as diverse as artistic creation, social organizations, computer code development, education or the productive sector. This book is the result of a year worth of work for in the "Collaborative Construction of Knowledge" seminar, during which we
used the same new forms of knowledge production we have studied. The videos of the sessions, electronic participations and the full contents of this book are available under a permisive license at
http://seminario.edusol.info/seco3/
We will soon have the book ready in IIEc's e-store (which is mostly meant for national requests). I am also uploading the book to the lulu.com self-publishing service, and we are working on a epub-like edition. Right now it is still not available, but it should be there in some days. I will keep you posted. Meanwhile, the full contents can be read online at http://seminario.edusol.info/seco3

25 October 2011

Wouter Verhelst: diff6

There are six servers. They're meant to be used for the same purpose, and are mostly the same too, but not quite entirely. This being the case, mostly because of how they were maintained in the past: with cssh mostly, but it's inevitable that eventually there will be differences. So we're in the process of migrating them to puppet now. One of the things I need to do while doing that, however, is figure out what the differences are, and get rid of them where applicable. Differences such as, say, in the installed packages. Some of these servers have extra things installed, for a reason that isn't clear anymore, that others don't. So how does one figure out what the difference is? If this were two servers, I'd create a list of installed packages and use 'diff' on them. If there were three, I'd use 'diff3' instead. But if there are 6? Turns out that isn't too hard. First, of course, you need a list of packages installed on each individual host. Both rpm and dpkg can do this with a simple command line invocation. Assuming that's done, and the output is stored in files called installed-host1 through installed-host6, the procedure is:
$ comm -12 installed-host1 installed-host2 > installed-common
$ for i in $(seq 3 6)
> do
>   comm -12 installed-common installed-host$i > installed-tmp
>   mv installed-tmp installed-common
> done
And there, you now have a file "installed-common" containing everything which is installed everywhere. If you use "comm" or "diff" to compare that file against the installed-hostX files, you can easily see what the difference is. Granted, that doesn't give you the overview in just one file, but usually that's not really necessary. The 'installed-common' file contains the largest common denominator, which really is everything you need.

Kai Wasserb ch: Removal of sun-java6 and ElsterOnline

Reading Sylvestre Ledru's announcement, that sun-java6 was removed from the archives, I'd like to point out, that the recommended immediate purge of any binary packages built by sun-java6 should be postponed until you did have time to check, that important applications are working for you with the OpenJDK implementation. I need to retain sun-java6-plugin until upstream bug #588 for icedtea-plugin is fixed. If you have equal requirements (using ELSTER is required by tax law for me), make sure everything works with OpenJDK/IcedTea, otherwise you need to fetch the latest shipped version from snapshot.debian.org or install something directly from Oracle. Now, as security issues were mentioned in Sylvestre's post, I'm NOT recommending to have sun-java6-plugin running in your browser on default. Just switch the Java plugins before you really need it. For Iceweasel you can (de-)activate plugins in the add-on manager's plugin tab. Apart from that I'd recommend to not surf with any scripting or plugins active at all, NoScript! is a great way to do this conveniently.

Next.

Previous.