Search Results: "will"

30 March 2007

Patrick Winnertz: cipux as admintool for DebianEdu - a second test

Mh… I tested today again cipux, a admintool which one of the two tools which will replace our(Debian-edu) old admintool wlus . Since I dislike cipux a bit I regulary test it (the last time 1 week ago) and most of the errors I announced last week are fixed. But here the new report: The CipUX team fixed many issues I mentioned the last time… but there are still very hugh errors for productive software :S During the installation an the run of cipux_setup -s I recognised an error in the script: it uses wrong options for an other subinstallation script of cipux. The cookie handling is mostly fixed but in some scripts I still got this nice picture.. Apparently there are still hugh errors in the cookie handling. Furthermore it was not possible to edit the user data (e.g. full name, …. ) in the useradmin, it allows only to add users, resetting the passwords and deleting them. I think this is not enough for an admintool as we need it in debian-edu as a replacement for webmin/wlus. While searching for editing the users data I clicked on “Userselfadmin” and … got a error 404.. this script does not exist. So here is also no possibility to change the user details. I noticed something strange… there are many groups for users, e.g: assistant, teacher, tutor, … but I don’t find an group for students, quite strange. I asked upstream but until one week I got no answer. :S Because I was a bit frustrated I want to have a look on one of the other features of cipux.. the internetadmin. It should be possible to forbid a user or a complete group the internet access…this is the theorie. When I clicked on the internetadmin-button I got the cookie error mentioned above. Mh… so it is not possible to forbid your pupils to go into the internet. :S Another important feature we need for DebianEdu. Okay… the other things works. ;-) As a conclusion: Upstream works hard on fixing the errors I found last time, but there are still hugh errors which can be found by testing the software a bit. Atm I would suggest them to work on it and don’t upload to Debian-Edu since I think many features they have in theory doesn’t work properly and are not well tested.

Patrick Winnertz: cipux as admintool for DebianEdu - a second test

Mh… I tested today again cipux, a admintool which one of the two tools which will replace our(Debian-edu) old admintool wlus . I started last week to test it and most of the errors I announced last week are fixed. But here the new report: The CipUX team fixed many issues I mentioned the last time… but there are still very hugh errors for productive software :S During the installation an the run of cipux_setup -s I recognised an error in the script: it uses wrong options for an other subinstallation script of cipux. The cookie handling is mostly fixed but in some scripts I still got this nice picture.. Apparently there are still hugh errors in the cookie handling. Furthermore it was not possible to edit the user data (e.g. full name, …. ) in the useradmin, it allows only to add users, resetting the passwords and deleting them. I think this is not enough for an admintool as we need it in debian-edu as a replacement for webmin/wlus. While searching for editing the users data I clicked on “Userselfadmin” and … got a error 404.. this script does not exist. So here is also no possibility to change the user details. I noticed something strange… there are many groups for users, e.g: assistant, teacher, tutor, … but I don’t find an group for students, quite strange. I asked upstream but until one week I got no answer. :S Because I was a bit frustrated I want to have a look on one of the other features of cipux.. the internetadmin. It should be possible to forbid a user or a complete group the internet access…this is the theorie. When I clicked on the internetadmin-button I got the cookie error mentioned above. Mh… so it is not possible to forbid your pupils to go into the internet. :S Another important feature we need for DebianEdu. Okay… the other things works. ;-) As a conclusion: Upstream works hard on fixing the errors I found last time, but there are still hugh errors which can be found by testing the software a bit. Atm I would suggest them to work on it and don’t upload to Debian-Edu since I think many features they have in theory doesn’t work properly and are not well tested.

Rob Bradford: Dates translations

We will be making a release of Dates soon and so are on the look out for more translations. To submit a translation please file a bug on the OpenedHand Bugzilla against the Dates product. The latest code can be found in trunk.

29 March 2007

Matthew Garrett

Relating to my previous post, it's pretty clear that some people think of the Ubuntu code of conduct as (effectively) political correctness gone mad, and that anyone who thinks it's a good idea is clearly a wuss. nou suggested that this isn't inherently a bad thing, and that the range of different opportunities in Linux means that whether or not one distribution aims to be "fluffy" isn't really a problem.

I'd possibly go slightly further than that. We have basically three classes of people:
  1. People who won't work on "fluffy" projects
  2. People who won't work on "hostile" projects
  3. People who will work on pretty much any project, independent of the atmosphere
So, think of it as an optimisation tactic - projects benefit from having skilled people working on them. Do you gain more skilled people from being "fluffy" or "hostile"? Ubuntu's betting on the former, and my gut feeling is that that's the right answer. I don't have any reason to believe that the number of people in category 1 is terribly large, while I think category 2 is potentially much bigger.

Right now, I've got no evidence to back that up at all. But that's ok. In the long run, we'll probably get a better idea. If you think that Ubuntu's wrong to have chosen those criteria, then that's also ok. You're not obliged to be involved. Perhaps I'll be wrong, and the "hostile" projects will end up out-innovating the "fluffy" ones. But criticising the "fluffy" projects because they've dared to try something different? No, I don't think that's reasonable.

Benjamin Mako Hill: Dollar Books

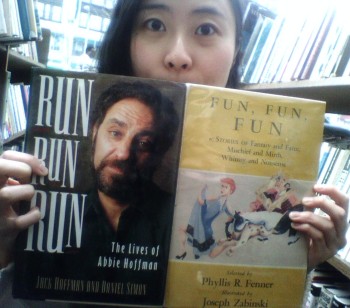
One of my favorite weekend activities is spending a Saturday afternoon going through the dollar book carts outside many New York and Boston area used book stores. It's not only because the books are cheap -- although I like that. The dollar book section is the great equalizer of bookstores. A neglected Dickens or Shakespeare can rub out against a discarded Mary-Cate and Ashley teeny-bopper quasi-romance novel. In the best cases, random shelving creates perfect (if unintuitive and ironic) pairs like Run Run Run about Abbie Hoffman and Fun Fun Fun about other youngsters -- a pair I found adjacent in a dollar book section last week.
/copyrighteous/images/run_fun_run.jpg
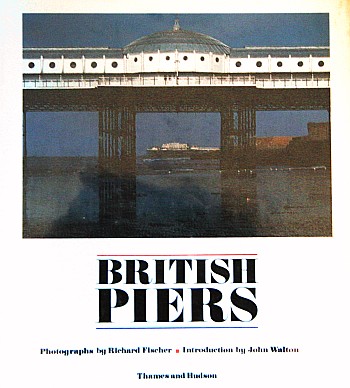
But you also get to meet books you will never meet in the bookstore sections you normally frequent. The dollar book section at the Strand has introduced me to a whole class of books with intriguing non-fiction sounding titles that I had pulled excitedly off the shelf only to find out that they were, in fact, novels. There are also the books with titles so good you suspect the book will be downhill from that point. The Complete Idiot's Guide To Being a Model (not, as one might expect, Becoming a model) and this guide to the British pierage are great examples.
/copyrighteous/images/british_piers.jpg

Pablo S. Torralba: ADN - Everything is connected

That's the company's slogan, whose offices we are working at. And I must admit it seems quite true.

Today, we have visited one of the data centers we are evaluating for our company hosting. It was a Tier 1 company, that is networking, connections... nothing special there. The amazing thing is one of the people we meet there was visiting Australia a year ago, and he is also a photograph passionated. I feel him a bit like a twin soul of mine as we are planning to visit Australia on our marriage trip where I will take a lot of pictures, of course. We were talking and he gave me some interesting URLs about his blog, travel agency and the like. So again everything seems connected, as Google knows so frightening well.

Anyway, we went there by motorbike which was a plus not connected to anything else, but too much funny in any case.

Matt Brown: My DPL Vote


- - -=-=-=-=-=- Don't Delete Anything Between These Lines =-=-=-=-=-=-=-=-
e0acebd2-71f1-4df8-ae4d-50355ad7aa81
[ 6 ] Choice 1: Wouter Verhelst
[ 6 ] Choice 2: Aigars Mahinovs
[ 3 ] Choice 3: Gustavo Franco
[ 3 ] Choice 4: Sam Hocevar
[ 2 ] Choice 5: Steve McIntyre
[ 4 ] Choice 6: Rapha l Hertzog
[ 1 ] Choice 7: Anthony Towns
[ 6 ] Choice 8: Simon Richter
[ 5 ] Choice 9: None Of The Above
- - -=-=-=-=-=- Don't Delete Anything Between These Lines =-=-=-=-=-=-=-=-
My rationale follows, if you care... I've been pondering how to vote for well over a week, and I'm still not entirely happy that the ballot I've chosen accurately expresses my wishes, but it's the best approximation of them that I can come up with at this time. My dilemma has two parts
  1. I don’t think the current office of the DPL is effective, due to how it is viewed by a significant proportion of the project (if not an outright majority), so regardless of how much I might like the goals and ideas proposed by an individual candidate I’m very pessimistic that being electing as DPL will actually bring those things to pass.
  2. Much of what will make a good DPL is about how a specific set of ideas and goals will be put into action, and how interpersonal relationships between the DPL and various parties will be managed. This comes down to the personal character, experience and leadership skills of the candidate While I can form some level of an opinion about each of these aspects from mailing list archives, and IRC, etc. I don’t really feel comfortable making judgements in these areas until I’ve actually met them in real life. Too many people come across badly in the (severely limited) online communication methods we use, and are actually very decent reasonable people in real life. Out of the candidates, AJ is the only one that I’ve ever actually met and talked to.
Given these problems, my first step in choosing how to vote was to eliminate those candidates who I will rank below NOTA based on their published platforms. I have nothing personal against any of these three people, but given the other possible candidates I think that we’d be better off having another election than just electing one of these three for the sake of it. That leaves five remaining candidates: *yawn* It’s made me tired writing all of that out. Maybe sometime soon I should explain in more detail exactly what parts of Debian’s governance model I think need changing or maybe I need to wait until I’ve achieved a few more technical things and gained enough respect before anyone will listen to my opinions…

Enrico Zini: remoteform-weird-error

TurboGears RemoteForm tip In case your RemoteForm misteriously behaves like a normal HTTP form, refreshing the page on submit, and the only hint that there's something wrong is this bit in the Iceweasel's error console:
Errore: uncaught exception: [Exception... "Component returned failure
code: 0x80070057 (NS_ERROR_ILLEGAL_VALUE) [nsIXMLHttpRequest.open]"
nsresult: "0x80070057 (NS_ERROR_ILLEGAL_VALUE)"  location: "JS frame ::
javascript: eval(__firebugTemp__); :: anonymous :: line 1"  data: no]
the problem can just be a missing action= attribute to the form. I found out after:
  1. reading the TurboGears remoteform wiki: "For some reason, the RemoteForm is acting like a regular html form, serving up a new page instead of performing the replacements we're looking for. I'll update this page as soon as I figure out why this is happening."
  2. finding this page on Google and meditating for a while while staring at it. I don't speak German, but often enough I manage to solve problems after meditating over Google results in all sorts of languages unknown or unreadable to me. I will call this practice Webomancy.

Russell Coker: questions regarding SE Linux

I just received a question about SE Linux via email. As I don't want to post private messages containing material that's globally useful I'll answer through my blog:

> other than strict and targeted policies......other policies like
> RBAC, MCS, Type Enforcement are also there....how are these policies
> implemented

The two main policies are the strict policy and the targeted policy. The strict policy is the earliest and was originally known as the sample policy (but was given the name "strict" after targeted was developed).

The strict policy aims to give minimal privileges to all daemons. The targeted policy aims to restrict the programs that are most vulnerable (network facing daemons) and not restrict other programs (for ease of use). There is currently work in progress on combining those policies so the person who compiles the policy can determine which features of strict they desire.

RBAC means Role Based Access Control. The strict policy assigns users to roles and the role then limits the set of domains that can be entered. For example the user_r role does not permit the sysadm_t domain so a user who is only permitted to enter the user_r role can not perform sys-admin tasks. Like many terms RBAC is used in different manners, some people consider that it means direct control by role (EG role user_r can not write to /dev/hda), while SE Linux has a more indirect use of roles (role user_r can not run programs in domain sysadm_t or any other domain that allows writing to type fixed_disk_device_t - the type for /dev/hda). You may consider that the strict policy supports RBAC depending on which definition of the term you use.

Generally the targeted policy is not considered to support RBAC, although if you consider a role to merely be a container for a set of accesses that are permitted then a SE Linux domain could be considered a in the RBAC sense. I don't think of targeted policy as being a RBAC implementation because all user sessions run in the domain unconfined_t which has no restriction. I think that to be considered RBAC a system must confine user logins.

Type enforcement is the primary access control mechanism for SE Linux. Every object that a process may access (including other processes) has a type assigned to it. The type of a process is known as a domain. The system has a policy database which for every combination of domain, type, and object class (which is one of dir, file, blk_file, etc - all the different types of object that a process may access) specifies whether the action is permitted or denied (default deny) and whether it is audited (default is to audit all denied operations and not audit permitted operations).

MCS is a confidentiality protection mechanism where each file has a set of categories assigned to it. The set may be empty, may contain all 1024 categories, or any sub-set. Each process has a set of categories that determines which files it may access. File access is granted if Unix permissions allow it, if the domain-type model allows it, and if MCS allows it (on an MCS system). I have just had an article on MCS published in Linux Journal.

MCS is an optional feature for people compiling Linux from source or for distribution vendors. For Red Hat Enterprise Linux, Fedora, and Debian the decision was made to include it, so the strict and targeted policies for those distributions include MCS.

There is another policy known as MLS. This is a policy build that comprises the strict policy plus Multi-Level Security. Multi-Level Security aims to give the highest confidentiality protection and comply with the LSPP (Labeled Security Protection Profile - roughly comparable to B1) Common Criteria certification. It would be possible to build a targeted policy with MLS but that wouldn't make sense - why have the highest protection of confidentiality with anything less than the highest protection of integrity?

As for how the policies are implemented, I'm not about to write a tutorial on policy writing for a blog post, I'm sure that someone will post a link to a Tresys or Fedora web page in the comments. ;)

> there r some packages of linux in which some changes has been made
> to support linux......for eg:- coreutils, findutils

That is correct. Every program that launches a process on behalf of a user at a different privilege user (EG /bin/login, sshd and crond) and every program that creates files for processes running in different domains (EG logrotate creating new log files for multiple daemons) needs to be modified to support SE Linux. Also ls and ps were modified to show SE Linux contexts as well as the obvious programs in coreutils.

> 'Z' is the new thing that have been added to most of the
> utilities......wherever I search I get the changes made only in few
> utilities like ps, mv, cp, ls
>
> Can u help me by giving all the changes made in each of the utilities.....

Unfortunately I can't. This has been identified as an issue and there is currently work in progress to determine the best way of managing this.
Gerfried Fuchs: Rhonda blogs

I think it's time to start blogging more often about this topic, and fill this section a bit more. I mean, Mermaids was a long time ago... And debconf in Mexico with my first try on skirts, getting rid of my beard and dying my hairs red is history in the meantime, too. So, what has happened in between... Well, there was of course the Regenbogenparade which I attended and which was nice. I even ordered a special t-shirt from a shop in Australia that I totally love. In summer I met up in Bratislava with a longtime friend from a MUD I played way back, and enjoyed running around in a skirt there, too. Gladly it was a sunny day. It was though... people back here in Vienna looked more awkward at me than in Bratislava. At least that was my impression... Had been to Extremadura for the i18n meeting which was quite nice. It was quite productive, even though I have to admit that I haven't done much on that front since. Even in Spain people didn't look that strange at my skirt as over here in Austria... At our company's Christmas party I got into a talk with a work colleague about the topic and she informed me that a former working colleague of us is starting with hormone treatment after the year change and if I'd fancy a meeting with him. I was quite happy about that offer so we arranged a meeting on December 23rd. It was a bit strange at first to address him as he, and we didn't know how to start talking because said working colleague was late, but after a while we talked about various things and even were finished with the more interesting topics when she finally appeared. We arranged to visit the next Trans-X meeting after the year change.
I left them for leaving home, but I wasn't able to catch my bus on time—the subway had serious problems. Well, I thought I might spend the night in the Flex so I called another working colleague who usually hangs out there about what was going on that evening, and interestingly he told me it was Gay Heaven night. I stopped believing in coincidence long ago... Anyway, was a nice evening all in all, they had a Christmas rabbit handing out "I love you" stamps with pink ink-pads. :) The Trans-X meeting wasn't too bad. It was some discussions about various topics. After a while my first shyness dropped a bit and I started to join in the discussion at some points. After the first started to leave I had some more direct talks with two of the women from there, one of them had mostly the same trip home as me so we talked on in the subway. A week later they had set a transgender weekend—no wonder, it was the weekend of the Rosenball. They were meeting in a cafe on Friday and I joined them, a bit less shy now that I at least knew some of the faces. Maria was quite ill and was sitting in her jacket within the cafe, shivering like hell... But all in all it was a nice meeting too, got to know some more nice people. I was a bit lazy from there on, didn't join another meeting... But another working colleague did invite me to the carnival party of his sister. I thought I could try a bit more than before, in the disguise of the carnival party, so I used a bra my former wife left behind, filled it with some socks, and put up some eye makeup (quite discreet, I hate overdone makeup already on natural females...) The light there wasn't the best, so they just saw my tall body at first. It took them a while to even notice the skirt, and only after I put off my long-sleeve they haven't noticed my breast. But well, I don't really blame them, my working colleague has announced me as a he, and given the low lights it's not too bad. Though, after the host noticed my breasts he asked if he could touch them and I even received a quite nice kiss from him. :D I stumbled upon the Gaia TG Guild on Gaia Online—a quite interesting web-based community. In general Gaia is filled with mostly kids, many of them immature, not able to spell and considering that even cool, but there are some quite special guilds that are lots of fun. But still, when I stumbled upon the TG Guild I was in awe of that such a thing could exist there. What I read made me feel totally happy and more confident on the path I'm having ahead of me. Last week I finally had been to an Trans-X meeting again, and Maria showed some quite interesting reportages about transsexual people—including one that was on TV just the day before about a 14 year old girl who is already on hormone treatment and has the absolute support from her family since she was 4 and confronted them with cutting "it" off when they don't allow her to wear skirts when going out, too. All the best to you, Kim! I so envy your strength... I'm sorry about the length of this entry—but I'm sick of people who tell me that I'm only playing it, or that I would hide... And I also see it as a chance to document my path for myself. I promise—the next entries will be more often and thus shorter.

Peter Van Eynde: modern times

A colleague at work got his 'final end of year bill' from his electricity supplier. In Belgium you pay every month an amount based on the guess of the supplier of your usage. Because , he claims, his new house is drying out, so requires less energy to heat up, he consumed about 20% less energy then last year so their estimate was too high. Good: he gets 400 back. Bad: the amount he has to pay a month goes up.

So he phones them up and asked why. The reason: the program to adjust the guess based on the usage of last year cannot handle a negative amount (you payed too much) so the program thinks the last estimate was 400 a month too low instead of too high, so it adjusts it upwards. Next year it will adjust it even more up :-).

Now I know that the ABS function in FORTRAN exists already since the late 1950's so I think the problem is not their programs, but that this is an easy way to get an interest-free loan out of people that don't watch their bill with a eye for details.

Miriam Ruiz: Free Software and Composer s Copyright Societies

We’re trying hard to include Frets on Fire in Debian. FoF is a really great game where you have to try to play a simulated guitar through your computer keyboard. The code is already GPL, and the developers are really nice and collaborative. The game consists of some code in python, some game data, graphics and so, and some songs, including a tutorial. The problem comes when we try to get the songs into Debian too. It seems that, for being able for someone to be something in the musical scene in Finland, they must sign an abusive contract with Teosto (Finish Composer’s Copyright Society, which AFAIK is a private organization), giving them exclusive rights on whatever songs you make, so you won’t be able to license any song at all without using a license that has been approved by them. More discussion here. This is wierd. Composer’s Copyright Societies should be there to help composers and artists, not to enslave them. For what I heard it’s not the only country in which that happens. Especially in Europe, the EU is extremelly protectionist to those matters, whether they do right or wrong, or whether they even go against the author’s will. Gosh, it’s the authors who should have the right to choose, not the mafias choose for them. In Spain I think it’s more or less the same, the SGAE seems to have the same attitude towards artists than Teosto. When will they realize they’re being anachronistic and unfair?

Russell Coker: death threats against Kathy Sierra

The prominent blogger and author Kathy Sierra has recently cancelled a tutorial at a conference after receiving death threats.

Obviously this is a matter for the police to investigate - and the matter has been reported to them.

It's also an issue that is causing a lot of discussion on the net. The strange thing is that a large portion of the discussion seems based on the idea that what happened to Kathy is somehow unusual. The sexual aspect of the attacks on Kathy is bizarre but campaigns of death threats are far from unusual in our society. The first post I saw to nail this is the I had death threats in high school blog entry. Death threats and campaigns of intimidation are standard practice in most high schools. After children are taught that such things are OK for six years straight it's hardly a surprise that some of them act in the same manner outside school!

But I don't expect anything to change. Columbine apparently didn't convince anyone who matters that there is a serious problem in high-schools, I don't expect anything else to.

I can clearly remember when I first heard about the Columbine massacre, a colleague told me about it and explained that he barracked for the killers due to his own experiences at high-school. While my former colleague probably had not given his statements much consideration, any level of support for serial-killers is something to be concerned about.

This is not to trivialise Kathy's experience. But I think that discussion should be directed at more fundamental problems in society instead of one of the symptoms. If the causes are not addressed then such things will keep happening.

28 March 2007

Neil Williams: Cross-building a rootfs

With updated cross-building toolchains and a much improved emdebian-tools package, work has finally started on actually building cross-built packages for Emdebian. Wookey has identified the first set - a usable rootfs. http://wiki.debian.org/EmdebianRootfs

Nineteen packages have been cross-built so far, from base-files and popt to util-linux and ncurses so I thought I'd make a note of how it has gone at this early stage. Packages, patches and build logs can be viewed at: http://www.emdebian.org/packages/search.php

Results:
======

1. CDBS cross-builds like a dream. No failures, no missing files, no misplaced files, no files Emdebian doesn't want (like changelogs and manpages). em_make replaces one makefile with a customised one and everything else falls into place. Fantastic.

2. debhelper packages generally cross-build quite well - as long as debian/rules sticks to actually using debhelper rather than creating bespoke rules that just do what dh_foo would have done anyway! (I then have to go behind them and remove the custom rules to get rid of manpages etc. when if the task had been left to dh_foo, em_make would have removed dh_foo automatically. Grrr.)

3. Packages built without CDBS or debhelper are an absolute PITA. I know it is a good exercise to build without "high-level" tools, but PLEASE, only put non-debhelper packages in the main archive if you really cannot have debhelper involved. It'd make my life SO much easier right now. :-)

4. Splitting out the translation files into individual, dedicated, packages one per language is having two related effects: there are a plethora of packages in the repository with only 19 source packages built; the size of the main binary packages has dropped substantially. Some translation packages are 30-60kb in size but in Debian, 12 maybe 30 of these are packaged inside the main binary or a similar combined _common package. Users get no choice, it's no translations or all translations. I cribbed the idea from OpenEmbedded and it's nice to see it paying off, even if it means that 'apt-cache search' listings will be at least an order of magnitude longer in Emdebian. (Sounds like a wrapper is needed.) Need to start testing 'langupdate' soon to make sure it can cope with keeping users up to date with translations of installed programs.

So far, haven't needed too many cache files to be used with ./configure --cache-file but I'm bound to meet those soon.

Overall, things are going well (famous last words).

Daniel Burrows: On emailing me.

Verizon has apparently decided that BOTH of my forwarding addresses, dburrows@debian.org and Daniel_Burrows@alumni.brown.edu, are actually spammers, and is randomly rejecting some emails sent to them. I have given Verizon as large a piece of my mind as they allow: they do not provide an email address, and instead put up a form where they graciously allow you to type a 70-character (!) message. This will presumably go straight into the bitbucket, but we'll see.

If you want to email me, please send mail directly to Daniel_Burrows@verizon.net.

Does anyone know of a broadband ISP serving Redmond that doesn't suck? As far as I know, my only alternative to the telephone monopoly is the cable monopoly.

MJ Ray: Online Banking: What works with GNU/Linux? (7)

Thanks again to all the updaters. Please, start lists for banks in other countries and tell me about them. If a list already exists for your country, consider sending updates there first. Added: Banca Popolare Etica, Caisses Populaires Desjardins, Caja Madrid, Caja de Segovia, Fortis Bank Belgium, KBC, netbank.de, Osuuspankki, PC Financial Master Card, Soci t G n rale, Sparebank 1-Gruppen, Storebrand Bank Updated: NatWest Andrew Donnellan suggested:
"Perhaps it would be useful to start a list of banks that *don't* work with Free Software as well so we can a) petition them, and b) boycott them until they make it work."
I'd prefer to keep this to a positive list for various reasons (including lawyer-fear, search engine rankings, rewarding the good and saying nothing if I've nothing nice to say). If a listed bank goes bad, it will show up as Removed. If you want to rant about how a bank screwed you, please use your own site. If I see it and like it, it will appear in one of my linkposts.

Kartik Mistry: Too hot

* Nearly boiling temperature here at Ahmedabad right now. Well, not that much but you can see.. * Like March Ending season, I am reviewing my all packages and doing updates daily 1 package. Hope that this will make things better :) I still need to steal time to answer PP questions :(

27 March 2007

Mark Brown: NIS and Network Manager in Debian etch

The version of NIS to be shipped with Debian 4.0 has support for Network Manager in ypbind, the program responsible for ensuring that NIS client systems can access a NIS server. Unfortunately Network Manager is targeted at client systems with dynamically assigned addresses and does not support some common network configurations, particularly static ones. When Network Manager is run on a computer with such a configuration it presents misleading information to NIS, causing NIS to think that it is not connected to a network and fail to connect to a server. In order to avoid these problems the version of NIS in etch disables Network Manager support by default but the configuration file with this change is not updated automatically on upgrade. To disable Network Manager support by hand edit the configuration file /etc/default/nis to add -no-dbus to YPBINDARGS: # Additional options to be given to ypbind when it is started.
YPBINDARGS=-no-dbus
Uninstalling the network-manager package if it is not in use will also resolve the problem. This also applies to the packages currently scheduled for release in the next version of Ubuntu (codenamed Feisty).

Martin-Éric Racine: I'm Thin, therefore I Can

Life sometimes goes in a funny direction, like a full circle d j vu: 20 years ago, I was studying Technology of Computerized Systems (a combination of electronics and programming). Now, 20 years later, I'm starting a dream job as the Business Development Manager of Artec Group and their core business is you guessed it exactly that. The really cool thing about Artec, from a Free Software advocate's point of view, is that they contribute firmware and drivers for their products to LinuxBIOS and the Linux kernel. At this point, my initial tasks will focus on marketing and selling Artec's flagship OEM product, the ThinCan. What is the ThinCan? Actually, you're already familiar with one iteration of the product: the Linutop is a branded ThinCan, delivered with a custom hardware configuration, plus custom casing artwork designed by Fr d ric Baille of Linutop SARL and loaded with Fred's favorite Xubuntu configuration. In the Linutop's case, their business model is to fill the market niche for a simple Internet surfing platform that fits 80% of average people's daily computing needs, so the hardware configuration they ordered reflects that. Still, as several readers of this blog noticed, the "Linutop" could make a fantastic thin client and, sure enough, that was the main purpose behind the ThinCan's original design; it sells well in the Fortune-500 market as an RDP client running under Windows CE. However, until recently, there simply wasn't much demand for a contemporary X11 terminal solution based on the ThinCan. That is, until LTSP took off, thanks to the contributions of Edubuntu and similar educational Linux distributions. Sure enough, someone spotted the opportunity and contacted Artec to order a branded ThinCan iteration with Etherboot and PXE support, which they call the Linuterm. By the way, for those who need a really cheap OEM thin client, I've got a great spring clearance offer for you:
Artec has about 500 pieces left of their older DBE60 ThinCan model, based on the AMD Geode SC2200, and we're selling them at 100 euro / piece, plus VAT and shipping.
The DBE60 is configured with three USB 1.1 ports, one parallel printer port, one 100baseT Ethernet port, one VGA port (up to 1024x768 @ 16bpp 60-85Hz or 1280x1024 @ 8bpp 60-75Hz) and one 1/8" stereo audio output jack. Its BIOS provides Etherboot support and its motherboard is populated with 64MB of RAM and 32MB of Stratoflash. It comes delivered with a European AC adapter. The Geode SC2200 is fully supported by the Linux kernel with the sole exception of a missing ALSA snd-scx200, but this could easily be ported from AMD's deprecated OSS driver and X.org support is provided by the "nsc" driver.
Minimum order size is 10 pieces. Contact me via my full name (unaccented, with one hyphen and one dot) at artecgroup.com quoting this special offer.
PS: someone was asking if that DBE60 special is also available in the aforementioned Fortune-500 configuration. It indeed is: add 16 euro / piece for the Windows CE 4.1 license with an RDP client.

Gustavo Franco: simple-cdd 0.3.0 is NEW!

Just uploaded simple-cdd 0.3.0 to experimental, as a simple-cdd user since Sarge days, I've helped a lot Vagrant with Etch support that required a huge amount of development due to the d-i and debian-cd changes. Thanks for those who helped us with testing and patches!

If you're lost, simple-cdd is a limited though relatively easy tool to create a customized debian-installer CD. It supports multiple install profiles for your CDD project (We can ask your user which to install, you can simple have one or preseed it); You can preseed the packages that will be installed as you can do using d-i; i18n support for those who want custom Debian localized images; multiarch support; postinst support for profiles; simple-cdd-profile udeb take care about extra packages installation, it doesn't need tasksel.

So say we all!

Next.

Previous.