Search Results: "ed"

7 March 2012

Petter Reinholdtsen: Debian Edu screencast: Mass creation of user accounts in Squeeze

One of the Debian Edu developers, Wolfgang Schweer, just created a screen cast documenting how to create a lot of new users in LDAP on Debian Edu Squeeze. The video is embedded here in quarter size, and also available from vimeo and download as a Ogg Theora file. Check it out below. <video controls="controls" height="184" id="gosa-mass-user-create-movie" preload="preload" width="256"> <source src="http://ftp.skolelinux.org/skolelinux/press/screencasts/2012-02-29-debian_edu_mass_create_user_accounts.ogv" type="video/ogg; codecs="theora, vorbis""> Download video as Ogg. </video>

Michal &#268;iha&#345;: Contest for phpMyAdmin books

Packt Publishing has offered phpMyAdmin to sponsor some coding contest with books. The contest is already running since Monday and we have first winner, but still, your chances are pretty high. So in case you are interested in having Mastering phpMyAdmin 3.4 for Effective MySQL Management, go ahead and check out the contest rules.

Filed under: English Phpmyadmin 0 comments Flattr this!

Dirk Eddelbuettel: RcppArmadillo 0.2.36

RcppArmadillo release 0..2.36 is now on CRAN. It contains just the changes from the new Armadillo release 2.4.4. The NEWS entry below summarises the changes.
0.2.36  2012-03-05
    o   Upgraded to Armadillo release 2.4.4
          * fixes for qr() and syl()
          * more portable wall_clock class
          * faster relational operators on submatrices
Courtesy of CRANberries, there is also a diffstat reports for 0.2.36 relative to 0.2.35 As always, more detailed information is on the RcppArmadillo page. Questions, comments etc should go to the rcpp-devel mailing list off the R-Forge page.

Steve Kemp: Continuous integration that uses chroots?

I'd like to setup some auto-builders for some projects - and theese projects must be built upon Lenny, Squeeze, Lucid, and multiple other distros. (i386 and amd64 obviously.) Looking around I figure it should be simple. There are a lot of continuous integration tools out there - but when looking at them in depth it seems like they all work in temporary directories and are a little different to how I'd expect them to be. Ultimately I want to point a tool at a repository (mercurial), and receive a status report and a bunch of .deb packages for a number of distributions. The alternative seems to be to write a simple queue submission system, then for each job popped from the queue run: Surely this wheel must already exist? I guess its a given that we have to find build-dependencies, and that we cannot just run "pbuilder *.dsc" - as the dsc doesn't exist in advance. We really need to run "make dependencies test build", or similar. Hudson looked promising, but it builds things into /var/lib/hudson, and doesn't seem to support the use of either chroots or schroots. ObQuote: "I feel like I should get you another sweater." - "Friends"

6 March 2012

Benjamin Mako Hill: Half the Battle Against DRM

As the free software and free culture movements have sat quietly by, DRM is now well on its way to becoming the norm in the electronic book publishing industry. The free culture movement has failed to communicate the reality of DRM and, as a result, millions of people are buying books that they won't be able to read when they switch to a different model of ebook reader in the future. They are buying books that will become inaccessible when the DRM system that supports them is shut down -- as we've already seen with music from companies including Wal*Mart, Yahoo, and Microsoft. They are buying books that require that readers use proprietary tools that lock them out from doing basic things that have always been the right of a book owner. Some anti-DRM advocates are, indirectly, part of this problem as they buy these books and turn to shady methods of stripping the DRM. Buying DRMed books is voting with your wallet for a system that criminalizes those that insist on living in freedom and will screw us all in the long run when DRM is the only choice we are offered and removing the DRM is difficult, unsafe, and illegal. Buying non-DRMed e-books is a more freedom-friendly alternative for those that, like me, are excited about not lugging kilograms of paper around our cities and the world. We can do this at "non-mainstream" publishers like Smashwords who explicitly reject DRM. Of course, the big ebook sellers like Amazon, and Barnes and Nobel, and Google all offer non-DRMed books. But none of the major ebook retailers explicitly reveal the DRM status of locked down books before purchase. On Amazon, there are some cryptic signs and signals that, if you understand them, suggest the absence of DRM. Google and Barnes and Nobel currently offer no way to know if a book is DRMed without buying it first and questions in their support forums go unanswered. It's hard to support non-DRM alternatives when we can't recognize them. It's hard to tell people to not buy DRM ebooks if we can't even tell them apart. Getting this message through to book buyers -- and perhaps even to ebook retailers -- seems like a critical first step.

Michal &#268;iha&#345;: Announcing Weblate

After about week of (not so heavy) development, I can announce availability of Weblate - web based translation tool with tight Git integration. The project was started because I was not happy with existing solutions (see my blog post) as all of them was missing some features I find useful. I started with quite simple definition:
Minimalistic web based translation with direct commit to git on each translation made. There is no plan in heavy conflict resolution as these should be primarily handled on git side.
Also the project started with defined list of features: Pretty much all of that is completed right now, however there will be definitely some issues which will need fixing. All important information about the project are available on it's website, the code is hosted on Github. If you are curious how it looks, you can try it out on demo server. You can login there with demo account using demo password or register your own user. Please give it some testing as I plan to deploy it on http://l10n.cihar.com/ pretty soon.

Filed under: Django English Weblate 5 comments Flattr this!

Mike Hommey: libgcc.a symbol visibility considered harmful

I recently got to rebuild an Android NDK with a fresh toolchain again, and hit an interesting problem. I actually had hit it before, but only this time I fully analyzed what s going on. [As a side note, if you build such a NDK, don't use mpfr 3.1.0, as there is a bug in the libtool it ships] Linking an application or a library pulls many things, that aren t part of the code being built. One of these many things is the libgcc static library. Part of libgcc consists in an implementation of the platform ABI. On Android systems, this means the ARM EABI. GCC, when compiling some instructions, will generate ABI calls. For example, integer divisions may call __aeabi_idiv. Consider the following minimized real world scenario:
$ echo "int foo(int a) return 42 % a; " > foo.c
$ arm-linux-androideabi-gcc -o libfoo.so -shared foo.c -mandroid
GCC will emit a call to __aeabi_idivmod for the % operation. With GCC 4.6.3, this function is in _divsi3.o under libgcc.a. That function itself calls __aeabi_idiv0, which lives in _dvmd_lnx.o under libgcc.a. When statically linking, ld will thus include foo.o, _divsi3.o and _dvmd_lnx.o, meaning it will include all functions from these object files. That is, foo, __divsi3, __aeabi_idiv, __aeabi_idivmod, __aeabi_idiv0 and __aeabi_ldiv0. And more than being included, these functions are exported, because symbol visibility in libgcc.a is default. So while we expect exporting foo from our library, we re actually exporting much more, including functions that just happened to be near the ones that our code (indirectly) uses. Now, let s say we want to build another library, using that foo function from libfoo:
$ cat > bar.c <<EOF
extern int foo(int a);
long long bar(long long a) return foo(a) % a;
EOF
$ arm-linux-androideabi-gcc -o libbar.so -shared bar.c -mandroid
(The code above has absolutely no meaning, it just triggers the same function calls as what I was getting in the actual real world case) When statically linking the above code, GCC will generate a call to __aeabi_ldivmod, which calls __aeabi_ldiv0, and many other things, directly or indirectly. When linking as above, nothing particularly nasty is going to happen. However, linking as above is actually wrong: the resulting library has an undefined reference to the foo symbol, and doesn t depend on libfoo. At runtime, if libfoo wasn t already loaded somehow, loading libbar would fail. The proper way to link is the following:
$ arm-linux-androideabi-gcc -o libbar.so -shared bar.c -mandroid -L. -lfoo
A feature of ELF static linking is that when it resolves undefined symbols, the linker will choose to use the first occurrence of a symbol it finds in the various objects and libraries given on its command line. So with the command line above, for each __aeabi_* symbol, it will first look in libfoo if there isn t one. And while __aeabi_ldivmod is not in libfoo, __aeabi_ldiv0 is (see above). So instead of including the code for __aeabi_ldiv0 from libgcc.a, it will call the copy from libfoo. This wouldn t be so much of a problem if __aeabi_ldiv0 wasn t a weak symbol. Enters faulty.lib. In the real world case, libfoo is loaded by the system dynamic linker, and libbar by faulty.lib. When resolving symbols for libbar, faulty.lib has to resolve libfoo symbols with the system linker, using dlsym(). On Android, dlsym() returns NULL for weak (defined) symbols, so faulty.lib can t resolve __aeabi_ldiv0. The real world case wasn t a problem with GCC 4.4.3 from the vanilla Android NDK because in that GCC version, __aeabi_ldivmod doesn t call __aeabi_ldiv0. This wouldn t happen if shared libraries wouldn t expose random platform ABI specific bits depending on what they use and depending on other symbols that happen to be in the same object files. A similar issue happened a little while ago on Debian powerpc because a shared library was exporting ABI specific bits. Even worse, the toolchain was assuming the symbols would come from libgcc.a and generated wrong relocations for these symbols. Update: Interestingly, the __aeabi_* symbols are hidden, in libgcc.a as provided on the Debian armel port.

Kartik Mistry: fonts-* migration

* We ve now done with big transition of Indic fonts from ttf-* naming to fonts-*. Debian-IN-Workers team now maintains around 61 packages. We ve also finished process of moving to Git from SVN along with this. Kudos to Vasudev, Muneeb and AbdulKarim for taking lead, help and pushing me hard for upload and testing. (31 packages upload on Sunday night = 62 times my GPG passphrase, not counting couple of wrong entries ;) )

Ian Wienand: Investigating the Python bound method

You work with Python for a while and you'll become familiar with printing a method and getting
<bound method Foo.function of <__main__.Foo instance at 0xb736960c>>
I think there is room for one more explanation on the internet, since I've never seen it diagrammed out (maybe for good reason!). An illustration of Python bound methods In the above diagram on the left, we have the fairly simple conceptual model of a class with a function. One naturally tends to think of the function as a part of the class and your instance calls into that function. This is conceptually correct, but a little abstracted from what's actually happening. The right attempts to illustrate the underlying process in some more depth. The first step, on the top right, is building something like the following:
class Foo():
      def function(self):
      	  print "hi!"
As this illustrates, the above code results in two things happening; firstly a function object for function is created and secondly the __dict__ attribute of the class is given a key function that points to this function object. Now the thing about this function object is that it implements the descriptor protocol. In short, if an object implements a __get__ function; then when that object is accessed as an attribute of an object the __get__ function is called. You can read up on the descriptor protocol, but the important part to remember is that it passes in the context from which it is called; that is the object that is calling the function. So, for example, when we then do the following:
f = Foo()
f.function()
what happens is that we get the attribute function of f and then call it. f above doesn't actually know anything about function as such what it does know is its class inheritance and so Python goes searching the parent's class __dict__ to try and find the function attribute. It finds this, and as per the descriptor protocol when the attribute is accessed it calls the __get__ function of the underlying function object. What happens now is that the function's __get__ method returns essentially a wrapper object that stores the information to bind the function to the object. This wrapper object is of type types.MethodType and you can see it stores some important attributes in the object im_func which is the function to call, and im_self which is the object who called it. Passing the object through to im_self is how function gets it's first self argument (the calling object). So when you print the value of f.function() you see it report itself as a bound method. So hopefully this illustrates that a bound method is a just a special object that knows how to call an underlying function with context about the object that's calling it. To try and make this a little more concrete, consider the following program:
import types
class Foo():
    def function(self):
        print "hi!"
f = Foo()
# this is a function object
print Foo.__dict__['function']
# this is a method as returned by
#   Foo.__dict__['function'].__get__()
print f.function
# we can check that this is an instance of MethodType
print type(f.function) == types.MethodType
# the im_func field of the MethodType is the underlying function
print f.function.im_func
print Foo.__dict__['function']
# these are the same object
print f.function.im_self
print f
Running this gives output something like
$ python ./foo.py
<function function at 0xb73540d4>
<bound method Foo.function of <__main__.Foo instance at 0xb736960c>>
True
<function function at 0xb73540d4>
<__main__.Foo instance at 0xb72c060c>
To pull it apart; we can see that Foo.__dict__['function'] is a function object, but then f.function is a bound method. The bound method's im_func is the underlying function object, and the im_self is the object f: thus im_func(im_self) is calling function with the correct object as the first argument self. So the main point is to kind of shift thinking about a function as some particular intrinsic part of a class, but rather as a separate object abstracted from the class that gets bound into an instance as required. The class is in some ways a template and namespacing tool to allow you to find the right function objects; it doesn't actually implement the functions as such. There is plenty more information if you search for "descriptor protocol" and Python binding rules and lots of advanced tricks you can play. But hopefully this is a useful introduction to get an initial handle on what's going on!

Russell Coker: SE Linux Status in Debian 2012-03

I have just finished updating the user-space SE Linux code in Debian/Unstable to the version released on 2012-02-16. There were some changes to the build system from upstream which combined with the new Debian multi-arch support involved a fair bit of work for me. While I was at it I converted more of them to the new Quilt format to make it easier to send patches upstream. In the past I have been a bit slack about sending patches upstream, my aim for the next upstream release of user-space is to have at least half of my patches included upstream this will make things easier for everyone. Recently Mika Pfl ger and Laurent Bigonville have started work on Debian SE Linux, they have done some good work converting the refpolicy source (which is used to build selinux-policy-default) to Quilt. Now it will be a lot easier to send policy patches upstream and porting them to newer versions of the upstream refpolicy. Now the next significant thing that I want to do is to get systemd working correctly with SE Linux. But first I have to get it working correctly wit cryptsetup. Related posts:
  1. SE Linux Status in Debian 2011-10 Debian/Unstable Development deb http://www.coker.com.au wheezy selinux The above APT sources.list...
  2. SE Linux Status in Debian 2012-01 Since my last SE Linux in Debian status report [1]...
  3. Debian SE Linux Status At the moment I ve got more time to work on...

5 March 2012

Vincent Bernat: Asynchronicity & Net-SNMP AgentX protocol

One of the best way to add SNMP support to an application is the use of AgentX protocol: an application can act as a subagent and handle requests from a master agent using AgentX protocol. The most widespread implementation for such a task is the one from Net-SNMP. TL;DR: An application asynchronously leveraging Net-SNMP AgentX implementation has many opportunities to get stuck when the master agent becomes temporarily unavailable. A mostly efficient workaround is to dedicate a master agent for AgentX and delegate MIB handling to a subagent.

Pinging the master agent Net-SNMP uses an event-based model. It also provides some synchronous functions but they are built on top of the asynchronous ones. It is shipped with its own event loop. Therefore, Net-SNMP AgentX protocol implementation seems a fine choice to add SNMP support to an event-based program, for example in Keepalived, a VRRP daemon and a monitoring daemon for LVS clusters. Unfortunately, an AgentX subagent is expected to check, at a regular interval, if the master agent is alive . This is handled automatically with Net-SNMP implementation as long as you call run_alarms() function which will call agentx_check_session():
/*
 * check a session validity for connectivity to the master agent.  If
 * not functioning, close and start attempts to reopen the session 
 */
void
agentx_check_session(unsigned int clientreg, void *clientarg)
 
    /* [...] */
    DEBUGMSGTL(("agentx/subagent", "checking status of session %p\n", ss));
    if (!agentx_send_ping(ss))  
        snmp_log(LOG_WARNING,
                 "AgentX master agent failed to respond to ping.  Attempting to re-register.\n");
        /*
         * master agent disappeared?  Try and re-register.
         * close first, just to be sure .
         */
        agentx_unregister_callbacks(ss);
        agentx_close_session(ss, AGENTX_CLOSE_TIMEOUT);
        /* [...] */
        if (main_session != NULL)  
            /* [...] */
            main_session = NULL;
            agentx_reopen_session(0, NULL);
         
        else  
            snmp_close(main_session);
            main_session = NULL;
         
      else  
        DEBUGMSGTL(("agentx/subagent", "session %p responded to ping\n",
                    ss));
     
 
This piece of code will end up calling (directly or indirectly) the following functions1 which are using agentx_synch_response():
  • agentx_send_ping()
  • agentx_open_session()
  • agentx_reopen_session()
  • agentx_close_session()
  • agentx_register()
  • agentx_unregister()
  • agentx_register_index()
  • agentx_unregister_index()
  • agentx_add_agentcaps()
  • agentx_remove_agentcaps()
agentx_synch_response() will synchronously wait for an answer from the master agent. Your event-based program will just sit here doing nothing while this happens. For example, keepalived may be unable to send VRRP probes resulting in some serious havoc in your cluster. Functions prefixed by agentx_ are not part of NetSNMP API and could therefore be rewritten to do their work asynchronously. Unfortunately, talk is cheap. Moreover, there exists other deep paths that will block a subagent. For example, the low-level connection to the master agent (using TCP or a Unix socket, but not with UDP) will use a blocking connect() call. It seems quite difficult to fix this. Here are some (partial) workarounds:
  • Call agentx_check_session() less often. The default interval is 15 seconds. Disabling it completely or using a very high value is not advised because this function is the only way to reestablish a connection to the master agent when it is, for example, restarted. Here is how to change the delay to 120 seconds:
    netsnmp_ds_set_int(NETSNMP_DS_APPLICATION_ID,
                       NETSNMP_DS_AGENT_AGENTX_PING_INTERVAL, 120);
    
  • Don t call agentx_check_session() if we know the master agent is alive. For example, if it just sent us a new request, no need to ping it. I have written a patch implementing such a workaround. The ABI is left untouched, therefore, you only need to recompile Net-SNMP libraries.
  • Use a lower timeout and no retry. By default, the timeout for synchronous requests is 1 second and a failed request will be retried 5 times. Because several synchronous functions are used in a row, you may be trapped for as long as 30 seconds with those settings. Here is how2 to disable the retry mechanism and to set the timeout to a very low value:
    static int
    snmp_setup_session_cb(int majorID, int minorID,
                  void *serverarg, void *clientarg)
     
        netsnmp_session *sess = serverarg;
        sess->timeout = ONE_SEC / 3;
        sess->retries = 0;
        return 0;
     
    void some_init_function()
     
        /* [...] */
        snmp_register_callback(SNMP_CALLBACK_LIBRARY,
           SNMP_CALLBACK_SESSION_INIT,
           snmp_setup_session_cb, NULL);
        /* [...] */


Unresponsive master agent Why is the master agent unresponsive? snmpd is also an event-based program and, trust me, there are a lot of places where it will become unresponsive. Here are two examples:
  • When using the pass or the pass_persist directive, Net-SNMP will block until the delegated command outputs a complete line.
    /* var_extensible_pass() in agent/mibgroup/ucd-snmp/pass.c */
    /*
     * valid call.  Exec and get output 
     */
    if ((fd = get_exec_output(passthru)) != -1)  
        file = fdopen(fd, "r");
        if (fgets(buf, sizeof(buf), file) == NULL)  
            fclose(file);
            wait_on_exec(passthru);
            /* [...] */
            continue;
         
        /* [...] */
        fclose(file);
        wait_on_exec(passthru);
        /* [...] */
     
    
  • DISMAN-PING-MIB implementation will just hang while pinging the remote host. If the host is down and you have requested 5 probes with a timeout of 1 second, snmpd will be unresponsive for 5 seconds. A similar problem exists with DISMAN-TRACEROUTE-MIB.

Minimal master agent More and more code is running in the main agent. You cannot expect it to not block. But we could add a minimal master agent to the mix: it will handle only a few MIB modules by itself while most MIB modules will be delagated to a complete agent running as a subagent. Your own subagent will connect to the minimal master agent. Schema showing the use of a minimal master agent It is quite easy to turn snmpd into a subagent: just use -X flag. We should also disable unwanted MIB modules for each agent with -I flag. For the minimal master agent, we only enable some modules. All other modules3 will be served by snmpd acting as a subagent.
$ MODS="snmp_mib,sysORTable,usmConf,usmStats,usmUser,vacm_conf,vacm_context,vacm_vars"
$ snmpd -Lsd -Lf /dev/null -u snmp -g snmp \
>   -C -c /etc/snmp/snmpd.master.conf \
>   -p /var/run/snmpd.master.pid \
>   -I $MODS
$ snmpd -Lsd -Lf /dev/null -u snmp -g snmp \
>   -p /var/run/snmpd.pid -X \
>   -I -$MODS
Access control configuration should be placed in /etc/snmp/snmpd.master.conf, as well as master agentx directive. Other directives (like pass, pass_persist, load, sysname, ) in /etc/snmp/snmpd.conf. The minimal master agent is very unlikely to block and while the ground cause is still here, it is now very much mitigated. You may extend this solution by splicing snmpd into several subagents: one handling safe modules, one handling pass and pass_persist stuff and a last one for unsafe modules (like DISMAN-PING-MIB).

  1. agentx_reopen_session() will call agentx_close_session() and agentx_open_session(). agentx_register() and the following functions will be called by those two functions.
  2. NETSNMP_DS_AGENT_AGENTX_TIMEOUT and NETSNMP_DS_AGENT_AGENTX_RETRIES variables are only used by the master agent, not by a subagent.
  3. Use snmpd -Dmib_init -H to get the list of modules. You may want to add smux module to the master agent.

Russell Coker: LUV Hardware Library

What is it? Last month I started what I am calling the LUV Hardware Library. It s a briefcase full of computer parts that are free to LUV members which I plan to bring to all LUV meetings [1]. The issue is that there is a lot of hardware which has no great value to people and is often excess to requirements but which is still somewhat expensive or difficult to obtain and thus transferring it from the people who don t need it to people who do provides a significant benefit to the recipient but no real cost to the donor. Currently my briefcase has a range of different types of DIMM, some PCI cards, some assorted cables, a laptop SATA disk, and a bunch of other random things. Most of the stuff has been in my spare parts pile for a year or two, but some of it has been donated by other people. What we Need The next thing we need is more packaging, anti-static bags for RAM and PCI cards, sealable bags for screws, and some way of storing motherboard batteries. In terms of hardware that can be donated one thing that would be really useful is SATA disks. I m sure that there are lots of people who have upgraded the storage of their computer and kept the old drive with no real chance of using it. But there are lots of people who need such disks, for example I ve been giving away a bunch of P4 systems which lack disks and are not cabled for IDE disks a supply of SATA disks would make them a lot more usable. Also any other random electronic stuff is of interest, including non-Linux things such as mobile phones (but only if not network locked). If you have something that s big or heavy to donate then contact me via email first. Other Options Computerbank does great work in rebuilding old PCs and selling them cheaply to worthy people [2], but most of the spare hardware I get is below the minimum specs that they will accept. I m not planning to compete with Computerbank in any way, I just want to provide a useful service to LUV members who want to upgrade their PC for free. I encourage other people to do the same at other LUG meetings! Related posts:
  1. Donating old Hardware On a recent visit to my local e-waste disposal place...
  2. Giving Away Hardware For the last few years I have been actively seeking...
  3. Shelf-life of Hardware Recently I ve been having some problems with hardware dying. Having...

DebConf team: DebConf12 Website online (Posted by Felix Delattre)

After using our small pre-website for some time now, we are very happy to announce the official website has gone live: http://debconf12.debconf.org Now it is the right time for you to get involved supporting the event or just enjoy the design and help us to spread the new website, f.e. by using our nice banners in the artwork section. Please stay tuned: Registration is going to be opened soon.
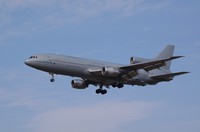
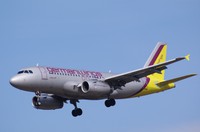
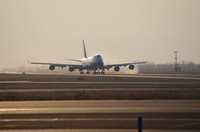
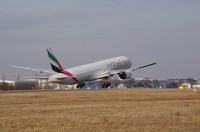
Michal &#268;iha&#345;: Ruzyn airport

During weekend, I had great opportunity not only to visit Prague Airport, but also to taste airspotting. As photography is my hobby, this was interesting experience, though I don't think it would be my favorite thing to capture. Anyway we could see some interesting places - L1011 TriStar KC1 from Royal Air Force, two Boeings 747-400F and Boeing 777-300. The Boeings being the biggest airplanes you can regularly see in Prague. So lets stop talking and here are few pictures:

Filed under: English Photography 0 comments Flattr this!

John Sullivan: Plus One

In mailing list discussions, I've noticed that the practice of replying "+1" to messages with which one agrees has become very widespread. I think this is interesting for a lot of reasons, such as what it shows about habits picked up in communicating via social network sites that grew out of e-mail percolating back to e-mail. We seem to have really grown to like this idea of "voting" for people's messages, and if there's no "Like" or "+1" button on their message, we'll make our own. (Likewise, apparently a person's name is no longer sufficient to indicate that one is addressing them in an e-mail -- am I right, @dear_reader?) The problem for me is that I have my venerable awesome e-mail client Gnus set to hide quoted text in messages by default with (add-hook 'gnus-article-prepare-hook (lambda () (gnus-article-hide-citation 1))), and it thinks that "+" is the start of a quoted line -- so it hides the "+1". While there's a certain poetic justice to that, it confuses me because it makes the message look empty, and someone could do something like "+1 I'm pregnant too", causing me to miss some very important news. The fix for this is to change the regexp pattern Gnus uses to decide if a line is a message quote or not. gnus-message-cite-prefix-regexp is built using message-cite-prefix-regexp, so I changed the value of the latter, removing the literal "+". I also found while investigating this that I already configure that variable in order to add "#>" which someone sometime during my 9 years of using Gnus must have used. The net result is (setq message-cite-prefix-regexp "\\([ ]*[-_.#[:word:]]+>+\\ [ ]*[]> ]\\)+"). (Note that some of those whitespace characters are tabs, which probably won't display properly here, but you can compare to the default value to see what I actually changed). +1?
Benjamin Mako Hill: Unhappy Birthday Hall of Shame

/copyrighteous/images/no_happy_bday.png I roll my eyes a little when I think that Unhappy Birthday is the document I have written that has been read by the most people. The page -- basically a website encouraging people to rat on their friends for copyright violation for singing Happy Birthday in public -- has received millions of page views and has generated tons of its own media (including a rather memorable interview of CBC's WireTap). At the bottom of the page I am listed, by name and email, as the "copyrighteous spokesman" for the initiative. And since the page has been online, I have received hate mail about it. Constantly. Since the email only goes to me, I thought it might be fun to share some of these publicly. All these messages are quoted verbatim but I have not included the senders' names. Be warned: the language is often salty. This email is years old now but it is probably still my favorite:
Atrocity and strife run rampant in this world. Babies are abandoned in dumpsters. Teachers molest students. Impoverished Indonesians make sneakers for pennies while the spoiled jackhole in the 30-second commercial makes millions for sinking a three-pointer and smirking at the camera. Forms of religion are interpreted as to compel people to strap explosives to their chest and board buses full of innocents. Boss Tweeds embezzle and get severance pay while John Q. Workingman gets put out on the street when the corporation goes belly up. Out of all these indignities and countless others I haven't the time to mention, why do you make it your personal crusade to assist in the flagrant persecution of family restaurants for partaking in the time-honored tradition of singing "Happy Birthday"? God forbid these foul brigands bend copyright law in order to bring a smile to somebody's face. Food for thought...without the accompanying song.
Many others strike a defiant, if less poetic, tone:
Good luck! There are millions of us who refuse to accept the ridiculous "copyright" on Happy Birthday. If Time Warner were an ethical company rather than a greedy megacorp they would do something truly special and release it into the public domain. There are some things in this world more important than money.
Quite a few people notice that my last name is Hill and suspect that I must be related to the Hill sisters who originally penned the song. I'm not, to my knowledge, although since Time Warner bought the rights, it's not clear it would matter:
I am writing to just let you know how disappointed I am that a large corporation and others (like the HILL family) are making $2 million plus for a song that was created over 100 years ago with noone knowing who created the lyrics! None of us at our place of employment could believe this and we certainly won't encourage people to send money to ASCAP. It is a shame that ASCAP license fees aren't used to pay more to up-and-coming artists who I'm sure need this money alot more than Time Warner. We all plan to sing Happy Birthday MORE now in public places and if anyone asks if it is copyrighted we will say "of course not". Maybe this way the song will not die out completely as more and more other "birthday" songs are being sung. It would also be nice if your website cited whose opinion is writing the piece and your obvious conflict of interest.
Or another:
Is it a coincidence that your last name is the same as the last name of the authors of the song "Happy Birthday?" You seem to have a personal monetary motive for your work with the "grassroots project" you call Unhappy Birthday, and if you do not, your concern is misplaced all the same. Whom do you imagine your campaign serves? And do you realize whom it harms? I do not question the illegality of performing the copyrighted song publicly. And you are correct that most of the public is not even aware that the song is under copyright. I think the harm done to Time Warner and its associates by such public performances is far outweighed by the joy created when the much-loved happy tune is shared. I urge you to ask yourself why you think the immortal Hill sisters wrote the song in the first place. It was not to put more money Time Warner's pocket. It was, I would argue, for the sake of the song itself and the happiness it brings when performed (publicly or otherwise). Please consider siding with the children and the artists; let the lawsuits alone.
Some people suspect the site may be satire, but include insults and and attacks just in case it isn't:
I'm trying to figure out if your Unhappy Birthday site is meant to be in jest. If so Rofl, and congrats on a hilarious site. If you're actually serious, then fuck you Nazi cunts and your corporate butt buddies. Thank you for your time.
Or these two alternatives (each were separate emails):
If this is a joke then it's rather funny. However if this website is serious then you're a fucking idiot. Get a life!!!! if it is a form of protest, then THANK YOU! if it is not, then screw you all!
One memorable piece of mail was from someone who knew of me from my activities in the free software and free culture communities and had a hard time reconciling my work there with the high protectionist website:
I was quiet surprised to see your name and email address at the bottom of the home page of the site Unhappy Birthday. The site claims that you are their spokesman. Is this correct? I do not understand... You have all this Open Source/ Free Software background and then this site that defends one of the most controversial copyright issues??? Do you really mean this? Do you want to help Time Warner?
I've also received probably half a dozen mails that offer some sort of support! For example, this person liked the website -- and even wanted to buy one of our t-shirts -- but objected to our logo:
I was going to buy one of your products from your Unhappy Birthday Shop at CafePress but there's a problem. I hate emblems that uses human skulls in them. Being a member of ASCAP I really do support your cause but I can't buy a product that I would never wear.
And many people are simply confused asking something like this one:
So I saw the unhappy birthday site and I'm just a little confused. Is this a joke or a serious thing?
I usually reply and explain that I have tried to ensure that the site describes the legal situation around Happy Birthday honestly and correctly. That said, the vast majority of messages I receive are unequivocal. Like this email that I received last week addressed to "you anti-free speech fascists":
         __
        /  \


 __  __      __
/  \/  \    /  \
                \
                  
                 /
                 \
                  /
\                /
                 
                 
Half an hour later, the author followed up with a English version of the same message, set to the tune of happy birthday. You might think that getting insulted and flipped off by confused people on the Internet might get me down. It doesn't! I made Unhappy Birthday because I thought that the fact that something as important to our culture as Happy Birthday could be owned was outrageous. Every piece of hate mail means that somebody else -- almost always somebody who isn't a "copyfighter" or a free culture geek -- is now upset about the current state of copyright too. Sure, Unhappy Birthday makes me a tiny bit sad about people's ability to recognize satire. But it makes me really happy about people's ability to get very annoyed at what they think is the outrageous control of our culture through copyright. When more people are as mad as the the people I've quoted above, we will be able to change copyright into something less outrageous to all of us.

4 March 2012

Jamie McClelland: Managing KVM instances

At May First/People Link we have been using KVM for several years now and recently I have been running KVM instances on my local laptop. I'm pleased to see all the work that has gone into libvirt, which seems like a robust and full-featured suite of tools for managing many virtualization technologies, including KVM. However, we don't use it at May First/People Link for a number of reasons. The most pressing is that it runs all virtual guests as the same user, but also because it offers far more features than we need (such as graphical access to virtual server, which we don't need since none of our guest servers run X). On May First/People Link hosts, we are using a relatively simple set of bash scripts (accessible via git at git://lair.fifthhorseman.net/~dkg/kvm-manager). These scripts re-use many tools we are already familiar with to build and launch kvm guests. Each guests runs as a dedicated non-provileged user, with a console available using screen, and the kvm process is managed using runit. Since our admins are familiar with these tools already, the learning curve involved is much less steep. Despite the relative simplicity of kvm-manager, it was still more complicated and involved than I wanted on my laptop. Additionally, I wanted to fully understand every piece of the puzzle and separating out user privileges wasn't important to me. So - I wrote the following bash script to launch virtual servers. It assumes you are using logical volume manager. Some editing required if you want to re-use it.
#!/bin/bash
# manage a virtual server
# add /etc/udev/rules.d/92-kvm.rules with the following line (change "jamie" 
# to the group you are running as and vg_animal0 to the name of your volume 
# group):
# ACTION=="change", SUBSYSTEM=="block", ATTR dm/name =="vg_animal0-*_root", GROUP="jamie"
#
# install a new server by:
# * create logical volume with the name: servername_root
# * $0 servername start /usr/local/share/ISOs/default.iso
bridge=virbr0
user=jamie
base=/home/jamie
server="$1"
vg=vg_animal0
# modify server memory here
mem=768
command="$2"
[ -z "$command" ] && command=start
die ()  
  printf "$1\n"
  exit 1
 
cdarg=
if [ -n "$3" ]; then
  [ ! -f "$3" ] && die "Third argument should be path to cd iso. Can't find that path."
  cdarg="-cdrom $3"
fi
function start()  
  lvname="$ vg -$ server _root"
  # trigger udev to ensure we have proper ownership of the block device
  sudo udevadm trigger --subsystem-match=block --attr-match=dm/name="$lvname"
  lv="/dev/mapper/$lvname"
  [ ! -e "$lv" ] && die "Can't find $lv"
  sudo modprobe -v tun   die "Failed to modprobe tun module"
  # create network device if it doesn't already exist
  ip tuntap   grep "$tap"   sudo ip tuntap add dev "$tap" mode tap user "$user"   die "Failed to create device $tap"
  # bring up device if it's not already up
  ip link   grep " $tap "   sudo ip link set "$tap" up   die "Failed to set $tap to up"
  # add the device to the bridge so it get use the upstream network connections
  /sbin/brctl show   grep "$tap"   sudo brctl addif "$bridge" "$tap"   die "Failed to add tap to bridge"
  # launch kvm in a screen session
  screen -S "$server" kvm -drive "file=$lv,if=virtio,id=hda,format=raw" -m "$mem" -device "virtio-net-pci,vlan=1,id=net0,mac=$mac,bus=pci.0" -net "tap,ifname=$tap,script=no,downscript=no,vlan=1,name=hostnet0" $cdarg -nographic   die "Failed to start kvm" 
 
function cleanup()  
  read -p "Please shutdown the host first then hit any key to continue..."
  sudo brctl delif "$bridge" "$tap"
  sudo ip link set "$tap" down
  sudo ip tuntap del mode tap dev "$tap"
 
# generate reproducible mac address
mac="$(printf "02:%s" "$(printf "%s\0%s" "$(hostname)" "$ server "   sha256sum   sed 's/\(..\)/\1:/g'   cut -f1-5 -d:)" )"
tap="$ server 0"
case "$command" in
  start)
    start
    ;;
  cleanup)
    cleanup
    ;;
  *)
    die "Please pass start or cleanup as first argument"
esac

Iustin Pop: Nikkor 24mm f/2.8D

I'm still (ever) looking for the portable, somewhat lightweight photo system but with fast AF, adequate low light capabilities system. Also, I love prime lenses. I have a Nikon DX format camera, but none of the zoom lenses are what I want, and Nikon hasn't updated their wide primes. So I tried for a while a Fuji X100, which has much better ISO/noise results than my camera, but it focuses very badly in low light. What's the use of the low-light capability if you can't focus? So, after also fighting with the UI, I realised that the Fuji was not for me, and went back to my Nikon. And the first photo I took again with a DSLR was like Yes, this is what I expect: shutter half-press, instant focus, confirmation beep, shutter full-press, photo taken, ready for next one . Don't get me wrong, the Fuji X100 is a very nice camera, but it is not a DSLR; and I realised I wanted a portable DSLR, not simply a portable camera. What I did learn though from the Fuji is how good the 23mm (35mm FX equivalent) lens is for general , i.e. street photography. And it was also a prime. So after much head-scratching, I got myself a Nikkor 24mm f/2.8D lens. Yes, I know, it's the old 'D' type, the optics are the same for about 20-25 years, and it's not as sharp as the 're-issued' primes (not even close to the famous 35mm f/1.8 G DX), and it has lots of flare in direct sunlight (as common with wide-angle lenses). However it's a lightweight (270g), small (64.5 46 mm) and quite nice lens. And to be honest, I rather like the old-style distance scale (since it has lots of numbers!), so it compensates for the lack of AF-S. The only downside of the non-AF-S is that it wouldn't work on some of the DX bodies. As to the image quality actually a bit better than I expected. Here is a picture I took in Z rich, granted in perfect light. JPEG, straight-from-camera, just with EXIF data removed (click on the link for the original, full-size image; note that the camera was configured for the 'medium' size instead of 'large' you can see how careful I am when taking pictures: not):
Near Z rich Central
Settings were: I think this is quite good quality for a non-processed JPEG; and given how light the lens is, and that it can go down to f/2.8 (with more softness, though), I think this is quite good for a travel lens. And since I have a short trip coming up sometimes soon, I'll only take this lens, to see how it goes as an all-around lens. If it doesn't perform well, I can always blame my bad technique ;-) PS: I had to learn about the 'underlay' plugin in ikiwiki, as I didn't want to commit megabytes of basically read-only, binary data to git; it works well, so I'll be able to post more pics in the future.

Gregor Herrmann: RC bugs 2012/09

as usual, here's my RCBW report. like in the last weeks, a mixture of NMUs and mails to the BTS, grabbing and writing patches, ...

Stefano Zacchiroli: bits from the DPL for February 2012

Released a few hours ago, here is the monthly report of DPL activities for February 2012.
Howdy, dear Project Members,
here's another round of updates about what has happened in DPL land, this time during February 2012. Highlights Quit a bit of highlights for this month: Talks, interviews, and the like Sprints Plenty of sprints related news! It would be amazing to have an average of one sprint per month for 2012, and we're on good track for it. If you want to help, organize one for your team as documented on the wiki. Legal stuff Appointments In addition to the GSoC admins delegation (see above), I've agreed with former secretary Kurt Roeckx to reappoint him as a secretary for another year. Many thanks, Kurt! Miscellaneous Happy Debian hacking.
PS as usual, the boring day-to-day activity log is available at master:/srv/leader/news/bits-from-the-DPL.*

Next.

Previous.