Search Results: "ag"

28 September 2011

Erich Schubert: Privacy in the public opinion

Many people in the united states seem to have the opinion, that the "public is willing to give up most of their privacy" in particular when dealing with online services such as Facebook. I believe in his keynote at ECML-PKDD, Albert-L szl Barab si of Harvard University expessed such a view, that this data will just become more and more available. I'm not sure if it was him or someone else (I believe it was someone else) that essentially claimed "privacy is irrelevant". Another popular opinion is that "it's only old people caring for privacy".
However, just like politics, these things tend to oscillate from one extreme to another. For example, the recent years in Europe, conservative parties were winning one election after another. Now in France, the socialist parties have just won the senate, the conservative parties in Germany are losing in one state after the other and so on. And this will change back again, too. Democracy also lives from changing roles in government, as this drives both progress and fights corruption.
We might be seeing the one extreme in the united states right now, where people are readily giving away their location and interests for free access to a web site. This can swing back any time.
In Germany, one of the government parties - the liberal democrats, FDP - just dropped out of the Berlin city government, down to 1.8% of voters. Yes, this is the party the German foreign minister, Guido Westerwelle is from. The pirate party [en.wikipedia.org] - much of their program is about privacy, civil rights, copyright reforms and the internet - which didn't even participate in the previous elections since they were was founded just 5 years ago jumped to 8.9%, scoring higher than the liberal democrats did in the previous elections. In 2009 they scored a surprising high 2% in the federal elections - current polls see them anywhere from 4% to 7% at the federal level, so they will probably get seats in parliament in 2013. (There are also other reasons why the liberal democrats have been losing voters so badly, though! Their current numbers indicate they might drop out of parliament in 2013.)
The Greens in Germany, which are also very much oriented towards privacy and civil rights, are also on the rise, and in march just became the second strongest party and senior partner in the governing coalition of Baden-W rttemberg, which historically was a heartland of the conservatives.
So don't assume that privacy is irrelevant nowadays. The public opinion can swing quickly. In particular in democratic systems that have room for more than two parties - so probably not in the united states - such topics can actually influence elections a lot. Within 30 years, the Greens now frequently reach values of 20% in federal polls and up to 30% in some states. It doesn't look as if they are going to go away soon.
Also don't assume that it's just old people caring about privacy - in Germany, in particular the pirate party and the Greens are very much favored by the young people. The typical voter for the pirates is less than 30 years old, male, has a higher education and works in the media or internet business.
In Germany, much of the protest for more privacy - and against the too readily data collection by companies such as Facebook and Google - is driven by the young internet-users and -workers. I believe this will be similar in other parts of Europe - there are other pirate parties all over Europe. And this can happen to the united states any time, too.
Electronic freedom - e.g. pushed by the Electronic Frontier Foundation, but also the open source movement - does have quite a history in the united states. But in particular open source has made such a huge progress the last decade, these movements in the US could just be a bit out of breath right now. I'm sure they will come back with a strong push against the privacy invasions we're seeing right now. And that can likely take down a giant like Facebook, too. So don't bet on people continuing to give up their privacy!

27 September 2011

Sylvain Beucler: 3D OpenGL plotting

gnuplot? Here's the fourth tutorial from Guus on Scientific OpenGL, this time going 3D, plotting the "Mexican Hat" function, and covering various line drawing methods as well as Index Buffer Objects.
http://en.wikibooks.org/wiki/OpenGL_Programming/Scientific_OpenGL_Tutorial_04

Vincent Bernat: Speeding up SSL: enabling session reuse

Session reuse is one of the most important mechanism to improve SSL performance: by submitting an appropriate blob to the server, a client is able to trigger an abbreviated handshake, improving latency and computation time. There exists two distinct ways to achieve session reuse: session identifiers as described in RFC 5246 and session tickets as depicted in RFC 5077. A quick note: when I say SSL, unless I mention a version number, you should read TLS instead. Look at the article for TLS on Wikipedia for some background on this.

Theory of operation To establish a SSL connection, four messages need to be exchanged between client and server. With a latency of 50 ms, we have a 200 ms overhead to establish the connection (plus TCP handshake). Moreover, to share a common secret, both the client and the server needs to achieve some public-key cryptographic operations which are costly, computation-wise. SSL full handshake To avoid a full SSL handshake each time a client request a resource, it is possible for the client to request an abbreviated handshake, saving a complete round-trip (100 ms) and avoiding the costliest part of the full SSL handshake. SSL abbreviated handshake Two mechanisms can be used to accomplish an abbreviated handshake:
  1. When the server sends the Server Hello message, it can include a session identifier. The client should store it and present it in the Client Hello message of the next session. If the server finds the corresponding session in its cache and accepts to resume the session, it will send back the same session identifier and will continue with the abbreviated SSL handshake. Otherwise, it will issue a new session identifier and switch to a full handshake. This mechanism is detailed in RFC 5246. It is the most common mechanism because it exists since earlier versions of SSL.
  2. In the last exchange of a full SSL handshake, the server can include a New Session Ticket message (not represented in the handshake described in the picture) which will contain the complete session state (including the master secret negotiated between the client and the server and the cipher suite used). Therefore, this state is encrypted and integrity-protected by a key known only by the server. This opaque datum is known as a session ticket. The details lie in RFC 5077 which supersedes RFC 4507.
The ticket mechanism is a TLS extension. The client can advertise its support by sending an empty Session Ticket extension in the Client Hello message. The server will answer with an empty Session Ticket extension in its Server Hello message if it supports it. If one of them does not support this extension, they can fallback to the session identifier mechanism built into SSL. RFC 5077 identifies situations where tickets are desirable over session identifiers. The main improvement is to avoid to maintain a server-side session cache since the whole session state is remembered by the client, not the server. A session cache can be costly in term of memory and difficult to share between multiple hosts when requests are load-balanced across servers.

Browser support Session identifiers are part of SSL and are therefore supported since a long time by clients and servers. However, session tickets are an optional TLS extension and therefore, the support is not as widespread as for session identifiers. Support for tickets was added in OpenSSL 0.9.8f (October 2007). In GnuTLS, this is version 2.9.3 (August 2009). For NSS, the set of libraries behind most browsers, support of RFC 5077 is in version 3.12 (June 2008). Schannel, Microsoft implementation of TLS, does not currently supports tickets. To check if a browser supports session resume without and with tickets, I have written a web server listening to several ports with different configurations (session cache disabled or enabled, ticket support disabled or enabled). With the help of some Javascript, it is possible to interact with this server to determine what kind of session resume a browser support. Checking for browser support for session resume It is difficult to get extensive results this way since you need to install a lot of browsers to get something valuable. Surprisingly, Android 2.3.4 browser (as shipped by Cyanogen Mod) does not support any session resume. Another way to check if a browser supports session resume is to use a sniffer and to spot Client Hello messages. If a client tries to resume a session, it will use an appropriate session identifier or send a ticket. A simple program parsing PCAP files allows to automate this task and get some interesting statistics. Here are random facts from more than 300 000 requests (38 000 clients) to a customer care service of an important French telco:
  • 35% of requests exhibit support of tickets;
  • 53.3% of requests ask to resume without tickets; 25.6% with tickets;
  • 67.2% of requests exhibit support of SNI;
  • 86.7% of requests use TLS 1.0; the remaining uses SSL 3.0; almost no TLS 1.1/1.2;
  • in average, a client execute 8 SSL handshakes;
  • ciphers supported by all clients are 3DES-SHA, RC4-MD5 and RC4-SHA.
With some log analysis to match each requests with the appropriate user agent, we can split the world in two parts: browsers supporting RFC 5077 (Chrome and Firefox) and browsers not supporting RFC 5077 (Internet Explorer, Opera 9.80, Safari for MacOS and iOS and Android browser).

Web server support There is no unique recipe to configure a web server to handle appropriately and efficiently session resume. Here are some generic directions :
  • if the web server uses multiple processes, you need to configure a shared memory session cache; usually, tickets will work just fine in this setup;
  • if you use local load-balancing, one easy way to avoid any problem is to use ensure that one IP is mapped to one server (either statically with hashing or dynamically with a stick table); if your load-balancer understands SSL, you can also use session identifier (and disable tickets1) to build a stick table;
  • if you don t want to apply the previous advice, you need to share the session cache between the servers with something like memcached and disable tickets;
  • if you use global load-balancing (DNS based), there is no need to ensure that session resumption works across geographic pools since a user will usually stick to one pool.
Remember that only one client out of three supports TLS tickets. Therefore, you cannot rely on them to ensure proper session resume. You need a session cache.

Setting a session cache with Apache & nginx Apache features two different SSL engines. The first one is mod_ssl and uses OpenSSL as backend. It is possible to setup a shared session cache with SSLSessionCache but the memcached-enabled session cache is available only in the development branch. You can also get one by switching to mod_gnutls backend. The cache is enabled with GnuTLSCache. In this case, do not enable tickets because they cannot be shared. With nginx, you need to enable the shared session cache with ssl_session_cache. Currently, it lacks a memcached-enabled session cache but Matt Palmer has some patches to add it to the 0.8 branch. However, those patches can have a serious impact on nginx performance since retrieving a session from memcached is done synchronously (mostly because a limitation in OpenSSL design who does not allow to register asynchronous callbacks with SSL_CTX_sess_set_get_cb()). As a proof of concept, I have also added a similar feature to stud, the scalable TLS unwrapping daemon, a very efficient network proxy terminating SSL connections. The same limitation as for nginx applies: performances will suffer. Look at the pull request for more details.

Sharing tickets RFC 5077 tells tickets allow to load-balance requests across servers. However, to the best of my knowledge, there is currently no web server able to share tickets across a pool. Actually, when a server initializes its SSL stack, it will randomly generate some keys that will be used to protect and encrypt tickets. In OpenSSL, from ssl/ssl_lib.c:
    /* Setup RFC4507 ticket keys */
    if ((RAND_pseudo_bytes(ret->tlsext_tick_key_name, 16) <= 0)
              (RAND_bytes(ret->tlsext_tick_hmac_key, 16) <= 0)
              (RAND_bytes(ret->tlsext_tick_aes_key, 16) <= 0))
            ret->options  = SSL_OP_NO_TICKET;
Therefore, with a round-robin load-balanced pool of servers, tickets have to be disabled because servers would not accept tickets from neighbors. One way to solve this is to generate keys deterministically by hashing some common secret with the private key. I have implemented this approach for stud. Here is a simplified version (no error handling, no allocation) of the pull request for this feature:
    unsigned char keys[48];
    EVP_PKEY *pkey = grab_private_key();
    /* To get our key, we sign the seed with the private key */
    unsigned int siglen;
    unsigned char sign[LARGE_ENOUGH];
    EVP_MD_CTX mdctx;
    EVP_MD_CTX_init(&mdctx);
    EVP_SignInit(&mdctx, EVP_sha256());
    EVP_SignUpdate(&mdctx, some_secret, strlen(some_secret));
    EVP_SignFinal(&mdctx, sign, &siglen, pkey);
    /* And we keep only the first bytes. */
    memcpy(keys, sign, sizeof(keys));
    /* Tell OpenSSL to use those keys */
    SSL_CTX_set_tlsext_ticket_keys(ctx, keys, sizeof(keys));

Testing While tests can be done with just openssl s_client and openssl sess_id, testing all aspects can take a lot of time. For this purpose, I have written a client testing session resume with and without tickets. Here is a typical result: twitter.com RFC session resume The program will try to establish five consecutive SSL connections for each IP without and with tickets. For each IP, the last four SSL connections should always reuse the first SSL session. Here, Twitter web servers seem properly configured: for each IP, session resume is successful. Their web servers do not support tickets or they may have disabled it because they share the session cache between servers inside the same pool.

  1. RFC 5077 describes interactions between session identifiers and session tickets. When using tickets, the server should send back an empty session identifier. The client may present an empty session identifier or generate one. However, for all practical purposes, it seems that servers send back a non-empty session identifier and clients just stick to this identifier. Please, investigate if you want to use SSL session identifiers for load-balancing while keeping tickets enabled.

Christian Perrier: Stop making sense...

Hope a few of my readers got it from the title of this blog post. And maybe many others didn't. So let's talk about "Stop Making Sense". You're warned: nothing to do with free software...or running, this time. This is all about music. Music from the 80's. "Stop Making Sense" is indeed, in my opinion, one of the best achieved musical movie. It is simple: it features a gig by the Talking Heads, back in 1983, when this band was among the most innovative ones that ever appeared in the late 70's. And I finally managed to take time to actually buy the DVD and see it again as I didn't see it since 1985. For many people, Talking Heads is the incredible person that's David Byrne. That's certainly true for some parts (and this is what lead to their split in 1991), but the movie really gives credit to all members of the band, either the "regular" ones (Tina Weymouth, Chris Frantz, Jerry Harrison) or the tour musicians (Bernie Worrell, Alex Weir, Steven Scales, Lynn Mabry, Edna Holt). The construction of the movie is simple: it just starts with Byrne bringing a music box on an empty stage, with his acoustic guitar and playing an incredible tense "Psycho Killer" (there are so many different version of that mythical piece but this one is among the best). Then Tina joins for a not-so-often played "Heaven" and brings her so inimitable bass line (I count Tina among my very favourite bass player, immediately after Tony Levin). At the end of the piece, the crew quietly brings a full drum set, then Chris Frantz joins, smiling as ever, and the rhythm increases with "Thank you for sending me an angel". Then Jerry Harrison joins, to make the original Heads line-up for a really funky "Found a Job", where Jerry shows that he was THE Heads lead guitar (and Tina is still keeping the foundations so strong). Continuing the increasing tension, the rest of the musicians join for Slippery People, then Burning Down the House ("Who's got a match?"). All this culmminates in a crazy joggin on stage during "Life During Wartime" and Byrne performing incredible and stellar movements on stage. THis one surely makes the band entirely exhausted. How can they survive this? The few next songs are a little bit less stunning (oh, well, "Making Flippy Floppy" still features a dream bass line)...until a really special "Once in a Lifetime" that...has just to be seen (SAME AS IT EVER WAS), then a break where....the Tom Tom Club (namely Chris, Tina and the rest of the band) perform a giant "Genius of Love", so funky. All this is indeed meant for Byrne to prepare for his top appearance, in "Girlfriend is Better", in a giant suit, that makes his head over his long neck yet more...strange. This leads to a crazy "Take me to the River" which has always been the top of the Heads shows during the 80's and a tireless encore on "Crosseyed and Painless". The movie ends up and you nearly never had a breath. So, yes, if you think you enjoy the Heads music and have never seen that movie, just try doing it once. That's how music was in the 80's..and, doh, these folks were so good! By the way, all parts of the movie can be seen on YouTube in case you just want to see what *I* enjoy. Ah, and yes I share the love of the Heads with Danese "we never meet often enough" Cooper, by the way. We once made a promise ourselves to sing Psycho Killer in karaoke if we're happy (and drunk) enough to meet again before we're too old for this..:-).

Michal &#268;iha&#345;: GePeS continued

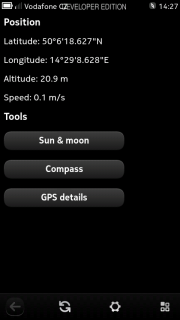
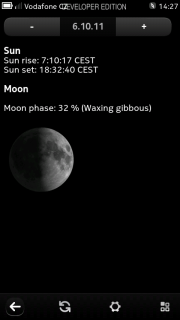
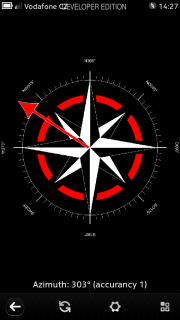
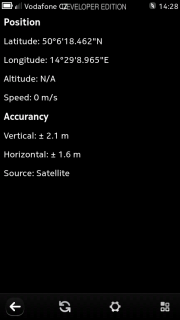
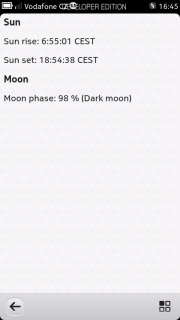
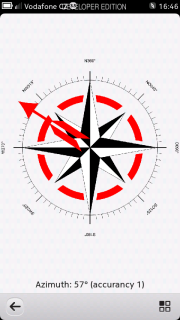
Continuing on my Hackweek project, I've polished GePeS a bit today. I started with better display of GPS coordinates and added some more GPS details to separate page. Adding images for moon phase was also part of the plan, though it force me to learn how to switch application to black theme, which looks much better with moon image. Rest of time was spent on cleaning up the code and adding preferences (for now only refresh rate). Updated screenshots: Main screen Sun and moon screen Compass screen GPS details screen PS: Some numbers look weird (altitude and speed), though I'm pretty sure this is what phone reports me.

Filed under: English Meego Suse 4 comments Flattr this!

Rapha&#235;l Hertzog: Contribute to Debian while promoting the Debian Administrator s Handbook

We just announced the launch of the fundraising campaign for the Debian Administrator s Handbook. We wanted to use this opportunity to let people contribute money both to our project but also to Debian itself. That s why we have setup a special link that you can use to participate. 15% of any donation made through this link (after VAT has been subtracted) will be given back to the Debian Project. Here s the link: http://debian-handbook.info/go/ulule-debian/ Feel free to use this link when promoting the project to your friends, so that even more money goes back to Debian. You can also embed a special widget on your website where any visitor that ends up becoming a supporter will also contribute 15% to the Debian project.
Help us spread the word about the project, and help raise money for Debian!

5 comments Liked this article? Click here. My blog is Flattr-enabled.

Rapha&#235;l Hertzog: Do You Want a Free Debian Book? Read This.

A bit more than a year elapsed since we announced our plans to translate our Debian book into English and to try to get it published under a license compatible with the Debian Free Software Guidelines. But we re now ready to go to the next step. Completing the translation of 450 pages book is a huge work, we estimate it s going to take roughly 3 full time months for both Roland and me. Since we re freelancers, we can take the required time provided that we have a minimum income during that period. That s where you come into play: we have setup a crowdfunding campaign on Ulule.com and we need your support to raise 15000 (this is the absolute minimum for us to be able to commit the required time). Even if a good and up-to-date book on Debian is a great perspective, we want to go further than that by adding the perspective of getting a DFSG-free Debian book. That s why we have transformed the crowfunding campaign in a liberation campaign. When you support the project, you can pledge money towards a liberation fund and if this fund reaches 25000 then the book will be published under the GPL-2+ and CC-BY-SA 3.0 licenses. On top of this, when you support this project you can select a reward that goes from a copy of the ebook to a dinner with the authors (only 10 places for the latter)! Among the other rewards, there s obviously a paperback version of the book, but also an individual one-hour mentoring session with me a nice way to get you hooked as a new Debian contributor (limited to 40 persons, don t miss the opportunity!).
Wait no longer, click here and pledge some money to bring this reference book to Debian and the rest of the world.
We also need your help to spread the news and get as many supporters as possible. Share the link with your friends, write an article on your blog, put a widget on your website, etc. Thank you very much!

Click here to go to the fundraising page and to learn more about this project.

10 comments Liked this article? Click here. My blog is Flattr-enabled.

26 September 2011

Gunnar Wolf: e-voting: Something is brewing in Jalisco...

There's something brewing, moving in Jalisco (a state in Mexico's West, where our second largest city, Guadalajara, is located). And it seems we have an opportunity to participate, hopefully to be taken into account for the future. Ten days ago, I was contacted by phone by the staff of UDG Noticias, for an interview on the Universidad de Guadalajara radio station. The topic? Electronic voting. If you are interested in what I said there, you can get the interview from my webpage. I held some e-mail contact with the interviewer, and during the past few days, he sent me some links to notes in the La Jornada de Jalisco newspaper, and asked for my opinion on them: On September 23, a fellow UNAM researcher, C sar Astudillo, claims the experience in three municipalities in Jalisco prove that e-voting is viable in the state, and today (September 26), third generation of an electronic booth is appearingly invulnerable. Of course, I don't agree with the arguments presented (and I'll reproduce the mails I sent to UDG Noticias about it before my second interview just below They are in Spanish, though). However, what I liked here is that it does feel like a dialogue. Their successive texts seem to answer to my questioning. So, even though I cannot yet claim this is a real dialogue (it would be much better to be able to sit down face to face and have a fluid conversation), it feels very nice to actually be listened to from the other side! My answer to the first note:
El tema de las urnas electr nicas sigue dando de qu hablar por ac en Jalisco... nosotros en Medios UDG hemos presentado distintas voces como la del Dr. Gabriel Corona Armenta, que est a favor del voto electr nico, del Dr. Luis Antonio Sobrado, magistrado presidente del tribunal supremo de elecciones de Costa Rica, quien nos habl sobre los 20 MDD que les cuesta implementar el sistema por lo que no lo han logrado hasta el momento, pudimos hablar hasta argentina con Federico Heinz y su rotunda oposici n al voto electr nico y por supuesto la entrevista que le realizamos a usted. Sin embargo este d a La Jornada Jalisco publica la siguiente nota http://www.lajornadajalisco.com.mx/2011/09/23/index.php?section=politica... nos gustar a saber cu l es su punto de vista al respecto, quedo a la espera de su respuesta
Hola, Pues... Bueno, s que el IFE hizo un desarrollo muy interesante y bien hecho hace un par de a os, dise ando desde cero las urnas que propon an emplear, pero no se instrumentaron fuera de pilotos (por cuesti n de costos, hasta donde entiendo). Se me hace triste y peligroso que el IEPC de Jalisco est proponiendo, teniendo ese antecedente, la compra de tecnolog a prefabricada, y confiando en lo que les ofrece un proveedor. Se me hace bastante iluso, directamente, lo que propone el t tulo: comicios en tres municipios prueban la viabilidad del voto electr nico en todo el estado . Pong moslo en estos t rminos: El que no se caiga una choza de l mina con estructura de madera demuestra que podemos construir rascacielos de l mina con estructura de madera? Ahora, un par de p rrafos que me llaman la atenci n de lo que publica esta nota de La Jornada:
la propuesta de realizar la elecci n en todo el estado con urnas electr nicas que desea llevar a cabo el Instituto Electoral y de Participaci n Ciudadana (IEPC) es viable, pues los comicios realizados en tres municipios son pruebas suficientes para demostrar que la urna es fiable
y algunos p rrafos m s adelante,
Cu ntas experiencias m s se necesitan para saber si es confiable, 20, 30, no lo s (...) Pero cuando se tiene un diagn stico real, efectivo y serio de cu ndo t cnicamente procede, se puede tomar la decisi n
Como lo menciono en mi art culo... No podemos confundir a la ausencia de evidencia con la evidencia de ausencia. Esto es, que en un despliegue menor no haya habido irregulares no significa que no pueda haberlas. Que haya pa ses que operan 100% con urnas electr nicas no significa que sea el camino a seguir. Hay algunas -y no pocas- experiencias de fallas en diversos sentidos de urnas electr nicas, y eso demuestra que no puede haber confianza en las implementaciones. Aunque el equipo nos saliera gratis (que no es el caso), hay que invertir recursos en su resguardo y mantenimiento. Aunque se generara un rastro impreso verificado por el votante (que s lo ha sido el caso en una peque a fracci n de las estacione de votaci n), nada asegura que los resultados reportados por el equipo sean siempre consistentes con la realidad. El potencial para mal uso que ofrecen es demasiado. Saludos,
And to September 26th:
Disculpe que lo molestemos otra vez, pero este d a fue publicada otra nota m s sobre el tema de las Urnas electr nicas en Jalisco donde se asegura que la urna es invulnerable. http://www.lajornadajalisco.com.mx/2011/09/26/index.php?section=politica... nos podr a conceder unos minutos para hablar con usted, como la vez pasada, v a telef nica sobre el caso espec fico de Jalisco, en referencia a estas notas publicadas recientemente? si es posible podr a llamarle este d a a las 2 pm? Quedo a la espera de su respuesta agradeci ndole su ayuda, apreciamos mucho esta colaboraci n que est haciendo con nosotros
Hola, ( ) Respecto a esta nota: Nuevamente, ausencia de evidencia no es evidencia de ausencia. Se le permite a un peque o segmento de personas jugar con una m quina. Significa eso que fue una prueba completa, exhaustiva? No, s lo que ante un jugueteo casual no pudieron encontrar fallos obvios y graves. Un verdadero proceso que brindara confianza consistir a en (como lo hicieron en Brasil - Y resultaron vulnerables) convocar a la comunidad de expertos en seguridad en c mputo a hacer las pruebas que juzguen necesarias teniendo un nivel razonable de acceso al equipo. Adem s, la seguridad va m s all de modificar los resultados guardados. Un par de ejemplos que se me ocurren sin darle muchas vueltas:
  • Qu pasa si meto un chicle a la ranura lectora de tarjeta magn tica?
  • Qu pasa si golpeo alguna de las teclas lo suficiente para hacerla un poquito menos sensible sin destruirla por completo? (o, ya entrados en gastos, si la destruyo)
La negaci n de servicio es otro tipo de ataque con el cual tenemos que estar familiarizados. No s lo es posible modificar el sentido de la votaci n, sino que es muy f cil impedir que la poblaci n ejerza su derecho. Qu har an en este caso? Bueno, podr an caer de vuelta a votaci n sobre papel - Sobre hojas de un block, probablemente firmadas por cada uno de los funcionarios, por ejemplo. Pero si un atacante bloque la lectura de la tarjeta magn tica, que es necesaria para que el presidente de casilla la marque como cerrada, despoj de su voto a los usuarios. S , se tienen los votos impresos (que, francamente, me da mucho gusto ver que esta urna los maneja de esta manera). El conteo es posible, aunque un poco m s inc modo que en una votaci n tradicional (porque hay que revisar cu les son los que est n marcados como invalidados - no me queda muy claro c mo es el escenario del elector que vot por una opci n, se imprimi otra, y el resultado fue corregido y marcado como tal)... Pero es posible. Sin embargo, y para cerrar con esta respuesta: Si hacemos una corrida de prueba, en circunstancias controladas, obviamente no se notar n los much simos fallos que una urna electr nica puede introducir cuando los "chicos malos" son sus programadores. Podemos estar seguro que este marcador Atlas-Chivas-Cruz Azul tenga el mismo ndice de fiabilidad como una elecci n de candidatos reales, uno de los cuales puede haberle pagado a la empresa desarrolladora para manipular la elecci n? Y a n si el proceso fuera perfecto, indican aqu que est n _intentando_ licitar estas urnas (y nuevamente, si lo que menciona esta nota es cierto, son de las mejores urnas disponibles, y han atendido a muchos de los se alamientos - Qu bueno!)... Para qu ? Qu nos van a dar estas urnas, qu va a ganar la sociedad? Mayor rapidez? Despreciable - Media hora de ganancia. A cambio de cu nto dinero? Mayor confiabilidad? Me queda claro que no, siendo que no s lo somos cuatro trasnochados los que ponemos su sistema en duda, sino que sus mismos proponentes apuntan a la duda generalizada. La frase con la que cierra la nota se me hace digna para colgar un ep logo: "en ese futuro quiz no tan distante la corrupci n tambi n ocurre y sta se debe siempre al factor humano". Y el factor humano sigue ah . Las urnas electr nicas son programadas por personas, por personas falibles. Sin importar del lado que est n, recordar n la pol mica cuando se hizo p blico que la agregaci n de votos en el 2006 fue supervisada por la empresa Hildebrando, propiedad del cu ado del entonces candidato a la presidencia Felipe Calder n. Qu evita que caigamos en un escenario similar, pero ampliamente distribu do? Y aqu hay que referirnos a la sentencia de la Suprema Corte de Alemania: En dicho pa s, las votaciones electr nicas fueron declaradas anticonstitucionales porque s lo un grupo de especialistas podr an auditarlas. Una caja llena de papeles con la evidencia clara del sentido del voto de cada participante puede ser comprendida por cualquier ciudadano. El c digo que controla a las urnas electr nicas, s lo por un peque o porcentaje de la poblaci n.

John Goerzen: Five

Dad, will you and mom stay up all night decorating the house for me?
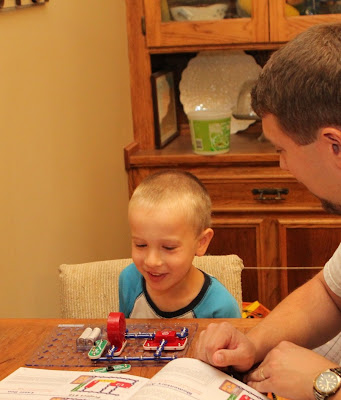
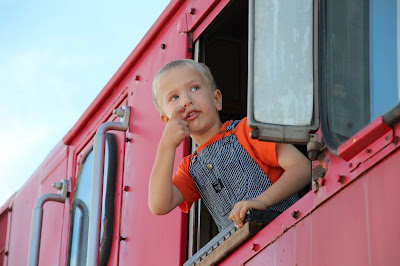
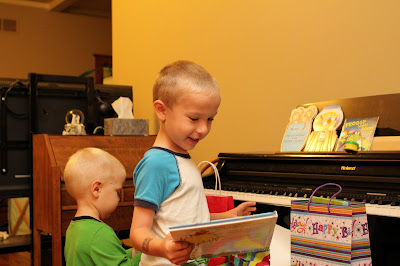
That was Jacob s question to me at bedtime the evening before his fifth birthday. Jacob had already had his birthday party a few weeks ago. When scheduling means that parties happen that far away from the boys real birthdays, they get a smaller celebration with just Terah and me where we open their presents from us. A low-key thing, so we weren t planning to decorate the house. I said, Well, I don t think we ll be doing all that since you already had your birthday party. And the look of eager anticipation on his face turned to a very sad and disappointed look, and made me feel really bad. Uhoh. So while Jacob was sleeping, I mentioned it to Terah. We decided we should improvise something simple, so she found some old streamers and we taped them up, running them through several rooms in the house and across his door. It took a few minutes using supplies we already had, but the joy the next morning was priceless. Oh dad, you said you wouldn t stay up all night, BUT YOU DID! Oh I am SO HAPPY! YAY YAY YAY! And he ran through the house to discover what else was set up. Then he ran to find Oliver and gave him a tour of everything. Then we sat down to open his presents. Here he is, holding a present from Terah and me: That s a copy of The Lorax. My friend Jonathan had brought a copy along during our road trip in Mexico, and Jacob was really excited about it. And didn t really want to give it up, because You can only get The Lorax in Mexico. He (and Oliver) really enjoyed all his presents he also got a train book from us (which he said, Oh, yay, it s the book they have at preschool! ), and a game and some other presents from the distant relatives. But the highlight was something of an impulse buy. I was at the RadioShack in Derby a place I ve written about before, It is what a RadioShack should (and used to) be. It has a large amateur radio section, sells all sorts of coax by the foot, and provides astonishingly good post-sale service. Well, I was there with a radio question, and Mark (the owner) who is an excellent salesman in a positive way pointed me to a display of snap kits. I noticed their Electronics 101 Snap-Kit (a rebranded Snap Circuits Jr. SC-100). A ham in Pennsylvania had suggested them to me once, and as Jacob s birthday was coming up, I gave it some thought. The kit said ages 8 and up. I asked Mark what he thought about a boy just turning 5. He said, Well, probably not normally. But knowing you, if you re there to work on them with him, I think he d enjoy it. But I wouldn t have him work on it by himself. I agreed and we bought it. I pondered how to explain the concept of this thing to Jacob. Eventually I decided I would call it a toy-building kit. He understood that. Jacob and I spent hours together working with it. He would flip through the book, either picking circuits that looked interesting or telling me what kind of circuit he wanted to build. Then I would tell him what to put where, and he d snap them together and play with them. He only played with each finished product a few minutes before he was ready to try another. Once I got him very excited with my offer to show him how to hook up two switches in parallel for the fan he built (and later introduced the parallel vs. series concept by hooking them up in series instead.) Here we are working on it together. Jacob repeatedly called Terah over to look at the things he built. He was very excited that he assembled it himself. Eventually, Oliver (age 2) came over wanting to help. So he sat on my lap, and handed parts to Jacob, then Jacob put them on the grid. Oliver really enjoyed being involved in this way, even though I had to keep him from doing things like ripping the capacitor off its mount. We tend to be modest in terms of the number of things we give the boys and their cost, reasoning that we, like many, already have too many toys in our house, and that greater cost doesn t necessarily equate with a better experience for the boys. I particularly look for things with lasting value and unique experiences for them, and I think we succeeded this year. But I realized quickly that the greatest value of this kit wasn t electronics. It was having a great way for me to spend a lot of time doing things with the boys which all of us enjoyed. Those hours building things together were as much a present for me as for Jacob, I m quite sure. Jacob s real party was a few weeks ago at the Great Plains Transportation Museum in Wichita. They let people rent a historic caboose to use for a birthday party for children. So we did that for Jacob this year. That was a huge hit for the boys. Jacob got to help his grandpa make some pie (instead of cake) for the party. He enjoyed eating it, of course. He enjoyed opening his presents high up on the observation chair in the caboose. And the boys got to play on all the other equipment in the museum. Jacob enjoyed playing tour guide for family since most of them hadn t been there. He also enjoyed watching freight trains pass on the other side of the fence from the museum preferably while sitting in one of the museum s engines. Oliver certainly didn t get left out. Train-watching is serious business, after all. Jacob has long talked about going to the train museum and the airplane museum (Kansas Aviation Museum) on the same day, so one of his birthday surprises was that we went to the airplane museum after his party. His favorite item there is a retired FedEx 727. Here he is walking down the rear of the plane. And, of course, they played captain and co-pilot in several different planes.

Benjamin Mako Hill: Science as Dance

The following selected bibliography showcases only a small portion of the academics who have demonstrated that while it may take two to tango, it only takes one to give a scholarly paper a silly cliche title:
Briganti, G. 2006. It Takes Two to Tango-The CH-53K is arguably the first serious US attempt to open the defense cooperation NATO has been seeking. Rotor and Wing 40(7):60 63.
Coehran, J. 2006. It Takes Two to Tango: Problems with Community Property Ownership of Copyrights and Patents in Texas. Baylor L. Rev. 58:407.
Diamond, M.J. 1984. It takes two to tango: Some thoughts on the neglected importance of the hypnotist in an interactive hypnotherapeutic relationship. American Journal of Clinical Hypnosis 27(1):3 13.
Kraack, A. 1999. It takes two to tango: The place of women in the construction of hegemonic masculinity in a student pub. Masculinities in Aotearoa/New Zealand 153 165.
Lackey, J. 2006. It takes two to tango: beyond reductionism and non-reductionism in the epistemology of testimony. The Epistemology of testimony 160 89.
Miller, C.A. 1998. It takes two to tango: understanding and acquiring symmetrical verbs. Journal of psycholinguistic research 27(3):385 411.
Modiano, N. 1984. It Takes Two to Tango, or Transmission is a Two-Way Street. Anthropology & Education Quarterly 15(4):326 330.
Ott, M.A. 2008. It Takes Two to Tango: Ethical Issues Raised by the Study of Topical Microbicides with Adolescent Dyads. The Journal of adolescent health: official publication of the Society for Adolescent Medicine 42(6):541.
Rubenstein, J.H. 2009. It takes two to tango: dance steps for diagnosing Barrett s esophagus. Respiratory Care Clinics of North America 69(6):1011 1013.
Settersten Jr, R.A. 2009. It takes two to tango: the (un) easy dance between life-course sociology and life-span psychology. Advances in Life Course Research 14(1-2):74 81.
Skaerbaek, E. 2004. It takes two to tango on knowledge production and intersubjectivity. NORA: Nordic Journal of Women's Studies 12(2):93 101.
Spencer, M. 2005. It takes two to tango. Journal of Business Strategy 26(5):62 68.
Vanaerschot, G. 2004. It Takes Two to Tango: On Empathy With Fragile Processes. Psychotherapy: Theory, Research, Practice, Training 41(2):112.
Viskochil, D.H. 2003. It takes two to tango: mast cell and Schwann cell interactions in neurofibromas. Journal of Clinical Investigation 112(12):1791 1792.
Weiner, A. 2001. It Takes Two to Tango:: Information, Metabolism, and the Origins of Life. Cell 105(3):307 308.
Wittman, M.L. 1990. It Takes Two to Tango: Your Simplistic System for Self-survival. Witmark Pub. Co.
There are also a few hundred groups who have demonstrated that larger groups can so as well.

Michal &#268;iha&#345;: GePeS - another hacweek project

With no clear plans for Hackweek this year, I decided to play even more with N950. As I quite lack some GPS application I decided to write it :-). The feature set will be based on things I would use, though I still think it will be useful for others: I've named the application as GePeS and you can find sources on Gitorious: https://gitorious.org/gepes During first day I've managed to implement basic things, check screenshots: Main screen Sun and moon screen Compass screen

Filed under: English Meego Suse 0 comments Flattr this!

Biella Coleman: Now for the harder photo request: Free Dmitry!

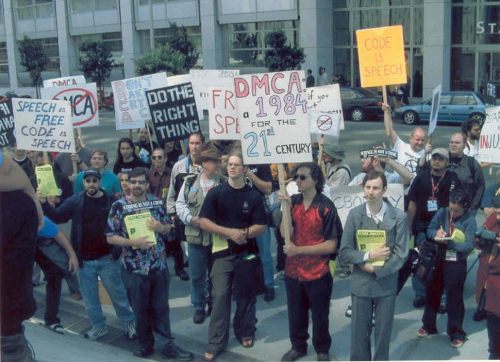
Free Dmitry! So one my favorite fieldwork photos is the one above and I would love to include it in my book but I have no idea where I got it from much less who took it. The photo was taken during a San Francisco protest against the DMCA, and more urgently at the time, also calling for the release of Dimitry Sklyrov (and we were all listening to Richard Stallman who was giving a small speech and I am on the right hand side of the photo, furiously scribbling notes) I am looking for a high quality photo from one of the many Dmitry Sklyarov protests that were held in San Francisco or San Jose a photo that is either under CC license or given to me with formal permission to publish (I have forms to get official permissions). As I mentioned in my previous post, the book will be published with Princeton University Press with a CC license.

Biella Coleman: Photos for Coding Freedom

So my first book, Coding Freedom: The Ethics and Aesthetics of Hacking is mostly sort of done. All the arguments are in place and I am doing the final, very annoying, seemingly endless work of adding a few final citations, hunting for permissions, and tweaking about 10 paragraphs that I feel can be slightly improved (down from about 20 last week). The book is based on the dissertation but re-framed significantly with lots of new material and best of all a lot of the cruft has been zapped away, I think. The book will include two published pieces, although slightly revised. One of them is one of my all time favorite pieces on the hacker conference (which is the least academic/jargony of the peer reviewed articles). I thought it might be fun to change some of the photos for my book: so if you have some awesome, high quality photos that exude the joy of conferencing from past Debconfs or ANY hacker conference (preferably with computers in the background) please share. I am open to anything although I am looking for a high quality/sharp photo of people hacking away in the hack lab. The photo I have is good but I would like one with better lighting/sharper focus. The book will be published under a CC license (the most restrictive one, but heck as a junior scholar, I took what I could get and it is the first book that Princeton University Press is releasing under such a license). If you hold the copyright, I will need more official permission, otherwise, if it is under a CC or copyleft license, I will be adding the correct attribution/notice in the book.

Julien Danjou: Google Contacts for Emacs

I finally finished a thing I was really missing: accessing my Google Contacts from Emacs. That's now possible, thanks to my new google-contacts.el package.

<video controls="controls"> <source src="http://julien.danjou.info/images/emacs-google-contacts.ogv" type="video/ogg"> </video> It includes searching for any contact and displaying the result in a window. You can also jump to a contact from Gnus by pressing a key, and complete e-mail addresses while composing a mail.
Flattr me!

25 September 2011

Joachim Breitner: Yesod packaged for Debian

As Clint writes on his blog, we have now Yesod, a Haskell web framework, packaged in Debian. Despite his humble choice of words, it was mostly his work, and it is quite some work, given that Yesod has a huge number of dependencies that were not yet packaged. So if you want to use Yesod on Debian, and prefer pre-built libraries without dependency problems and clean installation/deinstallation with dpkg over having always latest and greatest, this should provide you with a solid base.

Flattr this post

Gregor Herrmann: RC bugs 2011/38

quick overview over my RC bug activities during the last week: random notes:

Christian Perrier: [life] [running] Berlin marathon: I ran in the world record race...

...but I didn't break it myself. Still, Patrick Makau broke today Haile Gebresselassie's world record by 21 seconds, lowering it down to 2h03'38". This is an impressive performance, considering the quite "high" temporature today in Berlain (about 23 C). My own race was quite good, though not perfect. My goal was targeting 3h36', to break my own record (3h40'24"). However, my preparation was complicated by an hurted ankle in early August, then a very shaky September month at work with a lot of stress and work days up to 12 hours. Not the best way to prepare a marathon. Last two weeks were fairly good wrt running, with an half-marathon run in 1h43' two weeks ago. Still, we complicated this by speding a few days to do sightseeing in Berlin (you can't really be in such a nice city and not try to see it!). So, that means a lot of walking here or there, with museum visits and quite long days. Again, not the best way to prepare a marathon..:-) Still, my watch was set on a 5'07"/km pace. My goal was starting like this, work to avoid going faster over the first 20K ad see what happens. At the beginning, it worked fairly well. Contrary to Paris marathon, Berlin's start in Strasse des 17. Juni is very cool for the first 3 kilometers with an incredibly wide avenue, whilst Paris marathon shrinks in Rue de Rivoli after km 1.5, making it fairly complicated to pass. Also, runners in Germany are much more respectful of running principles and very few register for starting blocks that are nont their real performance (like registering for 3h30 while your best time if 4h). So less passing and a much more costant pace. Up to km15 in Kreuzbeg, everything went well, though the heat was growing, which already made me suspect that I would not make it (0-5K in 25'31", 5-10K in 25'54", 10-15K in 25'55") . From this point, I had to "fight" a bit more to keep the pace...and a few streets without shade had their effect. Moreover, I already had to refill my belt bottle after drinking 0,8l for the first 17KM. The pace thus went down to about 5'10-5'15" and I reached half-marathon in 1h50'28", already not really on time for less than 3h40). 15-20K in 26'41", including a bottle refill. Then 20-25 in 25'44", so small drop after all. However, the wall hit me on km28. For the first time in my marathon life, I think I considered abandoning because I was feeling without any energy and still 1/3 of a marathon to run. Well, that was only the 30K wall which they apparently moved 2K earlier..:-) After calming myself down, I decided to do what has to be done in such case: refill with energy. So long for the gels I had and particularly the hyper-glucidic "Coup de Fouet". Finally, around KM30, I found more motivation to complete the race. Anyway, we were then very very far away, at the end of Hohenzollendamm, so the only option was to come back anyway! Despite all this, I kept a very decent pace, after all: 26'45" for 25-30K. Each kilometer, my watch was beeping to remind me that I was not crawling on the street but more keeping about 5'20". Still, the last kilometers on these giants avenues (oh, endless Leipziger Strasse after Postdamer Platz!) needed a lot of motivation to be completed. It's indeed only at Gendarmenmarkt that I finally could be reliefed and know that I would not only finish, but also do it in a very decent time. 30-35K in 27'43", 35-40K in 27'38". Then we turned in Unter den Linden and, even better, at KM41, my beloved Elizabeth was there yelling. This, plus Brandenburder Tor not so far away....I could then "sprint" at 5'08" for the last kilometer. Finally, this marathon (my 6th official) was completed in 3h44'50", which is my second best. I'm really happy with this result, finally. OK, I didn't break my record as I was intending to (I think I can go down to 3h35 with a normal preparation and good conditions), but the way I managed the difficulty was finally good. So, now, let's prepare the next goal, a 67km night race in November, the longest distance I have ever run. Yet another different thing to prepare. And what about Berlin in all this? Well, in short, that city is *great*. What could I tell more?

Tanguy Ortolo: Increase your productivity with two spaces

Shell prompts are often designed to provide a reminder of useful context information such user name, host and current directory:
PS1="\u@\h:\w\$"
tanguy@muscat:~/public_html$
Such a prompt is sufficient to serve its original purpose, but it can be enhances in at least one useful way. Sometimes you have to copy the path of the current directory: with this prompt, it means selecting it by precisely dragging the mouse over it. Well, by adding spaces around the current directory you can become able to select it with a simple double click:
PS1="\u@\h: \w \$"
tanguy@muscat: ~/public_html $
Indeed, with such a prompt, you can now roughly point to the path, double click, and let your terminal emulator's word detection feature select the whole path for you. This simple modification may save you several tenths of seconds!

24 September 2011

Sylvain Beucler: Smooth lighting

phong After some restless hours of debugging, here's Phong lighting :)
http://en.wikibooks.org/wiki/GLSL_Programming/GLUT/Smooth_Specular_Highlights
The code can be optimized, but should give you a clear understanding on how to make smooth OpenGL lighting. And you can admire the stunning results with a mere basic material and one lamp!

Biella Coleman: Hack Week On the Media

So much reporting on hacking is . so bad (no surprise to readers here). Worse is that term term was bandied out constantly during the News of the World Scandal. In contrast to this historical tradition, On the Media has curated a stellar Hack Week that provides depth, breath, and nuance; the producer of the show, Alex Goldman, poured an enormous amount of time, labor, and thought in compiling a rich set of materials to get at the term hackers, the many facets of hacking (from phreaking to hardware hacking) and best of all, interviewed the fantastic Marcia Hoffman from the EFF on one of the laws, the Computer and Fraud Abuse Act, whose massiveness (and vagueness) has the potential to do a lot of damage and which is often wielded against hackers (and many non-hackers as well). There is also an audio section on the term hacker, which I myself might have done slightly differently, emphasizing, that alongside the MIT hacker (covered so well by Steven Levy) phone phreaking (only called as such in 1973 but well and alive before then) fed into a transgressive tradition that was not simply about malicious hacking nor about the media portrayals that started to explode in the 1980s. The interview gets at the fact that there are differences and hackers can be quite sectarian but I might have pushed this fact a little further. All in all and after the ad nauseum use and abuse of the term hacking during the News of the World scandal (and its overabuse with Anonymous), this collection is the perfect antidote.

Next.

Previous.