Armadillo is a powerful and expressive C++ template library for linear algebra and scientific computing. It aims towards a good balance between speed and ease of use, has a syntax deliberately close to Matlab, and is useful for algorithm development directly in C++, or quick conversion of research code into production environments. RcppArmadillo integrates this library with the R environment and language and is widely used by (currently) 1027 packages other packages on CRAN, downloaded 26.9 million times (per the partial logs from the cloud mirrors of CRAN), and the CSDA paper (preprint / vignette) by Conrad and myself has been cited 503 times according to Google Scholar.
This release reflect as new upstream bugfix release 11.4.2 made recently by Conrad. To accomodate CRAN and their preference for at most a release per month, we held it back since the 11.4.0 release early October. As we usually do, we generally update once upstream Armadillo releases are made. When we do not immediately release to CRAN (in order to lower the release cadence), we make those interim releases available via GitHub source and the Rcpp drat repo.
This release also brings a rearranged, and as we think, simplified layout of the header files. All existing locations are still supported but we will be starting a (very patient and slow) transition at some point.
The full set of changes (since the last CRAN release 0.11.4.0.1) follows.
Changes in RcppArmadillo version 0.11.4.2.1 (2022-11-08)
Upgraded to Armadillo release 11.4.2 (Ship of Theseus)
more robust handling of corner cases in multi-threaded contexts
Internal header organisation with new sub-directories while providing full compatibility via existing paths (#395#396)
Changes in RcppArmadillo version 0.11.4.1.0 (2022-10-10) (GitHub Only)
Upgraded to Armadillo release 11.4.1 (Ship of Theseus)
fix data race in Cube::slice()
workarounds for false warnings emitted by GCC 12 when compiling with FORTIFY_SOURCE enabled (already in RcppArmadillo 0.11.4.0.1 too)
Computer terminals have traditionally had an actual bell
that would ring when a certain control character (the bell
character, typically control-g or \a in an C escape
sequence) would come in the input stream.
That feature actually predates computers altogether, and was present
in Baudot code, "an early character encoding for telegraphy
invented by mile Baudot in the 1870s", itself superseding Morse
code.
Modern terminal emulators have, of course, kept that feature: if
you run this command in a terminal right now:
printf '\a'
... you may hear some annoying beep. Or not. It actually depends on
a lot of factors, including which terminal emulator you're using, how
it's configured, whether you have headphones on, or speakers
connected, or, if you're really old school, a PC speaker, even.
Typically, I have this theory that it does the exact opposite of what
you want, regardless of whether you have configured it or not. That
is, if you want it to make noises, it won't, and if you want it to
stay silent, it will make brutal, annoying noises in moments you would
the least expect. I suspect this is a law in computer science, but I'm
too lazy to come up with a formal definition.
Yet something can be done with this.
Making the bell useful and silent
Many terminal emulators have this feature where they can silence the
bell somehow. It can be turned into a "visual bell" which basically
flashes the screen when a bell arrives. Or that can also be disabled
and the bell is just completely ignored.
What I did instead is turn the bell into a "urgency hint" (part
of the ICCCM standard. In xterm, this is done with this X
resource entry (typically in ~/.Xresources):
XTerm*bellIsUrgent:  true
XTerm*visualBell: false
Interestingly, this doesn't clearly say "bell is muted", but it's
effectively what it does. Or maybe it works because I have muted
"System Sounds" in Pulseaudio. Who knows. I do have this in my startup
scripts though:
If the dash or 'off' are given, the bell will be turned off.
Interestingly, you have the option of setting the bell "volume",
"pitch, in hertz, and [...] duration in milliseconds. Note that not
all hardware can vary the bell characteristics." In any case, I think
that's the magic trick to turn the darn thing off.
Now this should send urgency hints to your window manager:
sleep 3 ; printf '\a'
Try it: run the command, switch to another desktop, then wait 3
seconds. You should see the previous desktop show up in red or
something.
In the i3 window manager I am currently using, this is
the default, although I did set the colors (client.urgent and
urgent_workspace in bar.colors).
Other window managers or desktop environments may require different
configurations.
Sending a bell...
Now that, on itself, will only be useful when something sets a
bell. One place I had found a trick like this, long ago, is this
post (dead link, archived) which has various instructions for
different tools. I'll recopy some of them here since the original site
is dead, but credit goes to the Netbuz blog.
(Note that the blog post also features an Awesome WM configuration for
urgency hints.)
Mutt
set beep=yes
set beep_new=yes
Irssi
/set beep_when_window_active ON
/set beep_when_away ON
/set beep_msg_level MSGS DCC DCCMSGS HILIGHT
It was also recommending this setting, but it appears to be deprecated
and gives a warning in modern irssi versions:
/set bell_beeps ON
GNU Screen
This is an important piece of the puzzle, because by default, terminal
multiplexers have their own opinion of what to do with the bell as
well:
# disabled: we want to propagate bell to clients, which should handle
# it in their own terminal settings. this  vbell off  is also the
# upstream and tmux's default
#
# see also: http://netbuz.org/blog/2011/11/x-bells-and-urgency-hints/
vbell off
# propagate bell from other windows up to the terminal emulator as well
bell_msg 'Bell in window %n^G'
The bell_msg bit is an extra from me: it uses the bell message that
pops up when screen detects a bell in another window to resend the
bell control character up to the running terminal.
This makes it so a bell in any multiplexed window will also
propagate to the parent terminal, which is not the default.
Tmux
Untested, but that is apparently how you do it:
# listen to alerts from all windows
set -g bell-action any
# notice bell in windows
set -g monitor-bell on
# only propagate bell, don't warn user, as it hangs tmux for a second
set -g visual-bell off
# send bell *and* notify when activity (if monitor-activity)
set -g visual-activity both
Note that this config goes beyond what we have in GNU screen in that
inactivity or activity will trigger a bell as well. This might be
useful for cases where you don't have the prompt hack (below) but it
could also very well be very noisy. It will only generate noise when
monitor-activity is enabled though.
bash and shell prompts
Now the icing on cake is to actually send the bell when a command
completes. This is what I use this for the most, actually.
I was previously using undistract-me for this, actually. That was
nice: it would send me a nice desktop notification when a command was
running more than a certain amount of time, and if the window was
unfocused. But configuring this was a nightmare: because it uses a
complex PROMPT_COMMAND in bash, it would conflict with my (already
existing and way too) complex bash prompt, and lead to odd
behaviors. It would also not work for remote commands, of course, as
it wouldn't have access to my local D-BUS to send notifications
(thankfully!).
So instead, what I do now is systematically print a bell whenever a
command terminates, in all my shells. I have this in my
/root/.bashrc on all my servers, deployed in Puppet:
PROMPT_COMMAND='printf "\a"'
Or you can just put it directly in the shell prompt, with something
like:
PS1='\[\a\]'"$PS1"
(I have the equivalent in my own .bashrc, although that thing is
much more complex, featuring multi-command pipeline exit status,
colors, terminal title setting, and more, which should probably
warrant its own blog post.)
This sounds a little bonkers and really noisy, but remember that I
turned off the audible bell. And urgency hints are going to show up
only if the window is unfocused. So it's actually really nice and not
really distracting.
Or, to reuse the undistract-me concept: it allows me to not lose focus
too much when I'm waiting for a long process to complete.
That idea actually came from ahf, so kudos to him on that nice
hack.
Caveats
That is not setup on all the machines I administer for work, that
said. I'm afraid that would be too disruptive for people who do not
have that configuration. This implies that I don't get notifications
for commands that run for a long time on remote servers, most of the
time. That said, I could simply run a command with a trailing printf
'\a' to get a notification.
This might not work in Wayland, your window manager, your desktop
environment, your Linux console, or your telegraphy session.
A new release 0.2.12 of RcppCCTZ is now on CRAN.
RcppCCTZ uses Rcpp to bring CCTZ to R. CCTZ is a C++ library for translating between absolute and civil times using the rules of a time zone. In fact, it is two libraries. One for dealing with civil time: human-readable dates and times, and one for converting between between absolute and civil times via time zones. And while CCTZ is made by Google(rs), it is not an official Google product. The RcppCCTZ page has a few usage examples and details. This package was the first CRAN package to use CCTZ; by now several others packages (four the last time we counted) include its sources too. Not ideal, but beyond our control.
This version adds support for NA values when parsing, and updates GitHub Action.
Changes in version 0.2.12 (2022-11-06)
Support NA values in numerical or character input
GitHub Actions were updated to checkout version 3.
A new release 0.3.3.9.3 of RcppEigen arrived on CRAN moments ago (and just went to Debian). Eigen is a C++ template library for linear algebra: matrices, vectors, numerical solvers, and related algorithms.
This update is again mostly maintenance. To accomodate one small aspect of the Fortran interface, we now require R 3.6.0 or later. Jonah Gabry spotted a really old typo and fixed it. The fastLm support code now uses the unabbreviated df.residual. We accomodated clang-15 in one signature as is common with many recent uploads, and also updated one aspect of GitHub Actions.
And once again as we said for the last four releases:
One additional and recent change was the accomodation of a recent CRAN Policy change to not allow gcc or clang to mess with diagnostic messages. A word of caution: this may make your compilation of packages using RcppEigen very noisy so consider adding -Wno-ignored-attributes to the compiler flags added in your ~/.R/Makevars.
We still find this requirement rather annoying. Eigen is only usable if you set, say,
asoptions in~/.R/Makevars . But CRAN makes the rules. Maybe if a few of us gently and politely nudge them they may relent one day. One can only hope.
The complete NEWS file entry follows.
Changes in RcppEigen version 0.3.3.9.3 (2022-11-04)
The dependency on R is now versioned to 3.6.0 or later for support for USE_FC_LEN_T from Fortran.
An old example typo was corrected (Jonah Gabry in #114).
The fastLm methods now reference df.residual by its full name (Closes #115).
A function prototype was updated for clang-15.
GitHub Actions were updated to checkout version 3.
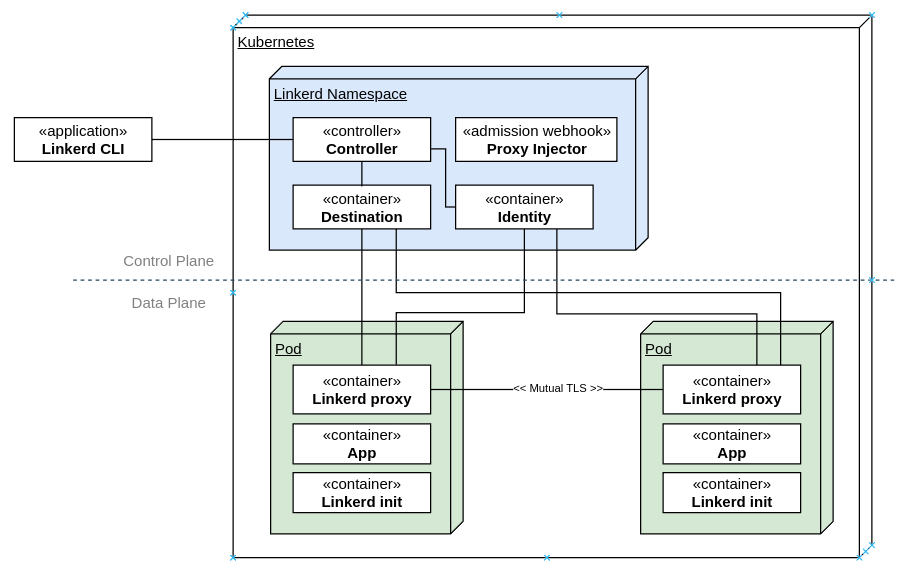
If you ve done anything in the Kubernetes space in recent years, you ve most likely come across the words Service Mesh . It s backed by a set of mature technologies that provides cross-cutting networking, security, infrastructure capabilities to be used by workloads running in Kubernetes in a manner that is transparent to the actual workload. This abstraction enables application developers to not worry about building in otherwise sophisticated capabilities for networking, routing, circuit-breaking and security, and simply rely on the services offered by the service mesh.In this post, I ll be covering Linkerd, which is an alternative to Istio. It has gone through a significant re-write when it transitioned from the JVM to a Go-based Control Plane and a Rust-based Data Plane a few years back and is now a part of the CNCF and is backed by Buoyant. It has proven itself widely for use in production workloads and has a healthy community and release cadence.It achieves this with a side-car container that communicates with a Linkerd control plane that allows central management of policy, telemetry, mutual TLS, traffic routing, shaping, retries, load balancing, circuit-breaking and other cross-cutting concerns before the traffic hits the container. This has made the task of implementing the application services much simpler as it is managed by container orchestrator and service mesh. I covered Istio in a prior post a few years back, and much of the content is still applicable for this post, if you d like to have a look.Here are the broad architectural components of Linkerd:The components are separated into the control plane and the data plane.The control plane components live in its own namespace and consists of a controller that the Linkerd CLI interacts with via the Kubernetes API. The destination service is used for service discovery, TLS identity, policy on access control for inter-service communication and service profile information on routing, retries, timeouts. The identity service acts as the Certificate Authority which responds to Certificate Signing Requests (CSRs) from proxies for initialization and for service-to-service encrypted traffic. The proxy injector is an admission webhook that injects the Linkerd proxy side car and the init container automatically into a pod when the linkerd.io/inject: enabled is available on the namespace or workload.On the data plane side are two components. First, the init container, which is responsible for automatically forwarding incoming and outgoing traffic through the Linkerd proxy via iptables rules. Second, the Linkerd proxy, which is a lightweight micro-proxy written in Rust, is the data plane itself.I will be walking you through the setup of Linkerd (2.12.2 at the time of writing) on a Kubernetes cluster.Let s see what s running on the cluster currently. This assumes you have a cluster running and kubectl is installed and available on the PATH.
On most systems, this should be sufficient to setup the CLI. You may need to restart your terminal to load the updated paths. If you have a non-standard configuration and linkerd is not found after the installation, add the following to your PATH to be able to find the cli:
export PATH=$PATH:~/.linkerd2/bin/
At this point, checking the version would give you the following:
$ linkerd version
Client version: stable-2.12.2
Server version: unavailable
Setting up Linkerd Control PlaneBefore installing Linkerd on the cluster, run the following step to check the cluster for pre-requisites:
kubernetes-api
--------------
  can initialize the client
  can query the Kubernetes API
kubernetes-version
------------------
  is running the minimum Kubernetes API version
  is running the minimum kubectl version
pre-kubernetes-setup
--------------------
  control plane namespace does not already exist
  can create non-namespaced resources
  can create ServiceAccounts
  can create Services
  can create Deployments
  can create CronJobs
  can create ConfigMaps
  can create Secrets
  can read Secrets
  can read extension-apiserver-authentication configmap
  no clock skew detected
linkerd-version
---------------
  can determine the latest version
  cli is up-to-date
Status check results are
All the pre-requisites appear to be good right now, and so installation can proceed.The first step of the installation is to setup the Custom Resource Definitions (CRDs) that Linkerd requires. The linkerd cli only prints the resource YAMLs to standard output and does not create them directly in Kubernetes, so you would need to pipe the output to kubectl apply to create the resources in the cluster that you re working with.
$ linkerd install --crds   kubectl apply -f -
Rendering Linkerd CRDs...
Next, run  linkerd install   kubectl apply -f -  to install the control plane.
customresourcedefinition.apiextensions.k8s.io/authorizationpolicies.policy.linkerd.io created
customresourcedefinition.apiextensions.k8s.io/httproutes.policy.linkerd.io created
customresourcedefinition.apiextensions.k8s.io/meshtlsauthentications.policy.linkerd.io created
customresourcedefinition.apiextensions.k8s.io/networkauthentications.policy.linkerd.io created
customresourcedefinition.apiextensions.k8s.io/serverauthorizations.policy.linkerd.io created
customresourcedefinition.apiextensions.k8s.io/servers.policy.linkerd.io created
customresourcedefinition.apiextensions.k8s.io/serviceprofiles.linkerd.io created
Next, install the Linkerd control plane components in the same manner, this time without the crds switch:
$ linkerd install   kubectl apply -f -
namespace/linkerd created
clusterrole.rbac.authorization.k8s.io/linkerd-linkerd-identity created
clusterrolebinding.rbac.authorization.k8s.io/linkerd-linkerd-identity created
serviceaccount/linkerd-identity created
clusterrole.rbac.authorization.k8s.io/linkerd-linkerd-destination created
clusterrolebinding.rbac.authorization.k8s.io/linkerd-linkerd-destination created
serviceaccount/linkerd-destination created
secret/linkerd-sp-validator-k8s-tls created
validatingwebhookconfiguration.admissionregistration.k8s.io/linkerd-sp-validator-webhook-config created
secret/linkerd-policy-validator-k8s-tls created
validatingwebhookconfiguration.admissionregistration.k8s.io/linkerd-policy-validator-webhook-config created
clusterrole.rbac.authorization.k8s.io/linkerd-policy created
clusterrolebinding.rbac.authorization.k8s.io/linkerd-destination-policy created
role.rbac.authorization.k8s.io/linkerd-heartbeat created
rolebinding.rbac.authorization.k8s.io/linkerd-heartbeat created
clusterrole.rbac.authorization.k8s.io/linkerd-heartbeat created
clusterrolebinding.rbac.authorization.k8s.io/linkerd-heartbeat created
serviceaccount/linkerd-heartbeat created
clusterrole.rbac.authorization.k8s.io/linkerd-linkerd-proxy-injector created
clusterrolebinding.rbac.authorization.k8s.io/linkerd-linkerd-proxy-injector created
serviceaccount/linkerd-proxy-injector created
secret/linkerd-proxy-injector-k8s-tls created
mutatingwebhookconfiguration.admissionregistration.k8s.io/linkerd-proxy-injector-webhook-config created
configmap/linkerd-config created
secret/linkerd-identity-issuer created
configmap/linkerd-identity-trust-roots created
service/linkerd-identity created
service/linkerd-identity-headless created
deployment.apps/linkerd-identity created
service/linkerd-dst created
service/linkerd-dst-headless created
service/linkerd-sp-validator created
service/linkerd-policy created
service/linkerd-policy-validator created
deployment.apps/linkerd-destination created
cronjob.batch/linkerd-heartbeat created
deployment.apps/linkerd-proxy-injector created
service/linkerd-proxy-injector created
secret/linkerd-config-overrides created
Kubernetes will start spinning up the data plane components and you should see the following when you list the pods:
kubernetes-api
--------------
  can initialize the client
  can query the Kubernetes API
kubernetes-version
------------------
  is running the minimum Kubernetes API version
  is running the minimum kubectl version
linkerd-existence
-----------------
  'linkerd-config' config map exists
  heartbeat ServiceAccount exist
  control plane replica sets are ready
  no unschedulable pods
  control plane pods are ready
  cluster networks contains all pods
  cluster networks contains all services
linkerd-config
--------------
  control plane Namespace exists
  control plane ClusterRoles exist
  control plane ClusterRoleBindings exist
  control plane ServiceAccounts exist
  control plane CustomResourceDefinitions exist
  control plane MutatingWebhookConfigurations exist
  control plane ValidatingWebhookConfigurations exist
  proxy-init container runs as root user if docker container runtime is used
linkerd-identity
----------------
  certificate config is valid
  trust anchors are using supported crypto algorithm
  trust anchors are within their validity period
  trust anchors are valid for at least 60 days
  issuer cert is using supported crypto algorithm
  issuer cert is within its validity period
  issuer cert is valid for at least 60 days
  issuer cert is issued by the trust anchor
linkerd-webhooks-and-apisvc-tls
-------------------------------
  proxy-injector webhook has valid cert
  proxy-injector cert is valid for at least 60 days
  sp-validator webhook has valid cert
  sp-validator cert is valid for at least 60 days
  policy-validator webhook has valid cert
  policy-validator cert is valid for at least 60 days
linkerd-version
---------------
  can determine the latest version
  cli is up-to-date
control-plane-version
---------------------
  can retrieve the control plane version
  control plane is up-to-date
  control plane and cli versions match
linkerd-control-plane-proxy
---------------------------
  control plane proxies are healthy
  control plane proxies are up-to-date
  control plane proxies and cli versions match
Status check results are
Everything looks good.Setting up the Viz ExtensionAt this point, the required components for the service mesh are setup, but let s also install the viz extension, which provides a good visualization capabilities that will come in handy subsequently. Once again, linkerd uses the same pattern for installing the extension.
$ linkerd viz install   kubectl apply -f -
namespace/linkerd-viz created
clusterrole.rbac.authorization.k8s.io/linkerd-linkerd-viz-metrics-api created
clusterrolebinding.rbac.authorization.k8s.io/linkerd-linkerd-viz-metrics-api created
serviceaccount/metrics-api created
clusterrole.rbac.authorization.k8s.io/linkerd-linkerd-viz-prometheus created
clusterrolebinding.rbac.authorization.k8s.io/linkerd-linkerd-viz-prometheus created
serviceaccount/prometheus created
clusterrole.rbac.authorization.k8s.io/linkerd-linkerd-viz-tap created
clusterrole.rbac.authorization.k8s.io/linkerd-linkerd-viz-tap-admin created
clusterrolebinding.rbac.authorization.k8s.io/linkerd-linkerd-viz-tap created
clusterrolebinding.rbac.authorization.k8s.io/linkerd-linkerd-viz-tap-auth-delegator created
serviceaccount/tap created
rolebinding.rbac.authorization.k8s.io/linkerd-linkerd-viz-tap-auth-reader created
secret/tap-k8s-tls created
apiservice.apiregistration.k8s.io/v1alpha1.tap.linkerd.io created
role.rbac.authorization.k8s.io/web created
rolebinding.rbac.authorization.k8s.io/web created
clusterrole.rbac.authorization.k8s.io/linkerd-linkerd-viz-web-check created
clusterrolebinding.rbac.authorization.k8s.io/linkerd-linkerd-viz-web-check created
clusterrolebinding.rbac.authorization.k8s.io/linkerd-linkerd-viz-web-admin created
clusterrole.rbac.authorization.k8s.io/linkerd-linkerd-viz-web-api created
clusterrolebinding.rbac.authorization.k8s.io/linkerd-linkerd-viz-web-api created
serviceaccount/web created
server.policy.linkerd.io/admin created
authorizationpolicy.policy.linkerd.io/admin created
networkauthentication.policy.linkerd.io/kubelet created
server.policy.linkerd.io/proxy-admin created
authorizationpolicy.policy.linkerd.io/proxy-admin created
service/metrics-api created
deployment.apps/metrics-api created
server.policy.linkerd.io/metrics-api created
authorizationpolicy.policy.linkerd.io/metrics-api created
meshtlsauthentication.policy.linkerd.io/metrics-api-web created
configmap/prometheus-config created
service/prometheus created
deployment.apps/prometheus created
service/tap created
deployment.apps/tap created
server.policy.linkerd.io/tap-api created
authorizationpolicy.policy.linkerd.io/tap created
clusterrole.rbac.authorization.k8s.io/linkerd-tap-injector created
clusterrolebinding.rbac.authorization.k8s.io/linkerd-tap-injector created
serviceaccount/tap-injector created
secret/tap-injector-k8s-tls created
mutatingwebhookconfiguration.admissionregistration.k8s.io/linkerd-tap-injector-webhook-config created
service/tap-injector created
deployment.apps/tap-injector created
server.policy.linkerd.io/tap-injector-webhook created
authorizationpolicy.policy.linkerd.io/tap-injector created
networkauthentication.policy.linkerd.io/kube-api-server created
service/web created
deployment.apps/web created
serviceprofile.linkerd.io/metrics-api.linkerd-viz.svc.cluster.local created
serviceprofile.linkerd.io/prometheus.linkerd-viz.svc.cluster.local created
A few seconds later, you should see the following in your pod list:
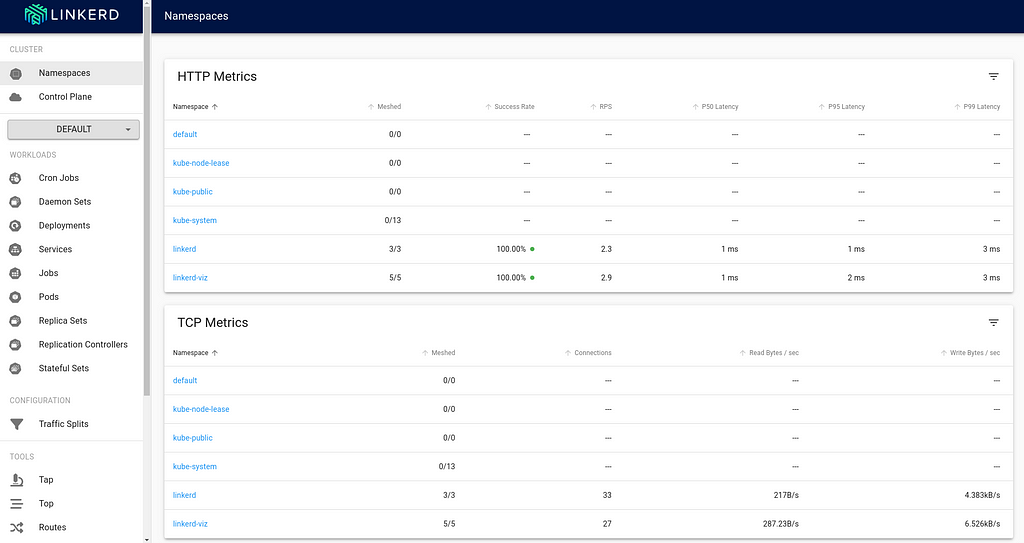
The viz components live in the linkerd-viz namespace.You can now checkout the viz dashboard:
$ linkerd viz dashboard
Linkerd dashboard available at:
http://localhost:50750
Grafana dashboard available at:
http://localhost:50750/grafana
Opening Linkerd dashboard in the default browser
Opening in existing browser session.
The Meshed column indicates the workload that is currently integrated with the Linkerd control plane. As you can see, there are no application deployments right now that are running.Injecting the Linkerd Data Plane componentsThere are two ways to integrate Linkerd to the application containers:1 by manually injecting the Linkerd data plane components 2 by instructing Kubernetes to automatically inject the data plane componentsInject Linkerd data plane manuallyLet s try the first option. Below is a simple nginx-app that I will deploy into the cluster:
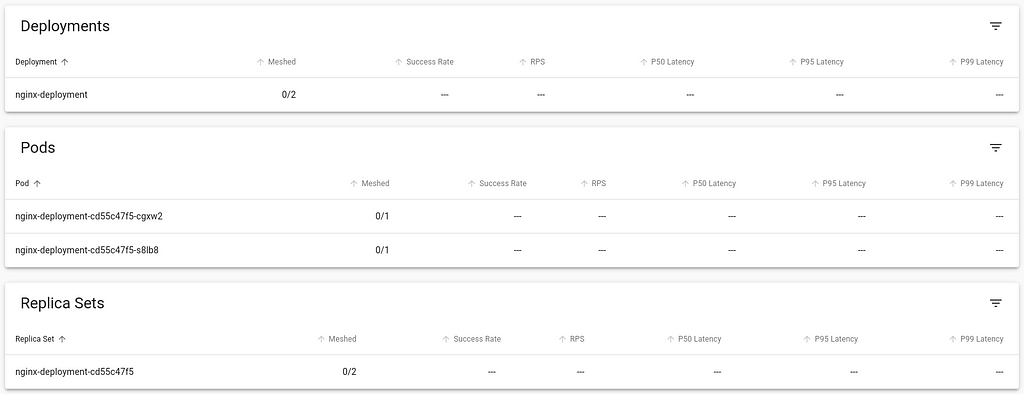
Back in the viz dashboard, I do see the workload deployed, but it isn t currently communicating with the Linkerd control plane, and so doesn t show any metrics, and the Meshed count is 0:Looking at the Pod s deployment YAML, I can see that it only includes the nginx container:
Let s directly inject the linkerd data plane into this running container. We do this by retrieving the YAML of the deployment, piping it to linkerd cli to inject the necessary components and then piping to kubectl apply the changed resources.
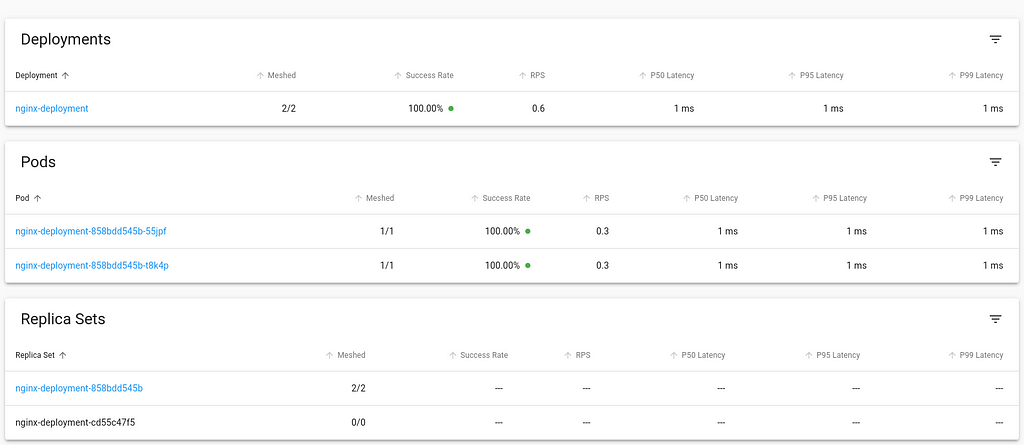
Back in the viz dashboard, the workload now is integrated into Linkerd control plane.Looking at the updated Pod definition, we see a number of changes that the linkerd has injected that allows it to integrate with the control plane. Let s have a look:
At this point, the necessary components are setup for you to explore Linkerd further. You can also try out the jaeger and multicluster extensions, similar to the process of installing and using the viz extension and try out their capabilities.Inject Linkerd data plane automaticallyIn this approach, we shall we how to instruct Kubernetes to automatically inject the Linkerd data plane to workloads at deployment time.We can achieve this by adding the linkerd.io/inject annotation to the deployment descriptor which causes the proxy injector admission hook to execute and inject linkerd data plane components automatically at the time of deployment.
This annotation can also be specified at the namespace level to affect all the workloads within the namespace. Note that any resources created before the annotation was added to the namespace will require a rollout restart to trigger the injection of the Linkerd components.Uninstalling LinkerdNow that we have walked through the installation and setup process of Linkerd, let s also cover how to remove it from the infrastructure and go back to the state prior to its installation.The first step would be to remove extensions, such as viz.
A brand-new version 0.0.9 of RcppSpdlog got onto CRAN overnight. RcppSpdlog bundles spdlog, a wonderful header-only C++ logging library with all the bells and whistles you would want that was written by Gabi Melman, and also includes fmt by Victor Zverovich.
This release contains two changes. First, we extend usability by offering both a set of simple R functions for logging from R, and a matching set of functions at the C++ level that are directly callable (and exported) from this package (so that client packages do not need to compile). Both these changes are described (as sections seven and eight) in the vignette. Second, while we were working on this Gabi released version 1.11.0 upstream so we included this as well.
The NEWS entry for this release follows.
A new release 0.4.20 of RProtoBuf arrived on CRAN earlier today. RProtoBuf provides R with bindings for the Google Protocol Buffers ( ProtoBuf ) data encoding and serialization library used and released by Google, and deployed very widely in numerous projects as a language and operating-system agnostic protocol.
This release is somewhat mechanical and in the spirit of many other recent releases. clang-15 is, as more recent compilers do, more stringent on definitions and wants to see some void in argument-less signatures. Happy to oblige. At the same time, GitHub Actions started to nag us about minimum versions of node code so an upgrade to a newer action is warranted, again as with many other affected packages. We also found another http:// URL hiding somewhere so that was cleaned. Lastly, it appears Protocol Buffers themselves moved on and now need / prefer C++17 so were happy to oblige.
The following section from the NEWS.Rd file has full details.
Changes in RProtoBuf version 0.4.20 (2022-11-02)
Two function prototype were updated for clang-15.
GitHub Actions were updated to checkout version 3.
One more http:// URL was updated to https://
The package compilation is now donw with C++17 as the Protocol Buffer headers require it (and clang-15 nags otherwise).
So this week I recycled a talk I'd given in the past, about how even using
extremely simple parsers allows a lot of useful static-analysis to be done,
for specific niche use-cases.
This included examples of scanning comments above classes to ensure they
referred to the appropriate object, ensuring that specific function
calls always included a specific (optional) parameter, etc.
Nothing too complex, but I figured I'd give a new example this time, and
I remembered I'd recently written a bunch of functions for an interpreter
which I'd ordered quite deliberately.
Assume you're writing a BASIC interpreter, you need to implement a bunch of
built-in maths functions such as SIN, COS, TAN, then some string-related
functions LEFT$, RIGHT$, MID$, etc.
When it comes to ordering there are a couple of approaches:
Stick them all in one package:
builtins/builtins.go
Create a package and group them:
builtins/maths.go
builtins/string.go
.. etc
Personal preference probably dictates the choice you make, but either way I think it would be rational and obvious that you'd put the functions in alphabetical order:
I did that myself, and I wrote a perl-script to just parse the file using a simple regexp "^func\s+([^(]+)\(" but then I figured this was a good time to write a real static-analysis tool.
The golang environment is full of trivial little linters for various purposes, and the standard "go vet .." driver makes it easy to invoke them. Realizing that I was going to get driven in the same way it was obvious I'd write something called "alphaVet".
So anyway, half written for a talk, half-written because of the name:
Golang linter that reports failures if functions aren't in alphabetical order
Department of Education confirms 12,544 Ukrainian pupils currently enrolled in Irish schools
#GreensInGovernment
The Department of Education can confirm that as of 1 November, 12,544 Ukrainian pupils have been enrolled in schools across Ireland. Out of that figure, 7,948 of these pupils have been accommodated in primary schools while 4,596 pupils have enrolled in post-primary schools.
To assist with the transition of Ukrainian refugees and their families into Irish schools Regional Education and Language Teams (REALT) continue to operate, hosted by the 16 regional education and training boards around Ireland and staffed by regionally based education support personnel.
These teams are ensuring that clear, accessible information flows are in place between schools, local education support services and national support structures in relation to people arriving from Ukraine.
Information for parents in Ukrainian and Russian on accessing school places is available on gov.ie/Ukraine.
The Department will continue to publish figures on the enrolment of Ukrainian children each month.
Carpe Jugulum is the 23rd Discworld novel and the 6th witches
novel. I would not recommend reading it before Maskerade, which introduces Agnes.
There are some spoilers for Wyrd
Sisters, Lords and Ladies, and
Maskerade in the setup here and hence in the plot description
below. I don't think they matter that much, but if you're avoiding all
spoilers for earlier books, you may want to skip over this one. (You're
unlikely to want to read it before those books anyway.)
It is time to name the child of the king of Lancre, and in a gesture of
good will and modernization, he has invited his neighbors in Uberwald to
attend. Given that those neighbors are vampires, an open invitation was
perhaps not the wisest choice.
Meanwhile, Granny Weatherwax's invitation has gone missing. On the plus
side, that meant she was home to be summoned to the bedside of a pregnant
woman who was kicked by a cow, where she makes the type of hard decision
that Granny has been making throughout the series. On the minus side, the
apparent snub seems to send her into a spiral of anger at the lack of
appreciation.
Points off right from the start for a plot based on a misunderstanding and
a subsequent refusal of people to simply talk to each other. It is partly
engineered, but still, it's a cheap and irritating plot.
This is an odd book.
The vampires (or vampyres, as the Count wants to use) think of themselves
as modern and sophisticated, making a break from the past by attempting to
overcome such traditional problems as burning up in the sunlight and fear
of religious symbols and garlic. The Count has put his family through
rigorous training and desensitization, deciding such traditional
vulnerabilities are outdated things of the past. He has, however, kept
the belief that vampires are at the top of a natural chain of being,
humans are essentially cattle, and vampires naturally should rule and feed
on the population. Lancre is an attractive new food source. Vampires
also have mind control powers, control the weather, and can put their
minds into magpies.
They are, in short, enemies designed for Granny Weatherwax, the witch
expert in headology. A shame that Granny is apparently off sulking.
Nanny and Agnes may have to handle the vampires on their own, with the
help of Magrat.
One of the things that makes this book odd is that it seemed like
Pratchett was setting up some character growth, giving Agnes a chance to
shine, and giving Nanny Ogg a challenge that she didn't want. This sort
of happens, but then nothing much comes of it. Most of the book is the
vampires preening about how powerful they are and easily conquering
Lancre, while everyone else flails ineffectively. Pratchett does pull
together an ending with some nice set pieces, but that ending doesn't
deliver on any of the changes or developments it felt like the story was
setting up.
We do get a lot of Granny, along with an amusingly earnest priest of Om
(lots of references to Small Gods here,
while firmly establishing it as long-ago history). Granny is one of my
favorite Discworld characters, so I don't mind that, but we've seen Granny
solve a lot of problems before. I wanted to see more of Agnes, who is the
interesting new character and whose dynamic with her inner voice feels
like it has a great deal of unrealized potential.
There is a sharp and condensed version of comparative religion from
Granny, which is probably the strongest part of the book and includes one
of those Discworld quotes that has been widely repeated out of context:
"And sin, young man, is when you treat people as things. Including
yourself. That's what sin is."
"It's a lot more complicated than that "
"No. It ain't. When people say things are a lot more complicated
than that, they means they're getting worried that they won t like the
truth. People as things, that's where it starts."
This loses a bit in context because this book is literally about treating
people as things, and thus the observation feels more obvious when it
arrives in this book than when you encounter it on its own, but it's still
a great quote.
Sadly, I found a lot of this book annoying. One of those annoyances is a
pet peeve that others may or may not share: I have very little patience
for dialogue in phonetically-spelled dialect, and there are two
substantial cases of that here. One is a servant named Igor who speaks
with an affected lisp represented by replacing every ess sound with th,
resulting in lots of this:
"No, my Uncle Igor thtill workth for him. Been thtruck by lightning
three hundred timeth and thtill putth in a full night'th work."
I like Igor as a character (he's essentially a refugee from The
Addams Family, which adds a good counterpoint to the malicious and
arrogant evil of the vampires), but my brain stumbles over words like
"thtill" every time. It's not that I can't decipher it; it's that the
deciphering breaks the flow of reading in a way that I found not at all
fun. It bugged me enough that I started skipping his lines if I couldn't
work them out right away.
The other example is the Nac Mac Feegles, who are... well, in the book,
they're Pictsies and a type of fairy, but they're Scottish Smurfs, right
down to only having one female (at least in this book). They're
entertainingly homicidal, but they all talk like this:
"Ach, hins tak yar scaggie, yer dank yowl callyake!"
I'm from the US and bad with accents and even worse with accents
reproduced in weird spellings, and I'm afraid that I found 95% of
everything said by Nac Mac Feegles completely incomprehensible to the
point where I gave up even trying to read it. (I'm now rather worried
about the Tiffany Aching books and am hoping Pratchett toned the dialect
down a lot, because I'm not sure I can deal with more of this.)
But even apart from the dialect, I thought something was off about the
plot structure of this book. There's a lot of focus on characters who
don't seem to contribute much to the plot resolution. I wanted more of
the varied strengths of Lancre coming together, rather than the focus on
Granny. And the vampires are absurdly powerful, unflappable, smarmy, and
contemptuous of everyone, which makes for threatening villains but also
means spending a lot of narrative time with a Discworld version of
Jacob Rees-Mogg. I
feel like there's enough of that in the news already.
Also, while I will avoid saying too much about the plot, I get very
suspicious when older forms of oppression are presented as good
alternatives to modernizing, rationalist spins on exploitation. I see
what Pratchett was trying to do, and there is an interesting point here
about everyone having personal relationships and knowing their roles (a
long-standing theme of the Lancre Discworld stories). But I think the
reason why there is some nostalgia for older autocracy is that we only
hear about it from stories, and the process of storytelling often creates
emotional distance and a patina of adventure and happy outcomes. Maybe
you can make an argument that classic British imperialism is superior to
smug neoliberalism, but both of them are quite bad and I don't want either
of them.
On a similar note, Nanny Ogg's tyranny over her entire extended clan
continues to be played for laughs, but it's rather unappealing and seems
more abusive the more one thinks about it. I realize the witches are not
intended to be wholly good or uncomplicated moral figures, but I want to
like Nanny, and Pratchett seems to be writing her as likable, even though
she has an astonishing lack of respect for all the people she's related
to. One might even say that she treats them like things.
There are some great bits in this book, and I suspect there are many
people who liked it more than I did. I wouldn't be surprised if it was
someone's favorite Discworld novel. But there were enough bits that
didn't work for me that I thought it averaged out to a middle-of-the-road
entry.
Followed by The Fifth Elephant in publication order. This is the
last regular witches novel, but some of the thematic thread is picked up
by The Wee Free Men, the first Tiffany Aching novel.
Rating: 7 out of 10
Someone recently asked what yak shaving means and, because I am a
professional at this pastime, I figured I would share my most recent
excursion in the field.
As a reminder, "yak shaving" describes a (anti?) pattern by which you
engage in more and more (possibly useless) tasks that lead you further
and further away from your original objective.
The path I took through the yak heard is this:
i wondered if i can use my home network to experiment with another
VPN software (e.g. Wireguard instead of IPsec)
I wasn't happy with that, so i tried an IPv6 tunnel
that broke after a few minutes, so i went on to try deploying
Wireguard with Puppet), which involved reviewing about 4
different Puppet modules
while I was there, I might as well share those findings with the
community, so I publish that as a blog post
someone else mentions that Nebula (from Slack) is a thing,
but after investigation, it's not well packaged in Debian, so
didn't test it, but add it to the blog post
now that I found the right Puppet module, I tried to deploy
it with Puppet's g10k, which requires me to input a checksum
I got lazy and figured if i would put the checksum wrong, it would
tell me what the right checksum was, but it didn't: instead it
silently succeeded instead of failing, which seemed really bad
then I looked upstream for such a bug report and saw that the
Debian package was many versions behind and, because I'm on
the Golang packaging team, I figured I would just do the
upgrade myself
... but then tried to readd it to Debian CI instead,
which didn't work
At that point, I had given up, after shaving a 12th yak. Thankfully, a
kind soul provided a working test suite and I was able to roll
back all those parenthesis and:
test the g10k package and confirm it works (and checks the
checksums)
Also notice the 8th yak, above, which might be a security issue. I
wasn't able to confirm it, because g10k does some pretty aggressive
caching, and I could "reproduce" it in the sense that the checksum
wasn't checked if it exists in the cache. So it might have just been
that I had actually already deployed the module before adding the
checksum... but I still had that distressing sentiment:
<anarcat> there's a huge yak breathing down my neck with "CVE" written in large red letters on the side
<anarcat> i'm trying to ignore it, it stinks like hell
Hopefully it's nothing to worry about. Right? Riiight.
Oh. And obviously, writing this blog post is the sugar on top, the one
last yak that is self-documented here.
A new version 0.1.4 of the tint package arrived at CRAN today. tint provides a style not unlike Tufte for use in html and pdf documents created from markdown. The github repo shows several examples in its README, more as usual in the package documentation.
This is the first release in over two years and it brings a few incremental changes which are described in detail below. The trigger was an email from CRAN desiring compacted pdf files inside the package sources. Which, coincidentally, was made a default about a year ago in the build.r script from littler I use to make packages. But as we had not updated tint this has not reached CRAN. So there.
The set of changes follows, which includes a helpful contributed PR for which we are always thankful. I also improved table rendering, most other changes are packaging mechanics.
Changes in tint version 0.1.4 (2022-11-01)
Added continuous integration at GitHub using run.sh
Non-margin reference in html mode now have an improved display (David Selby and Dirk in #47)
The LaTeX package array is now installed for improved table support (Dirk addressing #48)
Minor updates made the package directory and README.md
GitHub Actions were updated to checkout version 3.
A new maintenance release 0.0.6 of RcppXts is now on CRAN. The RcppXts package demonstrates how to access the export C API of xts which we contributed a looong time ago.
This release, like so many these days, was triggered by clang-15 wanting to see a void in an otherwise argument-less signature. We also updated a GitHub Action to avoid another nag from there.
The NEWS entries follow.
Changes in version 0.0.6 (2022-08-05)
One function prototype was updated for clang-15.
GitHub Actions were updated to checkout version 3.
I hope you had a nice Halloween!
I've collected together some songs that I've enjoyed over the last couple of
years that loosely fit a theme: ambient, instrumental, experimental, industrial,
dark, disconcerting, etc. I've prepared a Spotify playlist of most of
them, but not all. The list is inline below as well, with many (but not all)
tracks linking to Bandcamp, if I could find them there.
This is a bit late, sorry. If anyone listens to something here and has any
feedback I'd love to hear it.
(If you are reading this on an aggregation site, it's possible the embeds won't
work. If so, click through to my main site)
Spotify playlist: https://open.spotify.com/playlist/3bEvEguRnf9U1RFrNbv5fk?si=9084cbf78c364ac8;
The list, with Bandcamp embeds where possible:
Review: What Makes This Book So Great, by Jo Walton
Publisher:
Tor
Copyright:
January 2014
ISBN:
0-7653-3193-4
Format:
Hardcover
Pages:
447
Jo Walton, in addition to being an excellent science fiction and fantasy
writer, is a prodigious reader and frequent participant in on-line SFF
book discussion going back to the Usenet days. This book is a collection
of short essays previously published on Tor.com between July 2008 and February 2011. The unifying theme is that
Walton regularly re-reads her favorite books, and each essay (apart from
some general essays on related topics) is about why this specific book is
one that she re-reads, and (as the title says) what makes it so great.
Searching for the title of one of the essays turns it up on Tor.com still,
so this is one of those collections that you don't have to buy since you
can read its contents on-line for free. That said, it looks like these
essays were from before Tor.com started classifying posts into series, so
it's going to be challenging to track them down in the huge number of
other articles Walton has written for the site. (That said, you can't go
far wrong by reading any of her essays at random.)
I read these essays as they were originally published, so this was also a
re-read for me, but it had been a while. I'm happy to report that they
were just as much fun the second time.
In the introduction and in the final essay of this collection, Walton
draws a distinction between what she's doing, criticism, and reviewing.
As someone else who writes about books (in a far more amateur fashion), I
liked this distinction.
The way I'd characterize it is that criticism is primarily about the work:
taking it apart to see what makes it tick, looking for symbolism and
hidden meanings, and comparing and contrasting other works that are
tackling similar themes. I've often finished a work of criticism and
still had no idea if the author enjoyed reading the work being criticized
or not, since that isn't the point.
Reviewing is assistance to consumers and focuses more on the reader: would
you enjoy this book? Is it enjoyable to read? Does it say something new?
What genre and style is it in, so that you can match that to your tastes?
Talking about books is neither of those things, although it's a bit closer
to reviewing. But the emphasis is on one's personal enjoyment instead of
attempting to review a product for others. When I talk about books with
friends, I talk primarily about what bits I liked, what bits I didn't
like, where the emotional beats were for me, and what interesting things
the book did that surprised me or caught my attention. One can find a
review in there, and sometimes even criticism, but the focus and the
formality is different. (And, to be honest, my reviews are more on the
"talking about the book" side than fully proper reviews.)
These essays are indeed talking about books. They're all re-reads; in
some cases the first re-read, but more frequently the latest of many
re-reads. There are lots of spoilers, which makes for bad reviews (the
target audience of a review hasn't read the book yet) but good fodder for
conversations about books. (The spoilers are mostly marked, but if you're
particularly averse to spoilers, you'll need to read carefully.) Most of
the essays are about a single book, but there are a few on more general
topics, such as Walton's bafflement that anyone would skim a novel.
Since these are re-reads, and the essays collected here are more than a
decade old, the focus is on older books. Some of them are famous: Vinge's
A Fire Upon the Deep and
A Deepness in the Sky, early Le Guin,
Samuel Delaney's SF novels, Salmon Rushdie's Midnight's Children.
Some of them are more obscure. C.J. Cherryh, for example, is a writer who
never seems to get much on-line attention, but who is one of Walton's
favorites.
Most of the essays stand alone or come in small clusters about a writer,
often sprinkled through the book instead of clumped together. (The book
publishes the essays in the same order they originally appeared on
Tor.com.) The two largest groups of essays are re-readings of every book
in Steven Brust's Vlad Taltos universe (including
Brokedown Palace and the
Paarfi books) up to Jhegaala, and every book in Lois McMaster Bujold's Miles
Vorkosigan series up to Diplomatic
Immunity. This is fitting: those are two of the great series of science
fiction, but don't seem to be written about nearly as much as I would
expect.
There are over 130 essays in a 447 page book, so there's a lot of material
here and none of them outlive their welcome. Walton has a comfortable,
approachable style that bubbles with delight and appreciation for books.
I think it's impossible to read this collection without wanting to read
more, and without adding several more books to the ever-teetering to-read
pile.
This is perhaps not the best source of reading recommendations if you
dislike spoilers, although it can be used for that if you read carefully.
But if you love listening to conversations about the genre and talking
about how books bounce off each other, and particularly if you have read
most of these books already or don't mind spoilers, this collection is a
delight. If you're the type of SFF reader who likes reading the reviews
in Locus or is already reading Tor.com, highly recommended.
Rating: 8 out of 10
A new minor release 0.2.2 of our RcppRedis package arrived on CRAN this evening. RcppRedis is one of several packages connecting R to the fabulous Redis in-memory datastructure store (and much more). RcppRedis does not pretend to be feature complete, but it may do some things faster than the other interfaces, and also offers an optional coupling with MessagePack binary (de)serialization via RcppMsgPack. The package has carried production loads for several years now.
This packages now brings a neat enhancement to the real-time data plotter code (and example) I have been using with for a while now. Paul Murrell kindly suggested dev.hold() and dev.flush() when I inquired how to minimize flicker from frequent updated. And this is perfect. I can now keep several data displays on during market hours without being distracted by flicker . It just updates, smooth as silk. Also included in the release are the usual two updates so en vogue these days: a (sole) sprinkling of void to appease clang-15, and an update the GitHub Action for checkout. Both silence some nags we would rather not see.
The detailed changes list follows.
Changes in version 0.2.2 (2022-10-31)
Thanks to a suggestion by Paul Murrell, the real-time chart demo now uses dev.hold() and.flush() for flicker-free updates.
One function prototype was updated for clang-15.
GitHub Actions were updated to checkout version 3.
An Bord Plean la conceded that the N6 Galway City Ring Road was in contravention with the National Climate Action plan.
In planning for how we adapt to and mitigate climate change, the UN IPCC AR6 report summarised the state of research globally and modelled nearly 3000 scenarios. The scenarios that kept us below 2 degrees of warming (our Paris agreement commitments) overwhelmingly depended on a move away from car-dependent societies and relied on car-free cities. This report was signed off by every world government.
All EU and national modelling agrees. Accordingly our national Climate Action plan prepares for this global move from cars. It involves a reduction in car traffic, heavy investment in public transport and active travel (walking and cycling). This is essential as the research shows this works, and takes up to 84% less energy for transport in cities.
The N6GCRR plan ignored this, and assumed an increase in car traffic of up to 49%. It in practice would have locked in car dependency when we don t expect there to be enough materials (lithium, etc for batteries) or energy to support that number of cars.
Across Europe and the world we have seen how to move from cars in cities: rail, reliable bus services with dedicated bus corridors; safe, segregated cycle lanes, public space design that enables walking, cycling by keeping distances short the 15 minute city concept of having schools, shops, transport hubs less than 15 minutes from your door. From Paris, removing 40% of cars from the city, now removing a lane from the Peripherique (its ring road), to Korea where expressways in cities have been removed to improve traffic as part of its better design. In Ireland, Dublin has seen a 49% drop in peak-time traffic over recent decades with improved public transport and cycling.
But in Galway we ve ignored all this: not a kilometre of segregated cycle lane added, as there has been an over 80% drop in pupils cycling to school since the 1980s, amplifying traffic as parents commute to drop them to school, making roads more dangerous. No bus route passes over the Quincentennial bridge.
Rather than fix the traffic in Galway, a ring road would induce more traffic as the existing Bothar na dTreabh / Quincintennial bridge did; the current road opened up Knocknacarra for development; a new motorway to Barna would open up Barna for more development.
This is zombie planning: a roads plan from the 1990s lives on, while our County Development Plan has moved the focus to creating new satellite towns in Ardaun and Garraun instead. When all new business wants to be on the East, the new developments need to be near them; new schools are being built on the East, not the West. Rail is being double-tracked to Oranmore (and on to Athenry) to provide commuter rail to Renmore and the growing towns. This reduces the demand for cross-city commuting.
Active travel and public transport development in the city has been stalled awaiting the ring road. This needs to be implemented as quickly as possible. The bus corridor from Salthill (via the schools) to Oranmore (via the businesses at Ballybrit, Parkmore) needs to be completed; this will involve a bus lane on the bridge. The N6GCRR said this was impossible without a new bridge for cars; Dublin s experience with the quays shows otherwise. If we get a fraction of the drop Dublin has seen, the traffic problem will be solved, as shown when the schools are out for holidays.
The NTA and Galway councils have been stuck in thinking from 30 years ago. They assume that traffic cannot be reduced, only added; the ABP inspector agreed, despite overwhelming evidence elsewhere. We need to implement what has been shown to work elsewhere as quickly as possible; the funding is in place but the will and vision to do so has been lacking.
A new release 0.3.12 of RcppGSL is now on CRAN. The RcppGSL package provides an interface from R to the GNU GSL by relying on the Rcpp package.
This release accomodates, just like so many other releases this week, the more stringent views of clang-15 about what a correct function prototype is. While we were at it, an updatet to GitHub Actions was made as well.
The NEWS entry follows:
Changes in version 0.3.12 (2022-10-30)
Two function prototypes were updated for clang-15.
GitHub Actions were updated to checkout version 3.
A minor maintenance release for the RcppBDT package is now on CRAN.
The RcppBDT package is an early adopter of Rcpp and was one of the first packages utilizing Boost and its Date_Time library. The now more widely-used package anytime is a direct descentant of RcppBDT.
This release accomodates, just like so many other releases this week, the more stringent views of clang-15 about what a correct function prototype is. While we were at it, an updatet to GitHub Actions was made as well.
The NEWS entry follows:
Changes in version 0.2.6 (2022-10-30)
A function prototype was updated for clang-15.
GitHub Actions were updated to checkout version 3.
A new release of our RApiDatetime package is now on CRAN.
RApiDatetime provides a number of entry points for C-level functions of the R API for Date and Datetime calculations. The functions asPOSIXlt and asPOSIXct convert between long and compact datetime representation, formatPOSIXlt and Rstrptime convert to and from character strings, and POSIXlt2D and D2POSIXlt convert between Date and POSIXlt datetime. Lastly, asDatePOSIXct converts to a date type. All these functions are rather useful, but were not previously exported by R for C-level use by other packages. Which this package aims to change.
This release accomodates, just like so many other releases this week, the more stringent views of clang-15 about what a correct function prototype is. While we were at, updates to GitHub Actions and https URL were made as well.
Changes in RApiDatetime version 0.0.7 (2022-10-30)
A function prototype was updated for clang-15.
GitHub Actions were updated to checkout version 3.
Several remaining http:// URLs were converted to https://.

 Armadillo is a powerful and expressive C++ template library for linear algebra and scientific computing. It aims towards a good balance between speed and ease of use, has a syntax deliberately close to Matlab, and is useful for algorithm development directly in C++, or quick conversion of research code into production environments. RcppArmadillo integrates this library with the R environment and language and is widely used by (currently) 1027 packages other packages on CRAN, downloaded 26.9 million times (per the partial logs from the cloud mirrors of CRAN), and the CSDA paper (preprint / vignette) by Conrad and myself has been cited 503 times according to Google Scholar.
This release reflect as new upstream bugfix release 11.4.2 made recently by Conrad. To accomodate CRAN and their preference for at most a release per month, we held it back since the 11.4.0 release early October. As we usually do, we generally update once upstream Armadillo releases are made. When we do not immediately release to CRAN (in order to lower the release cadence), we make those interim releases available via GitHub source and the Rcpp drat repo.
This release also brings a rearranged, and as we think, simplified layout of the header files. All existing locations are still supported but we will be starting a (very patient and slow) transition at some point.
The full set of changes (since the last CRAN release 0.11.4.0.1) follows.
 So this week I recycled a talk I'd given in the past, about how even using
extremely simple parsers allows a lot of useful static-analysis to be done,
for specific niche use-cases.
This included examples of scanning comments above classes to ensure they
referred to the appropriate object, ensuring that specific function
calls always included a specific (optional) parameter, etc.
Nothing too complex, but I figured I'd give a new example this time, and
I remembered I'd recently written a bunch of functions for an interpreter
which I'd ordered quite deliberately.
Assume you're writing a BASIC interpreter, you need to implement a bunch of
built-in maths functions such as
 I hope you had a nice Halloween!
I've collected together some songs that I've enjoyed over the last couple of
years that loosely fit a theme: ambient, instrumental, experimental, industrial,
dark, disconcerting, etc. I've prepared a Spotify playlist of most of
them, but not all. The list is inline below as well, with many (but not all)
tracks linking to Bandcamp, if I could find them there.
This is a bit late, sorry. If anyone listens to something here and has any
feedback I'd love to hear it.
(If you are reading this on an aggregation site, it's possible the embeds won't
work. If so, click through to my main site)
Spotify playlist: