Search Results: "tar"

19 May 2009

James Morrison: Running home

I've been running home from work on mondays for the last couple months. I started with the direct 3.5 mile route home. Now each week I vary my route a bit, last night I took Geary most of the way west. However, while running I was thinking I should find as many hills to take on the way home with only a small amount of back tracking. Well this 5.3 mile run looks to be a good approximation. Anyone up for a run next monday evening?

Martin-Éric Racine: Invandringskonsult

In close to 11 years of living in Europe, I've accomplished plenty beyond working in the high-tech sector: I've also been fairly active in Immigration Policy, especially on aspects that affect migrant labor. Because of this, I keep on getting more and more requests to produce statements or to appear on panels to discuss issues pertaining to migrant labor and to immigrants' integration. The hot topic of last week was Swedish language for immigrants, the crux of the issue being that even though Swedish has an official language status in Finland, in practice, it is pretty much impossibly for immigrants to register their kids at the Swedish language school, to claim public services in Swedish or, even more so, to request labor training in the Swedish language at the Employment Office. The weekly newspaper Helsinki Times, in collaboration with the media think tank Magma, recently conduced a survey of the immigrant population, to find out how much they know about Swedish culture in Finland and about the Swedish language. It was in this context that the Helsinki Times and the national television's Swedish programming (FST) asked for an interview with yours truly, because I have recently visited the Ministry of Employment and Economics with a concrete proposal to facilitate the availability of labor training in the Swedish language. This FST webcast, starting at 16:03 minutes into the show, and the above Helsinki Times article provide more details about the context and about my proposal to the Ministry.

Martin Michlmayr: SheevaPlug lenny tar ball and SD cards

I updated my SheevaPlug installation instructions today to document how to boot from an SD card. The u-boot boot loader shipped with the SheevaPlug doesn't have SD/MMC card support, but PlugComputer forum user kwonsk created one that does (and which works pretty well, except for not working with some SD cards).

Joey Hess: "whatcha reading?"

I used to hate that question, particularly in high school, when showing my interlocutor the cover of whatever book I was tearing through was almost certain to end that conversation cold. Maybe that's part of why I switched to reading ebooks as soon as it was practical? Anyway, these days I'm happy to let you know what I'm reading; I just added my 1000th book on GoodReads. The easiest way to explain GoodReads is that it's like Netflix's movie rating and recommendation system, except it can't automatically know what you've got checked out, and it doesn't really do many recommendations, sadly. But it's good about showing you what friends are reading. In other words, it's a social networking site around books. One of several, though the others I've tried seemed clunkier, or too flashy. Goodreads is fairly easy to use, though the UI could use some work in a few places. It's not been especially burdensome to note when I start and finish each book. The best part is that it can keep track of books I want to read. Rating things on a five star system is not something I'm particularly good or consistant at, nor something I want to spend much time on, but I have painlessly rated about 500 books so far, as well as importing 500 more, unrated, from a list of books I read a decade ago. (500 others from that list failed to import.) I'd like to get a high percent of the books I've read recorded there, so I can a) get a grip on just how many books that is (guessing in the 3 thousand range?) and b) avoid accidental rereads and maybe remember some good books I've not read in a while. Of course, as when using any service that silos my data these days, I have to worry about getting it back out. For at least the most important bit -- the list of books, dates, and ratings, GoodReads has a good data export capability, though it's a bit hard to find (hidden here) and not ameanable to automated backups. (Aside: Is anyone working on a one-stop utility that can automatically back up your data from all web silos? Needed.) For the past six months or so, I've been in a bit of a dry spell for finding good new fiction; reading formal book review sites wasn't working for me (most reviews spoil books for me, or just turn me off to them); and ebooks cut down on that library serendipity. I think using this site is helping to break the drought for me, and I'm curious: Whatcha reading? PS: Thanks to whoever sent me the The Design of Everyday Things (your name wasn't listed). I especially like that it's a used copy. Had that on my wishlist and been wanting to read that forever!

18 May 2009

Gunnar Wolf: Summertime, summertime!

Summertime, summertime!
Finally, temperatures are back to sanity, and the air is no longer a mass of dust. For us Mexicans (well, for us central-Mexicans), spring is the hot, dry season. In spring, we usually reach up to 30 C... Not too much for many people, but hellish for me. Summer is much more palatable, having decently sunny days, cloudy evenings and a nice shower as it gets dark. Even if it is a bit harder for a cyclist to take the streets, I think this is my favorite season. This year, we had several (and early!) false starts. I have come to hate April/May's heath waves (that means I am usually grumpy for my birthday). But finally, we have had almost a week of cloudy skies, with almost daily rains. That makes me happy. But I am even happier when I come to work to my office, look out the window, and am not greeted anymore with a 5Km visibility range, but with 20Km. Mind you, this photo was taken past 5PM, when the sky turns nice and gray (just as I've proclaimed my life to be). According to the Weather Channel's information on Mexico City, we currently have 16.1Km Which makes sense, as I can no longer see the Chiquihuite mountain marking the Northern part of the city, but I can perfectly see some buildings near Polanco. The view earlier in the day was... Beautiful, partly perhaps because of the contrast just with last week's. Oh, and yes - Once again, thank you very much my dear University. Instead of the closed cubicles many people spend their hours in, this relaxing view was taken from my office's window. I love it!

Ingo Juergensmann: IPv6 enabled WWW certification program

The IPv6 Forum offers a free WWW certification program and logo for IPv6 enabled sites. You can find there a ISP certification program as well.

Well, it's not a big deal. No rocket science. But I think it might somewhat help to raise awareness level for IPv6. When people see some IPv6 ready logos all around the web, they will probably start to wonder what this is all about and want to have that stuff as well. Ok, not the average Planet Debian reader, but others... ;)

There's just some caveats:
  1. At least when you use Serendipity and the HTML Nugget plugin you have to turn of "Perform Markup Transformations". Otherwise the plugin will insert some newlines in the script code that make it fail.

  2. Currently the script doesn't work with HTTPS, but that's being worked on and should be fixed in the next version.

  3. The script displays a rather wide (>200 px) logo with statistics of IPv6 visitors. The width may break your theming. But I was told by some gently IPv6 Forum staff that this can be changed.


So, please support IPv6 and participate in that certification program. It doesn't hurt you, but might help spreading IPv6!

17 May 2009

Martin F. Krafft: Switzerland opts for biometric passports

Switzerland voted today for the introduction of biometric passports, with 50.1% for and 49.9% against, one of the closest votes since 1848 (according to NZZ). While the news don t fill me with glee there are too many unanswered questions around the digital passports one aspect of the decision surprised and even shocked me. I do not like biometric passports, because I like to know when my data are consumed, and by whom. The German government assures that only authorised parties can access those data, and published information about the security features of the German biometric passports, but I am unconvinced that those are adequate to protection for the 10 years of validity of the passport. Furthermore, I could find absolutely no information on who the authorised parties are, or which regulations cover who will become authorised in the near future. If that was properly addressed, e.g. by leaving it up to me and only me to decide who gets access, then the digital passport could actually be a good step forward, streamlining border control and making travel easier. But there is a completely different avenue of concern, no matter who gives permission to whom to consume whose data: how are they used, and where, and how long are they stored, and for what? Again, I cannot find any regulations. Instead, my question to the German Department of the Interior was answered (!) along the lines of it being up to each country to decide themselves over the use and storage of the data. In this light, it makes little difference that the German procedure for the digital passport does not permit the issuing bureau to store the data, while Switzerland s strategy is to build a central database of all these personal details (this is what shocked me). It might make you wonder what use the Swiss government is hoping for, and you might feel uncomfortable with your government building up an even tighter database of its people. But I d much rather have my data stored in Switzerland than consumed and stored every time I enter another country, because when I compare the style of governance of Switzerland to pretty much anything else out there, I am glad I get to live here (even though I am not Swiss and cannot vote). Yet, it s a worrying step in a direction of the glass human , of a society in which personal privacy is unknown and everything is part of the system. These are totalitarian visions, and it s doubtful whether we ll ever actually get there (so far, I don t think any state has come up with the information management strategies required to properly store, make use, and read sense out of the massive amounts of information), but the trend is clearly visible. In the end, however, what worries me the most is how relaxed people treat their personal information these days. Look at the infamous social networking sites, or other Web 2.0 gimmicks and you really start to wonder how headless people can be these days. I cannot immediately paint a scenario where it might be dangerous to push all kinds of information about yourself to the masses, but the mere idea of that is scary in and of itself. I d prefer to have the choice with whom to share what data. The biometric passports, despite the advantages they might bring, are one step away from that, because they empower the government to make that choice for you. I don t consider that progress at all. Update: NZZ reports that the issue is not closed. In the cantons of Grishuna and Lucerne, people are challenging the vote and a recount or even re-vote seems possible. I will post an update as soon as I know more. Then, I would also like to address some replies I ve received over the real problems behind the digital passports, because it cannot be just the central data storage it s not like your government doesn t already have all that, and I can t imagine how your fingerprint could be used against you.

Russell Coker: Appropriate Talks about Porn

There is currently some discussion about a talk which used pornographic imagery and jokes to illustrate points about Ruby programming [1]. A similar event happened in 2006 here is the description of the event from the author - which includes an unreserved apology [2]. It seems to me that the current discussion focusing on what is inappropriate for a public lecture is the wrong way to do it as there is a vast range of inappropriate material. I suggest that instead a white-list of appropriate references to porn in lectures will be more effective - if nothing else it makes for a much smaller list. Here is a first draft of such a list:

  1. Pornographic web sites handle a lot of traffic. There are significant technical problems that need to be solved. A lecture from an employee of an Internet porn company which covers the solutions to those technical problems would be of interest to many system administrators. Of course such a lecture should not promote the Internet porn company or show any samples of their products.

  2. Digital processing of images is an interesting topic. Having a digital editor from a magazine such as Vogue describe in detail how they do their job would be really interesting. There is a lot of overlap between the range of pictures displayed in Vogue and those displayed on porn sites. Having an employee of a porn company demonstrate how they touch up the picture of a fully clothed model would be an interesting technical topic, but of course it would be totally inappropriate to make any specific mentions of how the parts of the picture which are not PG-13 rated are edited. Even showing a picture of a porn star might be controversial, but I m sure that the same work could be reproduced with a photo of someone who has a more respectable career. Touching up a picture of RMS to make him look like a politician would make for a challenge for the presenter and an interesting lecture.

  3. The image known as Lenna is a photograph of a Playboy model named Lena that is widely used to test image compression [3]. While the image remains controversial, it seems to me that it would be impossible to give a complete and factual account of the history of image compression without mentioning it.

  4. The police have great discretionary powers to determine which crimes should be actively investigated. Senior police decide how many resources to assign to each case. I believe that in many jurisdictions the police will assign a much lower priority to a hacking case if the victim is running a porn service. Rumor has it that porn sites put a lot more effort into system security than most Internet services, partly due to not having as much protection from the police as other industries and partly because their customers don t want to be identified. I would be very interested in attending a presentation about practical computer security by a system administrator from a porn site. As an aside I m always interested in talking to people who do security work, so I would like to have a chat with someone who does such work for a porn site.

  5. A few years ago I attended a lecture about the security implications of porn surfing. It had some scary statistics on the number of porn sites that try to deploy malware on the computers of the people who view porn, and it made a good business case for banning porn at work without reference to HR issues (which is very relevant for the jurisdictions where viewing porn at work is not considered to be a social problem). I would like to see a new version of that talk with statistics based on more recent research, my theory is that modern porn sites are more toxic than the old ones due to the general increase in criminal activity on the net - but I have no evidence to support it.

Of course in all cases jokes about porn are not acceptable, mentions of porn need to be strictly on the basis of historical analysis or the description of technical and legal issues which are relevant to the audience. Delivering a talk about porn without inappropriate jokes would take a great deal of effort, but it can be done (and I ve seen it done once). For these five cases (and the few others that will probably be suggested in comments) it would probably be best if the conference organisers viewed the talk first to ensure that there was no misunderstanding about what is appropriate. I think that comparing a short list of specific cases where porn can reasonably be mentioned in a public lecture with the vast number of potential inappropriate references illustrates the probability of a random porn reference being acceptable. The probability of making a random porn reference that is appropriate is probably slightly less than that of winning the lottery.

Gunnar Wolf: Politicians time once again

It is time for stupid, empty politicians slogans once again in my dear country. And, as always, while we had lively, controversial presidential elections three years ago (and I won't rant this time on why so many Mexicans still believe the current president can only be called a de facto president), the mid-term elections... Fail to get any attention and cause only bored reactions. I am writing today mostly because I stumbled upon Francisco's post on why the Mexican Ecologist Green Party (PVEM) campaign does not impress him. As many, many other people with strong political opinions I know, I will go to the voting booth next July 5th, as I have done every time since I was of age - But I will most probably void my ballot, as I have found nobody worth my vote. And even if I am (and have always been) a leftist person, none of the four so-called leftist parties inspire the smallest bit of confidence. But hell, even the rightist or centrist parties fail to inspire confidence to their voters - After the 2006 electoral fiasco, we got a political system nobody believes in. And all analysts seem to concur that we moved from the most complete presidential regime to an utter partidocracy, where all of the (strong enough) parties cover each other's back not to lose the respective privileges (largely, money, but also law-making faculties and influence, which of course translates to impunity). Worth a very special mention is the crown jewel of political clowns in Mexico - PVEM, the Mexican Ecologist Green Party. A party that gets the gold medal for the most corrupt in our country (which is no small feat). A party where the National Party Presidents to date have only been father and son. And it is alarming because it is the only party apparently gathering more voters than they had before. But also, because of its utter pragmatism and lack of respect for anything they might once have stood for. I still remember on the 1994 elections, the first time they participated in general elections, their slogan was don't vote for a politician Vote for an ecologist... Little did the society know by then they were worse off than our oft-hated politicians. Can you imagine a so-called ecologist party that is expelled of the Global Greens as its behaviour is completely antithetical to anything a green party stands for? A party that promotes reinstating the death penalty (which was abolished from our Constitution, after decades of not being applied, less than a decade ago)? Or they say that, if a given medicine is not available at the Social Security hospitals, the government should pay the citizen so he can go and buy it at a drug store? (of course, if a needed medicine is not available at the Social Security it is most probably because the government is underfunded, not because the lazy administrators don't want to buy the medicines. And yes, with those two retrograde, stupid and -thankfully- completely unfeasible promises they have doubled their probable voters outcome in the past couple of months. The campaigns are only officially starting now. They are all really pathetic. A voter turnout of ~30% is expected. But yes, I am a politized person and just cannot help inviting everybody who has the right to go and vote. If there is somebody worth voting for in your district, please vote for him/her. However... Together with many people I admire, together with many of my friends, together with the people who still believe it is possible to make something out of this forsaken country's politic system... I invite you to void your ballots. Hopefully they will be enough so they must be heard this time.

16 May 2009

Andrew Pollock: [tech] Deciding between the Lenovo T400 and X301

I'm in the market for a new laptop. I've got almost 4 years out of my Dell D610 (which I've been despising from not long after purchasing) and decided that I'll never buy from Dell again. I used to be very down on ThinkPads because of the placement of the Escape key, but since I've been using one at work for the last 3.5 years, I've gotten used to the Escape key location, and found the laptops themselves to otherwise be very solid and well supported by Linux. So Lenovo it is. Next question: T400 or X301? I've seen both, and the X301 is very sexy in terms of thickness, weight, and having all the latest bells and whistles, but boy, is it expensive. I did a side-by-side comparison between a T400 decked out the way I wanted, and an X301 decked out the best I could choose, and I've opted for the T400. The main problems I had with the X301 were that there was no choice of processor, and the processor available seemed significantly slower than what I could get in the T400, and of course the cost. I seemed to be paying nearly $1000 more for a slower processor, just to get something extra thin and light, with LED backlighting and an SSD disk. What finally swayed me to spending less money and getting an arguably "better" laptop was if I paid less now, I'd be more comfortable possibly getting something in less than 4 years time down the track. So if it came down to the X301 for 4 years or the T400 for 2 years, the T400 seemed like a better deal. What will hopefully end up happening is I'll end up using the T400 for four years and not end up hating it by the end of that time. Here's what I ended up going with: All of that plus a 2 year warranty and an additional 90W AC adapter came out at $1,240 (they have a 15% off discount code thing running until tomorrow, which brought the price down a bit) I'm particularly excited about not having a proprietary graphics chipset. I'm particularly unexcited about it including Windows Vista Home Basic. Drat, enumerating all of the options made me just realise that I seem to have omitted the 5-in-1 media reader from the final order. Oh well. That was largely just a nice-to-have anyway. Sarah tends to do all of the photo management on her laptop. I doubt this will get to me before Thursday, so I should have it waiting for me by the time I get back from Barcelona.

Joey Hess: one of those days

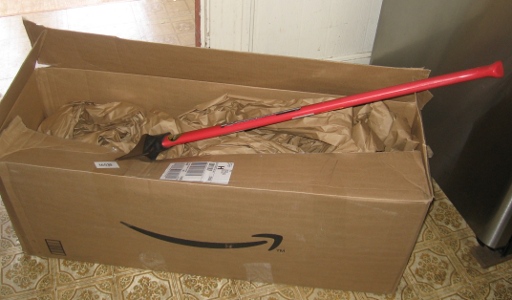
Some spring days just seem full to bursting with unusual experiences. I spent the night at the yurt and in just four hours today: big red axe Thanks to Iain M from Melbourne who writes, "We have never met. I have used your software and gained insight from your blog, over the years. So thanks. Also, I have never bought someone an axe before. This is cool." I forgot I had that in my wishlist, but now I can split wood with ease, when I run out of Amazon packaging material to burn.

Pablo Lorenzzoni: Inspiring picture

Just this week I went to the movies to check the latest incarnation of Cap. Kirk, Mr. Spock et al. It really was a great movie I was expecting less, I have to admit. But the movie was not bad at all With all that space and beyond thing in my mind, yesterday I was surprised with a greatly inspiring picture taken from Hubble Florida, before STS-125 reach Hubble (thanks Florian Weimer for the heads-up): How inspiring can that be? You can find the original here, along with the explanation of how and when it was taken.

Jaldhar Vyas: Classic Spock > Emo Spock

The original plan was to see the new Star Trek film on Mothers Day being the incurable romantic that I am but it didn't work out so we ended up going today instead. Overall we liked the film. It's best not to think about the plot too deeply or it will implode like red matter. (Red matter??? Are my children the scientists of the future? "I hereby name this new element Ballerinium") Anyway lots of jokes and explosions to keep your mind away from those kind of thoughts. As the title of this post suggests, I am not too fond of what they did with the Spock character. (Uhura Spock? Highly illogical.) The new Kirk is spot on as the green-alien-banging douchebag (amirite Uhura?) we know and love. And Chekhov, Scottie, and McCoy were great. The bad guy wasn't really that bad I thought. I hope they make the aliens badder and more alien in the inevitable sequels.

Antti-Juhani Kaijanaho: This is Alue

I have made a couple of references in my blog to the new software suite I am writing, which I am calling Alue. It is time to explain what it is all about. Alue will be a discussion forum system providing a web-based forum interface, a NNTP (Netnews) interface and an email interface, all with equal status. What will be unusual compared to most of the competition is that all these interfaces will be coequal views to the same abstract discussion, instead of being primarily one of these things and providing the others as bolted-on gateways. (I am aware of at least one other such system, but it is proprietary and thus not useful to my needs. Besides, I get to learn all kinds of fun things while doing this.) I have, over several years, come across many times the need for such systems and never found a good, free implementation. I am now building this software for the use of one new discussion site that is being formed (which is graciously willing to serve as my guinea pig), but I hope it will eventually be of use to many other places as well. I now have the first increment ready for beta testing. Note that this is not even close to being what I described above; it is merely a start. It currently provides a fully functional NNTP interface to a rudimentary (unreliable and unscalable) discussion database. The NNTP server implements most of RFC 3977 (the base NNTP spec IHAVE, MODE-READER, NEWNEWS and HDR are missing), all of RFC 4642 (STARTTLS) and a part of RFC 4643 (AUTHINFO USER the SASL part is missing). The article database is intended to support with certain deliberate omissions the upcoming Netnews standards (USEFOR and USEPRO), but currently omits most of the mandatory checks. There is a test installation at verbosify.org (port 119), which allows anonymous reading but requires identification and authentication for posting. I am currently handing out accounts only by invitation. Code can be browsed in a Gitweb; git clone requests should be directed to git://git.verbosify.org/git/alue.git/. There are some tweaks to be done to the NNTP frontend, but after that I expect to be rewriting the message filing system to be at least reliable if not scalable. After that, it is time for a web interface.

Marco d'Itri: Installing Debian on the Sheevaplug

This document explains how to use deboostrap --foreign to build from scratch and install a minimal Debian system on the Sheevaplug (but it is equally applicable to many other embedded systems). The only piece missing to be able to install from bare metal is a working kernel and initramfs pair, so this document assumes that you already have a kernel which can mount the root file system from a USB key. For the Sheevaplug, the factory kernel in the internal NAND flash will work fine. The Debian kernel package puts us in a chicken and egg situation: it cannot mount the root without an initramfs (because all drivers are modular), but we cannot build one until we can boot the system. I suppose that, as an exercise of style, somebody could create a minimal initramfs with busybox and the kernel modules needed to mount the root and then mount it manually, but if you really lack a working kernel then it's probably faster to boot the file system image for the first time using qemu and the "versatile" debian-installer target. The first step is to run the first stage of debootstrap on another system (which does not need to be ARM), to build a temporary root file system. I use the --variant and --include options to build the smallest possible system with network support, but they can be omitted.
debootstrap \
         --foreign --arch=armel \
         --variant=minbase \
         --include=linux-image-2.6-kirkwood,module-init-tools,udev,netbase,
                   net-tools,ifupdown,iproute,whiptail,vim-tiny \
         sid ./target/ http://ftp.it.debian.org/debian/
As usual when using debootstrap, some manual configuration is needed:
cd target/
echo bokassa.mi.bofh.it > etc/hostname
vi etc/network/interfaces
vi etc/resolv.conf
echo LANG=C > etc/default/locale
echo '127.0.0.1 localhost' > etc/hosts
cat <<END > etc/fstab
/dev/root / ext3 noatime 0 1
tmpfs /tmp tmpfs defaults 0 0
#/tmp /var/tmp none bind 0 0
END
I took some hints from http://wiki.debian.org/ReadonlyRoot to reduce writes to the flash file system:
# the blkid cache is evil anyway
ln -s /dev/null etc/blkid.tab
# this link will be created anyway by the package
ln -s /var/lib/initscripts/nologin etc/nologin
# it's better to not use a static mtab with modern kernels
ln -s /proc/mounts etc/mtab
# unless you plan to use multiple removable network interfaces, persistent
# interface names are not needed
: > etc/udev/rules.d/75-persistent-net-generator.rules
Two small workarounds are needed:
# if this is not set then the preinst of linux-image-* will die trying
# to ask a debconf question in the debootstrap second stage
echo 'do_initrd = yes' > etc/kernel-img.conf
# a workaround for bug #520742
: > etc/udev/disabled
Now you can format a USB pen drive and copy the root file system on it:
mke2fs /dev/sdb1
tune2fs -i 0 -c 0 /dev/sdb1
mount /dev/sdb1 /mnt/
rsync -aH target/ /mnt/
umount /mnt/
After powering the plug press a key to get to the U-Boot prompt and use the factory kernel to boot from USB:
setenv bootargs console=ttyS0,115200 root=/dev/sda1 rootdelay=10 panic=10 init=/bin/bash
run bootcmd
Then you can run the second stage of debootstrap, finish the bare minimal configuration and start init:
./debootstrap/debootstrap --second-stage
# disable the gettys for /dev/tty[1-6], which do not exist
vi /etc/inittab
# and add one for the serial console
echo 'T0:2345:respawn:/sbin/getty -L ttyS0 115200 linux' >> /etc/inittab
# do not forget to set the root password or you will not be able to login...
vi /etc/shadow
rm /etc/udev/disabled
exec /bin/bash
mount / -o ro,remount
exec /sbin/init
Congratulations, now you can login on the system and start to install the packages you like:
echo 'deb http://ftp.it.debian.org/debian/ unstable main' > /etc/apt/sources.list
echo 'APT   Install-Recommends "false";  ;' > /etc/apt/apt.conf.d/no-recommends
apt-get update
# dash is much faster
apt-get install dash
dpkg-divert --add /bin/sh
ln -sf dash /bin/sh
# I do not like these, YMMV
rm /vmlinuz /initrd.img
rmdir /selinux /srv
# the kernel is able to read the time from the RTC by itself, and this
# will allow using a read only root
echo HWCLOCKACCESS=no >> /etc/default/rcS
# faster boot
echo CONCURRENCY=shell >> /etc/default/rcS
# useless on this platform
mv /etc/rcS.d/S01glibc.sh /etc/rcS.d/K01glibc.sh
dpkg-reconfigure tzdata
apt-get install openssh-server screen iptables wget less
U-Boot requires that the kernel and initramfs have a special header:
apt-get uboot-mkimage
cd /boot/
mkimage -A arm -O linux -T kernel  -C none -a 0x00008000 -e 0x00008000 \
  -n Linux-2.6.29-2 -d vmlinuz-2.6.29-2-kirkwood uImage
mkimage -A arm -O linux -T ramdisk -C gzip -a 0x00000000 -e 0x00000000 \
  -n initramfs -d initrd.img-2.6.29-2-kirkwood uInitrd
Now you can reboot and configure u-boot to boot from the USB device. This is the variables scheme I like and it is not mandatory in any way, so I recommend that you read and understand the existing configuration before modifying it (some lines have been broken for readability):
setenv bootargs_nand $(bootargs)
setenv bootcmd_nand $(bootcmd)
setenv bootargs_root root=/dev/sda1
setenv bootargs_misc 'ro panic=10
  mtdparts=nand_mtd:0x400000@0x100000(uImage),0x1fb00000@0x500000(rootfs)'
setenv bootcmd_usb 'usb start; ext2load usb 0:1 0x00200000 /boot/uImage;
  ext2load usb 0:1 0x01100000 /boot/uInitrd'
setenv bootcmd 'setenv bootargs $(console) $(bootargs_root) $(bootargs_misc)
  $(bootargs_more); run bootcmd_usb; bootm 0x00200000 0x01100000'
Since now you are not using anymore the Marvell kernel tree it is mandatory to set these two variables and reboot:
setenv mainlineLinux yes
setenv arcNumber 2097
saveenv
reset
Installation to SD is identical, but requires an updated version of U-Boot with SD support. Due to a kernel bug which prevents autoloading the driver you will need to add mvsdio and mmc_block to /etc/initramfs-tools/modules and rebuild the initramfs. (Yes, the naming theme I use at home is "african dictators"...)

15 May 2009

Michael Banck: 15 May 2009

The other day, while "travelling Deutsche Bahn", I read an article in the venerable Frankfurter Allgemeine Zeitung. To my slight surprise, it included a link to some government document in form of a tinyurl.com URL - (http://tinyurl.com/cr8qso). As I had no internet acccess at the time I read the article, I had to defer checking out the link to some later time. Then I began to wonder how stable those URLs are compared to the stability of the link they service and of the newspaper article itself. The description of the link would probably allow for some targetted google searching, but is it not the responsibility of the newspaper to allow their readers to research the link in a couple of days, months or maybe years? Does tinyurl.com maybe have an enterprise feature where they guarantee long-living links to newspapers and similar customers?

Eddy Petri&#537;or: svn-buildpackage is now orphaned

I have decided that is high time to declare svn-buildpackage orphaned since many people are replying on it to be useful, but nobody cared enough to answer to the RFH Eduard Bloch made some 3 years ago.

I know it would have been better if I would have asked a request for adoption, but, honestly, the package didn't had a maintainer in the last year and that would have been lying to everybody.

The package is quite important and I would hate to see it leave the official archive since many people do need it and use it regularly (I know for sure the GNOME, Perl and the Debian Games Team use it) and I have enjoyed working on the package while I was motivated.

The code is maintained in SVN and the trunk can be viewed at:

http://svn.debian.org/wsvn/collab-maint/deb-maint/svn-buildpackage/trunk/

and can be checked out with any of these commands:

# read-only copy
svn co svn://svn.debian.org/svn/collab-maint/deb-maint/svn-buildpackage/trunk svn-buildpackage

# read write, if you have an account on alioth.debian.org:

svn co svn+ssh://svn.debian.org/svn/collab-maint/deb-maint/svn-buildpackage/trunk


Also, note that the package has several features which the new maintainer(s) should be aware of and must make sure they all work when changing the code. Also, there are some things to remember:

These being said, I am really hoping svn-buildpackage will find a new maintainer since it deserves a lot more attention than I am providing. Don't forget, 0.6.24 is wating for an upload already.


Update: Neil Williams answered and agreed to take over maintenance, but he doesn't usually use svn-inject and svn-upgrade, so somebody taking care of those would be needed. Ironically, those two scripts are the ones in the worst shape of the three main scripts.

Jan Hauke Rahm: Bug#528733: O: svn-buildpackage

Oh dear, it happened Hundreds of developers seem to have switched to git (man, I want to be as famous as Linus) and finally the packaging helper for subversion is orphaned. Yeah, I know, this is just partly related if at all but at least the low interest in its further development seems to prove my point. Anyways, I m not going to fully give up on it. Eddy just copied the bug message to d-devel to arrest some attention and actually I m trying the same here. svn-buildpackage is still needed, let alone the entire texlive stuff which is maintained in subversion repositories and many packages in collab-maint. So, let s see if we can t get it somewhere. 0.6.24 - release soon As Eddy mentioned in the bug report there is a version 0.6.24 prepared in trunk. Looking at my working copies I seem to have fixes for #363003, #414564, #467614, #480684, and #506876 lying around which I didn t commit yet. They should be sent to the bug reports, though. If you consider working on a release of svn-bp please contact me (or just write to the bug reports, I m subscribed). 0.7 - do it right ;-) This is far away but maybe a worthy goal. Two months ago I started working on a rewrite of svn-bp in order to fix some long outstanding bugs which would need gross hacks in the current version or aren t even fixable by design. Find my first experiments in branches/0.7. But then let me be honest, I didn t do anything about it lately - partly because of the low interest, but majorly because of vcs-pkg. I hope to figure out during debconf9 (I hope I can attend) if it is a possible replacement of svn-bp. But that s still up in the air. Well, that s my two cents about the situation.

14 May 2009

Julian Andres Klode: Ubuntu One


Today, I was testing Canonical s new Ubuntu One service. Ubuntu One is a service for syncing and sharing files online, with 2GB storage for free. I installed the Ubuntu One client on Ubuntu 9.04 and it s cool. Ubuntu One creates a directory named Ubuntu One in your home directory. Within this directory, there are two subdirectories. The first one is My Files and the second one is named Shared With Me . When you place files in the My Files directory, the Ubuntu One client gets notified (using inotify) about the change and begins uploading the file to the Ubuntu one server. When you access the web interface, which should work in every modern browser, and upload a file there, the next time your local client connects the files are fetched to your local hard disk. This also works when you have two different computers and create a file on the one computer, it will be visible on the second one as soon as it has fetched the new file. You could also copy your .mozilla directory into the synced directory, and create a symlink from your home directory to it. I have not tried it myself, but in theory this would allow you to have your profile synced on all your computers. And the best thing about Ubuntu One is that the client is completely free software and written in Python. This makes it possible to package the client for other distributions, like Debian. Packaging it for RPM-based distribution such as Fedora should also be doable, but may require some more time. There seems to have been some criticism that the server side is not free software. While that may not be the good, it s certainly better than other services where even the client is proprietary. And there still is the possibility to write your own server as the protocol is available. Ubuntu One is currently in private beta, if you want to try it out, you need an invitation (visit ubuntuone.com for further information). Posted in Ubuntu

Antti-Juhani Kaijanaho: Asynchronous transput and gnutls

CC0
To the extent possible under law,
Antti-Juhani Kaijanaho has waived all copyright and related or neighboring rights to
Asynchronous transput and gnutls. This work is published from Finland.
GnuTLS is a wonderful thing. It even has a thick manual but nevertheless its documentation is severely lacking from the programmer s point of view (and there doesn t even seem to be independent howtos floating on the net). My hope is to remedy with this post, in small part, that problem. I spent the weekend adding STARTTLS support to the NNTP (reading) server component of Alue. Since Alue is written in C++ and uses the Boost ASIO library as its primary concurrency framework, it seemed prudent to use ASIO s SSL sublibrary. However, the result wasn t stable and debugging it looked unappetizing. So, I wrote my own TLS layer on top of ASIO, based on gnutls. Now, the gnutls API looks like it works only with synchronous transput: all TLS network operations are of the form do this and return when done ; for example gnutls_handshake returns once the handshake is finished. So how does one adapt this to asynchronous transput? Fortunately, there are (badly documented) hooks for this purpose. An application can tell gnutls to call application-supplied functions instead of the read(2) and write(2) system calls. Thus, when setting up a TLS session but before the handshake, I do the following:
                gnutls_transport_set_ptr(gs, this);
                gnutls_transport_set_push_function(gs, push_static);
                gnutls_transport_set_pull_function(gs, pull_static);
                gnutls_transport_set_lowat(gs, 0);
Here, gs is my private copy of the gnutls session structure, and the push_static and pull_static are static member functions in my sesssion wrapper class. The first line tells gnutls to give the current this pointer (a pointer to the current session wrapper) as the first argument to them. The last line tells gnutls not to try treating the this pointer as a Berkeley socket. The pull_static static member function just passes control on to a non-static member, for convenience:
ssize_t session::pull_static(void * th, void *b, size_t n)
 
        return static_cast<session *>(th)->pull(b, n);
 
The basic idea of the pull function is to try to return immediately with data from a buffer, and if the buffer is empty, to fail with an error code signalling the absence of data with the possibility that data may become available later (the POSIX EAGAIN code):
class session
 
        [...]
        std::vector<unsigned char> ins;
        size_t ins_low, ins_high;
        [...]
 ;
ssize_t session::pull(void *b, size_t n_wanted)
 
        unsigned char *cs = static_cast<unsigned char *>(b);
        if (ins_high - ins_low > 0)
         
                errno = EAGAIN;
                return -1;
         
        size_t n = ins_high - ins_low < n_wanted
                ?  ins_high - ins_low
                :  n_wanted;
        for (size_t i = 0; i < n; i++)
         
                cs[i] = ins[ins_low+i];
         
        ins_low += n;
        return n;
 
Here, ins_low is an index to the ins vector specifying the first byte which has not already been passed on to gnutls, while ins_high is an index to the ins vector specifying the first byte that does not contain data read from the network. The assertions 0 <= ins_low, ins_low <= ins_high and ins_high <= ins.size() are obvious invariants in this buffering scheme. The push case is simpler: all one needs to do is buffer the data that gnutls wants to send, for later transmission:
class session
 
        [...]
        std::vector<unsigned char> outs;
        size_t outs_low;
        [...]
 ;
ssize_t session::push(const void *b, size_t n)
 
        const unsigned char *cs = static_cast<const unsigned char *>(b);
        for (size_t i = 0; i < n; i++)
         
                outs.push_back(cs[i]);
         
        return n;
 
The low water mark outs_low (indicating the first byte that has not yet been sent to the network) is not needed in the push function. It would be possible for the push callback to signal EAGAIN, but it is not necessary in this scheme (assuming that one does not need to establish hard buffer limits). Once gnutls receives an EAGAIN condition from the pull callback, it suspends the current operation and returns to its caller with the gnutls condition GNUTLS_E_AGAIN. The caller must arrange for more data to become available to the pull callback (in this case by scheduling an asynchronous write of the data in the outs buffer scheme and scheduling an asynchronous read to the ins buffer scheme) and then call the operation again, allowing the operation to resume. The code so far does not actually perform any network transput. For this, I have written two auxiliary methods:
class session
 
        [...]
        bool read_active, write_active;
        [...]
 ;
void session::post_write()
 
        if (write_active) return;
        if (outs_low > 0 && outs_low == outs.size())
         
                outs.clear();
                outs_low = 0;
         
        else if (outs_low > 4096)
         
                outs.erase(outs.begin(), outs.begin() + outs_low);
                outs_low = 0;
         
        if (outs_low < outs.size())
         
                stream.async_write_some
                        (boost::asio::buffer(outs.data()+outs_low,
                                             outs.size()-outs_low),
                         boost::bind(&session::sent_some,
                                     this, _1, _2));
                write_active = true;
         
 
void session::post_read()
 
        if (read_active) return;
        if (ins_low > 0 && ins_low == ins.size())
         
                ins.clear();
                ins_low = 0;
                ins_high = 0;
         
        else if (ins_low > 4096)
         
                ins.erase(ins.begin(), ins.begin() + ins_low);
                ins_high -= ins_low;
                ins_low = 0;
         
        if (ins_high + 4096 >= ins.size()) ins.resize(ins_high + 4096);
        stream.async_read_some(boost::asio::buffer(ins.data()+ins_high,
                                                   ins.size()-ins_high),
                               boost::bind(&session::received_some,
                                           this, _1, _2));
        read_active = true;
 
Both helpers prune the buffers when necessary. (I should really remove those magic 4096s and make them a symbolic constant.) The data members read_active and write_active ensure that at most one asynchronous read and at most one asynchronous write is pending at any given time. My first version did not have this safeguard (instead trying to rely on the ASIO stream reset method to cancel any outstanding asynchronous transput at need), and the code sent some TLS records twice which is not good: sending the ServerHello twice is guaranteed to confuse the client. Once ASIO completes an asynchronous transput request, it calls the corresponding handler:
void session::received_some(boost::system::error_code ec, size_t n)
 
        read_active = false;
        if (ec)   pending_error = ec; return;  
        ins_high += n;
        post_pending_actions();
 
void session::sent_some(boost::system::error_code ec, size_t n)
 
        write_active = false;
        if (ec)   pending_error = ec; return;  
        outs_low += n;
        post_pending_actions();
 
Their job is to update the bookkeeping and to trigger the resumption of suspended gnutls operations (which is done by post_pending_actions). Now we have all the main pieces of the puzzle. The remaining pieces are obvious but rather messy, and I d rather not repeat them here (not even in a cleaned-up form). But their essential idea goes as follows: When called by the application code or when resumed by post_pending_actions, an asynchronous wrapper of a gnutls operation first examines the session state for a saved error code. If one is found, it is propagated to the application using the usual ASIO techniques, and the operation is cancelled. Otherwise, the wrapper calls the actual gnutls operation. When it returns, the wrapper examines the return value. If successful completion is indicated, the handler given by the application is posted in the ASIO io_service for later execution. If GNUTLS_E_AGAIN is indicated, post_read and post_write are called to schedule actual network transput, and the wrapper is suspended (by pushing it into a queue of pending actions). If any other kind of failure is indicated, it is propagated to the application using the usual ASIO techniques. The post_pending_actions merely empties the queue of pending actions and schedules the actions that it found in the queue for resumption. The code snippets above are not my actual working code. I have mainly removed from them some irrelevant details (mostly certain template parameters, debug logging and mutex handling). I don t expect the snippets to compile. I expect I will be able to post my actual git repository to the web in a couple of days. Please note that my (actual) code has received only rudimentary testing. I believe it is correct, but I won t be surprised to find it contains bugs in the edge cases. I hope this is, still, of some use to somebody :)

Next.

Previous.