Search Results: "ag"

25 February 2014

Christian Perrier: Bug #740000

Miguel Landaeta reported Debian bug #740000 on Monday February 24th, against the checkstyle package. Bug #730000 was reported as of November 20th: 3 months and 4 days for 10,000 bugs. Nearly exactly same bug reporting rate than 720000-730000. And, of course, we're still on our way to bug #800000 and bug #1000000.

Don Armstrong: Debian Booth at Scale 12x

I spent the weekend at SCALE 12x running the Debian booth. SCALE is one of the best conferences that I get to attend every year; it has a great mix of commercial exhibitors and community groups, and routinely gets great speakers. As I've done for quite some time, I organized a Debian booth there, and talked to lots of people about Debian. If you're in the Southern California area, or have a chance to give a talk for SCALE 13x, you should do so! Thanks again to Matt Kraai and Paul Hardy for helping out in the Debian booth all weekend!

Andrew Pollock: [life] Day 28, Kindergarten, Taxes and a smattering of appointments

Today was yet another busy day. Zoe seems to have taken to waking up at around 5:30am instead of her normal 6:00am (or a bit later when I'm really lucky). Not sure what that's all about. I did get her to go back to bed until about 6:55am, and then she was happy to just come and snuggle in bed with me for a bit instead of play games on her Nexus 7. After that we had a leisurely start to day, making porridge with strawberries in the Thermomix, and then biked to Kindergarten. Somehow it still managed to be 8:45am by the time we got there. I was expecting it would be closer to 8:30am. Drop off looked like it was going to be clingy, but then she just waved me off, so that was nice. I had an appointment at the podiatrist at 11:40am, and that was back near Kindergarten, but further away from home, so I had this grand plan of cycling over there, and then twiddling my thumbs for a bit before Kindergarten pickup. That left me with only a couple of hours at home to work on my taxes before I had to leave again. I managed to make those couple of hours productive though, so that was good. I biked to the podiatrist, had my appointment, and then it was 1pm and I still needed lunch, so I decided to grab some at a cafe near the Kindergarten. I chilled out there for a while catching up on social media on my phone, and then headed over to the Kindergarten, but was still quite early, so I just hung out on one of the couches they have out by the front door, out of sight of the kids. The Kindergarten has an A-frame whiteboard out the front that they use to broadcast messages to parents at drop off and pick up time. One of the teachers came out to write something on it while I was sitting out there, and another parent reacted rather negatively to it as it was being written, so I had to go see it for myself. Apparently a child had a suspected gastro bug (he'd thrown up a couple of times). It was interesting observing the reactions of a few mothers as they trickled in for pick up. It's been a while since a gastro bug has gone through the household, so I guess the news didn't evoke a particularly powerful reaction in me. I'm going with the "suspected" and that hopefully Zoe didn't come into contact with patient zero. I guess time will tell. I certainly hope she doesn't come down with anything between now and Sunday, with all the travel we're doing. I had an accident report to sign today. Apparently a large wooden block hit Zoe in the head while they were packing up a tower they'd made. She had a bit of a lump on her head, but otherwise seemed fine. Zoe had a nap today, of unknown length, but woke up naturally as I entered the room. She took a fair while to get going though, and was grumpy and uncooperative getting on the bike. I ended up having to do it the "hard way" and we had a fabulous ride back with her doing a tired cry all the way. All the way until we passed a playground, when she snapped out of it and declared she wanted to have a play. I'd booked myself in for a haircut at 3pm, and a make up swim class at 4:45pm (to cover our absence this Saturday due to our Melbourne trip) so playing in the playground seemed like the perfect way to fill the gap. It was even on the way to swim class. So after I had my haircut, we popped home, grabbed her swim gear, and biked back to the playground for a bit. Then we went to swim class. This was her third one at her new level, and her progress continues to go very well. It's really exciting watching her. Zoe took her time leaving the pool, so we didn't get home until after 5:30pm and I hadn't started dinner yet. I whipped it up while Zoe watched some TV, and I managed to recoup all of the lost time after dinner and still get Zoe to bed at a reasonable hour. Bedtime itself went nice and smoothly. I used the canned goodnight video I asked Sarah to make for the first time tonight, and it was well received and I think defused any potential issues. I'm hoping she'll sleep well tonight, as her mosquito bites don't seem to be actively giving her trouble any more.

Andrew Pollock: [life] Sprained ankle, part 3

My right ankle has never been quite right ever since I sprained it in 2008. The ankle is always a bit enlarged, sometimes more so after running. With all the running I've been doing back in Brisbane, I had this niggling concern in the back of my head that I might be doing myself some long term damage, so last year I packed myself off to see a physiotherapist that was within walking distance of home. He declared that I had blown out two of the ligaments in my foot from the sprain, and that my calf was compensating for it a bit. The swelling was just scar tissue. He gave me a bunch of exercises to do, and I had some electrotherapy on my calf for a few weeks and I went on my way. I think I'm supposed to do the exercises every time before I run, but that hasn't happened. It's hard enough to make the time to run, without having to prepend a bunch of exercises as well. One of my neighbours works for my FootDr, so I asked her if they did video run gait analysis, because I was interested in seeing if there was anything I could do to improve my running gait. They did, and so I finally got around to making an appointment for today. The appointment wasn't as interesting as the one I had in the US, in that there was no fluoroscopy, just manual examination, but there was the video run gait analysis on the treadmill, which was not something I've had before. I was pleased that my running shoes (New Balance 940's) were deemed correct for my situation. The guy at Sports Basement obviously did a good job of fitting them to me. I was advised to refresh the shoes, though, so I lashed out on a pair of 940 v2's today. My health insurance also paid pretty generously for orthotics, so I'm going to get a pair for them to add to the ankle stability. The results of the run gait analysis were that, surprise surprise, I am rolling inwards a bit more on my right ankle than my left. Interestingly, my left calf was bigger than my right one, so I was advised to stick with the physiotherapy exercises (yay). So with the orthotics, new shoes, and forcing myself to do my physiotherapy exercises, I'm pretty satisfied that my continued running isn't likely to do too much damage to my body. The podiatrist concurred that because I'm currently pain free, everything should be good. I just had to live with the fact that my right ankle is going to always be a bit swollen.

Diego Escalante Urrelo: Habits and engagement

Nir Eyal Automatic customers: How to design user habits at WordCamp San Francisco 2012:
I came across this video by Nir Eyal about his model for analyzing and designing user engagement through habits. Successful services, he says, develop habits through triggers, actions, rewards and investments. A trigger is some kind of prompt that suggest an action promising a reward, these can be external (Twitter notification) or internal (boredom). Promising because our brains are wired for the thrill of search, of promise, rather than results. That s why we keep reloading the Twitter feed hoping for good tweets this time. Then comes the investment. Asking users to devote effort (following friends) in exchange of further rewards (better content) loads the value and triggers that will get the user to come back: direct messages, replies, suggested content. Or, simply put: the more you use Twitter, the more triggers and rewards you create, the more you hook yourself. This is really interesting as it is not limited to technology, the science behind it is actually nothing new. I m curious to see how this can be applied to Free Software and personal projects. Check out the abridged version linked above, and the longer workshop as soon as you have the time.
Nir Eyal: Automatic customers: How to design user habits

24 February 2014

John Goerzen: Good all-day light laptop?

I am trying to find a laptop with all-day battery life that s fairly light. Perhaps I am dreaming too big here, but I thought I d toss out my hopes and see if there are any recommendations. I am hoping for: The point is that I want to be able to do general web browsing with a real browser (Firefox), run Thunderbird for mail, hopefully even be able to run a VM or two under KVM or VirtualBox (with the understanding that this will kill battery life). I have been using a Thinkpad T420s for a couple of years now. Its battery life wasn t great even when it was new, and is worse now, of course. An Asus TF700t tablet has great battery life, but the storage system in it is so slow that I rather suspect that the browser cache is hurting, not helping, performance. I am also rather disappointed with the Android system. I can t really develop for it with my usual tools. Enough components are closed that, like Windows or MacOS X, I can t feel like I can truly trust it with sensitive data. Although it has SSH clients available, the SSH server there wants you to pay to use public key auth, and the SSH clients don t work all that well. Git can work, sort of. Battery life is great, and the keyboard is fine, but even flashing a different OS won t fix that terrible performance. I ve had people recommend certain Asus laptops, a Microsoft Surface Pro, or a Macbook Air. Any thoughts?

Daniel Pocock: GSoC Organisations announced, Ganglia selected for 2014

Google has just published the list of organisations for Google Summer of Code 2014 It is no surprise that big projects like Debian and Fedora are all back again. On the other hand, I am delighted to announce that the Ganglia project is participating this year. We have started publishing a list of project ideas and we are keen to start having discussion with potential students and anybody who would like to participate in our mentoring team. We have also invited the RRDtool community to be part of this big adventure because RRDtool is such a critical element of Ganglia's success. My Debian project ideas I've also published a couple of project ideas on the Debian wiki before the organisations were confirmed: As I am part of the admin team for Ganglia, these Debian projects can only go ahead if there are some additional mentors willing to participate in them. Please contact me if either of these projects is interesting for you. You don't have to be a Debian Developer to be a mentor for Debian. Given the highly generic nature of these projects, particularly the Java one, they could also be mentored under the umbrella of another organisation. The Java project is particularly suitable for any Linux distribution or project relying on many JARs and all distributions and Java users are likely to extract some benefit from it. Deadlines approaching GSoC works on a strict calendar, please see the dates here if you would like to participate as a mentor, co-mentor or student.

Vincent Bernat: Coping with the TCP TIME-WAIT state on busy Linux servers

TL;DR: Do not enable net.ipv4.tcp_tw_recycle. The Linux kernel documentation is not very helpful about what net.ipv4.tcp_tw_recycle does:
Enable fast recycling TIME-WAIT sockets. Default value is 0. It should not be changed without advice/request of technical experts.
Its sibling, net.ipv4.tcp_tw_reuse is a little bit more documented but the language is about the same:
Allow to reuse TIME-WAIT sockets for new connections when it is safe from protocol viewpoint. Default value is 0. It should not be changed without advice/request of technical experts.
The mere result of this lack of documentation is that we find numerous tuning guides advising to set both these settings to 1 to reduce the number of entries in the TIME-WAIT state. However, as stated by tcp(7) manual page, the net.ipv4.tcp_tw_recycle option is quite problematic for public-facing servers as it won t handle connections from two different computers behind the same NAT device, which is a problem hard to detect and waiting to bite you:
Enable fast recycling of TIME-WAIT sockets. Enabling this option is not recommended since this causes problems when working with NAT (Network Address Translation).
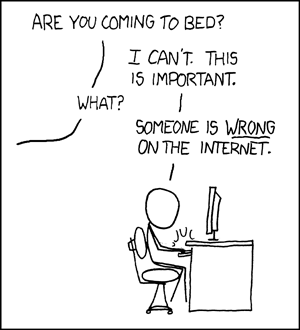
I will provide here a more detailed explanation in the hope to teach people who are wrong on the Internet. xkcd illustration As a sidenote, despite the use of ipv4 in its name, the net.ipv4.tcp_tw_recycle control also applies to IPv6. Also, keep in mind we are looking at the TCP stack of Linux. This is completely unrelated to Netfilter connection tracking which may be tweaked in other ways1.

About TIME-WAIT state Let s rewind a bit and have a close look at this TIME-WAIT state. What is it? See the TCP state diagram below2: TCP state diagram Only the end closing the connection first will reach the TIME-WAIT state. The other end will follow a path which usually permits to quickly get rid of the connection. You can have a look at the current state of connections with ss -tan:
$ ss -tan   head -5
LISTEN     0  511             *:80              *:*     
SYN-RECV   0  0     192.0.2.145:80    203.0.113.5:35449
SYN-RECV   0  0     192.0.2.145:80   203.0.113.27:53599
ESTAB      0  0     192.0.2.145:80   203.0.113.27:33605
TIME-WAIT  0  0     192.0.2.145:80   203.0.113.47:50685

Purpose There are two purposes for the TIME-WAIT state:
  • The most known one is to prevent delayed segments from one connection being accepted by a later connection relying on the same quadruplet (source address, source port, destination address, destination port). The sequence number also needs to be in a certain range to be accepted. This narrows a bit the problem but it still exists, especially on fast connections with large receive windows. RFC 1337 explains in details what happens when the TIME-WAIT state is deficient3. Here is an example of what could be avoided if the TIME-WAIT state wasn t shortened:
Duplicate segments accepted in another connection
  • The other purpose is to ensure the remote end has closed the connection. When the last ACK is lost, the remote end stays in the LAST-ACK state4. Without the TIME-WAIT state, a connection could be reopened while the remote end still thinks the previous connection is valid. When it receives a SYN segment (and the sequence number matches), it will answer with a RST as it is not expecting such a segment. The new connection will be aborted with an error:
Last ACK lost RFC 793 requires the TIME-WAIT state to last twice the time of the MSL. On Linux, this duration is not tunable and is defined in include/net/tcp.h as one minute:
#define TCP_TIMEWAIT_LEN (60*HZ) /* how long to wait to destroy TIME-WAIT
                                  * state, about 60 seconds     */
There have been propositions to turn this into a tunable value but it has been refused on the ground the TIME-WAIT state is a good thing.

Problems Now, let s see why this state can be annoying on a server handling a lot of connections. There are three aspects of the problem:
  • the slot taken in the connection table preventing new connections of the same kind,
  • the memory occupied by the socket structure in the kernel, and
  • the additional CPU usage.
The result of ss -tan state time-wait wc -l is not a problem per se!

Connection table slot A connection in the TIME-WAIT state is kept for one minute in the connection table. This means, another connection with the same quadruplet (source address, source port, destination address, destination port) cannot exist. For a web server, the destination address and the destination port are likely to be constant. If your web server is behind a L7 load-balancer, the source address will also be constant. On Linux, the client port is by default allocated in a port range of about 30,000 ports (this can be changed by tuning net.ipv4.ip_local_port_range). This means that only 30,000 connections can be established between the web server and the load-balancer every minute, so about 500 connections per second. If the TIME-WAIT sockets are on the client side, such a situation is easy to detect. The call to connect() will return EADDRNOTAVAIL and the application will log some error message about that. On the server side, this is more complex as there is no log and no counter to rely on. In doubt, you should just try to come with something sensible to list the number of used quadruplets:
$ ss -tan 'sport = :80'   awk ' print $(NF)" "$(NF-1) '   \
>     sed 's/:[^ ]*//g'   sort   uniq -c
    696 10.24.2.30 10.33.1.64
   1881 10.24.2.30 10.33.1.65
   5314 10.24.2.30 10.33.1.66
   5293 10.24.2.30 10.33.1.67
   3387 10.24.2.30 10.33.1.68
   2663 10.24.2.30 10.33.1.69
   1129 10.24.2.30 10.33.1.70
  10536 10.24.2.30 10.33.1.73
The solution is more quadruplets5. This can be done in several ways (in the order of difficulty to setup):
  • use more client ports by setting net.ipv4.ip_local_port_range to a wider range,
  • use more server ports by asking the web server to listen to several additional ports (81, 82, 83, ),
  • use more client IP by configuring additional IP on the load balancer and use them in a round-robin fashion,
  • use more server IP by configuring additional IP on the web server6.
Of course, a last solution is to tweak net.ipv4.tcp_tw_reuse and net.ipv4.tcp_tw_recycle. Don t do that yet, we will cover those settings later.

Memory With many connections to handle, leaving a socket open for one additional minute may cost your server some memory. For example, if you want to handle about 10,000 new connections per second, you will have about 600,000 sockets in the TIME-WAIT state. How much memory does it represent? Not that much! First, from the application point of view, a TIME-WAIT socket does not consume any memory: the socket has been closed. In the kernel, a TIME-WAIT socket is present in three structures (for three different purposes):
  1. A hash table of connections, named the TCP established hash table (despite containing connections in other states) is used to locate an existing connection, for example when receiving a new segment. Each bucket of this hash table contains both a list of connections in the TIME-WAIT state and a list of regular active connections. The size of the hash table depends on the system memory and is printed at boot:
    $ dmesg   grep "TCP established hash table"
    [    0.169348] TCP established hash table entries: 65536 (order: 8, 1048576 bytes)
    
    It is possible to override it by specifying the number of entries on the kernel command line with the thash_entries parameter. Each element of the list of connections in the TIME-WAIT state is a struct tcp_timewait_sock, while the type for other states is struct tcp_sock7:
    struct tcp_timewait_sock  
        struct inet_timewait_sock tw_sk;
        u32    tw_rcv_nxt;
        u32    tw_snd_nxt;
        u32    tw_rcv_wnd;
        u32    tw_ts_offset;
        u32    tw_ts_recent;
        long   tw_ts_recent_stamp;
     ;
    struct inet_timewait_sock  
        struct sock_common  __tw_common;
        int                     tw_timeout;
        volatile unsigned char  tw_substate;
        unsigned char           tw_rcv_wscale;
        __be16 tw_sport;
        unsigned int tw_ipv6only     : 1,
                     tw_transparent  : 1,
                     tw_pad          : 6,
                     tw_tos          : 8,
                     tw_ipv6_offset  : 16;
        unsigned long            tw_ttd;
        struct inet_bind_bucket *tw_tb;
        struct hlist_node        tw_death_node;
     ;
    
  2. A set of lists of connections, called the death row , is used to expire the connections in the TIME-WAIT state. They are ordered by how much time left before expiration. It uses the same memory space as for the entries in the hash table of connections. This is the struct hlist_node tw_death_node member of struct inet_timewait_sock.
  3. A hash table of bound ports, holding the locally bound ports and the associated parameters, is used to determine if it is safe to listen to a given port or to find a free port in the case of dynamic bind. The size of this hash table is the same as the size of the hash table of connections:
    $ dmesg   grep "TCP bind hash table"
    [    0.169962] TCP bind hash table entries: 65536 (order: 8, 1048576 bytes)
    
    Each element is a struct inet_bind_socket. There is one element for each locally bound port. A TIME-WAIT connection to a web server is locally bound to the port 80 and shares the same entry as its sibling TIME-WAIT connections. On the other hand, a connection to a remote service is locally bound to some random port and does not share its entry.
So, we are only concerned by the space occupied by struct tcp_timewait_sock and struct inet_bind_socket. There is one struct tcp_timewait_sock for each connection in the TIME-WAIT state, inbound or outbound. There is one dedicated struct inet_bind_socket for each outbound connection and none for an inbound connection. A struct tcp_timewait_sock is only 168 bytes while a struct inet_bind_socket is 48 bytes:
$ sudo apt-get install linux-image-$(uname -r)-dbg
[...]
$ gdb /usr/lib/debug/boot/vmlinux-$(uname -r)
(gdb) print sizeof(struct tcp_timewait_sock)
 $1 = 168
(gdb) print sizeof(struct tcp_sock)
 $2 = 1776
(gdb) print sizeof(struct inet_bind_bucket)
 $3 = 48
So, if you have about 40,000 inbound connections in the TIME-WAIT state, it should eat less than 10MB of memory. If you have about 40,000 outbound connections in the TIME-WAIT state, you need to account for 2.5MB of additional memory. Let s check that by looking at the output of slabtop. Here is the result on a server with about 50,000 connections in the TIME-WAIT state, 45,000 of which are outbound connections:
$ sudo slabtop -o   grep -E '(^  OBJS tw_sock_TCP tcp_bind_bucket)'
  OBJS ACTIVE  USE OBJ SIZE  SLABS OBJ/SLAB CACHE SIZE NAME                   
 50955  49725  97%    0.25K   3397       15     13588K tw_sock_TCP            
 44840  36556  81%    0.06K    760       59      3040K tcp_bind_bucket
There is nothing to change here: the memory used by TIME-WAIT connections is really small. If your server need to handle thousands of new connections per second, you need far more memory to be able to efficiently push data to clients. The overhead of TIME-WAIT connections is negligible.

CPU On the CPU side, searching for a free local port can be a bit expensive. The work is done by the inet_csk_get_port() function which uses a lock and iterate on locally bound ports until a free port is found. A large number of entries in this hash table is usually not a problem if you have a lot of outbound connections in the TIME-WAIT state (like ephemeral connections to a memcached server): the connections usually share the same profile, the function will quickly find a free port as it iterates on them sequentially.

Other solutions If you still think you have a problem with TIME-WAIT connections after reading the previous section, there are three additional solutions to solve them:
  • disable socket lingering,
  • net.ipv4.tcp_tw_reuse, and
  • net.ipv4.tcp_tw_recycle.

Socket lingering When close() is called, any remaining data in the kernel buffers will be sent in the background and the socket will eventually transition to the TIME-WAIT state. The application can continue to work immediatly and assume that all data will eventually be safely delivered. However, an application can choose to disable this behaviour, known as socket lingering. There are two flavors:
  1. In the first one, any remaining data will be discarded and instead of closing the connection with the normal four-packet connection termination sequence, the connection will be closed with a RST (and therefore, the peer will detect an error) and will be immediatly destroyed. No TIME-WAIT state in this case.
  2. With the second flavor, if there is any data still remaining in the socket send buffer, the process will sleep when calling close() until either all the data is sent and acknowledged by the peer or the configured linger timer expires. It is possible for a process to not sleep by setting the socket as non-blocking. In this case, the same process happens in the background. It permits the remaining data to be sent during a configured timeout but if the data is succesfully sent, the normal close sequence is run and you get a TIME-WAIT state. And on the other case, you ll get the connection close with a RST and the remaining data is discarded.
In both cases, disabling socket lingering is not a one-size-fits-all solution. It may be used by some applications like HAProxy or Nginx when it is safe to use from the upper protocol point of view. There are good reasons to not disable it unconditionnaly.

net.ipv4.tcp_tw_reuse The TIME-WAIT state prevents delayed segments to be accepted in an unrelated connection. However, on certain conditions, it is possible to assume a new connection s segment cannot be misinterpreted with an old connection s segment. RFC 1323 presents a set of TCP extensions to improve performance over high-bandwidth paths. Among other things, it defines a new TCP option carrying two four-byte timestamp fields. The first one is the current value of the timestamp clock of the TCP sending the option while the second one is the most recent timestamp received from the remote host. By enabling net.ipv4.tcp_tw_reuse, Linux will reuse an existing connection in the TIME-WAIT state for a new outgoing connection if the new timestamp is strictly bigger than the most recent timestamp recorded for the previous connection: an outgoing connection in the TIME-WAIT state can be reused after just one second. How is it safe? The first purpose of the TIME-WAIT state was to avoid duplicate segments to be accepted in an unrelated connection. Thanks to the use of timestamps, such a duplicate segments will come with an outdated timestamp and therefore be discarded. The second purpose was to ensure the remote end is not in the LAST-ACK state because of the lost of the last ACK. The remote end will retransmit the FIN segment until:
  1. it gives up (and tear down the connection), or
  2. it receives the ACK it is waiting (and tear down the connection), or
  3. it receives a RST (and tear down the connection).
If the FIN segments are received in a timely manner, the local end socket will still be in the TIME-WAIT state and the expected ACK segments will be sent. Once a new connection replaces the TIME-WAIT entry, the SYN segment of the new connection is ignored (thanks to the timestamps) and won t be answered by a RST but only by a retransmission of the FIN segment. The FIN segment will then be answered with a RST (because the local connection is in the SYN-SENT state) which will allow the transition out of the LAST-ACK state. The initial SYN segment will eventually be resent (after one second) because there was no answer and the connection will be established without apparent error, except a slight delay: Last ACK lost and timewait reuse It should be noted that when a connection is reused, the TWRecycled counter is increased (despite its name).

net.ipv4.tcp_tw_recycle This mechanism also relies on the timestamp option but affects both incoming and outgoing connections which is handy when the server usually closes the connection first8. The TIME-WAIT state is scheduled to expire sooner: it will be removed after the retransmission timeout (RTO) interval which is computed from the RTT and its variance. You can spot the appropriate values for a living connection with the ss command:
$ ss --info  sport = :2112 dport = :4057
State      Recv-Q Send-Q    Local Address:Port        Peer Address:Port   
ESTAB      0      1831936   10.47.0.113:2112          10.65.1.42:4057    
         cubic wscale:7,7 rto:564 rtt:352.5/4 ato:40 cwnd:386 ssthresh:200 send 4.5Mbps rcv_space:5792
To keep the same guarantees the TIME-WAIT state was providing, while reducing the expiration timer, when a connection enters the TIME-WAIT state, the latest timestamp is remembered in a dedicated structure containing various metrics for previous known destinations. Then, Linux will drop any segment from the remote host whose timestamp is not strictly bigger than the latest recorded timestamp, unless the TIME-WAIT state would have expired:
if (tmp_opt.saw_tstamp &&
    tcp_death_row.sysctl_tw_recycle &&
    (dst = inet_csk_route_req(sk, &fl4, req, want_cookie)) != NULL &&
    fl4.daddr == saddr &&
    (peer = rt_get_peer((struct rtable *)dst, fl4.daddr)) != NULL)  
        inet_peer_refcheck(peer);
        if ((u32)get_seconds() - peer->tcp_ts_stamp < TCP_PAWS_MSL &&
            (s32)(peer->tcp_ts - req->ts_recent) >
                                        TCP_PAWS_WINDOW)  
                NET_INC_STATS_BH(sock_net(sk), LINUX_MIB_PAWSPASSIVEREJECTED);
                goto drop_and_release;
         
 
When the remote host is in fact a NAT device, the condition on timestamps will forbid allof the hosts except one behind the NAT device to connect during one minute because they do not share the same timestamp clock. In doubt, this is far better to disable this option since it leads to difficult to detect and difficult to diagnose problems. The LAST-ACK state is handled in the exact same way as for net.ipv4.tcp_tw_recycle.

Summary The universal solution is to increase the number of possible quadruplets by using, for example, more server ports. This will allow you to not exhaust the possible connections with TIME-WAIT entries. On the server side, do not enable net.ipv4.tcp_tw_recycle unless you are pretty sure you will never have NAT devices in the mix. Enabling net.ipv4.tcp_tw_reuse is useless for incoming connections. On the client side, enabling net.ipv4.tcp_tw_reuse is another almost-safe solution. Enabling net.ipv4.tcp_tw_recycle in addition to net.ipv4.tcp_tw_reuse is mostly useless. And a final quote by W. Richard Stevens, in Unix Network Programming:
The TIME_WAIT state is our friend and is there to help us (i.e., to let old duplicate segments expire in the network). Instead of trying to avoid the state, we should understand it.

  1. Notably, fiddling with net.netfilter.nf_conntrack_tcp_timeout_time_wait won t change anything on how the TCP stack will handle the TIME-WAIT state.
  2. This diagram is licensed under the LaTeX Project Public License 1.3. The original file is available on this page.
  3. The first work-around proposed in RFC 1337 is to ignore RST segments in the TIME-WAIT state. This behaviour is controlled by net.ipv4.rfc1337 which is not enabled by default on Linux because this is not a complete solution to the problem described in the RFC.
  4. While in the LAST-ACK state, a connection will retransmit the last FIN segment until it gets the expected ACK segment. Therfore, it is unlikely we stay long in this state.
  5. On the client side, older kernels also have to find a free local tuple (source address and source port) for each outgoing connection. Increasing the number of server ports or IP won t help in this case. Linux 3.2 is recent enough to be able to share the same local tuple for different destinations. Thanks to Willy Tarreau for his insight on this aspect.
  6. This last solution may seem a bit dumb since you could just use more ports but some servers are not able to be configured this way. The before last solution can also be quite cumbersome to setup, depending on the load-balancing software, but uses less IP than the last solution.
  7. The use of a dedicated memory structure for sockets in the TIME-WAIT is here since Linux 2.6.14. The struct sock_common structure is a bit more verbose and I won t copy it here.
  8. When the server closes the connection first, it gets the TIME-WAIT state while the client will consider the corresponding quadruplet free and hence may reuse it for a new connection.

Bits from Debian: Invitation to the MiniDebConf 2014 Barcelona: 15-16 March 2014

Debian Women will hold a MiniDebConf in Barcelona on Saturday 15th and Sunday 16th of March, 2014. Everyone is invited to both talks and social events, but the speakers will all be people who identify themselves as female. This is not a conference about women in Free Software, or women in Debian, rather a usual Debian Mini-DebConf where all the speakers are women. The talks schedule has already been published. It is going to be an exciting event, packed with interesting talks for all audiences, in a beautiful venue, in one of the most famous European cities. Registration is not mandatory, but strongly encouraged, as it helps the event's organisation and logistics. Please, register in the wiki. We are still raising funds to cover the costs of running the conference and to offer travel sponsorship to people who can't pay for it. Please, consider donating any amount you can in our crowd-funding campaign, or contact us if you would like to become a sponsor. The conference organisers want to thank the organisations that have already became sponsors, making this event possible, and specially our Platinum sponsor, Google; our Gold sponsors, C tedra de Programari Lliure - Universitat Polit cnica de Catalunya, Blue Systems and our Silver sponsors, CAtalan LInux Users, CAPSiDE and Fluendo. For more information, visit the website of the event: http://bcn2014.mini.debconf.org

Matthew Garrett: The importance of a community-focused mindset

Piston, an Openstack-in-a-box vendor[1] are a sponsor of the Red Hat[2] Summit this year. Last week they briefly ceased to be for no publicly stated reason, although it's been sugggested that this was in response to Piston winning a contract that Red Hat was also bidding on. This situation didn't last for long - Red Hat's CTO tweeted that this was an error and that Red Hat would pay Piston's sponsorship fee for them.

To Red Hat's credit, having the CTO immediately and publicly accept responsibility and offer reparations seems like the best thing they could possibly do in the situation and demonstrates that there are members of senior management who clearly understand the importance of community collaboration to Red Hat's success. But that leaves open the question of how this happened in the first place.

Red Hat is big on collaboration. Workers get copies of the Red Hat Brand Book, an amazingly well-written description of how Red Hat depends on the wider community. New hire induction sessions stress the importance of open source and collaboration. Red Hat staff are at the heart of many vital free software projects. As far as fundamentally Getting It is concerned, Red Hat are a standard to aspire to.

Which is why something like this is somewhat unexpected. Someone in Red Hat made a deliberate choice to exclude Piston from the Summit. If the suggestion that this was because of commercial concerns is true, it's antithetical to the Red Hat Way. Piston are a contributor to upstream Openstack, just as Red Hat are. If Piston can do a better job of selling that code than Red Hat can, the lesson that Red Hat should take away is that they need to do a better job - not punish someone else for doing so.

However, it's not entirely without precedent. The most obvious example is the change to kernel packaging that happened during the RHEL 6 development cycle. Previous releases had included each individual modification that Red Hat made to the kernel as a separate patch. From RHEL 6 onward, all these patches are merged into one giant patch. This was intended to make it harder for vendors like Oracle to compete with RHEL by taking patches from upcoming RHEL point releases, backporting them to older ones and then selling that to Red Hat customers. It obviously also had the effect of hurting other distributions such as Debian who were shipping 2.6.32-based kernels - bugs that were fixed in RHEL had to be separately fixed in Debian, despite Red Hat continuing to benefit from the work Debian put into the stable 2.6.32 point releases.

It's almost three years since that argument erupted, and by and large the community seems to have accepted that the harm Oracle were doing to Red Hat (while giving almost nothing back in return) justified the change. The parallel argument in the Piston case might be that there's no reason for Red Hat to give advertising space to a company that's doing a better job of selling Red Hat's code than Red Hat are. But the two cases aren't really equal - Oracle are a massively larger vendor who take significantly more from the Linux community than they contribute back. Piston aren't.

Which brings us back to how this could have happened in the first place. The Red Hat company culture is supposed to prevent people from thinking that this kind of thing is acceptable, but in this case someone obviously did. Years of Red Hat already having strong standing in a range of open source communities may have engendered some degree of complacency and allowed some within the company to lose track of how important Red Hat's community interactions are in perpetuating that standing. This specific case may have been resolved without any further fallout, but it should really trigger an examination of whether the reality of the company culture still matches the theory. The alternative is that this kind of event becomes the norm rather than the exception, and it takes far less time to lose community goodwill than it takes to build it in the first place.

[1] And, in the spirit of full disclosure, a competitor to my current employer
[2] Furthering the spirit of full disclosure, a former employer

comment count unavailable comments

Andrew Pollock: [life] Day 27, Kindergarten, Debian, Hawthorne Road

I realised yesterday morning that I will have biked up Hawthorne Road at least once a day for 5 days in a row by tomorrow (unless it happens to rain). It's not a bad hill, really, it has a sort of a stair-step gradient. There's a short, gentle incline, just to get your heart going, then there's a flat bit, to recover, then there's a less friendly incline, which is both more unfriendly and longer. Then you get to the top, gasping for breath, before there's a short decline and usually a red traffic light. This morning I had the bright idea of leaving the bike trailer at Kindergarten, so it made the journey home much more pleasant, as was the aforementioned climb up Hawthorne Road in the afternoon. I spent the day doing Debian stuff, but unfortunately didn't result in a package upload to show for it. Library packages are tricky, and I'm far from experienced or competent at maintaining them. Zoe didn't nap today at Kindergarten, and wasn't too worse for wear for it. When we got home, Zoe wanted to make a crown for Mummy like the one she made at Playgroup last week. Unfortunately we didn't really have any good crown-sized paper, so I made a little crown out of some surplus Letter-sized paper, and then Zoe decided to do some painting. The painting devolved into a lot of hand painting of her cardboard box rocket, inside and out. We managed to keep the mess to a minimum. After we cleaned up, Zoe watched a bit of TV, and my girlfriend came over and together we all made a vegetable stir fry for dinner. After dinner we walked down to the Hawthorne Garage to get some unwanted cardboard fruit boxes, to help with packing for our two night trip to Coochiemudlo Island later this week. Bedtime went pretty smoothly. Zoe managed to get a bunch of insect bites yesterday, which was the cause of a 4am wake up this morning. They're still giving her grief, so I'm expecting some sort of disturbance overnight tonight.

Rog rio Brito: Trivial fact #3: Continued fractions via matrices

Note Apparently, it's not Debian planet that has problems to deal with MathJax (which makes posts usingn it appear illegible on Debian planet), but the ikiwiki plugin that I am using which generates garbage in the feeds that get consumed by planet.debian.org. If you it know of a better plugin (which doesn't generate such output) please let me know, especially if it is not super computationally expensive for a Core 2 Duo T7250 (which is my notebook).

The real thing As William Stein is now offering a course on Number Theory and he has been posting recorded videos of his lectures, I started watching some of them (mainly, the ones regarding continued factions). In particular, he shows the usual recursive formula for convergents of a continued fraction and that's super nice. For the curious reader, the recurrence relations for the convergents of !!mathjaxbegin-i!! W2FfMCwgYV8xLCBcbGRvdHMsIGFfbiwgXGxkb3RzXQ== !!mathjaxend-i!! are: !!mathjaxbegin-d!! CnBfbiA9IGFfbiBwX3tuLTF9ICsgcF97bi0yfVxcCnFfbiA9IGFfbiBxX3tuLTF9ICsgcV97bi0y fSwK !!mathjaxend-d!! with initial conditions (!!mathjaxbegin-i!! cF97LTJ9ID0gMA== !!mathjaxend-i!!, !!mathjaxbegin-i!! cF97LTF9ID0gMQ== !!mathjaxend-i!!, !!mathjaxbegin-i!! cF8wID0gYV8w !!mathjaxend-i!!, !!mathjaxbegin-i!! cV97LTJ9ID0gMQ== !!mathjaxend-i!!, !!mathjaxbegin-i!! cV97LTF9ID0gMA== !!mathjaxend-i!!, !!mathjaxbegin-i!! cV8wID0gMQ== !!mathjaxend-i!!). He even motivated the use of continued fractions with the golden ratio, which is super nice, given that I like the subject and have been writing a document collecting facts that I know about the Fibonacci numbers (well, this document is horribly incomplete and not even close to something that I would consider proper for public consumption I plan on publishing them soon). OK, after he discussed the basics of it convergents, he noted that the recurrence relations are like those defining the Fibonacci numbers, just that one of the terms is "weighted" by the coefficients of the continued fraction. I missed one thing, though: neither his book nor wikipedia's article on continued fractions mentions a very neat, alternative way to express the convergents of continued fractions (truth be said, I took a quick peek at wikipedia's article and I found that it doesn't mentionat least explicitly, in a 1 min skim it may well be buried somewhere else). I, then, proposed the following exercise for his students (which he apparently liked, as he +1's the suggestion): Prove that the recurrence relation of the !!mathjaxbegin-i!! cF9p !!mathjaxend-i!!'s and !!mathjaxbegin-i!! cV9p !!mathjaxend-i!!'s that we mentioned before can be obtained via matrix multiplication. More precisely, prove that: !!mathjaxbegin-d!! ClxiZWdpbntibWF0cml4fQphXzAgJmFtcDsgMVxcCjEgJmFtcDsgMApcZW5ke2JtYXRyaXh9Clxi ZWdpbntibWF0cml4fQphXzEgJmFtcDsgMVxcCjEgJmFtcDsgMApcZW5ke2JtYXRyaXh9ClxjZG90 cwpcYmVnaW57Ym1hdHJpeH0KYV9uICZhbXA7IDFcXAoxICZhbXA7IDAKXGVuZHtibWF0cml4fQog PQpcYmVnaW57Ym1hdHJpeH0KcF9uICZhbXA7IHBfe24tMX1cXApxX24gJmFtcDsgcV97bi0xfQpc ZW5ke2JtYXRyaXh9Lgo= !!mathjaxend-d!! As a corollary, derive Cassini's identity for the Fibonacci Numbers.
Please, if you any errors on this, please let me know so that I can fix it. Edit: Thanks "noone" for spotting a typographical error.

Daniel Kahn Gillmor: Inline-PGP considered harmful

We changed the default PGP signatures generated by enigmail in debian from Inline PGP to PGP/MIME last year, and the experiment has gone well enough that we're now using it in jessie and wheezy (where it arrived as part of a security update to make the extension work with the security-updated icedove package). After having several people poke me in different contexts about why inline cleartext PGP signatures are a bad idea, i got sufficiently tired of repeating myself, and finally documented some of the problems explicitly. The report includes a demonstration of a content-tampering attack that changes the meaning of a signed inline-PGP message without breaking the signature, which i first worked out on the notmuch mailing list, but hadn't gotten around to demonstrating until recently. The attack is demonstrated against clearsigned messages, but also works against inline encrypted messages (but is harder to demonstrate since a demonstration would require sharing secret key material for the decryption step). Please don't generate Inline-PGP messages. And if you must parse and accept them, please consider carefully the risks you expose your users to and think about ways to mitigate the problems.Tags: charset, inline-pgp, openpgp, security

23 February 2014

Paul Tagliamonte: Debile + Docker = love

I ve spent a bit of time this saturday Dockerizing Debile s slave / workers (for those who don t know about Debile yet, there are a few posts where I explain it) Many thanks to Tianon Gravi for his work in helping me out :) I created two images to test - the base image for any slave (paultag/debile-slave-base, and a preconfigured image for our test master server. This includes a script to preconfigure the slave worker (OpenPGP keys, username, password) that are passed to it via a tarball generated by debile-remote. Hopefully this makes deploying debile slaves easier :) I was able to do a test build of about 300 packages with the dockerized slave, and I think it s a huge step forward. Onward!

Russell Coker: Electric Car Charging in Melbourne

GoGet plug-in Prius chargingChargePoint Chargers This morning I noticed some parking bays reserved for car charging in a car park at the corner of Sydney Rd and Glenlyon St in Brunswick (near Aldi). One of the parking spots was occupied by a Plug-in Prius from GoGet [1]. I didn t even realise that you could get a plug-in Prius in Australia. The charging station is run by Charge Point [2]. The charging points are about 1.5m high and the cable is about 3cm thick (about as thick as the pipe used for filling a car with petrol), so it would charge a car much faster than could be done with a regular power point. One big problem with the Charge Point web site is that they don t give any information on pricing. They sell home charge points (which I guess means just an all-weather two-phase power point) but don t give a price for that. They sell charge points that can be used by commercially but don t give a price for them either. Also their infrastructure for billing is apparently based on companies installing charge points and setting a price for the service. Some charge points may offer free service (I guess staff car parks and some government agencies) and others will charge varying rates none of which is available on the web site. Apparently they have an online portal which gives information on such things to registered users so you have to register to discover what it costs. Of course hardly anyone is going to register before discovering the price, not even when registration is free. But while registration is free the web site demands the make and model of the electric car, so presumably one has to spend $40,000 or more on a vehicle before discovering the price and availability of charging it. Charge Point can be used as an example of how not to design a web site that promotes a service, or at least how not to promote a service that is aimed at saving money (electricity is significantly cheaper than petrol so it s of interest to people and organisations that want to save money). The Charge Point site seems to be better suited to showing that the concept can work than convincing people that they should sign up for it. It seems to me that the best thing that they could do would be to prominently display the average cost of all non-free charge points that are open to the public along with an explanation of the price of driving a desirable car (such as a plug-in Prius or a Nissan Leaf) with such an electricity cost. The contact section on the web site only has a link for careers . I don t think it s possible to get widespread use of electric vehicles without getting better information out there. It appears that Charge Point is relying on councils to do the work of promoting their business by installing their stations and reserving car parking as Moreland council has done in this case.

Andrew Pollock: [tech] My thoughts on the Ozobot Kickstarter campaign

I'm not an avid Kickstarter follower (if I were, I'd have gone broke long ago). I tend to wind up backing campaigns that come to my attention via other means (in other words, they're in the process of going viral). That said, I've backed plenty of campaigns over the years, and so I'd like to think I have a little bit of familiarity with how they usually operate. When Ozobot came to my attention, I found it unusual, because they were pre-promoting their Kickstarter campaign before it opened. To me, this looked like a case of them trying to build hype prior to the campaign opening, which was a new one to me. The whole thing seemed incredibly slick, and I was surprised they were "only" seeking $100K. The product looked like it'd be something cool for Zoe to play with, so I decided to back it anyway. Then all the updates started flowing in about how well it was being received at various trade shows and whatnot. Yet the amount of dollars flowing into the Kickstarter campaign didn't seem to be reflecting the external hype. I was watching the campaign's dashboard with great interest, because as time marched on, it was looking more and more likely that it wasn't going to make its funding target. This seemed highly unusual to me, given the slickness of the product and purported external interest in it. And then they pulled the plug on the campaign. Purportedly because they were pursuing equity funding instead. They admitted they'd also read the writing on the wall and it was unlikely they were going to make their funding target. I haven't followed other campaigns to see how much of a last minute funding "pop" they have. Usually I've found they've closed at many multiples of their original target, and hit their target well in advance of their deadline, when they're ridiculously popular. My interpretation of Ozobot's campaign, from a funding perspective, is that Kickstarters gave it a big fat "MEH", which surprised me somewhat. Then the question comes up: was the Kickstarter campaign a ruse all along? Was it just a new way of pitching for venture capital? The videos seemed pretty slick. The product seemed already complete, and $100K didn't seem like enough to take it to manufacturing. It'll be interesting to see what becomes of Ozobot now.

Sylvain Le Gall: Release of OASIS 0.4.2

I am happy to announce the release of OASIS v0.4.2. Logo OASIS small OASIS is a tool to help OCaml developers to integrate configure, build and install systems in their projects. It should help to create standard entry points in the source code build system, allowing external tools to analyse projects easily. This tool is freely inspired by Cabal which is the same kind of tool for Haskell. You can find the new release here and the changelog here. More information about OASIS in general on the OASIS website. Here is a quick summary of the important changes: BSD3 and BSD4 are still valid but marked as deprecated. When one of the modules of a library has the name of the library, ocamlbuild tends to just transform this module into a .cmxs. Now, the use of a .mldylib fix that problem and the .cmxs really contains all modules of the library. I have published a quick intermediate version 0.4.1, a few days after the previous release. This was a bug fix related to threads. I also decided to skip the release of last month. I was in the US at this time and didn't have time to work enough on OASIS (christmas vacation and a travel to the US). This month I am back on track. This new version doesn't feature a lot of visible changes. I mostly work on the command line interface code, in order to be able to create external plugins. A first external plugin is almost ready, but need some more polishing before release. This first plugin project is a port of the script that I have used for a long time and that was present in the source code of oasis (oasis-dist.ml). It will be a project on its own and have a different release cycle. The point of this plugin is to create .tar.gz out of an OASIS enabled project. I also must admit that I am very happy to see contributors sending me pull-request through GitHub. It helps me a lot and I also realize that the learning curve to enter OASIS code is steep. This last point is something I will try to improve.

Steve Kemp: Two minor toys ..

Two minor things:
graphite_send
A simple shell-script to submit metrics to a graphite server, extensible via local plugins, but covers the obvious metrics by default. Metrics are submitted via simple calls to netcat. Trivial, but much more lightweight than collectd and similar.
HTML::Emoji
A perl module for converting HTML like "<p>:smile:</p>" into something graphical. This was written for my markdown sharing site, but is pretty fun. The konami-code page demonstrates usage. (This parses the HTML so it won't transform attributes, ids, or anything that isn't in the "text" part of any HTML input.)
The graphite sending script is perhaps the most useful, but at the same time it feels too small to be a package of its own. I'm tempted to bundle it up into my sysadmin-util collection, but I can't quite decide if it belongs there either.

Vincent Cheng: Hello, Planet Debian! (also, RFH: sponsorship-requests)

Hi Debian! Just to briefly introduce myself, I'm Vincent (vcheng@d.o, vincent_c on OFTC/Freenode) and I'm a recent graduate of the NM process, having attained DD-ship (is that even a word?) about a month ago in January. Before that, I was a DM since mid-2012, and just another contributor for a few years prior to that. Most of my contributions to the Project are related to packaging, especially packages maintained within the Debian Games Team. Outside of Debian, well, I'm just another 20-year-old, 3rd-year undergrad student studying at the University of British Columbia, working towards a major in computer science. I anticipate that I'll be able to ditch academia for good in 2016; just 2 more years to go... More about my life story in my AM's report. It's fairly boring, if I say so myself. This blog post isn't just about me; I'd like to touch upon another topic that I consider important, i.e. attracting new contributors, and in many cases that involves package sponsorship. That's one of the many things I'd like to work on as a DD, and to that effect I've dedicated a large chunk of the time I currently spend on Debian sponsoring various packages, including packages that I'm not familiar with. I would love to see the sponsorship-requests queue empty one day, but I admit that I find that increasingly unlikely to happen, now that I've gotten a taste of the time commitment involved with sponsoring. Team maintenance and sponsorship seems to work relatively well in Debian; why does that success not translate over to sponsorship-requests / debian-mentors@l.d.o, where a considerable amount of RFS requests don't see any response at all, and merely get closed once those packages get removed from mentors.debian.net (AFAIK they automatically get removed after 20 weeks)? Well, I'm not here to offer an answer for that, but I will point out that there was a relevant thread that originated on debian-devel a month ago: <87ha8lzl7n.fsf@inf-8660.int-evry.fr> (and no, I'm not talking about the giant init-related threads that pop up on debian-devel every other week or so and drown out everything else on the list...). Are DDs in general reluctant to engage in "fly-by sponsoring"? Most packages coming through the sponsorship-requests queue are not team-maintained, and are sent from sponsorees who are not already in contact with a sponsor, and who have no other way of getting in touch with a potential sponsor (assuming that there isn't an existing team or a DD who happens to be interested in that package). Regardless of the merits of fly-by sponsoring (many arguments in favour of, and against, this type of sponsorship have already been discussed in that thread; no need to re-iterate them here), it's discouraging for potential contributors new to Debian, who may just give up and move on to something else. I've now had the opportunity to be a sponsor (rather than just a sponsoree), and I acknowledge that being a sponsor is more work than I imagined it to be a month ago, and it can be quite tedious and not-fun at times. I suppose I can draw a parallel between sponsoring packages and RC bug fixing; neither is what I'd consider to be a highly enjoyable way of spending my leisure time, and both can eat up a large chunk of time and effort; both often involve working on something that you aren't familiar with. But both are beneficial to Debian. No, beneficial isn't a strong enough word; how about "essential" instead? Yeah, that makes more sense. Without dedicated RC bug squashers, Debian would never be able to make a release; without dedicated sponsors, the size of Debian's archive would be smaller and of lesser quality, and its community also a lot smaller. With all that said...I hope this blog post inspires at least a few DDs, possibly more, to dedicate a little bit more of their time towards sponsoring packages. :)

22 February 2014

Petter Reinholdtsen: New home and release 1.0 for netgroup and innetgr (aka ng-utils)

Many years ago, I wrote a GPL licensed version of the netgroup and innetgr tools, because I needed them in Skolelinux. I called the project ng-utils, and it has served me well. I placed the project under the Hungry Programmer umbrella, and it was maintained in our CVS repository. But many years ago, the CVS repository was dropped (lost, not migrated to new hardware, not sure), and the project have lacked a proper home since then. Last summer, I had a look at the package and made a new release fixing a irritating crash bug, but was unable to store the changes in a proper source control system. I applied for a project on Alioth, but did not have time to follow up on it. Until today. :) After many hours of cleaning and migration, the ng-utils project now have a new home, and a git repository with the highlight of the history of the project. I published all release tarballs and imported them into the git repository. As the project is really stable and not expected to gain new features any time soon, I decided to make a new release and call it 1.0. Visit the new project home on https://alioth.debian.org/projects/ng-utils/ if you want to check it out. The new version is also uploaded into Debian Unstable.

Next.

Previous.