Search Results: "will"

20 June 2010

Daniel Baumann: Debian Live Web Images Builder

Richard Nelson, an outstanding debian-live contributor and team member since many years, has setup an instance of the live-helper CGI scripts that are included within live-helper. This webbuilder lets users get their own customized images without the need of having to install live-helper and build them on their own. It's available at live-helper.debian.net. Apart from having some better looking html form and adding an online-help that will be worked on soon, it's working great. Thanks you, Richard.

Francois Marier: Reducing website bandwidth usage

There are lots of excellent tools to help web developers optimise their websites.

Here are two simple things you have no excuse for overlooking on your next project.
HTML, XML, Javascript and CSS filesOne of the easiest ways to speed up a website (often to a surprising degree) is to turn on compression of plaintext content through facilities like mod_deflate or the Gzip Module.

Here's the Apache configuration file I normally use:
<ifmodule>AddOutputFilterByType DEFLATE text/html text/plain text/css text/javascript text/xml application/x-javascript application/javascript
BrowserMatch ^Mozilla/4 gzip-only-text/html
BrowserMatch "MSIE 6" no-gzip dont-vary
BrowserMatch ^Mozilla/4\.0[678] no-gzip</ifmodule>
ImagesAs far as images go, the following tools will reduce file sizes through lossless compression (i.e. with no visual changes at all):
(An alternative to optipng is pngcrush.)

Note that the --strip-all argument to jpegoptim will remove any EXIF/comments tags that may be present.

19 June 2010

Torsten Werner: Results from the Debian Community Poll

I have announced the Debian Community Poll in my former blog post. I have closed the poll today and I will start publishing its results now.
What is the codename of the current stable release?This is the only compulsory question with the intention to block spammers. The correct codename is Lenny but I have accepted almost any answer that is somehow related to Debian. Version numbers, names from Sarge to Experimental, even well known codenames and version numbers from Ubuntu have been counted as correct. 22 partipants answered wrongly and their submissions got removed from the result set. A whopping number of 3258 submissions have been accepted and get analyzed now. Thanks to all participants!
How long have you been using Debian?

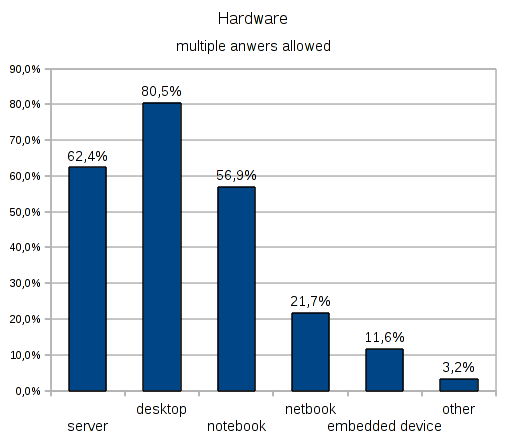
On what kind of hardware are you using Debian?
Multiple answers are allowed for this question and that is why the values do not sum up to 100%.
  • 80.5% are using Debian on the desktop
  • 62.4% on the server
  • 56.9% on the notebook
  • 21.7% on the netbook
  • 11.6% on embedded device(s)
  • 3.2% on other device(s)
The following other devices have been mentioned: smartphone, virtual machine, nettop, NAS, HTPC, workstation, pendrive, live cd, cluster, thin client, router, rocket flight computer, ibm mainframe, and automatic bar tender.

Do you contribute to Debian?
  • 50.0% choose answer #5: I don't contribute on a regular base.
  • 31.2% choose answer #4: I'm regularly helping other Debian users.
  • 8.0% choose other (see below) or simply did not answer
  • 4.9% choose answer #3: I'm regularly contributing to Debian packages without uploading them by myself.
  • 4.5% choose answer #1: I'm a Debian developer.
  • 1.4% choose answer #2: I'm a Debian maintainer.
The following other answers have been provided:
  • upstream developer or contributor
  • translator
  • bug reporter
  • advocator
  • former DD or DM
  • prospective DD or DM
  • mirror maintainer
  • package/installer tester
  • documentation writer
  • donator or debconf sponsor
  • debconf organizer or helper

How do you think about the Debian Free Software Guidelines (DFSG)?
  • 46.0% choose answer #2: I like the DFSG but it is not the most important reason for using Debian.
  • 36.6% choose answer #1: The DFSG is very important to me. I could live with many changes in Debian but I would be very upset if Debian would allow non-free software into its main component in the future.
  • 10.1% choose answer #3: I don't know.
  • 4.9% choose answer #4: I don't care.
  • 2.4% did not answer.

Are you using Debian derived distributions, too?
Multiple answers are allowed for this question and that is why the values do not sum up to 100%. There were a lot of different answers but the most frequent are:
  • 47.1%: Ubuntu (Kubuntu, Lubuntu, Xubuntu)
  • 40.8%: no answer; this was the only way to say that someone does not use a derived distribution
  • 11.0%: other (see below)
  • 7.0%: damn small linux
  • 4.8%: Sidux
  • 4.3%: grml (juxlala)
  • 2.2%: Knoppix
  • 1.6%: ELive
  • 1.4%: Maemo
The other answer includes the following distributions: 64studio, ALT Linux, arch linux, ArtistX, BackTrack, BRLix, Canaima GNU/Linux, catix, cdlinux.pl, CloneZilla, CrunchBang, Custom, ddwrt, debian arm userspace for zipit z2, DebXO (?), DreamLinux, Easy Peasy, eb4, eeebuntu, EMC2 Ubuntu (linuxcnc.org), Emdebian, Estrella Roja, Fedora, Finnix, Gentoo, gNewSense, Hackable:1, Kanotix, Kuliax, LFS and CLFS, LinEx, Linux Mint, live CDs, live-helper, Mepis antix, Musix, My own LiveCD, Mythbuntu, OpenInkpot, openwrt, paipix gnu, Parsix, Peppermint, personal debian derived, proxmox, Puppy, PureOS, qtopia, SHR, simplyMEPIS, Skolelinux, slackware, SymphonyOS, Toutou, Trisquel, tty GNU/Linux, UHU Linux, Univention Corporate Server, vinux, Voyage, Vyatta, whiite, Xandros, Xarnoppix. Not all of them are derived from Debian.

- to be continued -

Julien Valroff: My experience without Adobe Flash Player

Adobe recently announced they have (temporarily) stopped working on the amd64 version of their Flash Player for GNU/Linux. The previous releases contain a big security issue, which makes them totally unusable. As I didn t want to wait until the flashplugin-nonfree package to be updated to support the i386 plugin through nspluginwrapper (as suggested in #586273), I have decided to simply switch to the free alternative: gnash. After a few hours with it, I am now able to use most of the websites I usually visit, including Youtube and Dailymotion. Note that I use Iceweasel, which does not support WebM (for now), nor H.264 (which will never be supported by Mozilla). Youtube support is brought by a Greasemonkey user script available at: http://turanct.wordpress.com/2010/02/25/gnash-youtube/
The only tiny drawback is that the videos load in pause mode. For now, everything else seems to work fine. Users of other browers (Chromium, Safari, Opera) can try their HTML5 beta: http://www.youtube.com/html5 It is even easier for Dailymotion, as the videos on their HTML5 beta program are encoded in the Ogg Theora format, which is natively supported by Iceweasel/Firefox >= 3.5. To ease things, I have written a small Greasemonkey script which simply automatically redirects www.dailymotion.com to openvideo.dailymotion.com. This script can be downloaded here. The drawback is that videos won t play before they are loaded completely, which is not a big problem anyway. I still cannot play the videos avilable on Vimeo, and have noticed while wirting this post that the Flash file uploader of WordPress didn t work with gnash (obviously, WP provides an alternative way for file upload). I will go on with this experience as long as I do not see major issue with gnash.
I will also update this post, or add comments, if I encounter other issues, or find any alternatives. I would be curious to read your comments if you have run similar experience.

18 June 2010

Christoph Berg: Cool Unix Features: flock

Lockfiles are usually hard to get right, especially in sh scripts. The best bet so far was "lockfile" included with procmail, but its semantics are pretty weird. (Try to understand what exit code you want, with or without "-!".) Not to mention that failing to clean up the lockfile will stop the next cron run, etc. Since Lenny, util-linux ships "flock". Now you simply say
$ flock /path/to/lockfile /path/to/command
and are done. If you want it non-blocking, add "-n":
$ flock -n /path/to/lockfile /path/to/command
I should probably migrate all my cronjobs to use this.

16 June 2010

Christoph Berg: Cool Unix Features: /dev/full

I've always thought about collecting random bits of useful/interesting/cool Unix features and the like. Before I let that rot indefinitely in a text file in my $HOME, I'll post it in a series of blog posts. So here's bit #1: Everyone knows /dev/null, and most will know /dev/zero. But /dev/full was unknown to me until some time ago. This device will respond to any write request with ENOSPC, No space left on device. Handy if you want to test if your program catches "disk full" - just let it write there:
$ echo foo > /dev/full
bash: echo: write error: No space left on device

Mehdi Dogguy: Buildd status pages

Recently, I started to write some web tool to track the status of ongoing transitions in unstable. I thought I could use some code from the Buildd status project (to see how it fetches the status for each package). Unfortunately, this caused some nightmares for some WB admin :) (because they used to rely on the generated BDB files and not the PGSql database, where the former is a snapshot of the latter stored in a funny format). Those BDB files were considered deprecated and status pages were looking for some love. Besides, the BDB files were kept in sync by regenerating them regularly (every 15 minutes, AFAIK). So, the information stored there was up-to-date only for a couple of seconds and then outdated, waiting for the next run to be updated. Last weekend, I rewrote the status pages from scratch to make them use the PGSql database. I kept the same user interface (and pages arguments) to make it a drop-in replacement for the old one. Today, thanks to the WB admins, the new status pages replaced the old ones! There are no new visible features for now (except the backend and some links) but I have a list of new features that I intend to implement. These new features will be implemented in my local copy first and then integrated if WB admins want them. And, as some of you already noticed, the new status pages are aware of non-free packages (because it happens that the data is present in the PGSql database :) thank WB admins for that!).

Petter Reinholdtsen: Calling tasksel like the installer, while still getting useful output

A few times I have had the need to simulate the way tasksel installs packages during the normal debian-installer run. Until now, I have ended up letting tasksel do the work, with the annoying problem of not getting any feedback at all when something fails (like a conffile question from dpkg or a download that fails), using code like this:
export DEBIAN_FRONTEND=noninteractive
tasksel --new-install
This would invoke tasksel, let its automatic task selection pick the tasks to install, and continue to install the requested tasks without any output what so ever. Recently I revisited this problem while working on the automatic package upgrade testing, because tasksel would some times hang without any useful feedback, and I want to see what is going on when it happen. Then it occured to me, I can parse the output from tasksel when asked to run in test mode, and use that aptitude command line printed by tasksel then to simulate the tasksel run. I ended up using code like this:
export DEBIAN_FRONTEND=noninteractive
cmd="$(in_target tasksel -t --new-install   sed 's/debconf-apt-progress -- //')"
$cmd
The content of $cmd is typically something like "aptitude -q --without-recommends -o APT::Install-Recommends=no -y install ~t^desktop$ ~t^gnome-desktop$ ~t^laptop$ ~pstandard ~prequired ~pimportant", which will install the gnome desktop task, the laptop task and all packages with priority standard , required and important, just like tasksel would have done it during installation. A better approach is probably to extend tasksel to be able to install packages without using debconf-apt-progress, for use cases like this.

Julien Danjou: Announcing rainbow-mode

While customizing Emacs this last weeks, I had the need to customize also the color theme. Color themes are always a pain in the ass to edit, because you're supposed to read color strings like #aabbcc and guess what colors they represent. This is why I wrote rainbow-mode, a minor mode for Emacs that will highlight strings that represents color, using the color they represent. This support hexadecimal syntax, HTML color name, X color names and rgb() CSS syntax.

15 June 2010

Marco T&uacute;lio Gontijo e Silva: Summer of Code weekly report #5

My project. This post assumes that the reader has read my last post. This was a week full of segfaults, failed assertions, changes in the user data and other crazy stuff. I started working on the allocation of memory on the freed lines. In the first glance, it seemed to be much harder than the small changes I ve done to free memory in lines, because of the a never-seen-before-by-me datatypes being dealed with in alloc_for_copy(), from rts/sm/Evac.c: gen_workspace. But in a short time the code of alloc_for_copy() has shown itself to be simple, and it was easy to do an initial implementation. I went in the same path I was going on before, trying the simplest solution that works. For instance, the line representation used is not ideal, because groups of lines are not considered, but it was the simplest at that time, and I plan to improve it latter. The gen_workspace data type contains a pointer to an area of a block that is not being used (todo_free) and a pointer to the end of that area (todo_lim). When a space for an object is requested, it s allocated in this area, and todo_free is adjusted. If the area is full, a new block is requested. My intended change was to return the first free line of the generation when the object is smaller or equal to the size of a line, and use the current approach otherwise. This is the simplest way I could think, but has the problem that the only one object is allocated per line. This was a known issue.
    if(size <= BITS_IN(W_) && gen->first_line != NULL)  
        to = gen->first_line;
        gen->first_line = (StgPtr) *gen->first_line;
        return to;
     
    ws = &gct->gens[gen->no];
After that I got the first round of segfaults. One problem I could spot so far was in the code in rts/sm/Sweep.c, related to the liberation of the lines. The block is allocated by need, and there s a pointer to the first free byte, free. This free space is used by alloc_for_copy(). So, we should only think of lines in the region already allocated in the block, that is, where the address is smaller than free.
                    if(bd->u.bitmap[i] == 0 && bd->u.bitmap[i - 1] == 0 &&
                       start + BITS_IN(W_) <= bd->free)
But the segfaults, memory corruptions, etc, kept going on. I tried some restrictions, like allocating in lines only objects with the exact size of a line, or very small objects (size == 2), or allocating just one object for generation, or only one object at all. I also tried checking for the type of the allocated object, to see a correlation with the problems I was having. Nothing helped by now. So I thought I should work on other things, so that maybe my mind gets clearer and I can spot the problem. I followed the suggestion of using todo_free and todo_lim to make it possible to allocate more than one object in a line. I liked this change, since I had the impression that it fits better with the rest of the code than the initial implementation, and it will be easier to addapt it when I improve the representation of the free lines. As I said, I wanted something to work while I think in how I ll solve the segfault problems. The bad side of this choice is that I ll not be able to test it, since it s just a reimplementation of the same idea in the allocation code, and is not expected to work. The good size is that it may work, and solve the problems I was having by accident.
    if (ws->todo_free > ws->todo_lim)  
        if (size <= BITS_IN(W_) && gen->first_line != NULL)  
            ws->todo_free = gen->first_line;
            gen->first_line = (StgPtr) *gen->first_line;
            to = ws->todo_free;
            ws->todo_lim = ws->todo_free + BITS_IN(W_);
          else  
            to = todo_block_full(size, ws);
         
     
I got the same results as with the older implementation, and no ideas about how to solve it (yet). So I thought about another thing to work on, which I m talking about all through this post: improve the free line representation. This has the advantage of being testable, since it s unrelated to the allocation code, and may give me an idea about how I can fix the segfaults. The bad side is that it probably won t fix my problems directly. I m working on it right now.
Following a suggestion, I ve started using gdb to see what was happening in the GC instead of including printfs everywhere, and it s been useful. I ve noticed that sometimes printf is more effective, but sometimes gdb is much better.

Craig Small: Australian Internet Censorship and Data Retention

Just going on how they treat matters regarding the internet, it seems that the current Australian government is trying to beat the previous government's poor record. Where the previous government seemed to think the internet a scary and unimportant thing that they didn't really understand and therefore ignored it, the current government seems to be trying to do something, but like a lot of other things they do, do something badly.

Internet Filtering
One of their bright ideas is to censor the internet, by putting some rather large filters right in the middle of all the ISPs. Supposedly this is going to protect the children, though other than some mad ranting by Senator Conroy he hasn't said which children or how.

The clearest information is that it will block Refused Content or RC rated information. The problem with this is there is no clear definition what this is. With no clear boundary you can get what is "scope creep". Bit by bit, each group with their own agenda will try to get whatever they don't like banned. Some will fail, but others will get their little set of demons onto the list.

From "children overboard" to the strange siezure of the wikileaks founder's passport when he returned to Australia, you can never trust the government fully. As the filter list will be a closed list, who is to say if it is right a particular webpage or website should be banned? Books or films that are banned are known, you can find out what they are and why. A proper discussion and review can then be undertaken. By contrast, you won't even know something is banned unless you try to visit it.

I've personally seen the "great firewall of china". What is filtered is often arbitary, though anything that is embarassing to the government is filtered. It slows a lot of sites down and makes others look strange. Do you really what to live in a country where the government decides what ideas should be seen? Or even a country that places like China can point to and say they are doing the same thing, so its all ok?

Data Retention
The next bright idea by the government is to make ISPs keep 10 years of internet browsing history of all their users. This would be like tapping everyone's phone, just in case you did something wrong in the next 10 years.

There hasn't been much detail about this proposal but let's assume for a moment that it keeps URLs. Now of course most people's internet addresses move around, so you will also need to keep some sort of log of which account used what address for the same time.

The URLs will tell the government which websites you have visited, but URLs also tell them which pages you visited. You can also often assume which pages you read and which you didn't because of the time between this viewed page and the next.

Search engine queries are also encoded into a url. Google searches usually have something at the end of the url which is what you were searching for. There is also a chain of visited pages, so someone looking at a log could see your search, you go to a site, perhaps you then visit a banking or paypal site (have you bought something now?)

Even if you think you have nothing to worry about what the government might do with this information, including future governments, this information has to sit somewhere. Data sitting around for 10 years has 10 years time of being stolen or copied. Perhaps some activists obtain this log and publish a list of names of people who visited a particular website.

There is current laws for lawful interception. This is where the police or another security agency goes to the court and says a particular person has done certain bad things and asks if they can intercept their internet traffic. It's the same rules if they want to tap your phone. Except for "fishing trips" where police just randomly look at information from anyone hoping to trip up on something, what is this system going to be used for?

What can you do?
If you're not happy about either, or both, of these new proposals, it is time to do something about it. Visit the website Open Internet Website for what you can do. One of the things is to
tell you mum about internet censorship which has a funny message from comedian Akmahl Saleh that also has an important side.

Most of important of all, don't let these proposals become law because of apathy!

<script defer="defer" src="http://static.zemanta.com/readside/loader.js" type="text/javascript"></script>

Stefano Zacchiroli: debian squeeze artwork contest

we want you for Squeeze artwork You might have heard that Debian is closing up on the forthcoming Squeeze release. In its aim to be "universal", Debian addresses several different kinds of users and Squeeze will be no exception. For several users, and in particular for desktop users, artworks do matter and initiatives like the one started by Valessio Brito are likely to improve their user experience. In essence, the initiative is a Debian Squeeze artwork "contest" where Debian enthusiasts skilled in graphics can contribute themes and propose them to become the official/default theme for Debian Squeeze. So, are you a Debian enthusiast that would like to help Debian by putting into use your graphic skills?
This is a big chance to do that! Before going forward, please check the rather precise requirements that Valessio prepared and check some of the already submitted proposals. Good luck!

Andrew Pollock: [tech] The ondemand CPU frequency governor should be better in Linux 2.6.35

I'm still wading through my backlog of LWN articles, but I found this one to be of interest. From my interpretation of the article, I/O intensive workloads currently cause the ondemand governor to drop the CPU frequency, whereas it ideally shouldn't. It looks like the fixes have been merged into what will become 2.6.35

14 June 2010

Erich Schubert: Facebook clickjacking (aka: Facebook worms)

It doesn't look like Facebook gets its clickjacking issues under control. The various so called "Facebook worms" keep on reappearing every couple of days on new pages. Users don't get the concept of a "hidden like button" causing these issues, and Facebook obviously doesn't want to shut down the "like" functionality, since it will make them the ultimate heavyweight on the advertising market: which other company can give you such detailed demographics as Facebook can for your web sites?So far there seem to be two protections available: Maybe the Antivirus companies should step up here, too - and on one hand, block the Like function to stop this worm from spreading, and on the other hand, prevent Facebook from spying on their users.It's already making the news that Facebook doesn't get these issues under control.

Russell Coker: Should Passwords Expire?

It s widely regarded that passwords should be changed regularly. The Australian government declared last week the National Cyber Security Awareness Week [1] and has published a list of tips for online security which includes Get a stronger password and change it at least twice a year . Can a Password be Semi-Public? Generally I think of a password as being either secret or broken. If a password is known to someone other than the sysadmin and the user who is authorised to use the account in question then you have potentially already lost all your secret data. If a password is disclosed to an unauthorised person on one occasion then merely changing the password is not going to do any good unless the root cause is addressed, otherwise another anothorised person will probably get the password at some future time. Hitachi has published a good document covering many issues related to password management [2]. I think it does a reasonable job of making sysadmins aware of some of the issues but there are some things I disagree with. I think it should be used as a list of issues to consider rather than a list of answers. The Hitachi document lists a number of ways that passwords may be compromised and suggests changing them every 60 to 90 days to limit the use of stolen passwords. This seems to imply that a password is something that s value slowly degrades over time as it s increasingly exposed. I think that the right thing to do is to change a password if you suspect that it has been compromised. There s not much benefit in having a password if it s going to be known by unauthorised people for 89 days before being changed! Fundamentally a password is something that can have it s value rapidly drop to zero without warning. It doesn t wear out. Why are terms such as Three Months used for Maximum Password Ages? The Hitachi document gives some calculations on the probability of a brute-force attack succeeding against a random password with 90 days of attacking at a rate of 100 attempts per second [2]. I think that if a service is run by someone who wouldn t notice the load of 100 attempts per second then you have bigger security problems than the possibility of passwords being subject to brute-force attacks. Also it s not uncommon to have policies to lock accounts after as few as three failed login attempts. Rumor has it that in the early days of computing when the hashed password data was world readable someone calculated that more than 3 months of CPU time on a big computer would be needed to obtain a password by brute-force. But since then the power of individual CPUs has increased dramatically, computers have become cheap enough that anyone can easily gain legal access to dozens of systems and illegal access to a million systems, and it has become a design feature in every OS that hashed passwords are not readable by general users. So the limiting factor is to what degree the server restricts the frequency of password guesses. I don t think that specifying the minimum password length and maximum password age based on the fraction of the key space that could be subject to a brute-force attack makes sense. I don t think that any attempt to make an industry-wide standard for the frequency of password changes (as the government is trying to do) makes sense. Can there be a Delay between a Password being Compromised and being Used by an Attacker? Hypothetically speaking, if a password was likely to be compromised (EG by having the paper it was written on lost or stored insecurely) for some time before an attacker exploited it, then if the password was changed during that time period it could solve the problem. For example when a company moves office there is the possibility of notepaper with passwords to be lost. So if the sysadmin caused every user password to expire at the time of the move then a hostile party would be unable to gain access. Another possibility is the theft of backup tapes that contain the list of unencrypted passwords. If users change their passwords every three months then the theft of some four month old backup tapes will be less of a problem. Another possibility concerns the resale of old computers, phones, and other devices that may contain passwords. A reasonably intelligent user won t sell their old hardware as soon as the replacement device arrives, they will want to use the new device for some time to ensure that it works correctly. If passwords expire during this trial period with the new device then passwords stored in the old device won t have any value. The down-side to this idea is that people probably sell their old gear fairly quickly and making passwords expire every two weeks would not be accepted well by the users. It seems to me that having bulk password changes (all passwords for one user or for one company) based on circumstances that lead to potential insecurity would do more good than changing passwords at a fixed schedule. How are Passwords typically Compromised? Dinei Flor ncio and Cormac Herley of Microsoft Research and Baris Coskun of Brooklyn Polytechnic University wrote a paper titled Do Strong Web Passwords Accomplish Anything? [3] which discusses this issue. The first thing that they note is that nowadays passwords are most commonly compromised by phishing and keylogging. In those cases passwords are typically used shortly after they are stolen and the strength of a password never does any good. That paper suggests that banks should use stronger user-names rather than stronger passwords to combat the threat of bulk brute-force attacks. Can a Password Last Forever? If a password is entered in a secure manner, authenticated by a secure server, and all network links are encrypted or physically protected then there should never be a need to change it. Of course nothing is perfectly secure, so for some things with minimal short-term value or which can be used without anyone noticing there is a benefit in changing the password. But in the case of Internet banking if a hostile party gets your login details then you will probably know about it in a few days when the bank calls you about the unusual transactions from foreign countries long before a 90 day password change schedule would have done any good. Maybe one of the issues determining whether a password should be changed regularly is whether an attacker could use long-term read-only access to gain some benefit. Being able to read all the email someone received for a year could be a significant benefit if that person was a public figure, and there s usually no way for an ISP customer to know that someone else is downloading all their mail via POP or IMAP. Should a Password be the only Authentication Method? It is generally agreed that an authenitcation method should ideally involve something you have plus something you know. That means a password and a physical device such as a smart card, token with a changing sequential password, or a key such as a Yubikey [4]. If the physical device can t be cloned (through some combination of technical difficulty and physical access control) then it significantly improves security. When a physical device is used the purpose of the password is merely to stop someone who steals the physical device from being immediately exploit everything the password only has to be strong enough to keep the accounts secure until a new token can be issued. The combination of something you have and something you know is very strong. Having a physical token stored on the desk next to the PC that is used for logging in provides a significant benefit, then an attacker needs to break in to the house and can t sniff the password by compromising the PC remotely. Conclusion In all aspects of security you need to consider what threats you face. If an attacker is likely to launch an immediate noisy attack (such as transferring the maximum funds out of an Internet banking account) then changing the password regularly won t do any good. If a subtle long-term attack is expected then changing the password can do a lot of good but a physical token is the ideal if the account is valuable enough. But to put things in to perspective, it s technically possible to use a mobile phone camera at close range (or a SLR with a big lens at long range) to take a photo of keys that allow reproducing them. But this hasn t stopped people from carrying their house keys in an obvious manner that permits photography or leaving them on their desk at work. Also I ve never heard of anyone routinely changing the door locks in case a hostile party might have got a key although I m sure that such practices are common in highly secure locations. Few people even take their house keys off the key-ring when they have their car serviced! Related Posts Defense in Depth and Sudo when using sudo can increase security and when it can t.
Logging Shell Commands how to log what the sysadmin does and what benefits that provides you, it doesn t help if the sysadmin is hostile.
Logging in as Root should you login directly as root?

Gunnar Wolf: What Mexico feels like

I have been recently approached by several friends, from different countries. Mexico and the violence seems to be a frequent news topic all over the world. I live in Mexico City, as ~25% of the country's population does. This is not an easy city, of course, and I won't deny it has tons of problems of its own. However, Mexico City (and even more so the approximately of it that is politically located in Distrito Federal, the formal country capital) is very lucky in this regard. Still, in most of the country, the violence is mostly in the news, mostly a worrying perception that is every day more insistent. My parents live in Cuernavaca, Morelos, ~80Km south from us. Morelos has been known for decades for being the druglords' getaway and safe haven, so it remained a mostly peaceful state for most of this time. This has changed, and at some points during this year, militarization feels quite creepy... Fortunately, just for a couple of weeks, and then back to what seems like normal. The real problems in Morelos is the undeniable corruption of its successive governments, the lack of regard for the population, the inexistent urban planning... However, I know from several friends living in the North of the country (and all along the very long border - The most drug-related violent states nowadays are Chihuahua, Durango, Sinaloa, Tamaulipas and Nuevo Le n, with only two states in the South Michoac n and Guerrero) that violence is really felt by local population on the streets. Some friends say they have grown used to hearing shootings (Durango), others say that it is now usual that the cartels openly strangle the city's vial system with the express purpose of showing off their strength (Monterrey, Nuevo Le n, one of Mexico's most important cities and taken in the past as a token of industrialization and first-world-like life conditions... Just don't look towards the poor areas). About Chihuahua, I'd rather not even talk, as by all accounts (official even) it rivals Iraq in the lack of control the government has of its territory. Still, with all that as background... I am afraid of what I read today in the news. I know a single declaration is not enough to worry about (as said in El Quijote, una golondrina sola no hace verano , a single swallow does not mean it's summer), but those things always start small... Until they explode. La Jornada reports that The retired general Luis Garfias Maga a recommends suspending constitutional guarantees in the country to be able to properly fight violence. The last century we had a sad and long history of cases where the military took over civilian power and suspended the constitutional rights in basically every nation in Latin America Except for Mexico. Not one of those cases was overall successful. Not one of them went by without raging abuses, without terrible consequences. I don't see imminent we will go over to a military rule nor anything close to it, but the environment is getting each time closer to how it was like before said rights suspension. We should learn that it is just not the way, it leads nowhere. I am convinced, and will keep insisting on it at every ocassion, that the only possible way to fight violence is by reducing the social distance, and that should be achieved most importantly by reducing poverty, but also by making it harder to become incredibly rich. Mexico's percentage of poor people has grown over the last decades, but at the same time, the amount of wealth concentrated in very few hands has grown much faster. A society with terribly rich and terribly poor people leads to hatred, leads to desperation, leads to violence. A flatter society, even if the overall standard was to be somewhat lower, tends to a better equilibrium. And yes, I know the original problem with drugs is that Mexico is a great transit area for drugs to reach the USA (and I could also rant about drug legalization I won't, it's late and I must go to work), but the main fuel for young people to leave everything behind and take the risk of starting a life of open ilegality is the lack of future they face all life long. That leads many to risk their lives attempting to cross the border to the USA (Mexico "exports" 500,000 people every year), but also lures them to jobs where they will have easy money... In exchange for their lifes, ultimately. Anyway... Just to repeat and round off: The answer to this problem is not repression, is not policial or military strength. Our only way out is through social justice.

Biella Coleman: Baby Panda wants YOU to submit to DEBCONF


bad mood destroyer, originally uploaded by the biella.
People s the deadline is fast approaching. Don t worry though, the best ideas come under deadlines and your proposal need not be lengthy. So get those typing hands out and submit a proposal (a few sentences suffices) for a presentation!
The annual Debian conference is being held in NYC this year. First time
setting foot in the imperial empire. Are you doing something related to
free software that might be interesting to share, show off or talk about
at Debconf? I bet you are! We are looking for art installations,
performances, movie screenings, maybe you are wanting to host a
roundtable/panel discussion, coordinate a workshop (you dont have to
know the subject deeply to do this!). I know the deadline is soon, but don t let that scare you. The
submission requirement bar is very low, and we are flexible! here is the submission information: [1] ********************* Calling all potential contributors to DebConf10! One more week until
the final submission deadline! The DebConf team is excited to announce that we are now accepting
proposals for contributions to this year s Debian conference! We
invite you to submit proposals for how you would contribute until the
deadline: soon There are many ways you can contribute, you could present a technical
paper, host a panel discussion, put on a tutorial, do a performance,
an art installation, a debate, host a meeting (BoFS, or Birds of a
Feather Session), or other possibilities that you devise. This year we
are also accepting proposals for tracks=E2=80=94a thematic grouping around a
particular subject, and people to coordinate those tracks. If you are
looking for ideas of things that you could contribute, or have ideas
for things that you would like to see happen at DebConf, have a look
at the Contribution Brainstorm[0] page. DebConf talks will be broadcast live on the Internet where possible,
unless otherwise requested. Videos of the talks will be published on
the web along with the presentation slides and papers. =3D=3D Step 1. Submit Proposal =3D=3D Proposals should provide an overview of your proposed contribution,
similar to an abstract, and be no more than 600 words. Since
contributions can cover a range of issues, please describe what your
proposal covers, be it political (Free Software, law, advocacy,
access, etc.), technical (d-i, OpenPGP, etc.), social (Debian
structures and groups). It s okay to hit all three of these. Your
proposal should also include some information on why you re qualified
to present, or coordinate this topic. For example, you can include
links to posts you have made to Debian mailing lists or other material
that indicates your qualifications. Proposals and their abstracts will
be accepted until May 1st, 2010, 23h59 UTC. To submit your proposal, go to Penta[1] and register as an
attendee. Once you are registered, there is a Submit a proposal
link. You will see your proposal on the site. You can choose between
different presentation types. If you are unsure what type you should
use, please read our glossary of definitions[2]. If it s not there for
some reason, or you have questions, please contact us immediately at
mailto:talks@debconf.org. =3D=3D Step 2. Committee Review =3D=3D The review committee for this year will make its decision by May 1st,
2010. All correspondence will be done by email. =3D=3D Step 3. Paper Submission =3D=3D Like last year, we are asking for papers to be submitted along with
the presentations. A full paper is optional, however we strongly
encourage you to submit one if possible as we intend to provide
written information along with transcripts of the sessions for later
viewing. Having written papers in advance will allow us to get
translations done to help non-native-English speakers feel more
comfortable with the topics presented. Papers are due by July 1st,
2010, and should cover the topic in reasonable depth (3 pages A4 text,
plus pictures and diagrams). We will use LaTeX to typeset the
proceedings. Please submit your paper formatted in LaTeX. Should you
be unfamiliar with LaTeX earlier submission in plain text is also
fine. =3D=3D Step 4. Live Presentation =3D=3D Longer presentations may have a break in the middle and should include
workshop items that directly involve the participants. If using slides
or any other presentation, please consider that your audience will
consist of people who use free software, and your choice of
application to prepare and display the slides should reflect this if
at all possible. =3D=3D Fine Print Publication Rights =3D=3D DebConf requires non-exclusive publication rights to papers,
presentations, and any additional handouts or audio/visual materials
used in conjunction with the presentation. The authors have the
freedom to pick a DFSG-free license for the papers themselves and
retain all copyrights. The presentations will be recorded, and may be
broadcast over the Internet. Any copies of the presentation will be
made available =3D=3D Failure to Submit =3D=3D In the event that a deadline is missed we reserve the right to revoke
any offer to present. =3D=3D About DebConf =3D=3D The annual DebConf conference is a technical and social forum for
Debian developers, sponsors, affiliates, and friends. It allows
various groups within Debian a chance to come together, network, and
share their work. Until we see you in the big city,
DebConf Talks Team [1] introduction written by Micah Anderson

Gunnar Wolf: Planned obsolescence and propietary gear - Dear lazyweb, a sports tracking app for a N95 phone?

Grah. I got my current phone (a Nokia N95) back in January 2008. It was the first phone I ever paid for, and I don't expect that to change - The feature set I need from a phone is extremely basic, but I wanted to have a GPS unit on me, without needing to plan for it beforehand. As I recently blogged, I just got over the 5000Km mark (5269 as of last Friday), with almost daily usage since I registered. A couple of days ago (although please note I don't log in often to the web page, I just upload my , I was greeted by this gem:
IMPORTANT NEWS Thank you Nokia Sports Tracker beta users! After two and a half years of operation, the Nokia Sports Tracker beta service will close as of June 30, 2010. Thanks to all of you exercise enthusiasts who used the service and contributed valuable feedback to its improvement. We want you to stay active. You can keep tracking workouts through a new, non-Nokia service provided by Sports Tracking Technologies available for free in the Ovi Store. The new service is open for registrations at sports-tracker.com, and you'll even be able import your workout history from Nokia Sports Tracker until August 31, 2010.
In my case, instead of Thank you they could have just said Fuck off. They are directing me to a new application available in Nokia's Ovi store. Of course, this application is linked to a new 100% Flash-powered website. That would be a big turnoff for me, yes, although there are many ways around it (after all, I don't need the website functionality every day). However, I find the list of supported phones does not include the N95 (any version). This means, my two year old phone (which I bought as soon as the model arrived in Mexico) is obsolete now and they want me to (spend more money and) switch to a new one. Am I going to do that? Hell no! The N95 phone is quite good. The only gripes I have is with the (slow, buggy and memory leak and phone crash prone) Symbian S60 operating system. I will probably keep using the SportsTracker application, although I won't be able to link my tracks as easily as I do today. So... Dear lazyweb, do you know of any similar program? The feature set I use in Sports Tracker is:
  1. Have different activity profiles. I use Running and Cycling, and very ocassionaly Walking.
  2. Of course, GPS tracking, getting average and top speeds, altitude profile, etc.
  3. Aggregation into something website-friendly
  4. The ability to do my uploads post-factum (i.e. do not rely on a data plan, allow me to upload my excercising when I get home)
There are probably more things I'd want. But I am a geek, and I basically enjoy tracking myself, and sharing my tracks with $world. Thanks, dear lazyweb. I am confident you won't let me down.

John Goerzen: Camping with 2 Boys

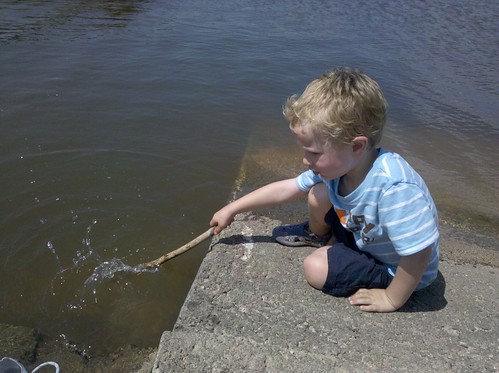
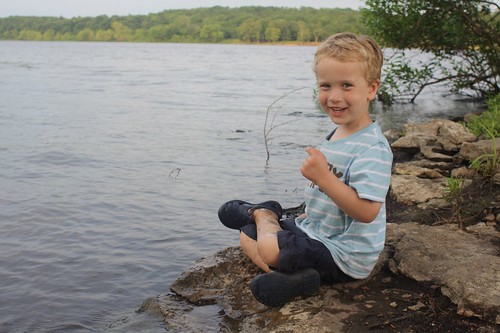
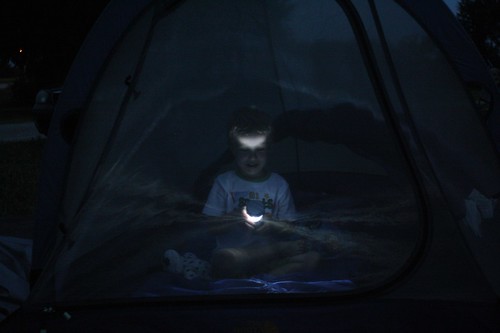
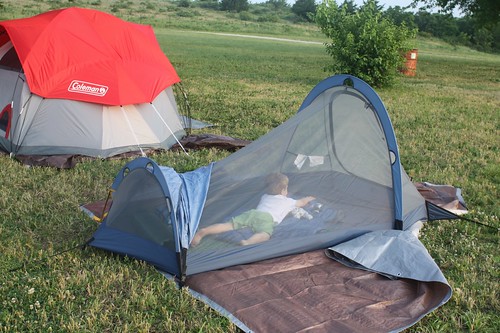
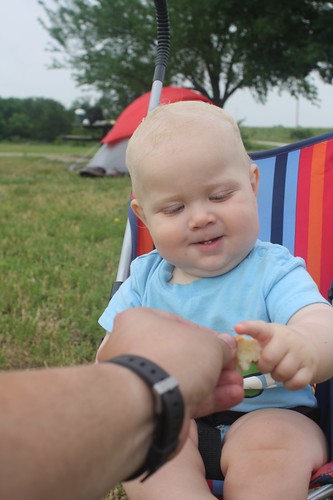
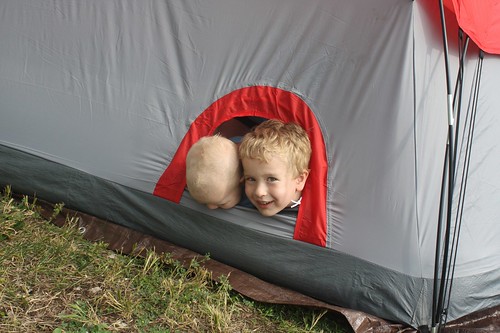
Friday I took the day off for us to go camping. Due to the birth of Oliver, our last time camping was in 2008. Back then, Terah had asked me what I wanted for father s day, and I suggested camping. Except when she was pregnant last year (and then Oliver was little), we have sort of had a standing plan to go camping twice a year: around father s day and my birthday. She says that s way more camping in a year than anyone needs. Anyhow, Jacob doesn t remember the last time we went camping; he was not quite 2 at the time. I explained that we would sleep in tents, and he d get one just his size. He laughed at that. Then I explained that he would get a bag to sleep in, and he thought that was hilarious. He kept talking about tents and even more so about sleeping bags until he actually got to be in one. It seems like each time we go camping, we wind up somewhere else. We ve camped at Kanoplis Lake and Marion Park and Lake in the past few years. But this time we went to Cedar Valley Reservoir near Garnett, KS. It was a nice place to be, with some wilderness camping areas far from any RV hookups (though right next to a gravel driveway where we could park). Almost as soon as we got out of the car, Jacob found a partially-burned stick left in a fire ring. So of course his hands were black pretty quick. He kept track of that stick the whole time we were there, and used it for everything he could think of. His favorite use, though, was at the lake to splash water: 2010-06-11 15.20.21.jpg The lake really was his favorite feature. He loved to throw rocks and sticks in it with me, to splash himself, and to stick his feet in. Oh, and to splash me. IMG_4057.JPG The pier was also a great thing for him he at first thought it was a boat, then really wanted to go. I made him hold my hand the whole time, and he liked walking on it. But he was frustrated that he couldn t reach the water. Somehow, Jacob acted as if he could sit in the hot sun for hours, just making small splashes with a stick. I, on the other hand, felt the 90-degree heat strongly, and eventually we found a shady spot to play in the lake. Oliver enjoyed crawling around on a blanket or on the grass. Though Terah put a stop to that after she noticed that he came across a pile of fish heads and was about to reach for one and put it in his mouth. We cooked over a campfire Friday night and Saturday morning. It took me a lot longer to start a fire than normal. Part of the problem was that there had been a lot of rain in the area, and it was humid, so there was little kindling to be found. Plenty of larger pieces of wood, so once the fire got going, it burned nicely. We cooked brats, brought along some homemade bread, had grilled foil-wrapped potatoes, and had stir-fry vegetables. Oliver got to eat with us too, of course: IMG_4022.JPG Terah is a big believer in smores, so after supper we made some smores Jacob predictably got sticky from the marshmallows and chocolate. Jacob started asking when I d set up the tent almost as soon as he found his stick. All afternoon he kept asking. Finally we got it set up, and of course he was so excited that he played inside it for an hour before he fell asleep. Terah had bought a $4 lantern at Walmart to give to him to use in his tent. I told him that there would be a surprise lantern in his tent for him to use. And he loved his lantern. It could turn on, off, and flash red. At one point he asked me, Dad, do you have a surprise lantern too? No, I will just use my flashlight. He looked a bit sad about that. For about 5 seconds. Then he turned on his lantern again. Here he is with it, still playing happily about 2 hours after his bedtime: IMG_4100.JPG And in the morning, of course he was still wanting that, but also wanted to play with his digital camera (a kid s version that also has a simple game or two on it). Without leaving the tent, of course. IMG_4105.JPG Oliver was getting hungry while we worked on breakfast, so I gave him some bread to munch on. IMG_4119.JPG We used our cast iron skillet to fry some bacon for breakfast. Then Terah made some pancakes in the skillet (with the bacon grease). Greasiest and best pancakes ever. After that, we had some fried and scrambled eggs. After that, we had more smores (I wasn t kidding about Terah being a big believer in them.) Jacob decided that he wanted to play in the other tent. He enjoyed playing with Terah, Oliver, and the air mattress (that Terah appreciated as much as I thought it took up too much space in the car). There s a little window on the back that can open to a screen or open completely. Jacob and Oliver enjoyed looking out of it while open. Or rather, Jacob enjoyed that, while Oliver enjoyed licking it. IMG_4161.JPG I had my Droid with me to keep an eye on the weather. The forecast for several days had called for a 20% chance of storms on Saturday. I checked Saturday morning at 7, and it still called for 20% chance of storms after 1PM. We decided we d pack up our tents after breakfast so we could stay as long as we liked or leave on short notice if we preferred. Clouds seemed to be building, though, so I checked the forecast again at maybe 9. Now it called for 60% chance of thunderstorms and heavy rain before 1PM. Guess I shouldn t have been surprised; it is Kansas after all. As I had the first tent about 90% put away, it started to rain. We rushed to get the rest of the stuff in the car, and by the time we did, it was raining heavily. We had planned to spend at least part of the afternoon there, but decided we d look for another place to stop on the way home. We stopped first at Garnett s North Lake, as the rain had let up for awhile. We spotted a fishing pier that Jacob wanted to walk on, but the bridge out to it was underwater, so we passed on that. While Terah fed Oliver in a shelter, Jacob and I played on some swings. Then we walked down to that lake. Jacob carefully came to an abrupt stop and looked both ways at each disused road between us and the lake, saying OK when it was clear to go. The rain picked up again, so we started heading towards home. It got quite heavy, with thunder and everything, which Jacob didn t care for at all. Both boys went to sleep, though. We stopped at Marion Reservoir on the way home. Jacob hadn t been able to play in the lake at Garnett (the place we stopped had a bank that was too steep) and so we played there. He waded into the water at the swimming area, and predictably enjoyed yes throwing rocks into the lake. When we got home, I set out the wet tent and tarps (it s not good to store that stuff wet) to dry there hadn t been rain at home yet. Camping s a lot of work, but it was a good family activity. I m looking forward to our next time, and hope we can choose a weekend a little less hot and damp.

Christine Spang: Christine Spang: the end of an era

The world around me seems to whirl these days. One week ago, I graduated from MIT. People I've known during the last four years have been dispelling to various parts of the globe one by one, day by day. California, Canada, Indonesia, Seattle. Some will be back again. Some will not, or if so only to visit. pika is a continuous bustle of activity as the summer has commenced and it has filled with creative and adventurous MIT students who've suddenly found themselves having free time. A hammock being built on the roofdeck. Thrice-weekly icecream forays. Common areas overflowing with people playing musical instruments, chatting, and messing around on laptops. Summer's warmth has arrived, bringing with it farmer's markets, strawberry picking, and swimming expeditions. While it's wonderful to get to meet so many new people living in a college environment, I can't help but feel sadness thinking about everyone who's left. There are always more friends to be made as new people arrive, but old ones moving away leave bittersweet memories, and the new relationships are always a bit different as the age discrepancy between me and others changes. Or the me-the-ephemeral-collection-of-thoughts-which-when-regarding-other-people-sometimes-involve-the-mentor/mentee-distinctions-caused-by-one-party-being-older-or-more-knowledgeable-than-the-other-at-least-in-certain-areas changes. The end of a semester always feels like this, but this year even more so as the people I started university with start down new paths. For me, that was going to involve staying on at MIT to complete a one-year master's program, the "M.Eng." in electrical engineering and computer science. That plan, too, has changed. I've deferred the degree and accepted a full-time engineering position at Ksplice, an exciting early-stage Linux startup here in Cambridge. I'd been working at Ksplice part-time since January before joining full-time immediately following graduation. Ksplice is the realization of ideas I saw being born on the whiteboard at SIPB when I was a freshman, and it's fun to see that play out in a small, ever-changing, low-bullshit company. All in all, there are many more exciting things down the road, and, working at an MIT startup, I haven't even escaped the MIT/Cambridge reality-distortion bubble yet. Still, it's tempting to resist change and let myself romanticize the good old days, hoping to catch every person I've ever enjoyed spending time with and hold them down here forever. That's not the way life works, though. Change happens.

Next.

Previous.