Search Results: "cas"

10 August 2006

Filip Van Raemdonck: No free ride

The picture below is a hardware test setup I ran this morning, with an old and discarded motherboard which has a Pentium III CPU on it running at 733 MHz. Since that's still faster than any other system I own save for the ibook (which is a G3 running at 800 MHz), I wanted to see if it was truely broken as reported, or not. The issue, which I actually witnessed before, was that on initial boot it tended to restart up, to a few dozen times. These restarts could happen from early post BIOS stage up to while logging on. Once it had been powered on for a little while, the restarts would usually go away.

Disassemble PC

I assembled any missing parts - video card, memory, and an AT case from which I used the reset button as the power switch to the ATX motherboard - and started by running memtest on it. Which ran just fine for nearly half an hour; but I ran memtest before to try and help diagnose the problem and it had run fine then, too.
So I crossed my fingers and tried running a Linux Live CD from it. Unfortunately, after about half a minute the system restarted once again. The only parts remaining from the original system were the motherboard and CPU, power supply and DVD-ROM (but not the IDE cable). With that in mind, the most likely culprits are indeed motherboard or CPU.

Chances of being able to rescue the parts are nearly nil, but I'm still curious about what could be the actual failing part. Are there any thorough hardware tests around, which could be run (preferably) from bootable CD or floppy?

Andrew Pollock: [tech] Performance comparison between LVM and a straight disk

The beauty of having your hardware arrive in installments is you can do all sorts of fooling around with lots of storage that you wouldn't otherwise do because you'd be falling over yourself to get it all up and running yesterday. So as I impatiently wait for my TV tuner card to arrive, I've been doing some "benchmarking" to see how various different configurations perform. One of the things I wanted to find out was how much overhead did LVM give you. So I took one of the four disks in my non-redundant array of Bloody Huge Storage, and ran bonnie++ on it as a straight JFS volume on /dev/sda and as a logical volume in a volume group that used all of the logical extents provided by making /dev/sda into a physical volume. Again, I ran bonnie++ as:
bonnie++ -d /mnt -s 2G -n 1024 -u nobody:nogroup
So here's the results of running it on a JFS filesystem straight on /dev/sda:
                    -Per Chr- --Block-- -Rewrite- -Per Chr- --Block-- --Seeks--
Machine        Size K/sec %CP K/sec %CP K/sec %CP K/sec %CP K/sec %CP  /sec %CP
minotaur         2G 13712  95 18561  21  9152  11 13874  94 20446  18 142.2   1
                    ------Sequential Create------ --------Random Create--------
                    -Create-- --Read--- -Delete-- -Create-- --Read--- -Delete--
              files  /sec %CP  /sec %CP  /sec %CP  /sec %CP  /sec %CP  /sec %CP
               1024  5999  37  7125  19  1604  12   616  12   168   0    61   1
And here's the results of running it on a JFS filesystem on a logical volume that used all of the free logical extents provided by a volume group consisting of a physical volume made from /dev/sda
Version  1.03       ------Sequential Output------ --Sequential Input- --Random-
                    -Per Chr- --Block-- -Rewrite- -Per Chr- --Block-- --Seeks--
Machine        Size K/sec %CP K/sec %CP K/sec %CP K/sec %CP K/sec %CP  /sec %CP
minotaur         2G 13790  96 18566  21  9132  11 14202  96 20628  18 146.3   1
                    ------Sequential Create------ --------Random Create--------
                    -Create-- --Read--- -Delete-- -Create-- --Read--- -Delete--
              files  /sec %CP  /sec %CP  /sec %CP  /sec %CP  /sec %CP  /sec %CP
               1024  5989  37  7056  20  1605  12   611  12   167   0    61   1
Yup, that's right. It was actually slightly faster in a few cases. I can't explain that one. But it certainly goes to show that there is no noticeable performance impact of using LVM. Nice.

9 August 2006

Josselin Mouette: Rediscover python packaging

After seeing several developer comments implying that they won't package python software because this has become too complicated, I was hit by the fact python-support had drifted away from its original goal: make the developer's life easier. The initial idea was to simplify dh_python and make it use something that could automatically handle byte-compilation, without the maintainer even noticing it.

Therefore, with the help of Manoj Srivastava's priceless work to clarify the policy and of Pierre Habouzit's background work on supervising the transition, I have improved dh_pysupport to be able to generate correct dependencies. I have also finally added the last missing piece of functionality: private modules needing a specific python version.

This is a necessary step for Joey Hess' plan to remove dh_python from debhelper. But the more important thing is, for most packages, dh_pysupport can now be a drop-in replacement for the old dh_python. This means that many remaining packages for the transition can be updated with s/dh_python/dh_pysupport/ and a new build-depend.

And, for anyone who's afraid of maintaining a python package because it is too complicated, let me show how to make a simple package using python:

Yes, that's all. You mean, just like with the old dh_python, the one that used to work without having to understand anything? Yes, just like this one. Don't add a XS-Python-Version field, it's not needed. Don't add a XB-Python-Version field, it's useless. Don't add a debian/pycompat file, it's deprecated. You can add a debian/pyversions file if the package has requirements on the python version, but it's not needed for many packages.

Of course, packages with binary extensions should build them for all available python versions, but dh_pysupport handles both cases. Of course, I don't claim it's free from bugs, but bugs can be fixed now there is a good design.

So finally, I can say it again: python packaging is simple. You shouldn't be afraid of it.

Rob Bradford: Bug buddy integration for GNOME Python apps

Just in case you missed it before…Fernando Herrera and Lorenzo Gil came up with a lovely bit of code that allows the parts of the GNOME experience written in Python to send traces via bug-buddy when something goes wrong. Pessulus will soon have this and i’m working on doing it for Deskbar. Update: Forgot the link to the code…bug-buddy-integration.py.

Carlos Villegas: Comparing preload 0.4 and 0.2 (SoC 2006)

I've tried preload 0.2 and 0.4 to compare its effects. Unfortunately my results don't hold with the results obtained some blogs ago: preload 0.2 reduced the boot time by 2 seconds. In this occasion, time was even lost (making me remember my first tests). This may be due to some upgrades had been made to sid since.
First I tried preload 0.2 with default with 1 second lost and a modified configuration with no boot time change.
Then I tried preload 0.4 with default and modified configuration both with no time change.
The bootcharts and log file are availabe at the project webpage.
Yesterday I presented a table with hotspots combinates and unlike it was expected, preload may not be helping anymore (preload 0.4 was used).

8 August 2006

Ross Burton: Cornish Bliss (part 2)

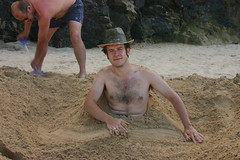
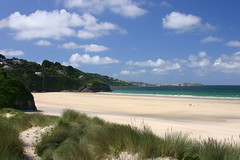
Now, where was I... Carbis Bay Carbis Bay Ah yes. After the horrendously grim weather had passed, the weather improved and we headed for the beach. On the way down we commented on how this was the classic British burning weather: bright sunshine, a strong breeze, and occassional clouds combine to burn skin without even feeling that hot. Of course knowing this meant nothing, we were too distracted with purchasing pasties and drink to think about putting a decent amount of sunblock on. Steve Relaxing Obviously the main thing to do at the beach, after we'd sat down, not applied sunblock, and scoffed a pasty, was to dig a hole. A huge hole. Spades were purchased and we took turns to help Pete dig The Hole. Digging Diggers Astute readers will notice the inevitable outcome of saying this is burning weather, not putting enough sunblock on, and digging a hole (an activity that results in the back being exposed to the sun). Ouch. After the hole had been dug we had to full it in again to avoid trapping small childen in it. Obviously this led to a series of hilarious scenes involving burying Pete up to his chest, modelling breasts and a penis, and so on. Finally the hole was flat again, at which point an impromptu long jump sand pit was arranged. I came first in the long jump, and although failing miserably at triple jump although I swear my technique was best (it's all in the wrists). Pete Next was to explore the costal path in the opposite direction towards Porthkidney beach. The beach is pretty huge by my standards, and due to the lack of facilities (no close car park, shops, toilets, and so on) it's almost deserted: there were a few other people there with dogs (the other local beaches are dog-free in summer) and that's about it. Googling to confirm the name of the beach reveals that there is a history of naturism and "inappropriate gay activity", but we didn't encounter any of that. ;) Progression Ross Footprints The costal path was great, far more rough than the walk to St Ives (often just a foot wide cutting in the ground), steep in places, and generally running very close to the cliff edge. The views were great, but I always think what a horror paths like these would be in winter, with the full force of the Atlantic winds pounding against the cliffs. As a finale it turns out that the costal path follows the cliff all the way along the back of the beach, which would easily be another twenty minutes of walking to reach sand. There is a shortcut down some stone stairs to the beach, but we arrived at high tide and the bottom of the stairs (well, rocks) were a foot deep in water. Wading up to the beach was a fitting end to the walk, and made the beach feel like our own little desert island! Cliff Steps Wading To Land Limpets! Ross I'll have to explain the expression on Vicky in the above photo. As a child when Vicky went to visit her father in Devon they used to go to the beach and spend the day annoying the wildlife: chasing crabs, kicking limpets off rocks and so on. When Vicky noticed that the rocks at the bottom of the cliff were covered in limpets, she shouted "limpets!" with a manic expression and preceeded to prod them frantically. After lots of sitting around and digging tunnels, we headed for the dunes for a spot of dune diving. This involves running at top spead down the dunes and throwing yourself into the sand at the bottom. Ah, the simple pleasures in life! Porthkidney Beach Dune Diving Dune Diving Dune Diving Dune Diving After my dive I ran back up the hill in the manner of a mad man, arms out-stretched to Vicky as I collapsed in front of her, gasping "It's". "What?", was the confused reply. This is terrible, I really need to get Vicky to watch the Best Of Monty Python DVD we have somewhere... It's! Possibly more to write, but Lost is on, so I'm off for now.

Lucas Nussbaum: Good questions to ask yourself when working inside teams

Many people agree that teams are good : doing team maintenance of packages is often seen as A Good Thing inside Debian, and Ubuntu enforces it by switching to the everything is team-maintained philosophy. However, teams are subject to complex group dynamics, and raise interesting issues that you don’t encounter when working alone. It is important to ask yourself those few questions Dilution of knowledge: Team members tend to individually know less about specific packages. Does the sum of all team members really know more than an individual developer would know about a specific package ? Responsibility: Are there some clear responsibilities in your team ? Are people feeling responsible for packages ? Not having clear responsibilities is dangerous, because a package could become sort-of-orphaned inside the team, because nobody would consider “his duty” to work on it. Hierarchy inside teams: Is there a clear hierarchy inside your team ? If there isn’t (which could be OK), are you sure there isn’t an unofficial hierarchy that built up with time, causing people to wait for an unofficial leader’s decision, while this leader might not even be aware that he is that leader ? Scalability: How much can a team scale ? How does *your* team scale ? How many team members are really active ? External interface: When dealing with the outside world (read: upstream), it’s easier to have a single point of communication. How does your team’s external interface look like ? Remember that teams’ external interfaces can easily become much more complex for upstream developers to deal with. There are no magic way to build a team that work, but it’s important to look at your team with a critical eye and try to improve its inner workings.

Joey Hess: moving kite

(This is a long ramble with a concluding announcement that kitenet.net users should read even if they skip the rest.)
Back in spring of '03 I bought a used VA Linux 2u on ebay for $300 and dropped it a cabinet in the blue spaceship halls of the Hurricane Electic co-lo in Fremont, CA. I've never seen it again; I use it every day. Weird world.
Digression: The reason I needed to have a hunk of silicon and spinning metal hooked up to a power and an ethernet cable somewhere is this: On the internet you can either be a soverign entity, controlling your own computation, choosing your own software, making your own mistakes, and doing things your way -- or you can be a sheep. Or at least that's what I believe; reasonable people think otherwise. Here's a story illistrating this concept. Not only do I want to be a sovereign entity on the internet, but I want to empower others to be the same, to the small extent that I can: making software that supports it easier to install; contributing to co-ops like the one that hosts my computer; working on software that empowers users to become programmers; fiddling with making special-purpose embedded hardware useful for general purpose use; and letting a few users run code and such on my server and use it much the same as I do. It's a theme through a lot of my activities.
Anyway, it seems like my computer has been there longer than three years, and it's had a good run, despite little incidents like: Mostly though it has kept on running without problems for years, being my personal server and performing a few other roles. This seems to prove something I've long suspected; that computer hardware runs much better when I'm not near it. But that can't last. Eventually a hard drive will die, eventually whatever fans have (probably) already died will overheat it. Eventually I'll screw up a kernel update (which still have to be done blind, since I never did get grub talking to that serial port.) One option was to go back out there and do enough maintenance for it to last another three years. The other option was to move away from running my server on that nasty computer hardware stuff. Happily, in the intervening three years, that has become, in a way, possible. Xen and the like are big news, letting a single standard server appear as multiple separate machines. Not a new idea, but an idea newly within easy reach. So when I heard that Steve Kemp was puttng together a Xen co-op to buy a machine and split it up 6 ways, into 6 virtual machines, I jumped at the opportunity. Not only does Steve know a lot more about administering Xen than I do, but he got a good deal for on hardware that should be fully managed in case of breakage. Plus, he's providing a template for doing this on a grassroots level that I hope many other people follow. (Only partly because I want to have more than one little virtual server other there, rather than one big physical one..)
I'm still a bit unsure about Xen from the point of view of wanting to fully control my machine, since it does a) let the admin of the underlying hardware get at any data they want to if it's not encrypted and, b) it doesn't make it easy to run your own kernel. Luckily I a) basically trust Steve, and b) he seems to want me to run the exact same kernel (latest Debian unstable stock kernel) that I want to run.
So, the conclusion to this ramble is that kitenet.net will be moving, over the next few weeks, to wren.kitenet.net, which is theoretically located in London, but which is not a "real" computer as you might be accustomed to thinking of them. I decided against moving it all at once, and will be trying to keep all the various services working while shifting them around. The utterly gory details of the transitions are being kept on kite's page in my wiki, and announcements for kite users will be posted to kite's blog.

6 August 2006

Josselin Mouette: How to introduce bugs in other packages

As the hdf5 maintainer, I already knew upstream developers are able to imagine really innovative ways of writing broken autoconf scripts, but this one made my day.

After my first package build on my fresh amd64 system, I noticed lintian complained about a rpath:
W: gconf2: binary-or-shlib-defines-rpath ./usr/bin/gconftool-2 /usr/lib64

I found soon that this was caused by /usr/lib64 being mentioned in the libpopt.la file. The popt build system is, well, interesting. Or funny, if it doesn't affect you.

In configure.ac:
dnl XXX Choose /usr/lib or /usr/lib64 for library installs.
MARK64=
case "$ target_cpu " in
x86_64* powerpc64* ppc64* sparc64* s390x*)        MARK64=64 ;;
esac
AC_SUBST(MARK64)

And in Makefile.am:
usrlibdir = $(libdir)@MARK64@

This is subtly breaking a large number of packages on amd64, as libtool, not knowing it is a symbolic link to /usr/lib, introduces a rpath for this directory it doesn't know about. This was already reported as #374797.

Daniel Jacobowitz: Look Ma, I can blog too!

I've been meaning to set up a blog to keep track of random things that I run into and feel like sharing. One of those happened today, so I finally figured out how to install blosxom. I haven't gotten around to making a pretty CSS for it yet (not sure if I ever will, but I can pretend...) so for now it's somewhat utilitarian and default-looking. Blosxom is pretty bare-bones without plugins, and while Blosxom itself seems well documented the plugins are much less so. I spent about ten hours mucking around with the minimal set of plugins I needed to get something acceptable (timezone, autoblock, feedback, entriescache, interpolate_conditional, permalink, cooluri2, lastmodified, and a bunch of modified templates to use feedback and permalink). I tried and then discarded followsymlinks and metadate (for not playing well with other plugins I was using) and entries_index (lastmodified wanted something which set %others, so I used entriescache instead). I needed to hack lastmodified to work with entriescache, since it cleverly gets the timestamps from the cache, which are now publication dates. So here's a slightly modified lastmodified plugin which stats files directly. I spent a while getting RSS to behave, too. I used lastmodified to set lastBuildDate, modified the story template to use permalinks which were acceptable to feedback (it wants .rss on the end or it decides they aren't story pages), and eventually figured out that I needed to set <guid> to prevent liferea from thinking each modified post was new by comparing descriptions. All in all it was far more work than I meant to do last night when I decided this was a good idea. Hopefully I haven't messed it up too badly. We'll see whether I upset Planet. Leave me a note if it makes your feed reader unhappy, or something. I was actually going to use ikiwiki, but chickened out at the last moment; blosxom had fewer dependencies and I didn't want to mess around with getting ikiwiki to install on sarge. And it still seems to be evolving - so while it's wicked cool, I think I'll let it have a little more time to settle first. I spent most of this morning messing around with OpenWRT. I bought a LinkSys WRT54G quite a while ago (to replace a flaky D-Link DI-614+), and put OpenWRT on it. It took a little work to get it to do what I wanted, including fixing a quoting bug in the WPA startup script and tracking down an updated dnsmasq, but eventually I got it set up. Mostly the stock things: NAT, firewalling, wireless with WPA2, DHCP, internal DNS. Except that it can do one thing that none of the stock firmwares could: provide static DHCP addresses to specific boards, including custom options. This was absolutely essential for me to retire my old DHCP server, since I keep an embedded board lab in my office. I need the DHCP server to be able to tell boards where to get kernels and root filesystems. Anyway, it works well. Except that I've been having too many dropped connections lately and I have no way to track down whether it's the laptop (Dell Latitude D400, ipw2200 - mostly in Windows lately, I haven't retested it in Ubuntu in a bit) or the AP. I updated the Windows drivers and now it periodically tries to rekey, fails, reports "duplicated RSN" whatever that means, and periodically reports authentication failures. About the same as before except that now it has better diagnostic tools to tell me in undocumented messages what went wrong, instead of just telling me that something went wrong. So I next went looking for an updated driver for the other end. Which was a mistake. Note to others: if most of your packages are on a cromfs, running "ipkg update" is going to tear through your available MTD space really fast. And ipkg is not graceful at updates the way dpkg is; it failed to upgrade base-files due to file conflicts, leaving the updated dnsmasq unable to start. These are the same sorts of conflicts that you see in apt-get upgrade periodically: files moving from one package to another without sufficient package relationships (or in ipkg's case, maybe sufficient package manager support) to do it seamlessly. Then when I retried the update it succeeded, but it wiped out my firewall config and password file without asking. I don't really blame OpenWRT for this. "ipkg update" just isn't a good idea with their tools. But I miss apt. And I really miss 2.6 kernels; the binary-only Broadcom drivers that power the WRT54G only work on 2.4.30. And it's tight on flash/RAM anyway. So I went looking at options. Obviously, I can't get something that does exactly what I want for the kind of mass-market price the WRT54G sells at. But a suggestion from a coworker sent me looking at Mini-ITX systems, like the nice-looking Mini-Box M200. And at smaller things, like the WRAP WiFi and Soekris boards. I haven't done a hardware project of any sort since last summer, so I'm thinking about building myself an access point with benefits. I haven't decided what the benefits will be yet - if I get something like one of the Soekris boards, probably just bigger compact flash and back to dnsmasq for internal DHCP. But if I get a Mini-ITX system, I can throw a hard drive in it, arrange over-the-network backups, and use it as an incoming mail hub. This would let me decomission one of the always-on computers in my office. A mighty attractive proposition, although a bit less so now that the heat wave has broken.

Alexander Sack: Please test firefox/thunderbird/mozilla security packages

Hi all, we uploaded preview packages for the next security update of mozilla applications
in debian sarge. This is the second maintenance release after mozilla foundation officially ended
support for the product versions we ship in sarge. The packages are based on the patches I
backported and announced a few days ago [1]. If you are a more or less advanced debian-sarge user (or developer) who wants to contribute and
you are using one of the mozilla apps, then please help by testing
this preview release and provide both, negative and positive feedback to pkg-mozilla-maintainers@lists.alioth.debian.org. To test this release, please upgrade your favorite mozilla app from the sources given below. The repository that contains the new packages can be found at http://people.debian.org/~asac/security. The applications and versions of concern are: You can either download the .debs manually or add the following to your apt sources.list:
deb http://people.debian.org/~asac/security ./
If you run into troubles with any of the new packages, chances are high this is due to some
extension that makes use of some corner-case feature. In order to help to track these cases down
you should disable your extensions one by one until you get rid of the problem. If you find the
extension that causes all the troubles, please don’t forget to mention its name and version. Thanks for your support! [1] – http://www.asoftsite.org/s9y/archives/112-Its-mozilla-patch-day!.html

5 August 2006

Steve Kemp: The foulest stench is in the air

I received a few interesting comments on my last post about mailing list software so I’m going to summerise my current thoughts. Before covering the available software I’ll say what I personally need from a mailing list manager: When it comes to the handling of spam I mostly don’t care. Messages are filtered via the mailserver at SMTP time (ditto for viruses) and although moderation is generally useful I prefer to either bounce or eat the messages which are not forwarded. (Either case is fine so long as logs are available). This simplifies things significantly since the pedning messages don’t need to be stored/queued. Here is a list of all the mailing list software which is available to users of Debian’s Sarge release along with some of my thoughts/comments/impressions. (Some of these details may be wrong, I’d happily be educated …):
ecartis
The Ecartis package for Debian GNU/Linux is mostly broken. In sid the package is essentially unmaintained, and that is a worrying sign. Ignoring that for the moment the software works reasonably well. It allows most of the kind of control I desire but the significant downside is that it is severaly broken with regard to character sets and encoding issues. For a cromulent example see this message.
enemies-of-carlotta
This software wins double-plus bonus points for a most excellent name. Naming software is hard, and although the relationship between the film and the purpose of the software is random I like it! eoc suffers from a virtually non-existant set of documentation. Whilst it might be simple to use I it isn’t documented except in a single manpage. I seem to recall I had difficulty getting my Exim4 configuration to pass relevent environment variables ($SENDER + $RECIPIENT) passed into the script properly. The lack of documentation just made this more irritating.
fml
There is a lot of documentation for this, which is half in English and half in Japanese. I admit I mostly didn’t explore this software - although my impression is that it doesn’t have support for virtual hosts.
mailman
Mailman is big, popular, and I dislike it with a passion. The admin interface has a billion configuration options, but even if you know they exist finding the damn things are an impossible job. The system requires about five python processes running even when it is “idle”. In my mind a mailing list software doesn’t need a daemon componant - just a program to spawn when a message “comes in”. The whole password system is broken and gains you zero additional security. Again to rail against mailman: it has integrated message archival, something i think should be distinct. (eg. mhonarc). Virtual hosting is possible, but I believe that mailing list names must be distinct regardless of domain name. That may not be correct honestly I’ve detested the softwware with a passion which suprises me and I may not be 100% objective here.
mlmmj
Looks nice. Looks clean. doesn’t look particularly joyful. (The name mlmmj means “mailing list managing made joyful”.) It doesn’t appear to support virtual hosting, and it doesn’t appear to support enough different list types.
quickml
Listens upon a network port (10025 by default) and not support different list types or virtual hosting.
smartlist
Complex. Icky.
sympa
Seems very featureful, but it is yet another system which has an integrated web-component like mailman == bad. It doesn’t support having the same named mailing list in multiple virtual hosts, although it appears to do everything else I desire.
In summery: There are several available packages, but none are good, and many are actively bad. I still believe that creating another list server would be a useful thing to do. I’ve written a brief design overview elsewhere which I will post for comment later. I’d like to support a couple of “advanced” features such as allowing the mailing list software to only accept GPG signed messages, or to act as a remailer such that messages posted to the list will be automatically GPG signed prior to delivery to all users. Looking around I think most of the individual bits of code are available (in Perl). eg. Mail::Message, Mail::GPG, etc. Its just a matter of gluing the bits together in a modular fashion.

4 August 2006

Wouter Verhelst: Password expiration sucks!

Just a few moments ago, I was trying to commit a minor fix to the NBD subversion repository. However, suddenly the server refused my commit; the password which I knew to be right wasn't working. So I loaded SourceForge.net in my browser and went to the admin link there to find out whether I had perhaps fucked up my own commit rights. I've been known to do that before. Doing so of course required me to log in. Which revealed the problem that was causing this in the first place: apparently my password had expired. I had been using the very same password since ages, but for some reason unknown to me, sourceforge has now decided that they want to introduce password expiry. Of course, good password management is very important if you want to avoid issues with people stealing your passwords. For that reason, I usually generate my passwords with pwgen -s 15, which generates passwords that are impossible to guess—one example of an actual password that I have used in the past (but that I do not have in use in any other system anymore today) is qChjZeWIbSDGON/. The hard part is, probably, to memorize that; for that, I have a pretty simple method: I enter 'gpg -o ~/foo' and enter my new password. Then I pick out some random .jpg file somewhere on my hard disk, and concatenate the gpg data to that file. It is usually still possible to view the file in a viewer with that extra data added to it; IME, most image viewers have the ability to view all data in a corrupt JPG-encoded image that occurs before the corruption—which in this case, will be all of the image. As such, if you don't know which file it is, and you don't know my GPG password, chances are low that you'll find it and steal my login data. Additionally, of course the .jpg file is either removed or restored to its original state when I memorized the password, and finally I also update my GPG key and the password of the system that contained the file with the encrypted password to be using the same new password, so chances of stomeone stealing it get even lower. However, even with this method, it still takes me a few days or weeks to memorize it. Also, synchronizing the new password to all the systems and websites on which I have an account takes a while. For that reason, I prefer not to do it too often. With that in light, it is slightly problematic to have an account on a system that has a password expiration policy in force, because a) this makes it impossible for me to use the highly secure passwords that I use "everywhere else" on these expiration-using systems, b) because the average expiration policy is 2 months, making it impractical for me to generate secure passwords for these sites as well (by the time I memorized the new password, we're already at least halfway through the two months if I need to use that password fairly regularly—or it might even be too short if I don't use the password regularly. The result of the above is that password expiration policies, in my case, force me to use less secure passwords of which I'm sure I can remember them—old passwords which I used before I had a GPG key or had learned about pwgen. I still use those on websites that require me to enter a password but which I do not trust to handle my passwords in a secure manner; I don't want to give these sites the password to unlock my gpg key, for example. The problem with these passwords is that they are easy to guess; they're usually not some unintelligible bit of random letters, but are six to eight characters that actually have a meaning. In fairness, I did have one of those old and insecure passwords in use at sourceforge, because I indeed didn't trust them with my secure passwords. If they base their password expiration policy on the strength of the password, then this whole blog post should be ignored. But in general, it is my point that password expiration policies do not improve security at all. It forces people to use passwords that they can quickly memorize (otherwise they're trying to memorize all the time), and it does not give people who usually pick easy to guess passwords any incentive to pick better, harder to guess passwords. On the contrary, in fact. Password expiration policies suck.

Christine Spang: Just Dinner

I feel a little scandalous when eating dinner in a sit-down restaurant by myself. There’s something weird about walking in and saying, “just one,” and then constantly being approached a little tentatively by the waitress, occasioning an “are you alright?” once or twice. Maybe I’m not smiling enough. Maybe I look depressed and friendless. But I really just was passing through the neighbourhood on the way from here to there, and happened to be really hungry and in the mood for this particular restaurant. Huh.

Erich Schubert: E-Passports cracked

As reported on engadget, E-Passports have been hacked less than one month before they are to be deployed. Apparently "hackers" (well: scientists) were able to copy the electronic passport. So seems like after all, the physical properties of the passport are still the more secure part. Note that you don't need RFID for making passports fast to read. My passports have been featuring easily machine readable letters for ages. And of course there are bar codes, too. No benefits from wireless here. It's all about tracking. About cutting into your privacy. Other related articles: VeriChip VeryEasy to clone longer article on this "hack", on wired.com

3 August 2006

Biella Coleman: In between pride and anxiety: the state of South Africa

Writing blog entries in South Africa did not come so easily, mainly for technological reasons. While for the first 4 days of my trip I had steady Internet access, most of my time was spent enjoying the Law and Society Summer Institute. Once over, I headed from Joburg to Durban and my access became much spottier, not to mention that Bernard, my indefatigable host, made sure the days were filled seeing the gritty but beautiful urban beach town, hanging with the crew of University of Chicago students/graduates that descended upon the city, and having a go at sufring in the Indian Ocean. In the evenings, I did have some free time, but they were too chilly for me to do much of anything but burrow myself deep under a small mountain of covers and pass out after a day filled with plenty to do and see. The theme of the conference I attended was the intersection of rights and regulations and given the Summer Institute was held in South Africa, it was not all that surprising that much of the conversation centered on one class of rights, those of human rights. Since the end of apartheid, SA has become a particularly-impossible-to-ignore beacon for human rights, and acts as a sort of modern guiding light that has defined the meaning and institutionalization of human rights post-WWII. So if WWII and the Holocaust represent the generative genesis of human rights, South Africa represents a new era of human rights, a place that revisited, rejuvenated the discourse and implementation in a post-Apartheid Constitution that has been touted, world-wide, as exemplary for its generous commitment to equality and other rights. In this respect, one feels, quite everywhere, the collective pride of a nation who managed to end a brutal regime and it did so under the gaze of world who followed the drama on TV screens, college campuses, and newspaper headlines. As SA has moved to another era of picking up pieces and trying to build a more equitable society, many in the world are still eagerly watching. But pride does not stand alone, in isolation, for it mixes with other collective sentiments. The collective admiration and pride of a nation, like the sweet water of a river, visibly and freely mixes with a more salty frustration and anxiety to produce an in-between brackish state of affairs. Pride in other words sits alongside social anxiety, which palpably manifests at different registers and tones, to texture the cultural and political landscapes of SA. The frustration follows from the fact that many are still living in dire poverty and in the last ten years, many steady jobs have vanished. Shantytowns, the symbols and material conditions of apartheid, are still omnipresent (though very well hidden from the middle class and the rich). The ruling government, while having roots in communism and socialism, has to contend with a world-wide regime of neoliberal governance and, thus, must try to balance satisfying commitments with the outside world with delivering promised goods to its population, demands that often run uncomfortably counter to the neoliberal logic of deregulation and financial austerity. Alongside this or perhaps as a manifestation of it, the talk of the town, especially in Johannesburg, is of the rampant crime. As a sign of crime and fear, most middle-class and wealthy houses are adorned with metal fences, barbed wires, electric fences, and a simple sign from private security companies (Chubb being the most common in Johannesburg) that announce they provide armed response security to break-ins. This is serious stuff. And while some of the fear of crime is a self-perpetuation exaggeration of itself (and as my friends explained, before the end of Apartheid the monitoring of crime was not as common, so crime statistic can only go one direction, up), it has in certain parts of cities spiraled out of control. And if there comes a time when the crime abates, the architecture of barbed wire and security services is now really an architecture-in-place and will be hard to dislodge from the mental and physical spaces of SA. So more than anything else, I found that the vibe of SA seesaws between pride and anxiety. As a visitor, you are enveloped in this dyanmic duality. You can’t help share in the pride now enshrined in national monuments and museums. But at the same time, you also are not sure what path the nation is heading in and you too share in the fear of crime and move your body and belongings cautiously through the cities. There is no doubt of the governmental commitment to provide services like health care and housing, a commitment that in places like the United States seems to exist more like an endangered species on the brink of perpetual extinction. And so it was awfully refreshing to be in a place where talk of such things is not seen with a suspicious eye that in the US is often tagged as something that runs counter to the realization of freedom and a just society. But whether these important goals can be brought into the plane of existence is another question, one that is not unique to SA but is something that many other countries, especially Latin American countries, from Venezuela to Bolivia are also asking and trying to answer. Bernard and others reminded me that South Africa is number 4 in terms of producing new millionaires, which is quite a remarkable statistic given how many nations there are in the world. But despite the poverty of the place, this wealth is evident and there was one place in particular that symbolized this: Melorse Arch. Located in Johannesburg, this is a lifestyle compound/gated community that mixes posh residential condos with posh restaurants and bars. To tell you the truth, I have never seen anything like this and it was probably been the most extraordinary thing I saw in South Africa. The United States and Puerto Rico (where I am from) and undoubtedly many parts of the world are no strangers to gated communities. But Melrose Arch took the implementation of them to a whole new, somewhat disturbing, level, in part because the domestic sphere of expensive housing co-mingles so intimately with sites of accentuated consumption, reminding visitors that the point of life, (hence the name lifestyle) is to make money so as to consume, and to do so lavishly. And what brought this really home was that the South African Bond Market was also located here in Melrose Arch. In fact we could see the building clearly from our restaurant, which proudly displayed a large Elephant statute (which, I think, harkens to the large bull in Wall Street NYC). I guess if you are a bond trader, and dislike commuting, and like good places to eat, well this is the place for you as you don’t ever have to leave your complex. Work and play become seamless and thus this place is perhaps one of the most powerful signs that the point of work is to play, is to consume, so that a perfect cycle is reached in which making money is a path for self-pleasure (or at least nuclear-family self-pleasure), a form of life, that does not have to engage with the rest of society, literally. Of course, there are many layers of production that do exist and make a place like Melrose Arch possible yet are well hidden from the visitors and residents of the compound. But Melrose Arch is not fully gated. It is open to outsiders so they can enjoy the fine dining, and if you sit in one of the many outdoor tables, one can fully take in the glittering performance of this social cycle, and for some, undoubtedly it is a measure for and of the good life, the right life, that to which others will aspire. What I find interesting about the place is that it captures, with unmistakable clarity and precision, the point of much of neoliberal economy, especially the love for finance (in which money seemingly is made out of nothing), a robust service economy (the service in the restaurant was unlike anything I have seen, with people bring you ceramic jugs of water to wash your hands, live entertainment, outdoor fires, and blankets, henna painters etc), and consumptive pleasure. To drive home the point, in Melrose Arch, there is not even a supermarket; lest there be any mistake, this place was constructed as a place of consumption, through and through. There were many other posh areas in South Africa, and as I mentioned earlier, the impoverished areas were kept a distance from middle class neighborhoods, so much so, that in some areas, like Cape Town, you really had to go out of your way to see them (again this is very different from many parts of Latin America where, in an instant, poor neighborhoods switch to wealthy). On the other hand, quite visible were things like malls and there were a lot of them. Apparently South Africa has been a testing ground for the modern mall. To get to the malls, there are very good roads to travel (much better than most of Latin America) and other basic services like tap water, and infrastructure like airports and phones, are in excellent condition. So it was somewhat surprising and frustrating that Internet services outside of business are somewhat scant, expensive, and slow. Sure Internet services are the best in Africa and you can get Cable, ADSL etc. at home but you have to pay a pretty Rand for it and on top of it, the access is pretty slow. Now, there are many parts of the world where this is the case (though apparently in a study that compared 12 countries at a similar lever of development to SA, Internet access was 10 times more expensive in SA than the most expensive country which was Chile), but for me, it was the juxtaposition of having such solid infrastructure and wealth mixed with lackluster Internet access that made it somewhat odd. And it also made me realize how much the Internet and access to it had not only saturated my life, but how I have come to see it as a something creeping close (though not the same) as a basic right. Of course, security and self-determination, food, shelter, and health services are for me are the basic architecture of human rights. Without these, existence in the most basic sense becomes difficult. Access to the Internet, though in no way is indispensable to the basic conditions of living, can at least greatly facilitate the type of political work and organizing needed to demand other basic human rights. In this sense, it is more like an extension of or at least serious complement to basic services like clean water, and it seems like once there has been an investment in securing fiber optic (which I am sure is pricey), the cost of maintenance compared to physical infrastructures is so much smaller that it is really worth the initial costs. This bring up some difficult questions and vexing specters related to many of the human rights (in the Universal declaration), which are I think not so much so how to define them in a general sense (I think this has been laid out somewhat well) but how to specify them so as to realistically implement them . On the one hand, the flexibility and vagueness of human rights is what gives it tremendous currency. Folks around the world have wielded the discourse of human rights to make demands that resound strongly and profoundly. But once a proclamation of a human right has been made, like article 25:
Everyone has the right to a standard of living adequate for the health and well-being of himself and of his family, including food, clothing, housing and medical care and necessary social services, and the right to security in the event of unemployment, sickness, disability, widowhood, old age or other lack of livelihood in circumstances beyond his control..
it seems like the real hard work is about specifying and implementation. We may easily agree that an adequate standard of living may not be Melrose Arch but it still does need definition and a plan for implementation. And so there seems to be plenty of room in human rights politics to move from the state of declaration to that of strategies of implementation.

Andrew Pollock: [tech] Why I like Open Source

20:19 < Caesar> Where best should I file a bug about eject not being installed on an etch desktop system
20:20 < Caesar> Right clicking on a CD and ejecting fails
20:20 < Caesar> tasksel?
20:21 < joeyh> did you install from cd?
20:25 < Caesar> joeyh: netboot
20:25 < joeyh> yeah, that'll be why, it's only installed in cd installs and maybe floppy on powerpc or something
20:26 < Caesar> But GNOME clearly uses it
20:26 < Caesar> So shouldn't the desktop task drag it in?
20:26 < CIA-1> tasksel: joeyh * r1474 /trunk/ (debian/changelog tasks/desktop):
20:26 < CIA-1> tasksel: * Add eject to desktop task as it's not installed by d-i in all cases and is
20:26 < CIA-1> tasksel:  used by gnome.
20:27 < Caesar> heh

2 August 2006

Roland Mas: Free as in freelance

It's official: I'm going to be on extended unpaid leave from my employer starting on the 22nd of June, for at least a year. I've been a part-time free software freelance for two years and a half, and I think now is a good time to grow that activity. Also, since I was hired almost seven years ago, the company grew (well, "was assimilated" is more like it) from about fifteen people (small start-up) to more than two hundred thousand (France T l com / Orange, you may have heard of them), and the growth pains haven't quite subsided yet. So I hope I'll get a breath of fresh air, at least, in case my venture goes flop and I go back to FT next year. So yeah, I'll be freelancing on everything I can, but my initial focus will probably stay on Gforge, Debian and related topics. Feel free to browse my Gnurandal website and contact me if you're looking for someone. I'm based in France, but if the job can't be done via Internet, I'd be happy to fly to all sorts of places.

Roland Mas: Dead PDA

It seems what I've called my PDA for almost seven years (a Sharp PA-X500) is now dead. Well, it's not quite dead, but apparently the touch-sensitive screen is no longer sensitive to touching, and I'm not aware of any other input device for it. So I'm appealing to my fellow geeks, at least to those of you who know about this kind of things; hear my plea, and please provide some advice. People from Japan, I'm especially eager for your wisdom. First, is there any way I could recover the data that's in it? There's nothing deadly important, it's just to save me the bother of collecting all these phone numbers and addresses again. Some have sentimental value, even if I have totally lost touch with their owners. Before someone suggests deep hackery like removing the memory chip and plugging it into some hand-soldered adaptor then into their old Amstrad, I was more thinking about something infrared, since there's an infrared port. The problem is: can it be activated from outside? I can't switch the thing on the usual way (since the touchscreen is, well, not touchy), I can only get to what's best depicted by this picture of what happens when I remove and re-insert the battery. It's the standard touchscreen calibration tool, from what I understood, but maybe it says somewhere that it can be switched to infrared file-server or so. The manual (in Japanese) mentions Zaurus thingies numerously, but I don't know what they say about them (my Japanese skills are old, and they were never that great anyway). Any idea? Second part, in the very likely case I'm going to replace it: what should I buy? My specs are: stuff the PDA features, I initially bought that as a kanji dictionary, so the replacement needs to have a kanji dictionary too. One where you draw the kanji on the screen, and it recognises it. I'm clueless when it comes to classifying kanji, and if I have to tell the thing that what I'm looking for is something with 17 strokes and the key for "hand", then it loses much of its interest. A kanji→English dictionary would be nice, but not needed. I've managed to cope with kanji→Japanese then Japanese→English. The other, more normal, PDA thingies (addressbook, scheduler, world clock, alarm, etc.) would be nice, but are not compulsory. I don't care about games. I'm going to visit Japan in October, and yes I will spend a couple of hours of Akihabara, but I'd like ideas and opinions beforehand. If someone has an idea for getting the data out but it would require the manual, just say so, I'll bring it along. Why it chose to break down now will stay a mystery. Maximum embarrassment for me because I'll be dictionary-less for a few days in Japan? Or longing for some well-deserved rest since I'm soon going to have the opportunity to replace it? No idea. In any case, it sucks.

Isaac Clerencia: ccache + pbuilder

As it looks like there is some ccache hype lately in Planet Debian, I’ll add some of my own. I use pbuilder to build my packages and it was a real PITA when some big package like wesnoth or kdesomething failed to build and I’d to restart the build from scratch, so (after several months of procastination) I decided to add ccache powers to my pbuilder setup. In fact, it was quite easy, although a bit “dirty”.
  1. Create a directory to store the ccache cache for your pbuilder, for example,
    /var/cache/pbuilder/ccache
  2. Create a directory to put the needed pbuilder hooks, for example, ~/debian/pbuilder-hooks/
  3. Add an A (run just before starting the build) hook to set up ccache, for example, A01ccache:

    #!/bin/sh
    echo "Setting up ccache"
    apt-get install ccache
    cd /usr/lib/ccache
    for c in *
    do
       ln -s /usr/bin/ccache /usr/sbin/$c
    done
    ln -s /var/cache/pbuilder/ccache /root/.ccache

    This is the dirty bit, as I can’t set $PATH from one of the hooks, I link the ccache stuff into /usr/sbin/ which precedes /usr/bin/ in $PATH, if somebody knows any other clean way (i.e., without modifying the chroot) to do this, please tell me.
  4. I’ve two more hooks, to run interactive shells when the package finishes building (or fails building), note that you need to run the shell like this:

    /bin/bash < /dev/tty > /dev/tty
  5. Run pbuilder with the correct options, I’ve a script named wonderbuild to do this:

    #!/bin/sh
    pdebuild -- --bindmounts /var/cache/pbuilder/ccache --hookdir ~/debian/pbuilder-hooks/ $*
I expect this to be useful to somebody else, it works really great for me :) Any improvement would be welcome.

Next.

Previous.