Vertical rhythm aligns lines to a consistent spacing cadence down the page. It
creates a predictable flow for the eye to follow. Thanks to the rlh CSS unit,
vertical rhythm is now easier to implement for text.1 But illustrations
and tables can disrupt the layout. The amateur typographer in me wants to follow
Bringhurst s wisdom:
Headings, subheads, block quotations, footnotes, illustrations, captions and
other intrusions into the text create syncopations and variations against the
base rhythm of regularly leaded lines. These variations can and should add
life to the page, but the main text should also return after each variation
precisely on beat and in phase.
Robert Bringhurst, The Elements of Typographic Style
Text
Three factors govern vertical rhythm: font size, line height and
margin or padding. Let s set our baseline with an 18-pixel font and a 1.5
line height:
CSS Values and Units Module Level 4 defines the rlh unit, equal to the
computed line height of the root element. All browsers support it since
2023.2 Use it to insert vertical spaces or to fix the line height
when altering font size:3
We can check the result by overlaying a grid4 on the content:
Using CSS rlh unit to set vertical space works well for text. You can display the grid using Ctrl+Shift+G.
If a child element uses a font with taller intrinsic metrics, it may stretch
the line s box beyond the configured line height.5 A workaround
is to reduce the line height to 1. The glyphs overflow but don t push the line
taller.
code,kbdline-height:1;
Responsive images
Responsive images are difficult to align on the grid because we don t know their
height. CSS Rhythmic Sizing Module Level 1 introduces the block-step
property to adjust the height of an element to a multiple of a step unit. But
most browsers don t support it yet.
With JavaScript, we can add padding around the image so it does not disturb
the vertical rhythm:
The image is snapped to the grid thanks to the additional padding computed with JavaScript. 216 is divisible by 27, our line height in this example.
As the image is responsive, its height can change. We need to wrap a resize
observer around the adjust() function:
Tables
Table cells could set 1rlh as their height but they would feel constricted.
Using 2rlh wastes too much space. Instead, we use incremental leading: we
align one in every five lines.
To align the elements after the table, we need to add some padding. We can
either reuse the JavaScript code from images or use a few lines of CSS that
count the regular rows and compute the missing vertical padding:
A header cell has twice the padding of a regular cell. With two regular rows,
the total padding is 2 2 0.2+2 0.4=1.6. We need to add 0.4rlh to reach
2rlh of extra vertical padding across the table.
One line out of five is aligned to the grid. Additional padding is added after the table to not break the vertical rhythm. 405 is divisible by 27, our line height in this example.
None of this is necessary. But once you start looking, you can t unsee it. Until
browsers implement CSS Rhythmic Sizing, a
bit of CSS wizardry and a touch of JavaScript is enough to pull it off. The main
text now returns after each intrusion precisely on beat and in phase.
For broader compatibility, you can replace 2rlh with
calc(var(--line-height) * 2rem) and set the --line-height custom
property in the :root pseudo-class. I wrote a simple PostCSS
plugin for this purpose.
It would have been nicer to compute the line height with
calc(round(up, calc(2.4rem / 1rlh), 0) * 1rlh). Unfortunately, typed
arithmetic is not supported by Firefox yet. Moreover, browsers support
round() only since 2024. Instead, I coded a PostCSS
plugin for this as well.
The following CSS code defines a grid tracking the line height:
Armadillo is a powerful
and expressive C++ template library for linear algebra and scientific
computing. It aims towards a good balance between speed and ease of use,
has a syntax deliberately close to Matlab, and is useful for algorithm
development directly in C++, or quick conversion of research code into
production environments. RcppArmadillo
integrates this library with the R environment and language and is
widely used by (currently) 1263 other packages on CRAN, downloaded 45.7 million
times (per the partial logs from the cloud mirrors of CRAN), and the CSDA paper (preprint
/ vignette) by Conrad and myself has been cited 683 times according
to Google Scholar.
This versions updates to the 15.2.5 and 15.2.6 upstream Armadillo releases from,
respectively, two and five days ago. The package has already been
updated for Debian, and built for
r2u. When we ran the
reverse-dependency check for 15.2.5 at the end of last week, one package
failed. I got in touch with the authors, filed an issue, poked some
more, isolated the one line that caused an example to fail and right
then 15.2.6 came out fixing just that. It was after all an upstream
issue. We used to ran these checks before Conrad made a release, he now
skips this and hence needed a quick follow-up release. It can
happen.
The other big change is that this R package release phases out the
dual support for both C++14 or newer (as in current Armadillo) along with a C++11
fallback for more slowly updating packages. I am happy to say that after
over eight months of this managed transition (during which CRAN expulsed some laggard
packages that were not moving in from C++11) we are now at all packages
using C++14 or newer which is nice. And I will take this as an
opportunity to stress that one can in fact manage a disruptive API
change this way as we just demonstrated. Sadly, R Core does not seem to
have gotten that message and rollout of this package was also still a
little delayed because of the commotion created by the last minute API
changes preceding the R 4.6.0 release later this week.
Smaller changes in the package are a switch in pdf vignette
production to the Rcpp::asis() driver, and a
higher-precision computation in rmultinom() (matching a
change made in R-devel during last week in its use of Kahan summation).
All detailed changes since the last CRAN release follow.
Changes in
RcppArmadillo version 15.2.6-1 (2026-04-20)
Upgraded to Armadillo release 15.2.6 (Medium Roast Deluxe)
Ensure internally computed tolerances are not NaN
The rmultinom deploys 'Kahan summation' as R-devel
does now.
Changes
in RcppArmadillo version 15.2.5-1 [github-only] (2026-04-18)
Upgraded to Armadillo release 15.2.5 (Medium Roast Deluxe)
Fix for handling NaN elements in .is_zero()
Fix for handling NaN in tolerance and conformance checks
Faster handling of diagonal views and submatrices with one
row>
Sunset the C++11 fallback of including Armadillo 14.6.3 (#504
closing #503)
The vignettes have refreshed bibliographies, and are now built
using the Rcpp::asis vignette builder (#506)
One rmultinom test is skipped under R-devel which
has switched to a higher precisions calc
FBReader
After my previous blog post about eBook readers in Debian [1] a reader recommended FBReader. I tried it and it s now my favourite reader. It works nicely on laptop and phone and takes significantly less RAM than Calibre or Arianna (especially important for phones). While the problems with my FLX1s not displaying text with Calibre or Arianna might be the fault of something on the FLX1s side those problems just don t happen with FBReader.
FBReader has apparently now got a proprietary version as the upstream, but we still have FOSS code to use in Debian. It would be nice if someone updated it to store the reading location using WebDAV and/or a local file that can be copied with the NextCloud client or similar. Currently there is code to store reading location in the Google cloud which I don t want to use. It s not THAT difficult to see what chapter you are at with one device and just skip to that part on another, but it is an annoyance.
One thing I really like about FBReader is that you can run it with a epub file on the command line and it just opens it and when it s been closed you can just open it again to the same spot in the same file. I don t want a library to view a book list, I just want to go back to what I was last reading in a hurry. Calibre might be better for some uses, for example I can imagine someone in the publishing industry with a collection of thousands of epub files finding that Calibre works better for them. But for the typical person who just wants to read one book and keep reading it until they finish it FBReader seems clearly better. The GUI is a little unusual, but it s not at all confusing and it works really well on mobile.
Okular
I tried Okular (the KDE viewer for PDF files etc) which displays epub files if you have the okular-extra-backends installed, but it appears to not display books with the background color set to black. I would appreciate it if someone who has read some public domain or CC licences epub files can recommend ones with a black background that I could use for testing as I can t file a Debian bug report without sample data to reproduce the bug. I decided not to use it for actual book reading as FBReader is far better for my use taking less RAM and being well optimised for mobile use.
Folite
Foliate supports specifying a book on the command-line which is nice. But it takes more memory than FBReader which is probably mostly due to using webkit to display things. The output was in 2 columns on my laptop in small text which is probably configurable but I didn t proceed with it. I determined that it doesn t compare with FBReader for my use. It s written in JavaScript which may be a positive feature for some people.
Koodo
I had a brief test of Koodo which isn t in Debian. Here is the Koodo Reader Github [2]. I installed the .deb that they created, it installs files to /opt/Koodo Reader/ (yes that s a space in the directory name) and appears to have Chromium as part of the runtime. I didn t go past that even though it appears to have a decent feature set. It is licensed under version 3 of the AGPL so is suitable for Debian packaging if someone wants to do it.
Thorium
I saw the Thorium reader on Github [3] which looks promising, it s under the BSD 3 clause license so is suitable for Debian packaging. The EDR Lab seems like a good project for advancing electronic document use [4] and it would be good to have their stuff in Debian.
For the moment I m happy using FBReader.
I recently released version 0.3.0 of my recipe manager application Kookbook find it in git in KDE Invent or as released tarballs in https://download.kde.org/stable/kookbook/
Changes since last time is more or less Minor bugfixes and a Qt6 port nothing as such noteworthy unless you aim to get rid of Qt5 on your system.
so what is kookbook?
It is a simple recipe viewer that works with semi-structured markdown. More details can be seen in the quite old 0.1.0 announcement
At some point I should do a 10 recipe example collection, but my personal collection is in danish, so I m not sure it is going to be useful. Unless someone will donate me some handfuls of pre-formatted recipes, I will happily announce it.
Surface Detail is the ninth novel in Banks's Culture science
fiction (literary space opera?) series. As with most of the Culture
novels, it can be read in any order, although this isn't the best starting
point. There is an Easter egg reference to Use of Weapons that would be easier to notice if you have read
that book recently, but which is not that important to the story.
Lededje Y'breq is an Indented Intagliate from the Sichultian Enablement.
Her body is patterned from her skin down to her bones, covered with
elaborate markings similar to tattoos that extend to her internal organs.
As an intagliate, she is someone's property. In her case, she is the
property of Joller Veppers, the richest man in the Enablement and her
father's former business partner. Intagliates are a tradition of great
cultural pride in the Enablement. They are a living representation of the
seriousness with which debts and honor are taken, up to and including
one's not-yet-born children becoming the property of one's debtor. Such
children are decorated as living works of art of the highest skill and
technical sophistication; after all, the Enablement are not barbarians.
As the story opens, Lededje is attempting, not for the first time, to
escape. This attempt is successful in an unexpected way.
Prin and Chay are Pavulean researchers and academics who, as this story
opens, are in Hell. They are not dead; they have infiltrated the Hell that
Pavuleans are shown to scare them into proper behavior in order to prove
that it is not an illusion and their society does indeed torture people in
an afterlife, in more awful ways than people dare imagine. They have
reached the portal through which temporary visitors exit, hoping to escape
with firm evidence of the existence and horrors of the Pavulean afterlife.
They will not be entirely successful.
Yime Nsokyi is a Culture agent for Quietus, the part of Contact that
concerns itself with the dead. Many advanced societies throughout the
galaxy have invented and reinvented the ability to digitize a mind and
then run it in a virtual environment. Once a society can capture the minds
of every person in that society from that point forward, it faces the
question of whether to do so and, if it does, what to do with those minds.
More specifically, it faces the moral question of whether to punish the
minds of people who were horrible in life. It faces the question of
whether to create Hell.
Vatueil is a soldier in a contestation, a limited and carefully monitored
virtual war. The purpose of that war game is to, once and for all, resolve
the question of whether civilizations should be allowed to create Hells.
Some civilizations consider them integral to their religion or
self-conception. Others consider them morally abhorrent, and that conflict
was in danger of spilling over into war in the Real. Hence the War in
Heaven: Both sides committed to fight in a virtual space under specific
and structured rules, and the winner decides the fate of the galaxy's
Hells. Vatueil is fighting for the anti-Hell side. The anti-Hell side is
losing.
There are very few authors who were better at big-idea science fiction
than Iain M. Banks. I've been reading a few
books about AI ships and remembered that I had two unread Culture novels
that I was saving. It felt like a good time to lose myself in something
sprawling.
Surface Detail does sprawl. Even by Banks's standards, there was an
impressive amount of infodumping in this book. Banks always has huge and
lovingly described set pieces, and this book is no exception, but there
are also paragraphs and pages of background and cultural musings and
galactic politics. We are introduced to not one but three new Contact
divisions; as well as the already-mentioned Quietus, there is Numina,
which concerns itself with the races that have sublimed (transcended), and
Restoria, which deals with hegemonizing swarms (grey goo nanotech,
paperclip maximizers, and their equivalents).
Infodumping is both a feature and a bane of big-idea science fiction, and
it helps to be in the right mood. It also helps if the info being dumped
is interesting, and this is where Banks shines. This is a huge, sprawling
book, but it deals with some huge, sprawling questions and it has
interesting and non-reductive thoughts about them. The problems posed by
the plot come with history, failed solutions, multi-sided political
disputes, strategies and tactics of varying morality and efficacy, and an
effort to wrestle with the irreducible complexity of trying to resolve
political and ethical disagreements in a universe full of profound
disagreements and moral systems that one cannot simply steamroll.
It also helps that the characters are interesting, even when they're not
likable. Surface Detail has one fully hissable villain (Veppers) as
a viewpoint character, but even Veppers is interesting in a "let me check
the publication date to see if Banks was aware of Peter Thiel" sort of
way. The Culture ships, of which there are several in this story, tend
towards a gently sarcastic kindness that I find utterly charming. Lededje
provides the compelling motive force of someone who has no involvement in
the broader philosophical questions and instead intends to resolve one
specific problem through lethal violence. Vatueil and Yime were a bit
bland in personality, more exposition generators than characters I warmed
to, but their roles and therefore the surrounding exposition were
fascinating enough that I still enjoyed their sections.
I'm sure this is not an original observation, but I was struck reading
this book in the first half of 2026 that the Culture functions as an
implementation of what the United States likes to think it is but has
never been. It has a strong sense of shared ethics and moral principles,
it tries to export them to the rest of the galaxy through example,
persuasion, and careful meddling, but it tries to follow some combination
of pragmatic and moral rules while doing so, partly to avoid a backlash
and partly to avoid becoming its own sort of hegemonizing swarm. That is a
powerfully attractive vision of how to be an advanced civilization, and
the fact that every hegemon that has claimed that mantle has behaved
appallingly just makes it more intriguing as a fictional concept. In this
book, like in many Culture books, the Culture is painfully aware of the
failure modes of meddling, and the story slowly reveals the effort the
Culture put into staying just on a defensible side of their own moral
lines. This is, in a sense, a Prime Directive story, but with a level of
hard-nosed pragmatism and political sophistication that the endless
Star Trek Prime Directive episodes never reach.
Surface Detail does tend to sprawl, and I'm not sure Banks pulled
together all the pieces of the plot. For example, if there was a point to
the subplot involving the Unfallen Bulbitian, it was lost on me. (There is
always a possibility with Banks that I wasn't paying close enough
attention.) But the descriptions are so elaborate and the sense of
politics and history are so deep that I was never bored, even when
following a plot thread that meandered off into apparent irrelevance. The
main plot line comes to a satisfying conclusion that may be even more
biting social commentary today than it was in 2010.
A large part of the plot does involve Hell, so a warning for those who
haven't read much Banks: He adores elaborate descriptions of body horror
and physical torture. The sections involving Prin and Chay are rather
grim and horrific, probably a bit worse than Dante's Inferno. I
have a low tolerance for horror and I was able to read past and around the
worst bits, but be warned that Banks indulges his love for the painfully
grotesque quite a bit.
This was great, and exactly what I was hoping for when I picked it up.
It's not the strongest Culture novel (for me, that's either
The Player of Games or
Excession), but it's one of the better
ones. Highly recommended, although if you're new to the Culture, I would
start with one of the earlier books that provide a more gradual
introduction to the Culture and Special Circumstances.
Followed, in the somewhat disconnected Culture series sense, by The
Hydrogen Sonata.
Content warnings: Rape (largely off-screen), graphic violence, lots of
Bosch-style grotesque torture, and a lot of Veppers being a thoroughly
awful human being as a viewpoint character.
Rating: 8 out of 10
If you have recently installed a very up-to-date Linux distribution with a desktop environment, or upgraded your system on a rolling-release distribution, you might have noticed that your home directory has a new folder: Projects
Why?
With the recent 0.20 release of xdg-user-dirs we enabled the Projects directory by default. Support for this has already existed since 2007, but was never formally enabled. This closes a more than 11 year old bug report that asked for this feature.
The purpose of the Projects directory is to give applications a default location to place project files that do not cleanly belong into one of the existing categories (Documents, Music, Pictures, Videos). Examples of this are software engineering projects, scientific projects, 3D printing projects, CAD design or even things like video editing projects, where project files would end up in the Projects directory, with output video being more at home in Videos .
By enabling this by default, and subsequently in the coming months adding support to GLib, Flatpak, desktops and applications that want to make use of it, we hope to give applications that do operate in a project-centric manner with mixed media a better default storage location. As of now, those tools either default to the home directory, or will clutter the Documents folder, both of which is not ideal. It also gives users a default organization structure, hopefully leading to less clutter overall and better storage layouts.
This sucks, I don t like it!
As usual, you are in control and can modify your system s behavior. If you do not like the Projects folder, simply delete it! The xdg-user-dirs utility will not try to create it again, and instead adjust the default location for this directory to your home directory. If you want more control, you can influence exactly what goes where by editing your ~/.config/user-dirs.dirs configuration file.
If you are a system administrator or distribution vendor and want to set default locations for the default XDG directories, you can edit the /etc/xdg/user-dirs.defaults file to set global defaults that affect all users on the system (users can still adjust the settings however they like though).
What else is new?
Besides this change, the 0.20 release of xdg-user-dirs brings full support for the Meson build system (dropping Automake), translation updates, and some robustness improvements to its code. We also fixed the arbitrary code execution from unsanitized input bug that the Arch Linux Wiki mentions here for the xdg-user-dirs utility, by replacing the shell script with a C binary.
Thanks to everyone who contributed to this release!
It s true processing data from software defined radios can be a bit
complex
which tends to keep all but the most grizzled experts and bravest
souls from playing with it. While I wouldn t describe myself as either, I will
say that I ve stuck with it for longer than most would have expected of me.
One of the biggest takeaways I have from my adventures with software defined
radio is that there s a lot of cool crossover opportunity between RF and
nearly every other field of engineering.
Fairly early on, I decided on a very light metadata scheme to track SDR
captures, called rfcap. rfcap has withstood my test
of time, and I can go back to even my earliest captures and still make sense of
what they are IQ format, capture frequencies, sample rates, etc. A huge
part of this was the simplicity of the scheme (fixed-lengh header, byte-aligned
to supported capture formats), which made it roughly as easy to work with as a
raw file of IQ samples.
However, rfcap has a number of downsides. It s only a single, fixed-length
header. If the frequency of operation changed during the capture, that change
is not represented in the capture information. It s not possible to easily
represent mulit-channel coherent IQ streams, and additional metadata is
condemned to adjacent text files.
ARF (Archive of RF)
A few years ago, I needed to finally solve some of these shortcomings and tried
to see if a new format would stick. I sat down and wrote out my design goals
before I started figuring out what it looked like.
First, whatever I come up with must be capable of being streamed and processed
while being streamed. This includes streaming across the network or merely
written to disk as it s being created. No post-processing required. This is
mostly an artifact of how I ve built all my tools and how I intereact with my
SDRs. I use them extensively over the network (both locally, as well
as remotely by friends across my widerlan). This decision sometimes even
prompts me to do some crazy things from time
to time.
I need actual, real support for multiple IQ channels from my multi-channel SDRs
(Ettus, Kerberos/Kracken SDR, etc) for playing with things like
beamforming.
My new format must be capable of storing
multiple streams in a single capture file, rather than a pile of files in
a directory (and hope they re aligned).
Finally, metadata must be capable of being stored in-band. The initial set of
metadata I needed to formalize in-stream were Frequency Changes and
Discontinuities. Since then, ARF has grown a few more.
After getting all that down, I opted to start at what I thought the simplest
container would look like,
TLV
(tag-length-value) encoded packets. This is a fairly well trodden path,
and used by a bunch of existing protocols
weallknow
and
love.
Each ARF file (or stream) was a set of
encoded packets (sometimes called data units in other specs). This means that
unknown packet types may be skipped (since the length is included) and
additional data can be added after the existing fields without breaking
existing decoders.
Heads up!
Once this is posted, I'm not super likely to update this page. Once this
goes out, the latest stable copy of the ARF spec is maintained at
draft-tagliamonte-arf-00.txt.
This page may quickly become out of date, so if you're actually interested in
implementing this, I've put a lot of effort into making the draft
comprehensive, and I plan to maintain it as I edit the format.
Unlike a traditional TLV structure, I opted to add flags to the top-level
packet. This gives me a bit of wiggle room down the line, and gives me a
feature that I like from ASN.1 a critical bit. The critical bit indicates
that the packet must be understood fully by implementers, which allows future
backward incompatible changes by marking a new packet type as critical. This
would only really be done if something meaningfully changed the interpretation
of the backwards compatible data to follow.
Flag
Description
0x01
Critical (tag must be understood)
Within each Packet is a tag field. This tag indicates how the contents of the
value field should be interpreted.
In order to help with checking the basic parsing and encoding of this format,
the following is an example packet which should parse without error.
 00, // tag (0; no subpacket is 0 yet)
 00, // flags (0; no flags)
 00, 00 // length (0; no data)
 // data would go here, but there is none
Additionally, throughout the rest of the subpackets, there are a few unique and
shared datatypes. I document them all more clearly in the draft, but to quickly
run through them here too:
UUID
This field represents a globally unique idenfifer, as defined by RFC 9562, as
16 raw bytes.
Frequency
Data encoded in a Frequency field is stored as microhz (1 Hz is stored as
1000000, 2 Hz is stored as 2000000) as an unsigned 64 bit integer. This has a
minimum value of 0 Hz, and a maximum value of 18446744073709551615 uHz, or just
above 18.4 THz. This is a bit of a tradeoff, but it s a set of issues that I
would gladly contend with rather than deal with the related issues with storing
frequency data as a floating point value downstream. Not a huge factor, but as
an aside, this is also how my current generation SDR processing code (sparky)
stores Frequency data internally, which makes conversion between the two
natural.
IQ samples
ARF supports IQ samples in a number of different formats. Part of the idea here
is I want it to be easy for capturing programs to encode ARF for a specific
radio without mandating a single iq format representation. For IQ types with
a scalar value which takes more than a single byte, this is always paired
with a Byte Order field, to indicate if the IQ scalar values are little or
big endian.
ID
Name
Description
0x01
f32
interleaved 32 bit floating point scalar values
0x02
i8
interleaved 8 bit signed integer scalar values
0x03
i16
interleaved 16 bit signed integer scalar values
0x04
u8
interleaved 8 bit unsigned integer scalar values
0x05
f64
interleaved 64 bit floating point scalar values
0x06
f16
interleaved 16 bit floating point scalar values
Header
Each ARF file must start with a specific Header packet. The header contains
information about the ARF stream writ large to follow. Header packets are
always marked as critical .
magic
flags
start
guid
site guid
#st
In order to help with checking the basic parsing and encoding of this format,
the following is an example header subpacket (when encoded or decoded this
will be found inside an ARF packet as described above) which should parse
without error, with known values.
Stream Header
Immediately after the arf Header, some number of Stream Headers
follow. There must be exactly the same number of Stream Header packets as are
indicated by the num streams field of the Header. This has the nice effect of
enabling clients to read all the stream headers without requiring buffering of
unread packets from the stream.
id
flags
fmt
bo
rate
freq
guid
site
In order to help with checking the basic parsing and encoding of this format,
the following is an example stream header subpacket (when encoded or decoded
this will be found inside an ARF packet as described above) which should parse
without error, with known values.
Samples
Block of IQ samples in the format indicated by this stream s format and
byte_order field sent in the related Stream Header.
id
iq samples
In order to help with checking the basic parsing and encoding of this format,
the following is an samples subpacket (when encoded or decoded
this will be found inside an ARF packet as described above). The IQ values
here are notional (and are either 2 8 bit samples, or 1 16 bit sample,
depending on what the related Stream Header was).
01, // id
ab, cd, ab, cd, // iq samples
Frequency Change
The center frequency of the IQ stream has changed since the
Stream Header or last Frequency Change
has been sent. This is useful to capture IQ streams that are jumping
around in frequency during the duration of the capture, rather than
starting and stopping them.
id
frequency
In order to help with checking the basic parsing and encoding of this format,
the following is a frequency change subpacket (when encoded or decoded
this will be found inside an ARF packet as described above).
01, // id
00, 00, b5, e6, 20, f4, 80, 00 // frequency (200 MHz)
Discontinuity
Since the last Samples packet for this stream, samples have been dropped
or not encoded to this stream. This can be used for a stream that has
dropped samples for some reason, a large gap (radio was needed for something
else), or communicating iq snippits .
id
In order to help with checking the basic parsing and encoding of this format,
the following is a discontinuity subpacket (when encoded or decoded this will
be found inside an ARF packet as described above).
01, // id
Location
Up-to-date location as of this moment of the IQ stream, usually from a GPS.
This allows for in-band geospatial information to be marked in the IQ stream.
This can be used for all sorts of things (detected IQ packet snippits aligned
with a time and location or a survey of rf noise in an area)
The sys field indicates the Geodetic system to be used for the provided
latitude, longitude and elevation fields. The full list of supported
geodetic systems is currently just WGS84, but in case something meaningfully
changes in the future, it d be nice to migrate forward.
Unfortunately, being a bit of a coward here, the accuracy field is a bit of a
cop-out. I d really rather it be what we see out of kinematic state estimation
tools like a kalman filter, or at minimum, some sort of ellipsoid. This is
neither of those - it s a perfect sphere of error where we pick the largest
error in any direction and use that. Truthfully, I can t be bothered to model
this accurately, and I don t want to contort myself into half-assing something
I know I will half-ass just because I know better.
In order to help with checking the basic parsing and encoding of this format,
the following is a location subpacket (when encoded or decoded this will be
found inside an ARF packet as described above).
Vendor Extension
In addition to the fields I put in the spec, I expect that I may need custom
packet types I can t think of now. There s all sorts of useful data that could
be encoded into the stream, so I d rather there be an officially sanctioned
mechanism that allows future work on the spec without constraining myself.
Just an example, I ve used a custom subpacket to create test vectors, the data
is encoded into a Vendor Extension, followed by the IQ for the modulated
packet. If the demodulated data and in-band original data don t match, we ve
regressed. You could imagine in-band speech-to-text, antenna rotator azimuth
information, or demodulated digital sideband data (like FM HDR data) too. Or
even things I can t even think of!
id
data
In order to help with checking the basic parsing and encoding of this format,
the following is a vendor extension subpacket (when encoded or decoded this
will be found inside an ARF packet as described above).
Tradeoffs
The biggest tradeoff that I m not entirely happy with is limiting the length
of a packet to u16 65535 bytes. Given the u8 sample header, this limits us
to 8191 32 bit sample pairs at a time. I wound up believing that the overhead in
terms of additional packet framing is worth it because always encoding 4
byte lengths felt like overkill, and a dynamic length scheme ballooned
codepaths in the decoder that I was trying to keep as easy to change as
possible as I worked with the format.
The nineteenth release of the qlcal package
arrivied at CRAN just now, and
has already been built for r2u. This version
synchronises with QuantLib 1.42
released this week.
qlcal
delivers the calendaring parts of QuantLib. It is provided (for the R
package) as a set of included files, so the package is self-contained
and does not depend on an external QuantLib library (which can be
demanding to build). qlcal covers
over sixty country / market calendars and can compute holiday lists, its
complement (i.e. business day lists) and much more. Examples
are in the README at the repository, the package page,
and course at the CRAN package
page.
This releases updates to the 2025 holidays for China, Singapore, and
Taiwan.
The full details from NEWS.Rd follow.
Changes in version 0.1.1
(2026-04-15)
Synchronized with QuantLib 1.42 released two days ago
Calendar updates for China, Singapore, Taiwan
Courtesy of my CRANberries, there
is a diffstat report for this
release. See the project page
and package documentation for more details, and more examples.
Debusine projects in Google s Summer of Code
While Freexian initiated Debusine, and is investing a lot of resources in the
project, we manage it as a true free software project that can and should have a
broader community.
We always had documentation for new contributors
and we aim to be reactive with them when they interact via the issue tracker or
via merge requests. We decided to put those intentions under stress tests by
proposing five projects
for Google s Summer of Code as part of Debian s participation in that program.
Given that at least 11 candidates managed to get their merge request accepted in
the last 30 days (interacting with the development team is part of the
pre-requisites to apply to Google Summer of Code projects these days), the
contributing experience must not be too bad. If you want to try it out, we
maintain a list of quick fixes
that are accessible to newcomers. And as always, we welcome your
feedback!
Debian CI: incus backend and upgrade to Bootstrap 5, by Antonio Terceiro
debci 3.14 was released on March 4th, with a followup 3.14.1 release with
regression fixes a few days afterwards. Those releases were followed by new
development and maintenance work that will provide extra capabilities and
stability to the platform.
This month saw the initial version of an incus backend
land in Debian CI. The transition into the new backend will be done carefully so
as to not disrupt testing migration. Each package will be running jobs with
both the current lxc backend and with incus. Packages that have the same result
on both backends will be migrated over, and packages that exhibit different
results will be investigated further, resulting in bug reports and/or other
communication with the maintainers.
On the frontend side, the code has been ported to Bootstrap 5
over from the now ancient Bootstrap 3. This need has been
originally reported back in 2024
based on the lack of security support for Bootstrap 3. Beyond improving
maintainability, this upgrade also enables support for dark mode in debci,
which is still work in progress.
Both updates mentioned in this section will be available in a following debci
release.
Salsa CI maintenance by Santiago Ruano Rinc n et al.
Santiago reviewed some Salsa CI issues and reviewed associated merge requests.
For example, he investigated a regression (#545),
introduced by the move to sbuild,
on the use of extra repositories configured as .source files; and reviewed the
MR (!712)
that fixes it.
Also, there were conflicts with changes made in debci 3.14
and debci 3.14.1
(those updates are mentioned above), and different people have contributed to
fix the subsequent issues, in a long-term way. This includes Rapha l who
proposed MR !707
and who also suggested Antonio to merge the Salsa CI patches to avoid similar
errors in the future. This happened shortly after.
Those fixes finally required the unrelated MR !709,
which will prevent similar problems when building images.
To identify bugs related to the autopkgtest support in the backport suites as
early as possible, Santiago proposed MR !708.
Finally, Santiago, in collaboration with Emmanuel Arias also had exchanges with
GSoC candidates for the Salsa CI project,
including the contributions they have made as merge requests. It is important to
note that there are several very good candidates interested in participating.
Thanks a lot to them for their work so far!
Miscellaneous contributions
Rapha l reported a zim bug
affecting Debian Unstable users, which was already fixed in git apparently. He
could thus cherry-pick the fix and update the package
in Debian Unstable.
Carles submitted translation errors in the debian-installer Weblate.
Carles, using po-debconf-manager,
improved Catalan translations: reviewed and submitted 3 packages. Also improved
error handling when forking or submitting an MR if the fork already existed.
Carles kept improving check-relations:
code base related general improvements (added strict typing, enabled pre-commit).
Also added DebPorts support, virtual packages support and added commands for
reporting missing relations and importing bugs from bugs.debian.org.
Antonio handled miscellaneous Salsa support requests.
Stefano and Santiago continued to help with DebConf 26 preparations.
Stefano reviewed some contributions to debian-reimbursements and handled admin
for reimbursements.debian.net.
Stefano attended the Debian Technical Committee meeting.
Helmut sent 8 patches for cross build failures.
Building on the work of postmarketOS,
Helmut managed to cross build systemd for musl in rebootstrap and sent several
patches in the process.
Helmut reviewed several MRs of Johannes Schauer Marin Rodrigues expanding
support for DPKG_ROOT to support installing hurd.
Helmut incorporated a final round of feedback for the Multi-Arch documentation
in Debian policy, which finally made it into unstable
together with documentation of Build-Profiles.
In order to fix python-memray, Helmut
NMUed libunwind
generally disabling C++ exception support as being an incompatible duplication
of the gcc implementation. Unfortunately, that ended up breaking suricata on riscv64.
After another NMU,
python-memray finally migrated.
Thorsten uploaded new upstream versions of epson-inkjet-printer-escpr and
sane-airscan. He also fixed a packaging bug in printer-driver-oki. As of
systemd 260.1-1 the configuration of lpadmin has been added to the sysusers.d
configuration. All printing packages can now simply depend on the
systemd-sysusers package and don t have to take care of its creation in
maintainer scripts anymore.
In collaboration with Emmanuel Arias, Santiago had exchanges with GSoC
candidates and reviewed the proposals of the
Linux livepatching GSoC 2026 project.
Colin upgraded tango and pytango to new upstream releases and packaged
pybind11-stubgen (needed for pytango), thanks to a Freexian customer. Tests of
reproducible builds revealed that pybind11-stubgen didn t generate imports in a
stable order; this is now fixed upstream.
Lucas fixed CVE-2025-67733
and CVE-2026-21863
affecting src:valkey in unstable and testing. Also reviewed the same fixes
targeting stable proposed by Peter Wienemann.
Faidon worked with upstream and build-dep Debian maintainers on resolving
blockers in order to bring pyHanko into Debian, starting with the adoption of
python-pyhanko-certvalidator. pyHanko is a suite for signing and stamping PDF
files, and one of the few libraries that can be leveraged to sign PDFs with
eIDAS Qualified Electronic Signatures.
Anupa co-organized MiniDebConf Kanpur
and attended the event with many others from all across India. She handled the
accommodation arrangements along with the registration team members, worked on
the budget and expenses. She was also a speaker at the event.
Lucas helped with content review/schedule for the
MiniDebConf Campinas. Thanks Freexian for
being a Gold sponsor!
Lucas organized and took part in a one-day in-person sprint to work on
Ruby 3.4 transition. It was held in a coworking space in Brasilia - Brazil on
April 6th. There were 5 DDs and they fixed multiple packages FTBFSing against
Ruby 3.4 (coming to unstable soon hopefully). Lucas has been postponing a blog
post about this sprint since then :-)
A maintenance release 0.3.13 of the anytime
package arrived on CRAN today,
sticking with the roughly yearly schedule we have now. Binaries for r2u have been built
already. The package is fairly feature-complete, and code and
functionality remain mature and stable.
anytime
is a very focused package aiming to do just one thing really
well: to convert anything in integer, numeric, character,
factor, ordered, input format to either POSIXct (when called as
anytime) or Date objects (when called as
anydate) and to do so without requiring a format
string as well as accomodating different formats in one input
vector. See the anytime page,
the GitHub repo
for a few examples, the nice pdf
vignette, and the beautiful documentation site
for all documentation.
This release was triggered by a bizarre bug seen on elementary os 8.
For reason anytime was
taking note on startup where it runs, and used a small and simply piece
of code reading /etc/os-release when it exists. We assumed
sane content, but this particular operating system and releases managed
to have a duplicate entry throwing us spanner. So now this code is
robust to duplicates, and no longer executed on each startup but as
needed which is a net improvement. We also switched the vignette to
being deployed by the new Rcpp::asis() driver.
The short list of changes follows.
Changes in anytime
version 0.3.13 (2026-04-14)
Continuous integration has received minor updates
The vignette now use the Rcpp::asis() driver, and
references have been refreshed
Stateful 'where are we running' detection is now more robust, and
has been moved from running on each startup to a cached 'as needed'
case
At last, I can run my own large language model artificial idiocy
generator at home on a Debian testing host using Debian packages
directly from the Debian archive. After months of polishing the
llama.cpp,
whisper.cpp and
ggml packages, and their
dependencies, I was very happy to see today that they all entered
Debian testing this morning. Several release-critical issues in
dependencies have been blocking the migration for the last few weeks,
and now finally the last one of these has been fixed. I would like to
extend a big thanks to everyone involved in making this happen.
I've been running home-build editions of whisper.cpp and llama.cpp
packages for a while now, first building from the upstream Git
repository and later, as the Debian packaging progressed, from the
relevant Salsa Git repositories for the ROCM packages, GGML,
whisper.cpp and llama.cpp. The only snag with the official Debian
packages is that the JavaScript chat client web pages are slightly
broken in my setup, where I use a reverse proxy to make my home server
visible on the public Internet while the included web pages only want
to communicate with localhost / 127.0.0.1. I suspect it might be
simple to fix by making the JavaScript code dynamically look up the
URL of the current page and use that to determine where to find the
API service, but until someone fixes
BTS report #1128381, I
just have to edit
/usr/share/llama.cpp-tools/llama-server/themes/simplechat/simplechat.js
every time I upgrade the package. I start my server like this on my
machine with a nice AMD GPU (donated to me as a Debian developer by
AMD two years ago, thank you very much):
It only takes a few minutes to load the model for the first time
and prepare a nice API server for me at
https://my.reverse.proxy.example.com:8080/v1/, available
(note, this sets up the server up without authentication; use a
reverse proxy with authentication if you need it) for all the API
clients I care to test. I switch models regularly to test different
new ones, the Qwen3-Coder one just happen to be the one I use at the
moment. Perhaps these packages is something for you to have fun with
too?
As usual, if you use Bitcoin and want to show your support of my
activities, please send Bitcoin donations to my address
15oWEoG9dUPovwmUL9KWAnYRtNJEkP1u1b.
I ve been using the Furilabs FLX1s phone [1] as my daily driver for 6 weeks, it s a decent phone, not as good as I hoped but good enough to use every day and rely on for phone calls about job interviews etc. I intend to keep using it as my main phone and as a platform to improve phone software in Debian as you really can t effectively find bugs unless you use the platform for important tasks.
Support Problems
I previously wrote about the phone after I received it without a SIM caddy on the 13th of Jan. I had a saga with support about this, on the 16th of Jan one support person said that they would ship it immediately but didn t provide a tracking number or any indication of when it would arrive. On the 5th of Feb I contacted support again and asked how long it would be, the new support person seemed to have no record of my previous communication but said that they would send it. On the 17th of Feb I made another support request including asking for a way of direct communication as the support email came from an address that wouldn t accept replies, I was asked for a photo showing where the problem is. The support person also said that they might have to send a replacement phone!
The last support request I sent included my disappointment at the time taken to resolve the issue and the proposed solution of replacing the entire phone (why have two international shipments of a fragile and expensive phone when a single letter with a cheap SIM caddy would do?). I didn t receive a reply but the SIM caddy arrived on the 2nd of Mar. Here is a pic of the SIM caddy and the package it came in:
One thing that should be noted is that some of the support people seemed to be very good at their jobs and they were all friendly. It was the system that failed here, turning a minor issue of a missing part into a 6 week saga.
Furilabs needs to do the following to address this issue:
Make it possible to reply directly to a message from a support person. Accept email with a custom subject to sort it, give a URL for a web form, anything. Collating discussions with a customer allows giving better support while taking less time for the support people.
Have someone monitor every social media address that is used by the company. When someone sends a support request in a public Mastodon post it indicates that something has gone wrong and you want to move quickly to resolve it.
Take care of the little things, like sending a tracking number for every parcel. If it s something too small for a parcel (the SIM caddy could have fit in a regular letter) then just tell the customer what date it was posted and where it was posted from so they have some idea of when it will arrive.
This is not just a single failure of Furilabs support, it s a systemic failure of their processes.
Problems I Will Fix Unless Someone Beats Me to it
Here are some issues I plan to work on.
Smart Watch Support
I need to port one of the smart watch programs to Debian. Also I want to make one of them support the Colmi P80 [2].
A smart watch significantly increases the utility of a phone even though IMHO they aren t doing nearly all the things that they could and should do. When we get Debian programs talking to the PineTime it will make a good platform for development of new smart phone and OS features.
Nextcloud
I have ongoing issues of my text Nextcloud installation on a Debian VM not allowing connection from the Linux desktop app (as packaged in Debian) and from the Android client (from f-droid). The desktop client works with a friend s Nextcloud installation on Ubuntu so I may try running it on an Ubuntu VM I run while waiting for the Debian issue to get resolved. There was a bug recently fixed in Nextcloud that appears related so maybe the next release will fix it.
For the moment I ve been running without these features and I call and SMS people from knowing their number or just returning calls. Phone calls generally aren t very useful for me nowadays except when applying for jobs. If I could deal with recruiters and hiring managers via video calls then I would consider just not having a phone number.
Wifi IPv6
Periodically IPv6 support just stops working, I can t ping the gateway. I turn wifi off and on again and it works. This might be an issue with my wifi network configuration. This might be an issue with the way I have configured my IPv6 networking, although that problem doesn t happen with any of my laptops.
Chatty Sorting
Chatty is the program for SMS that is installed by default (part of the phosh/phoc setup), it also does Jabber. Version 0.8.7 is installed which apparently has some Furios modifications and it doesn t properly support sorting SMS/Jabber conversations. Version 0.8.9 from Debian sorts in the same way as most SMS and Jabber programs with the most recent at the top. But the Debian version doesn t support Jabber (only SMS and Matrix). When I went back to the Furilabs version of Chatty it still sorted for a while but then suddenly stopped. Killing Chatty (not just closing the window and reopening it) seems to make it sort the conversations sometimes.
Problems for Others to Fix
Here are the current issues I have starting with the most important.
Important
The following issues seriously reduce the usability of the device.
Hotspot
The Wifi hotspot functionality wasn t working for a few weeks, this Gitlab issue seems to match it [3]. It started working correctly for a day and I was not sure if an update I applied fixed the bug or if it s some sort of race condition that worked for this boot and will return next time I reboot it. Later on I rebooted it and found that it s somewhat random whether it works or now.
Also while it is mostly working it seemed to stop working about every 25 minutes or so and I had to turn it off and on again to get it going.
On another day it went to a stage where it got repeated packet loss when I pinged the phone as a hotspot from my laptop. A pattern of 3 ping responses and 3 Destination Host Unreachable messages was often repeated.
I don t know if this is related to the way Android software is run in a container to access the hardware.
4G Reliability
Sometimes 4G connectivity has just stopped, sometimes I can stop and restart the 4G data through software to fix it and sometimes I need to use the hardware switch. I haven t noticed this for a week or two so there is a possibility that one fix addressed both Hotspot and 4G.
One thing that I will do is setup monitoring to give an alert on the phone if it can t connect to the Internet. I don t want it to just quietly stop doing networking stuff and not tell me!
On-screen Keyboard
The compatibility issues of the GNOME and KDE on-screen keyboards are getting me. I use phosh/phoc as the login environment as I want to stick to defaults at first to not make things any more difficult than they need to be. When I use programs that use QT such as Nheko the keyboard doesn t always appear when it should and it forgets the setting for word completion (which means spelling correction).
The spelling correction system doesn t suggest replacing dont with don t which is really annoying as a major advantage for spelling checkers on touch screens is inserting an apostrophy. An apostrophy takes at least 3* longer than a regular character and saving that delay makes a difference to typing speed.
The spelling correction doesn t correct two words run together.
Medium Priority
These issues are ongoing annoyances.
Delay on Power Button
In the best case scenario this phone has a much slower response to pressing the power button than the Android phones I tested (Huawei Mate 10 Pro and Samsung Galaxy Note 9) and a much slower response than my recollection of the vast majority of Android phones I ve ever used. For testing pressing buttons on the phones simultaneously resulted in the Android phone screens lighting up much sooner. Something like 200ms vs 600ms I don t have a good setup to time these things but it s very obvious when I test.
In a less common case scenario (the phone having been unused for some time) the response can be something like 5 seconds. The worst case scenario is something in excess of 20 seconds.
For UI designers, if you get multiple press events from a button that can turn the screen on/off please make your UI leave the screen on and ignore all the stacked events. Having the screen start turning on and off repeatedly when the phone recovers and processes all the button presses isn t good, especially when each screen flash takes half a second.
Notifications
Touching on a notification for a program often doesn t bring it to the foreground. I haven t yet found a connection between when it does and when it doesn t.
Also the lack of icons in the top bar on the screen to indicate notifications is annoying, but that seems to be an issue of design not the implementation.
Charge Delay
When I connect the phone to a power source there is a delay of about 22 seconds before it starts to charge. Having it miss 22 seconds of charge time is no big deal, having to wait 22 seconds to be sure it s charging before leaving it is really annoying. Also the phone makes an audible alert when it gets to 0% charge which woke me up one night when I had failed to push the USB-C connector in hard enough. This phone requires a slightly deeper connector than most phones so with some plugs it s easy to not quite insert them far enough.
Torch aka Flash
The light for the torch or flash for camera is not bright at all. In a quick test staring into the light from 40cm away wasn t unpleasant compared to my Huawei Mate 10 Pro which has a light bright enough that it hurts to look at it from 4 meters away.
Because of this photos at night are not viable, not even when photographing something that s less than a meter away.
The torch has a brightness setting which doesn t seem to change the brightness, so it seems likely that this is a software issue and the brightness is set at a low level and the software isn t changing it.
Audio
When I connect to my car the Lollypop player starts playing before the phone directs audio to the car, so the music starts coming from the phone for about a second. This is an annoying cosmetic error. Sometimes audio playing pauses for no apparent reason.
It doesn t support the phone profile with Bluetooth so phone calls can t go through the car audio system. Also it doesn t always connect to my car when I start driving, sometimes I need to disable and enable Bluetooth to make it connect.
When I initially set the phone up Lollypop would send the track name when playing music through my car (Nissan LEAF) Bluetooth connection, after an update that often doesn t happen so the car doesn t display the track name or whether the music is playing but the pause icon works to pause and resume music (sometimes it does work).
About 30 seconds into a phone call it switches to hands-free mode while the icon to indicate hands-free is not highlighted, so I have to press the hands-free button twice to get it back to normal phone mode.
Low Priority
I could live with these things remaining as-is but it s annoying.
Ticket Mode
There is apparently some code written to display tickets on screen without unlocking. I want to get this working and store screen-caps of the Android barcode screens of the different loyalty cards so I can scan them without unlocking. My threat model does not include someone trying to steal my phone to get a free loaf of bread on the bakery loyalty program.
Camera
The camera app works with both the back and front cameras, which is nice, and sadly based on my experience with other Debian phones it s noteworthy. The problem is that it takes a long time to take a photo, something like a second after the button is pressed long enough for you to think that it just silently took a photo and then move the phone.
The UI of the furios-camera app is also a little annoying, when viewing photos there is an icon at the bottom left of the screen for a video camera and an icon at the bottom right with a cross. Which every time makes me think record videos and leave this screen not return to taking photos and delete current photo . I can get used to the surprising icons, but being so slow is a real problem.
GUI App Installation
The program for managing software doesn t work very well. It said that there were two updates for Mesa package needed, but didn t seem to want to install them. I ran flatpak update as root to fix that. The process of selecting software defaults to including non-free, and most of the available apps are for desktop/laptop with no way to search for phone/tablet apps.
Generally I think it s best to just avoid this and use apt and flatpak directly from the command-line. Being able to ssh to my phone from a desktop or laptop is good!
Android Emulation
The file /home/furios/.local/share/andromeda/data/system/uiderrors.txt is created by the Andromeda system which runs Android apps in a LXC container and appears to grow without end. After using the phone for a month it was 3.5G in size. The disk space usage isn t directly a problem, out of the 110G storage space only 17G is used and I don t have a need to put much else on it, even if I wanted to put backups of /home from my laptop on it when travelling that would still leave plenty of free space. But that sort of thing is a problem for backing up the phone and wasting 3.5G out of 110G total is a fairly significant step towards breaking the entire system.
Also having lots of logging messages from a subsystem that isn t even being used is a bad sign.
I just tried using it and it doesn t start from either the settings menu or from the f-droid icon. Android isn t that important to me as I want to get away from the proprietary app space so I won t bother trying this any more.
Unfixable Problems
Unlocking
After getting used to fingerprint unlocking going back to a password is a pain. I think that the hardware isn t sufficient for modern quality face recognition that can t be fooled by a photo and there isn t fingerprint hardware.
When I first used an Android phone using a pin to unlock didn t seem like a big deal, but after getting used to fingerprint unlock it s a real drag to go without. This is a real annoyance when doing things like checking Wikipedia while watching TV.
This phone would be significantly improved with a fingerprint sensor or a camera that worked well enough for face unlock.
Plasma Mobile
According to Reddit Plasma Mobile (KDE for phones) doesn t support Halium and can never work on this phone because of it [4]. This is one of a number of potential issues with the phone, running on hardware that was never designed for open OSs is always going to have issues.
Wifi MAC Address
The MAC keeps changing on reboot so I can t assign a permanent IPv4 address to the phone. It appears from the MAC prefix of 00:08:22 that the network hardware is made in InPro Comm which is well known for using random addresses in the products it OEMs. They apparently have one allocation of 2^24 addresses and each device randomly chooses a MAC from that range on boot.
In the settings for a Wifi connection the Identity tab has a field named Cloned Address which can be set to Stable for SSID that prevents it from changing and allows a static IP address allocation from DHCP. It s not ideal but it works.
Network Manager can be configured to have a permanent assigned MAC address for all connections or for just some connections. In the past for such things I have copied MAC addresses from ethernet devices that were being discarded and used them for such things. For the moment the Stable for SSID setting does what I need but I will consider setting a permanent address at some future time.
Docks
Having the ability to connect to a dock is really handy. The PinePhonePro and Librem5 support it and on the proprietary side a lot of Samsung devices do it with a special desktop GUI named Dex and some Huawei devices also have a desktop version of the GUI. It s unfortunate that this phone can t do it.
The Good Things
It s good to be able to ssh in to my phone, even if the on-screen keyboard worked as well as the Android ones it would still be a major pain to use when compared to a real keyboard. The phone doesn t support connecting to a dock (unlike Samsung phones I ve used for which I found Dex to be very useful with a 4K monitor and proper keyboard) so ssh is the best way to access it.
This phone has very reliable connections to my home wifi. I ve had ssh sessions from my desktop to my phone that have remained open for multiple days. I don t really need this, I ve just forgotten to logout and noticed days later that the connection is still running. None of the other phones running Debian could do that.
Running the same OS on desktop and phone makes things easier to test and debug.
Having support for all the things that Linux distributions support is good. For example none of the Android music players support all the encodings of audio that comes from YouTube so to play all of my music collection on Android I would need to transcode most of them which means either losing quality, wasting storage space, or both. While Lollypop plays FLAC0, mp3, m4a, mka, webm, ogg, and more.
Conclusion
This is a step towards where I want to go but it s far from the end goal.
The PinePhonePro and Librem5 are more open hardware platforms which have some significant benefits. But the battery life issues make them unusable for me.
Running Mobian on a OnePlus 6 or Droidian on a Note 9 works well for the small tablet features but without VoLTE. While the telcos have blocked phones without VoLTE data devices still work so if recruiters etc would stop requiring phone calls then I could make one of them an option.
The phone works well enough that it could potentially be used by one of my older relatives. If I could ssh in to my parents phones when they mess things up that would be convenient.
I ve run this phone as my daily driver since the 3rd of March and it has worked reasonably well. 6 weeks compared to my previous use of the PinePhonePro for 3 days. This is the first time in 15 years that a non-Android phone has worked for me personally. I have briefly used an iPhone 7 for work which basically did what it needed to do, it was at the bottom of the pile of unused phones at work and I didn t want to take a newer iPhone that could be used by someone who s doing more than the occasional SMS or Slack message.
So this is better than it might have been, not as good as I hoped, but a decent platform to use it while developing for it.
The twentyfourth release of littler as a
CRAN package
landed on CRAN just now, following in the now twenty-one year history
(!!) as a (initially non-CRAN) package started by Jeff in 2006, and joined
by me a few weeks later.
littler
is the first command-line interface for R as it predates
Rscript. It allows for piping as well for shebang
scripting via #!, uses command-line arguments more
consistently and still starts
faster. It also always loaded the methods package which
Rscript only began to do in later years.
littler
lives on Linux and Unix, has its difficulties on macOS due to
some-braindeadedness there (who ever thought case-insensitive
filesystems as a default were a good idea?) and simply does not exist on
Windows (yet the build system could be extended see RInside for
an existence proof, and volunteers are welcome!). See the FAQ
vignette on how to add it to your PATH. A few examples
are highlighted at the Github repo:, as well
as in the examples
vignette.
This release, which comes just two months after the previous 0.3.22
release that brought a few new features, is mostly internal. (The
previous release erroneously had 0.3.23 in its blog and social media
posts, it really was 0.3.22 and this one now is is 0.3.23.) Mattias
Ellert address a nag (when building for a distribution) about one
example file with a shebang not have excutable modes. I accommodated the
ever-changing interface the C API of R (within about twelve hours of
being notified). A few other smaller changes were made as well polishing
a script or two or usual, see below for more.
The full change description follows.
Changes in littler
version 0.3.23 (2026-04-12)
Changes in examples scripts
Correct spelling in installGithub.r to lower-case
h
The r2u.r now recognises resolute aka
26.06
installRub.r can install (more easily) from
r-multiverse
A file permission was corrected (Mattias Ellert in #131)
Changes in package
Update script count and examples in README.md
Continuous intgegration scripts received minor updates
The C level access to the R API was updated to reflect most
recent standards (Dirk in #132)
My CRANberries
service provides a comparison to the
previous release. Full details for the littler
release are provided as usual at the ChangeLog
page, and also on the package docs website.
The code is available via the GitHub repo, from
tarballs and now of course also from its CRAN page and
via install.packages("littler"). Binary packages are
available directly in Debian as
well as (in a day or two) Ubuntu binaries at
CRAN thanks to the tireless Michael Rutter. Comments and suggestions
are welcome at the GitHub repo.
My Debian contributions this month were all sponsored by Freexian.
You can also support my work directly via Liberapay or GitHub Sponsors.
OpenSSH
I fixed CVE-2026-3497 in unstable, thanks to a fix in Ubuntu by Marc Deslauriers. Relatedly, I applied an Ubuntu patch by Athos Ribeiro to not default to weak GSS-API exchange algorithms.
I m looking forward to being able to split out GSS-API key exchange support in OpenSSH once Ubuntu 26.04 LTS has been released! This stuff will still be my problem, but at least it won t be in packages that nearly everyone has installed.
Python packaging
New upstream versions:
dill
django-modeltranslation
isort
langtable
pathos
pendulum
pox
ppft
pydantic-extra-types
pytango
python-asyncssh
python-datamodel-code-generator
python-evalidate
python-packaging (including fixes for python-hatch-requirements-txt and python-pyproject-examples)
python-zxcvbn-rs-py
rpds-py
smart-open
trove-classifiers
I packaged pybind11-stubgen, needed for new upstream versions of pytango. Tests of reproducible builds revealed that it didn t generate imports in a stable order; I contributed a fix for that upstream.
I worked with the security team to release DSA-6161-1 in multipart, fixing CVE-2026-28356 (upstream discussion). (Most of the work for this was in February, but the vulnerability was still embargoed when I published my last monthly update.)
In trixie-backports, I updated pytest-django to 4.12.0.
I fixed a number of packages to support building with pyo3 0.28:
Review: The Teller of Small Fortunes, by Julie Leong
Publisher:
Ace
Copyright:
November 2024
ISBN:
0-593-81590-4
Format:
Kindle
Pages:
324
The Teller of Small Fortunes is a cozy found-family fantasy with a
roughly medieval setting. It was Julie Leong's first novel.
Tao is a traveling teller of small fortunes. In her wagon, pulled by her
friendly mule Laohu, she wanders the small villages of Eshtera and reads
the trivial fortunes of villagers in the tea leaves. An upcoming injury, a
lost ring, a future kiss, a small business deal... she looks around the
large lines of fate and finds the small threads. After a few days, she
moves on, making her solitary way to another village.
Tao is not originally from Eshtera. She is Shinn, which means she
encounters a bit of suspicion and hostility mixed with the fascination of
the exotic. (Language and culture clues lead me to think Shinara is
intended to be this world's not-China, but it's not a direct mapping.) Tao
uses the fascination to help her business; fortune telling is more
believable from someone who seems exotic. The hostility she's learned to
deflect and ignore. In the worst case, there's always another village.
If you've read any cozy found-family novels, you know roughly what happens
next. Tao encounters people on the road and, for various reasons, they
decide to travel together. The first two are a massive mercenary (Mash)
and a semi-reformed thief (Silt), who join Tao somewhat awkwardly after
Tao gives Mash a fortune that is far more significant than she intended.
One town later, they pick up an apprentice baker best known for her
misshapen pastries. They also collect a stray cat, because of course they
do. It's that sort of book.
For me, this sort of novel lives or dies by the characters, so it's good
news that I liked Tao and enjoyed spending time with her. She's quiet,
resilient, competent, and self-contained, with a difficult past and some
mysteries and emotions the others can draw over time. She's also
thoughtful and introspective, which means the tight third-person narration
that almost always stays on Tao offers emotional growth to mull over. I
also liked Kina (the baker) and Mash; they're a bit more obvious and
straightforward, but Kina adds irrepressible energy and Mash is a good
example of the sometimes-gruff soldier with a soft heart. Silt was a bit
more annoying and I never entirely warmed to him, but he's tolerable and
does get a bit of much-needed (if superficial) character development.
It takes some time for the reader to learn about the primary conflict of
the story (Tao does not give up her secrets quickly), so I won't spoil it,
but I thought it worked well. I was momentarily afraid the story would
develop a clear villain, but Leong has some satisfying alternate surprises
in store. The ending was well-done, although it is very happily-ever-after
in a way that may strike some readers as too neat. The Teller of
Small Fortunes aims for a quiet and relaxed mood rather than forcing
character development through difficult choices; it's a fine aim for a
novel, but it won't match everyone's mood.
I liked the world-building, although expect small and somewhat
disconnected details rather than an overarching theory of magic. Tao's
ability gets the most elaboration, for obvious reasons, and I liked how
Leong describes it and explores its consequences. Most of the attention in
the setting is on the friction, wistfulness, and small reminders of coming
from a different culture than everyone around you, but so long ago that
you are not fully a part of either world. This, I thought, was very
well-done and is one of the places where the story is comfortable with
complex feelings and doesn't try to reach a simplifying conclusion.
There is one bit of the story that felt like it was taken directly out of
a Dungeons & Dragons campaign to a degree that felt jarring, but
that was the only odd world-building note.
This book felt like a warm cup of tea intended to comfort and relax,
without large or complex thoughts about the world. It's not intended to be
challenging; there are a few plot twists I didn't anticipate, but nothing
that dramatic, and I doubt anyone will be surprised by the conclusions it
reaches. It's a pleasant time with some nice people and just enough
tension and mystery to add some motivation to find out what happens next.
If that's what you're in the mood for, recommended. If you want a book
that has Things To Say or will put you on the edge of your seat, maybe
save this one for another mood.
All the on-line sources I found for this book call it a standalone, but
The Keeper of Magical Things is set in the same world, so I would
call it a loose series with different protagonists. The Teller of
Small Fortunes is a complete story in one book, though.
Rating: 7 out of 10
Welcome to the March 2026 report from the Reproducible Builds project!
These reports outline what we ve been up to over the past month, highlighting items of news from elsewhere in the increasingly-important area of software supply-chain security. As ever, if you are interested in contributing to the Reproducible Builds project, please see the Contribute page on our website.
Linux kernel hash-based integrity checking proposed
Eric Biggers posted to the Linux Kernel Mailing List in response to a patch series posted by Thomas Wei schuh to introduce a calculated hash-based system of integrity checking to complement the existing signature-based approach. Thomas original post mentions:
The current signature-based module integrity checking has some drawbacks in combination with reproducible builds. Either the module signing key is generated at build time, which makes the build unreproducible, or a static signing key is used, which precludes rebuilds by third parties and makes the whole build and packaging process much more complicated.
I think this actually undersells the feature. It s also much simpler than the signature-based module authentication. The latter relies on PKCS#7, X.509, ASN.1, OID registry, crypto_sig API, etc in addition to the implementations of the actual signature algorithm (RSA / ECDSA / ML-DSA) and at least one hash algorithm.
Distribution work
In Debian this month,
Lucas Nussbaum announced Debaudit, a new service to verify the reproducibility of Debian source packages :
debaudit complements the work of the Reproducible Builds project. While reproduce.debian.net focuses on ensuring that binary packages can be bit-for-bit reproduced from their source packages, debaudit focuses on the preceding step: ensuring that the source package itself is a faithful and reproducible representation of its upstream source or Vcs-Git repository.
Lastly, Bernhard M. Wiedemann posted another openSUSEmonthly update for their work there.
Tool development
diffoscope is our in-depth and content-aware diff utility that can locate and diagnose reproducibility issues. This month, Chris Lamb made a number of changes, including preparing and uploading versions, 314 and 315 to Debian.
Chris Lamb:
Don t run test_code_is_black_clean test in the autopkgtests. (#1130402). []
Adjust the PGP file detection regular expression. []
Michael R. Crusoe:
Reformat the source code using Black version 26.1.0 [][]
In addition, Vagrant Cascadian updated diffoscope in GNU Guix to version 315.
rebuilderd, our server designed monitor the official package repositories of Linux distributions and attempt to reproduce the observed results there; it powers, amongst other things, reproduce.debian.net.
A new version, 0.26.0, was released this month, with the following improvements:
Much smoother onboarding/installation.
Complete database redesign with many improvements.
New REST HTTP API.
It s now possible to artificially delay the first reproduce attempt. This gives archive infrastructure more time to catch up.
Upstream patches
The Reproducible Builds project detects, dissects and attempts to fix as many currently-unreproducible packages as possible. We endeavour to send all of our patches upstream where appropriate. This month, we wrote a large number of such patches, including:
Two new academic papers
Marc Ohm, Timo Pohl, Ben Swierzy and Michael Meier published a paper on the threat of cache poisoning in the Python ecosystem:
Attacks on software supply chains are on the rise, and attackers are becoming increasingly creative in how they inject malicious code into software components.
This paper is the first to investigate Python cache poisoning, which manipulates bytecode cache files to execute malicious code without altering the human-readable source code.
We demonstrate a proof of concept, showing that an attacker can inject malicious bytecode into a cache file without failing the Python interpreter s integrity checks.
In a large-scale analysis of the Python Package Index, we find that about 12,500 packages are distributed with cache files.
Through manual investigation of cache files that cannot be reproduced automatically from the corresponding source files, we identify classes of reasons for irreproducibility to locate malicious cache files.
While we did not identify any malware leveraging this attack vector, we demonstrate that several widespread package managers are vulnerable to such attacks.
A PDF of the paper is available online.
Mario Lins of the University of Linz, Austria, has published their PhD doctoral thesis on the topic of Software supply chain transparency:
We begin by examining threats to the software distribution stage the point at which artifacts (e.g., mobile apps) are delivered to end users with an emphasis on mobile ecosystems [and] we next focus on the operating system on mobile devices, with an emphasis on mitigating bootloader-targeted attacks. We demonstrate how to compensate lost security guarantees on devices with an unlocked bootloader. This allows users to flash custom operating systems on devices that no longer receive security updates from the original manufacturer without compromising security. We then move to the source code stage. [Also,] we introduce a new architecture to ensure strong source-to-binary correspondence by leveraging the security guarantees of Confidential Computing technology. Finally, we present The Supply Chain Game, an organizational security approach that enhances standard risk-management methods. We demonstrate how game-theoretic techniques, combined with common risk management practices, can derive new criteria to better support decision makers.
A PDF of the paper is available online.
Holger Levsen announced that this year s Reproducible Builds summit will almost certainly be held in Gothenburg, Sweden, from September 22 until 24, followed by two days of hacking. However, these dates are preliminary and not 100% final an official announcement is forthcoming.
Mark Wielaard posted to our list asking a question on the difference between debugedit and relative debug paths based on a comment on the Build path page: Have people tried more modern versions of debugedit to get deterministic (absolute) DWARF paths and found issues with it?
Finally, if you are interested in contributing to the Reproducible Builds project, please visit our Contribute page on our website. However, you can get in touch with us via:
A colleague asked me if we should move all our money to our pillow cases after
reading the latest AI editorial from Thomas
Friedman.
The article reads like a press release from Anthropic, repeating the claim that
their latest AI model is so good at finding software vulnerabilities that it is
a danger to the world.
I think I now know what it s like to be a doctor who is forced to watch Gray s
Anatomy.
By now every journalist should be able to recognize the AI publicity playbook:
Step 1: Start with a wildly unsubstantiated claim about how dangerous your
product is:
AI will cause human extinction before we have a chance to colonize mars
(remember that one? Even Kim Stanley Robinson, author of perhaps the most
compelling science fiction on colonizing mars calls bull
shit
on it).
AI will eliminate all of our jobs (this one was extremely effective at
providing cover for software companies laying off staff but it has quickly
dawned on people that the companies that did this are living in chaos not
humming along happily with functional robots)
AI will discover massive software vulnerabilities allowing bad actors to hack
pretty much every major software system in the world . (Did Friedman pull that
directly from Anthropic s press release or was that his contribution?)
Step 2: To help stave off human collapse, only release the new version to a
vetted group of software companies and developers, preferably ones with big
social media followings
Step 3: Wait for the limited release developers to spew unbridled
enthusiasm and shocking examples that seem to suggest this new AI produce is
truly unbelievable
Step 4: Watch stock prices and valuations soar
Step 5: Release to the world, and experience a steady stream of mockery as
people discover how wrong you are
Step 6: Start over
Even if Friedman missed the text book example of the playbook, I have to ask:
if you think bad actors compromising software resulting in massive loss of
private data, major outages and wasted resources needs to be reported on, then
where have you been for the last 10 years? This literally happens on a daily
basis due to the
fundamentally flawed way capitalism has been writing software even before the
invention of AI. A small part of me wonders - maybe AI writing software is not
so bad, because how could it be any worse than it is now?
Also, let s keep in mind that AI s super ability at finding vulnerable software
depends on having access to the software s source code, which most companies
keep locked up tight. That means the owners of the software can use AI to find
vulnerabilities and fix them but bad actors can t.
Oh, but wait, what if a company is so incompetent that they accidentally
release their proprietary software to the
Internet?
Surely that would allow AI bots to discover their vulnerabilities and destroy
the company right? I m not sure if anyone has discovered world ending
vulnerabilities in Anthropic s Claude code since it was accidentally released,
but it is fun to watch people mock
software that is clearly
written by AI (and spoiler alert, it seems way worse that software written
now).
Well we probably should all be keeping our money in a pillow case anyway.
The Upgrade I Didn't Have to Make
My teammate Steve Zarkos, who previously worked on upgrading OpenSSL in Amazon
Linux from 3.0 to 3.2, spent the last few months on the complex task of bumping
OpenSSL again, this time to 3.5. A bump like this only happens after extensive
code analysis and testing, something that I didn't foresee happening when
AL2023 was released but that was a notable request from users.
Having enabled HTTP/3 on
Debian, I was
always keeping an eye on when I would get to do the same for Amazon Linux (mind
you, I work at AWS, in the Amazon Linux org). The bump to OpenSSL 3.5 was the
perfect opportunity to do that, for the first time Amazon Linux is shipping an
OpenSSL version that is supported by ngtcp2 for HTTP/3 support.
Non-Intrusive Change
In order to avoid any intrusive changes to existing users of AL2023, I've only
enabled HTTP/3 in the full build of curl, not in the minimal one, this means
there is no change for the minimal images.
The way curl handles HTTP/3 today also does not lead to any behavior changes
for those who have the full variants of curl installed, this is due to the fact
that HTTP/3 is only used if the user explicitly asks for it with the flags
--http3 or --http3-only.
Side Quests
Supporting HTTP/3 on curl also requires building it with ngtcp2 and nghttp3,
two packages which were not shipped in Amazon Linux, besides, my team doesn't
even own the curl package, we are a security team so our packages are the
security related stuff such as OpenSSL and GnuTLS. Our main focus is the
services behind Amazon Linux's vulnerability handling, not package maintenance.
I worked with the owners of the curl package and got approvals on a plan to
introduce the two new dependencies under their ownership and to enable the
feature on curl, I appreciate their responsiveness.
Amazon Linux 2023 is forked from Fedora, so while introducing ngtcp2, I also
sent a couple of Pull Requests upstream to keep things in sync:
[ngtcp2] package latest release 1.21.0[ngtcp2] do not skip tests
While building the curl package in Amazon Linux, I've noticed the build was
taking 1 hour from start to end, and the culprit was something well known to
me; tests.
The curl test suite is quite extensive, with more than 1600 tests, all of that
running without parallelization, running two times for each build of the
package; once for the minimal build and again for the full build.
I had previously enabled parallel tests in Debian back in 2024 but never got
around to submit the same improvements to Amazon Linux or Fedora, this is now
fixed. The build times for Amazon Linux came down to 10 minutes under the same
host (previously 1 hour), and Fedora promptly merged my PR to do the same
there:
[curl] run tests in parallel
All of this uncovered a test which is timing-dependent, meaning it's not
supposed to be run with high levels of parallelism, so there goes another PR,
this time to curl:
Flag test 766 as timing-dependent#21155
What started as enabling a single feature turned into improvements that landed
in curl, Fedora, and Amazon Linux alike. I did this in a mix of work and
volunteer time, mostly during work hours (work email address used when this was
the case), but I'm glad I put in the extra time for the sake of improving curl
for everyone.
Discovery
Legacy cloud templates often lack the partitioning and bootloader
binaries required for UEFI Secure Boot. Attempting to switch such a VM
to OVMF in Proxmox results in not a bootable disk. We discovered that
a surgical promotion is possible by manipulating the block device and
EFI variables from the hypervisor.
The Problem
Protective MBR Flags: Legacy installers often set
the pmbr_boot flag on the GPT s protective MBR. Strict UEFI
implementations (OVMF) will ignore the GPT if this flag is present.
Missing ESP: Cloud images often lack a FAT32 EFI
System Partition (ESP).
Variable Store: A fresh Proxmox efidisk0 is empty and lacks both the trust certificates
(PK/KEK/db) and the BootOrder entries required for an automated
boot.
The Promotion Rule
To upgrade a SeaBIOS VM to Secure Boot without a full OS reinstall:
1. Surgical Partitioning: Map the disk on the host and
add a FAT32 partition (Type EF00). Clear the pmbr_boot flag from the MBR. 2. Binary
Preparation: Boot the VM in SeaBIOS mode to install shim and grub-efi packages. Use grub2-mkconfig to populate the new ESP. 3. Trust
Injection: Use the virt-fw-vars utility on the
hypervisor to programmatically enroll the Red Hat/Microsoft CA keys and
any custom certificates (e.g., FreeIPA CA) into the VM s efidisk. 4. Boot Pinning: Explicitly set
the UEFI BootOrder to point to the shimx64.efi
path via virt-fw-vars --append-boot-filepath.
Solution (Example Command
Sequence)
On the Proxmox Host (root):
# Map and Clean MBRDEV=$(rbd map pool/disk)parted-s$DEV disk_set pmbr_boot off# Inject Trust and Boot Path (VM must be stopped)virt-fw-vars--inplace /dev/rbd/mapped_efidisk \--enroll-redhat\--add-db<GUID> /path/to/ipa-ca.crt \--append-boot-filepath'\EFI\centos\shimx64.efi'\--sb
This workflow enables high-integrity Secure Boot environments using
existing SeaBIOS infrastructure templates.
Code Blue Emergency (annoying em-dash in original title) is the
seventh book of James White's Sector General science fiction series about
a vast multi-species hospital station. While there are some references to
(and spoilers for) earlier books in the series, you don't have to remember
the previous books to read this one. I had no trouble despite a nine-year
gap.
I read this as part of the Orb General Practice omnibus, which
collects this novel and The Genocidal Healer.
Cha Thrat is a Sommaradvan warrior-surgeon, member of a newly-discovered
species that is beginning the process of contact with the Federation. She
saved a Monitor corps human after an accident on her world, performing
some some highly competent surgery on a species she had never seen before.
That plus her somewhat outcast status on her own world due to her very
traditional attitude towards medical ethics led Sector General to extend
an offer of medical internship, and led her to leap into the unknown by
accepting. This may have been a mistake; there is a great deal that Sector
General does not understand about Sommaradvan medical ethics.
This series entry is another proper (if somewhat episodic) novel and the
first book of the series that doesn't primarily focus on Conway. He makes
an appearance in his new role as Diagnostician, but only as a supporting
character. Code Blue Emergency is told in the tight third-person
perspective of Cha Thrat, an alien who finds many things about Sector
General baffling, confusing, and ethically troubling (and who therefore
provides a good reader surrogate for reintroducing the basics of how the
hospital works).
Using an alien viewpoint is a more sophisticated narrative technique than
White has used previously. I'm glad he tried it, and it mostly works,
although I have some complaints. Cha Thrat comes from the middle caste of
a strictly hierarchical society of three castes, but is also immensely
stubborn and used to a medical system in which doctors take sole
responsibility for their patients. This creates a lot of cultural
conflicts, and I do enjoy science fiction where the human attitudes are
portrayed as the strange ones, but the cultural analysis offered by this
novel is not very deep.
The pattern of this book is for Cha Thrat to stumble into a successful
approach to a problem while being either oblivious to or hostile to the
normal hierarchical structure expected of medical trainees. This is
believable as far as it goes. She is a skilled and intelligent doctor with
some good instincts and a strong commitment to patient care, but is also
culturally inclined to not ask for help. It makes sense for that to be a
serious problem in a hospital. Unfortunately, no one says this directly.
Sector General staff get quite upset in ways that seem more territorial
than oriented towards patient safety, no one directly explains to Cha
Thrat why following a process is important or shows examples of what could
go wrong, and plot armor means that her mistakes usually have positive
outcomes. One can extrapolate the reasons why she is not a good medical
student, but the reader is forced to do the extrapolation.
This is the sort of book where the narration makes clear there are
unresolved cultural clashes that are going to cause problems but hides the
details. To Cha Thrat, her perspective is so obvious she never bothers to
explain it to the reader, so the specifics come as a surprise. As with the
alien perspective, I've seen this technique used with more subtlety and
sophistication in other books, but White's version mostly works. Cha Thrat
is a sympathetic protagonist because she is truly trying to take the most
ethical and empathetic action in every situation and is clearly competent.
Most of my frustration as a reader, ironically, lands on the other Sector
General doctors who seem to make little to no effort to understand her
perspective when she fails to conform to their expectations. This is
believable in the abstract, but the whole point of Sector General is that
they're supposed to be wiser about interspecies difference than this.
Also, sometimes their reactions just seem petty. Cha Thrat has a very
hierarchical concept of medicine that matches the social classes of her
culture. For her, the highest tier of doctor are wizards who treat rulers,
because the work of rulers is mostly mental and intellectual and therefore
the diseases of rulers are treated with magic spells performed with words
to reshape their thinking rather than surgery on their bodies. O'Mara and
the other Sector General psychologists take great offense at this,
muttering about being called witch doctors, which I found completely
absurd. This is a comprehensible, if odd, description of psychology from a
wholly alien species. Surely one's first reaction should be that words
like "wizard" or "magic" are translation errors. Don't get offended; look
to see if the underlying substance matches, which it clearly does.
Apart from cultural and psychological clashes, Code Blue Emergency
has the standard episodic Sector General structure of interesting medical
mysteries that require lateral thinking. I find this sort of puzzle story
satisfying, particularly given the firm belief of every character in an
essentially pacifist and empathetic approach to even the most alien of
creatures. This determined non-violence is one of the more interesting
things about this series, and it continues here.
White does tend towards both biological and gender essentialism for
everyone other than the protagonist and main supporting characters, but he
seemed to be walking back some of the more outrageous limitations on women
that appeared in previous books. There is still some nonsense in here
about how females of any species can't be Diagnosticians, but then Cha
Thrat, who is female, seems to violate the justification for that rule
over the course of this novel (sadly without comment). Perhaps he's
setting up for proving Sector General wrong about this prejudice.
I picked this up after reading Elizabeth Bear's Machine, which is essentially a (better written) Sector General
novel that got me in the mood for reading more. I wouldn't give Code
Blue Emergency any awards, but it delivered exactly what I was looking
for. This series is not as deep or well-written as some more recent SF,
but it is reliably itself and reliably entertaining. There are worse
things in a series. Recommended if you're in the mood for alien ER
in space.
The omnibus edition that I read has an introduction to both novels by John
Clute. It does add some interesting insights, but (as is somewhat typical
for Clute) it also spoils parts of both books. You may want to read it
after you read the novels.
Followed by The Genocidal Healer.
Rating: 7 out of 10
 Using CSS
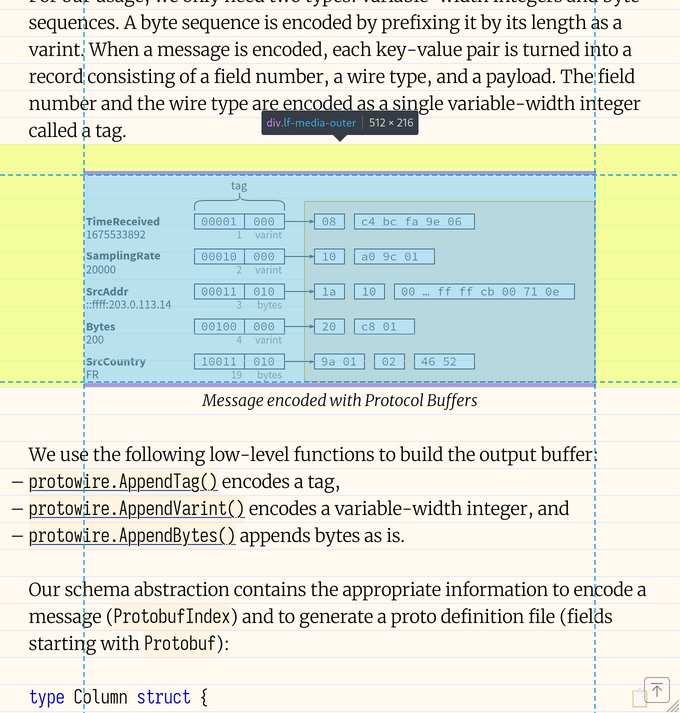 The image is snapped to the grid thanks to the additional padding computed with JavaScript. 216 is divisible by 27, our line height in this example.
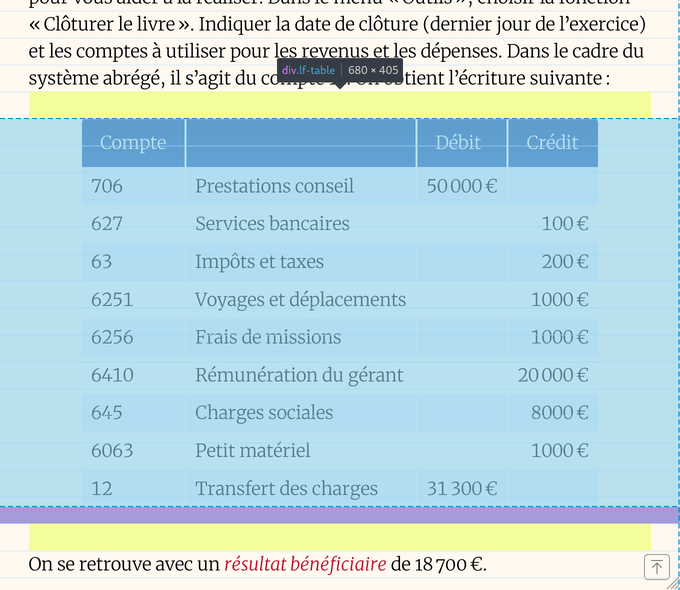 One line out of five is aligned to the grid. Additional padding is added after the table to not break the vertical rhythm. 405 is divisible by 27, our line height in this example.


 I recently released version 0.3.0 of my recipe manager application Kookbook find it in git in
 At some point I should do a 10 recipe example collection, but my personal collection is in danish, so I m not sure it is going to be useful. Unless someone will donate me some handfuls of pre-formatted recipes, I will happily announce it.


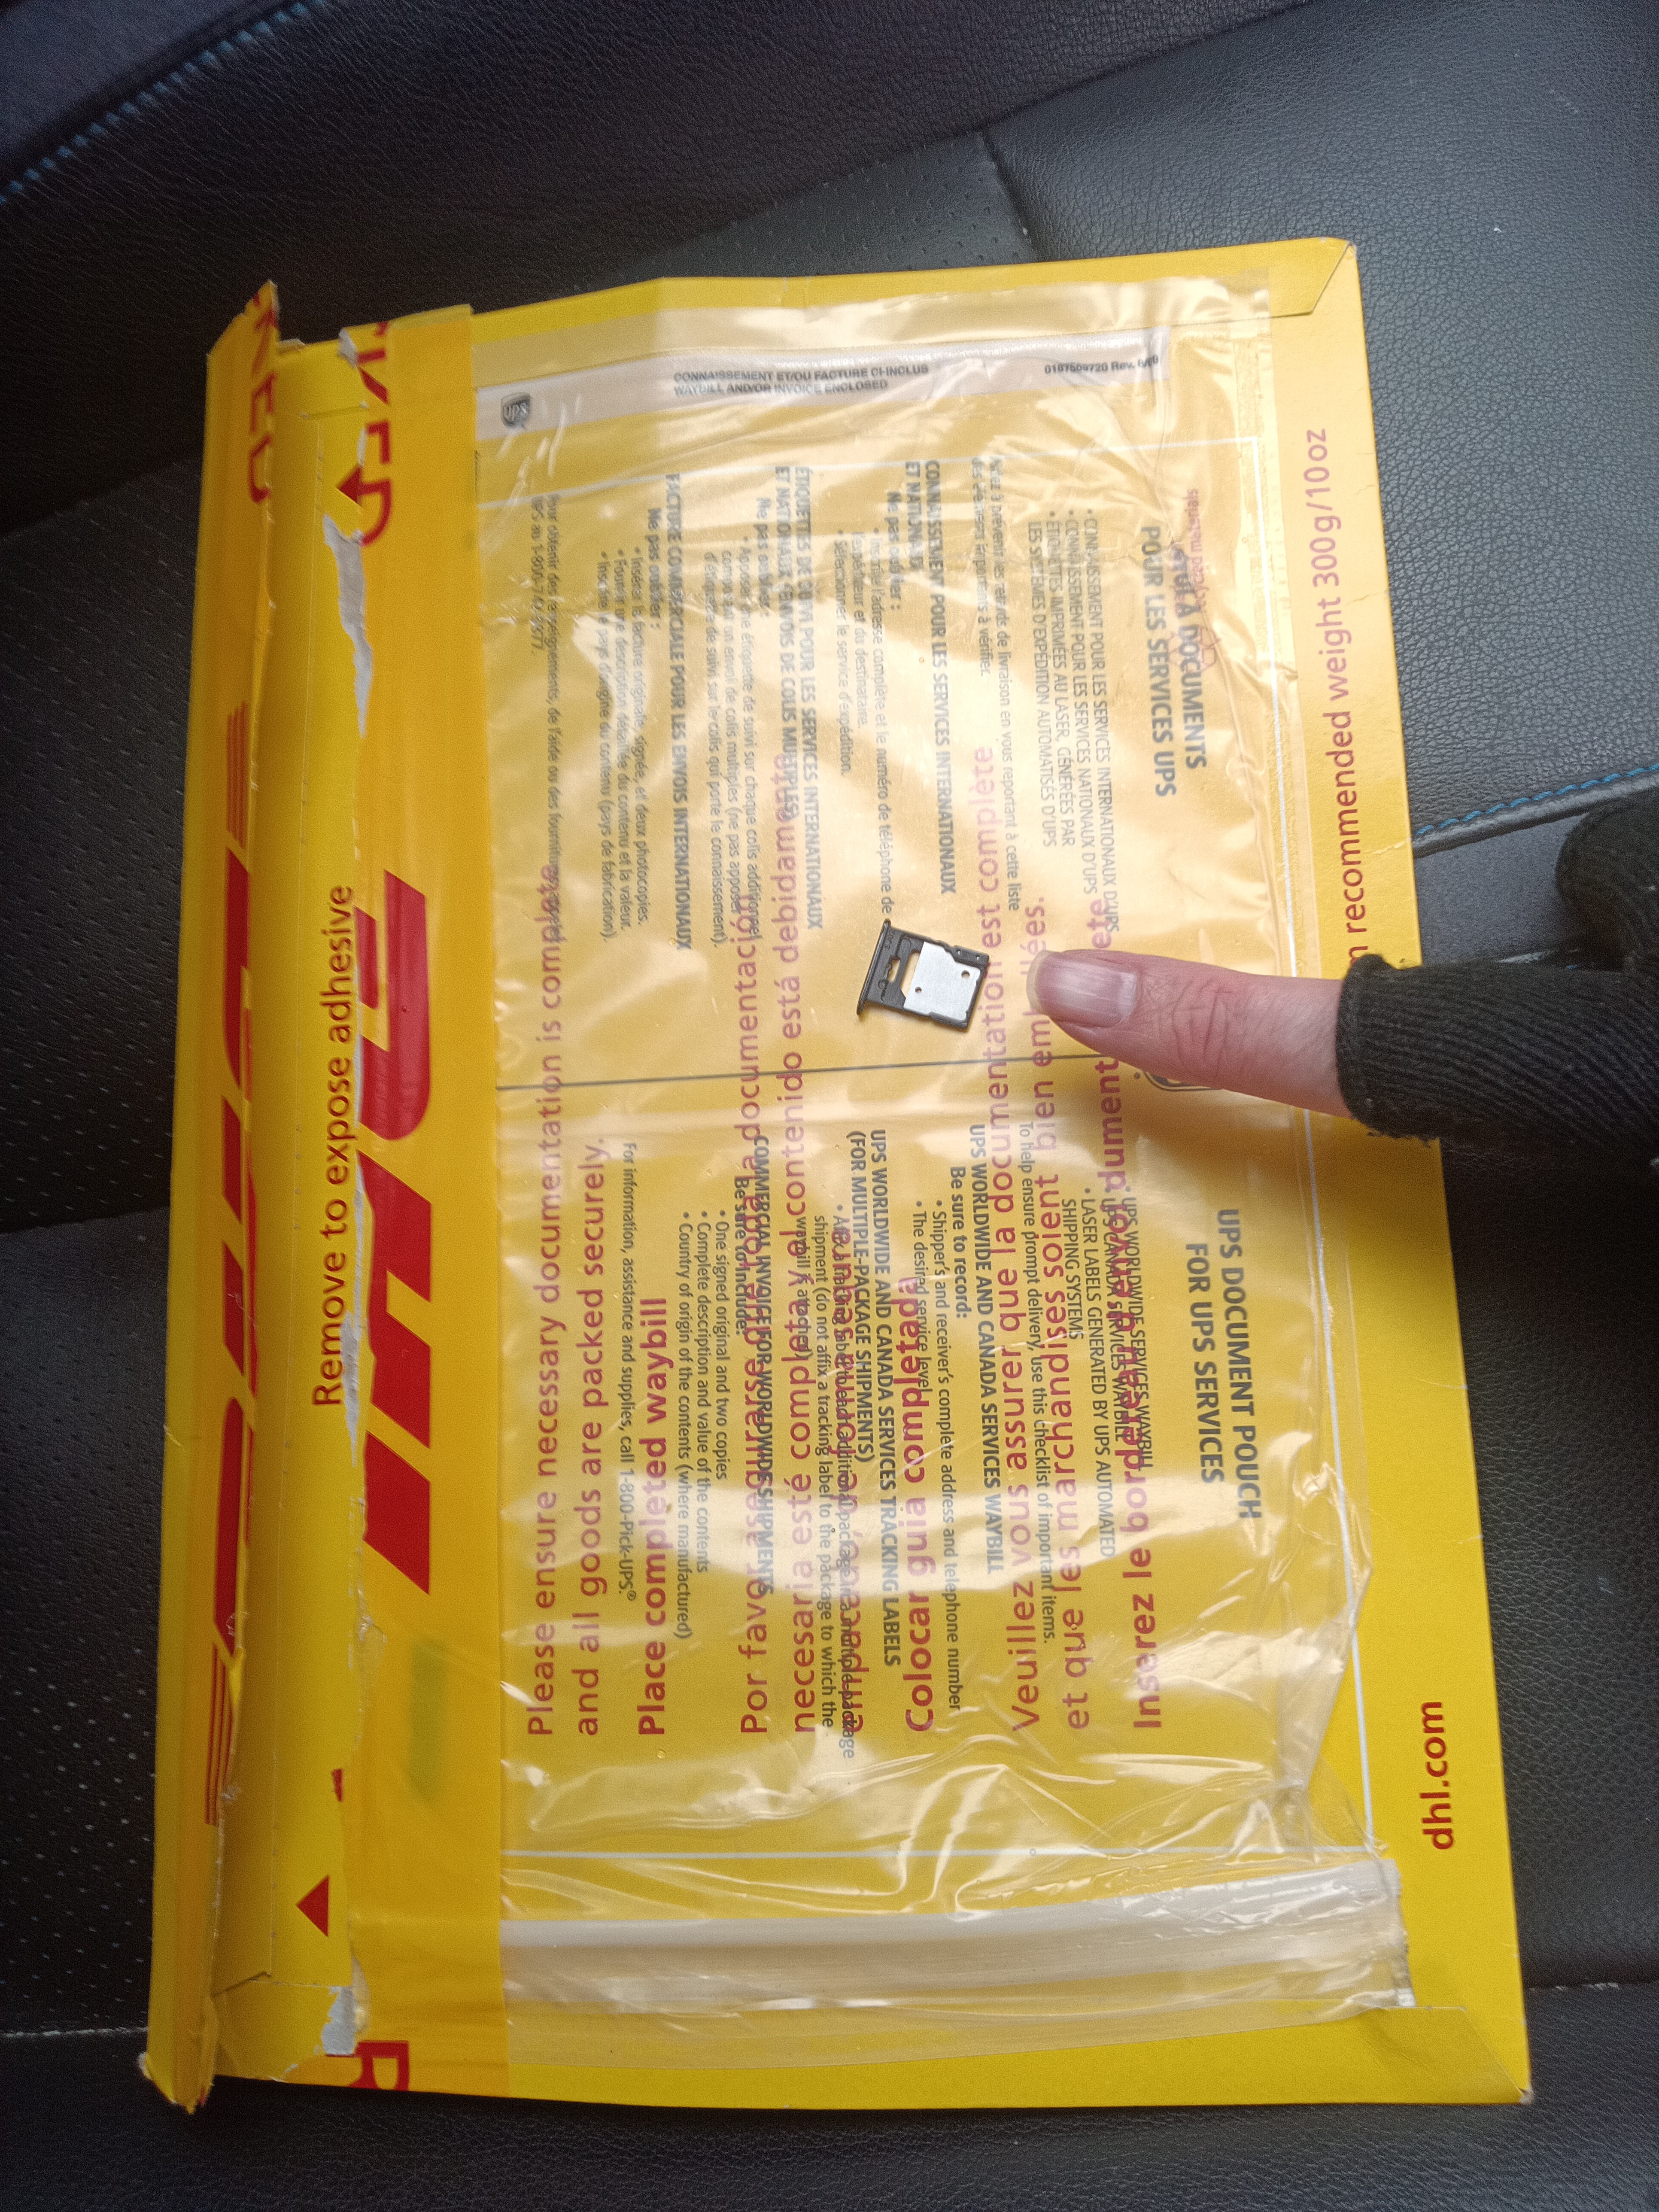
 The twentyfourth release of
 My Debian contributions this month were all